
awesome-android-security
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
android-securitycurated-resourceseducation+6
2.0k
saeidshirazi/awesome-android-securityA curated list of Android Security materials and resources For Pentesters and Bug Hunters
 nccgroup/conscrypttrustusercerts
Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 absholi7ly/poc-for-cve-2024-7014-exploit
Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit
 hunt-benito/two-dots-and-a-slash-cve-2026-18907-tecno-hi-browser-download-path-traversal
Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…
 adityatelange/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 acloudinthebluesky/cve-2019-6447-es-file-explorer
Technical analysis and safety-conscious research harness for CVE-2019-6447 in ES File Explorer for Android
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
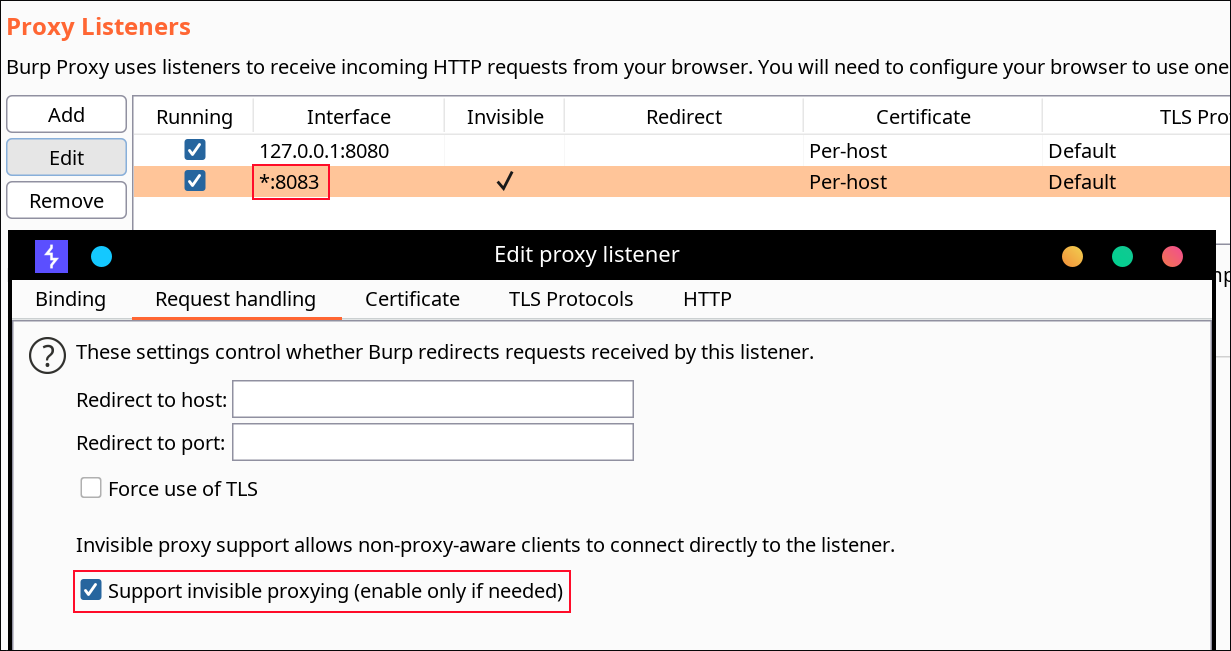 ptswarm/reflutter
Flutter Reverse Engineering Framework
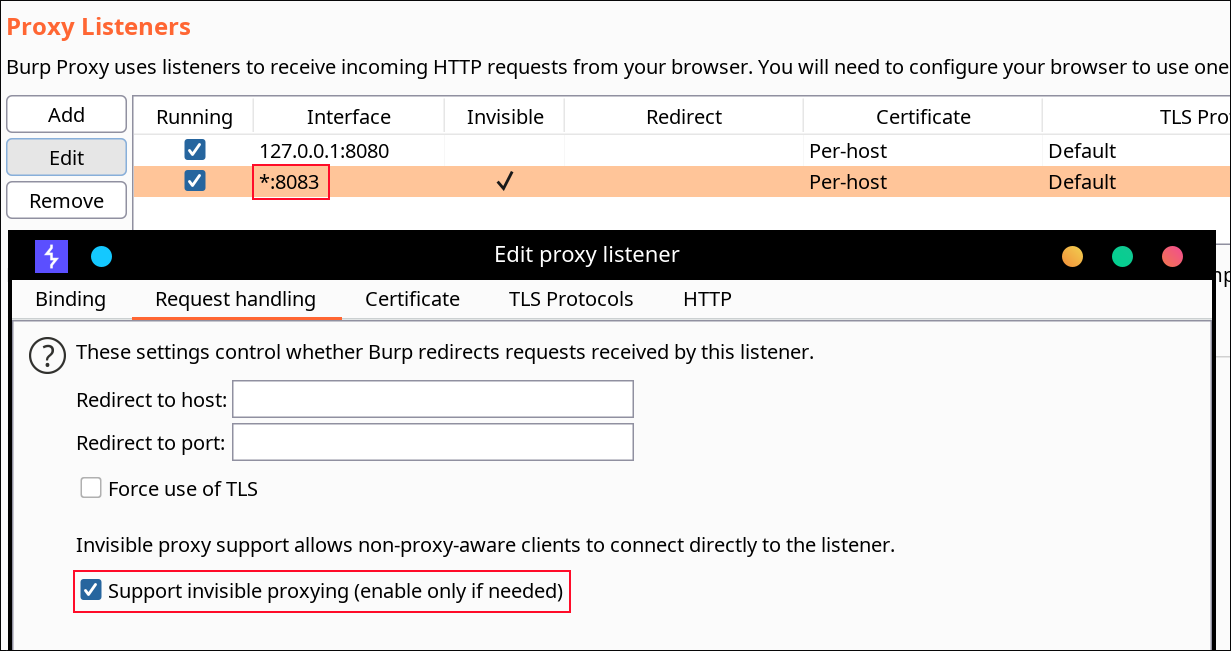 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 census/whatsapp-mitd-mitm
PoC and tools for exploiting CVE-2020-6516 (Chrome) and CVE-2021-24027 (WhatsApp)
 jaf0rk/cve-2026-14382
Proof-of-concept exploit for CVE-2026-14382, a high-severity ANGLE vulnerability in Chromium, with 32-bit and AArch64 PoCs achieving program counter…