
cve-2024-31317
 agg23/cve-2024-31317
Detailed discussion of Zygote vulnerability CVE-2024-31317
android-securityeducationexploitation+3
28
agg23/cve-2024-31317Detailed discussion of Zygote vulnerability CVE-2024-31317
 tinnci/cve-2024-31317
Detailed discussion of Zygote vulnerability CVE-2024-31317
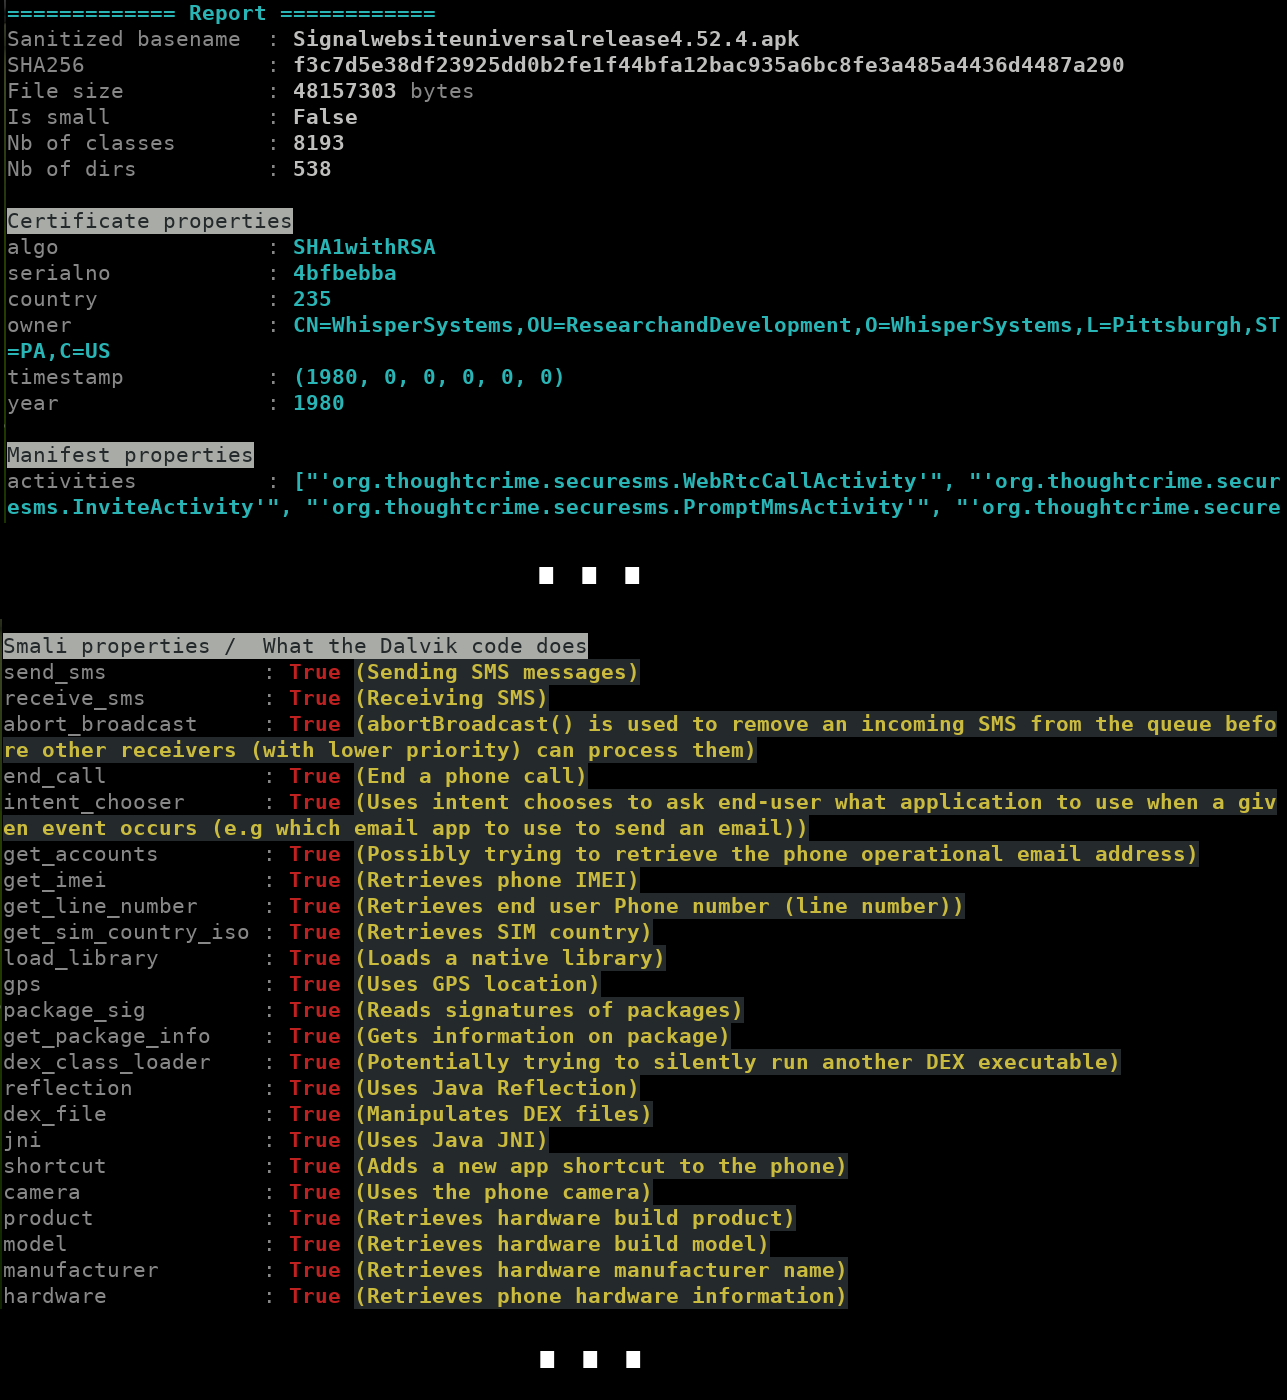 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
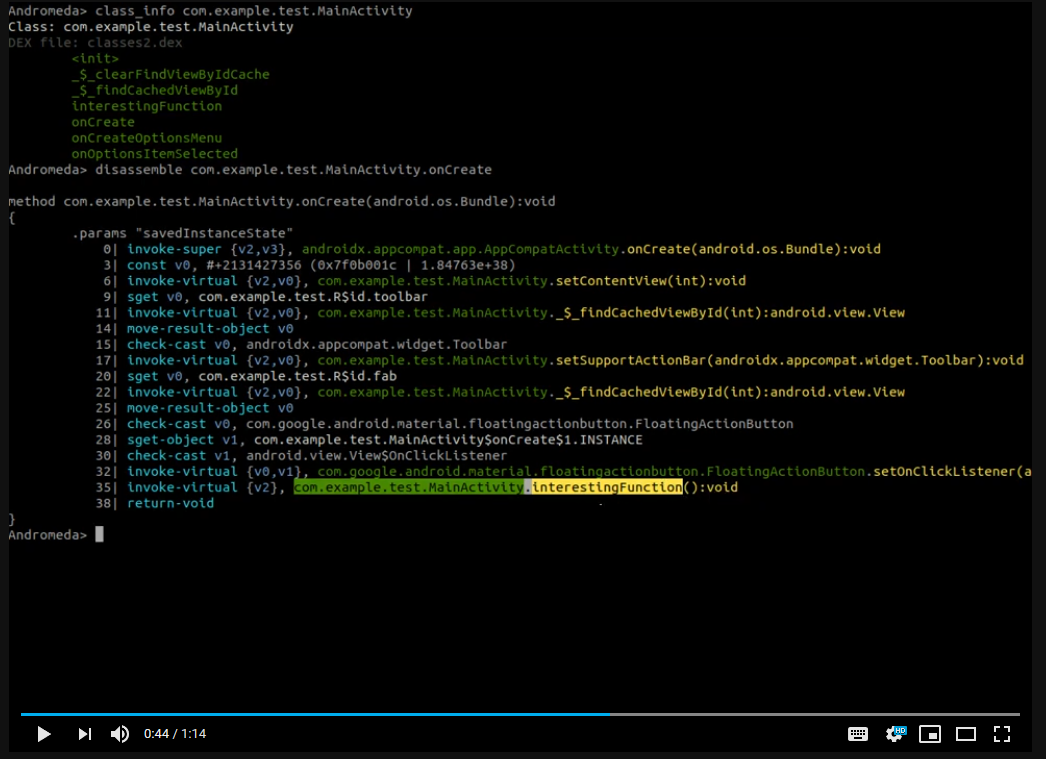 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…
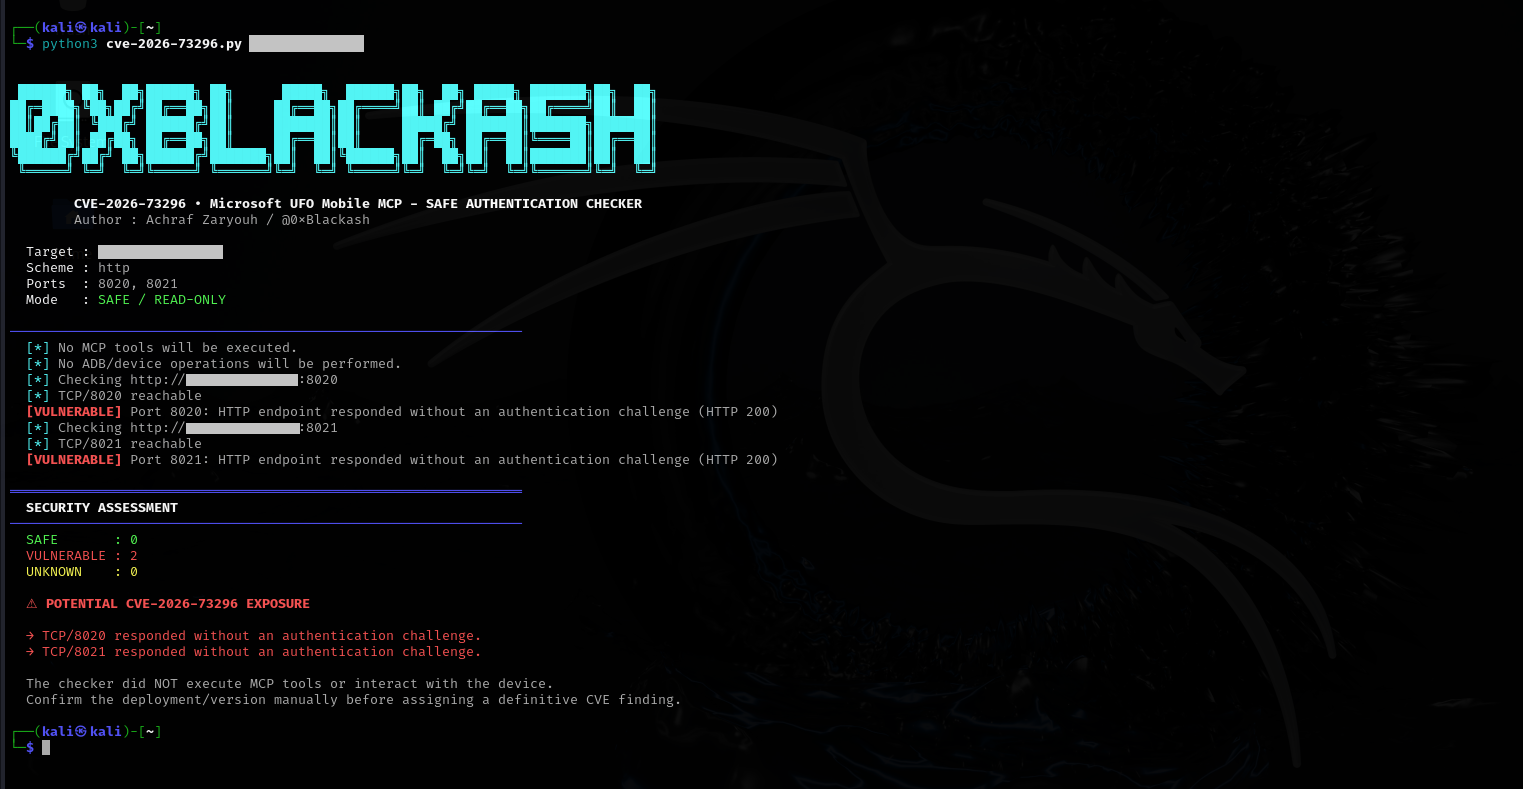 0xblackash/cve-2026-73296
Non-destructive security assessment tool for CVE-2026-73296, checking authentication boundaries on exposed Mobile MCP HTTP servers (ports 8020/8021)…
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 ashishb/android-security-awesome
A collection of android security related resources
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
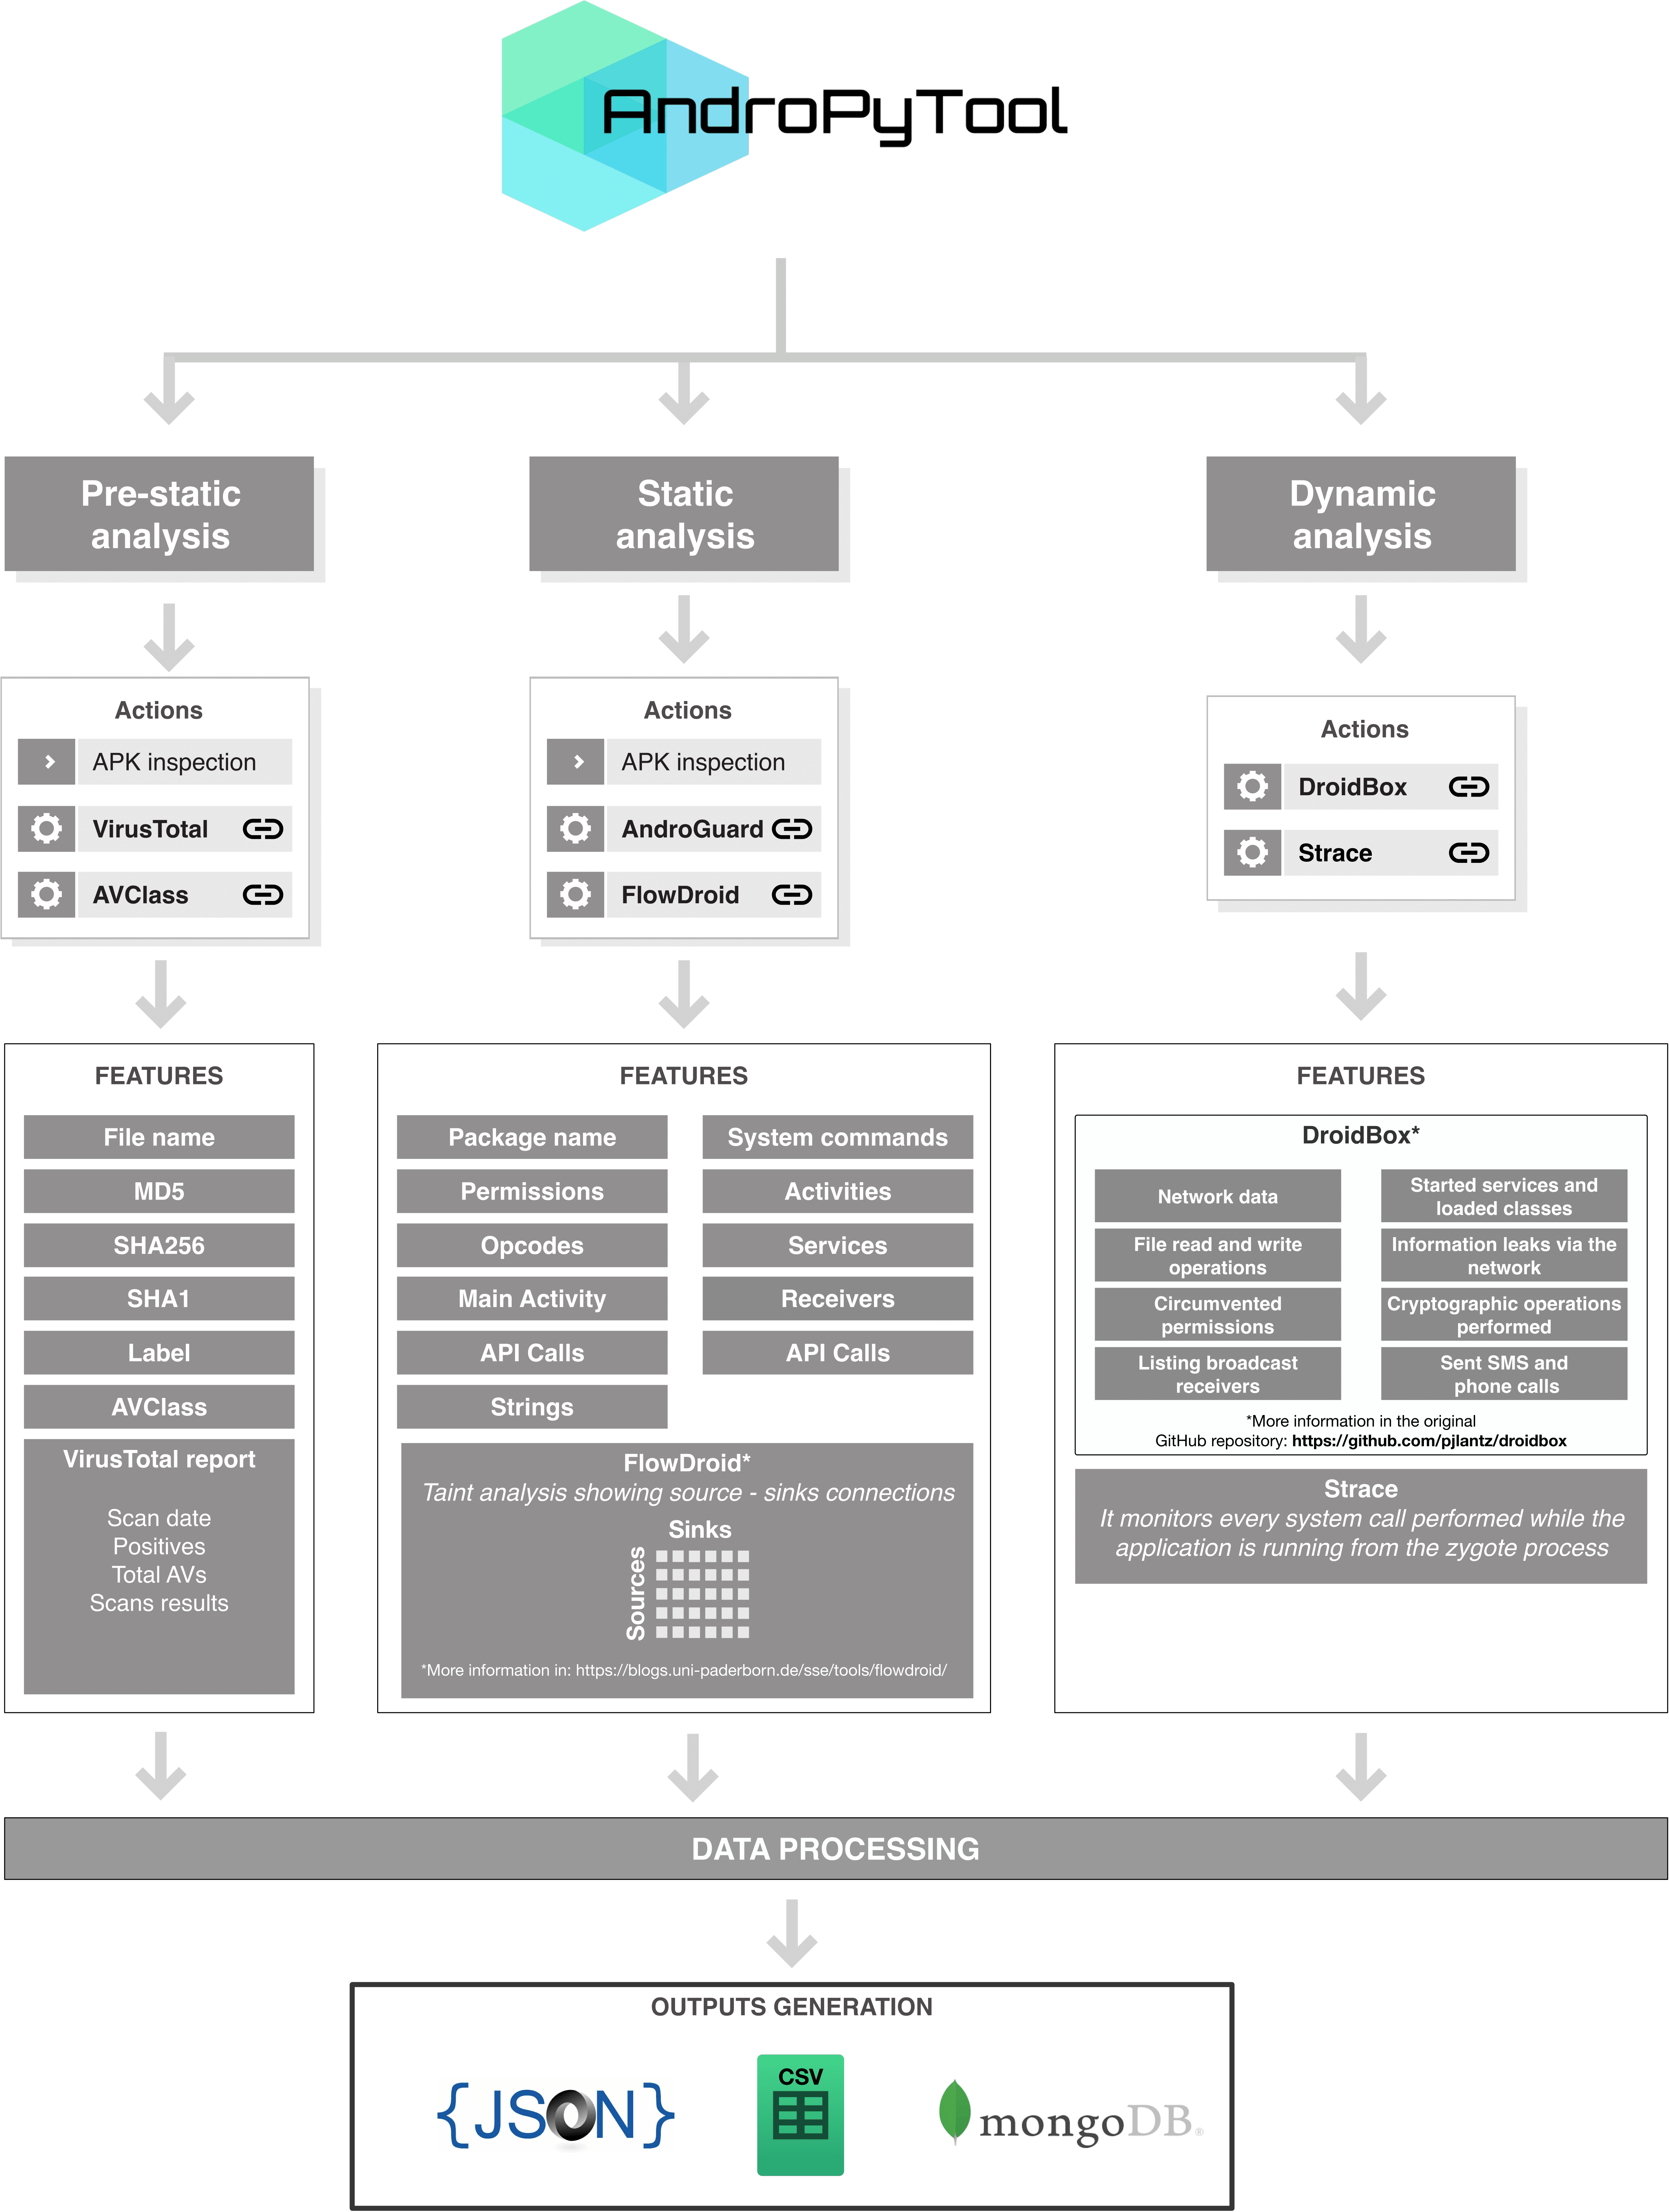 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 ele7enxxh/cve-2014-7911
Proof-of-concept exploit for Android local privilege escalation (CVE-2014-7911) targeting Nexus5 with ROP chain and heap spraying to gain system uid.
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.