
morf
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
android-securityios-securitymobile-security+4
85
amrudesh1/morfMobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 0x742/cve-2020-0082-externalvibration
This repo contains a proof-of-concept for 📱🚀👑⚡, a deserialization vuln for local escalation of privilege to system_server in Android 10. This…
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
 onesmiledx/cve-2026-43499
A modified method to root Android device with locked bootloader via new exploit. (Only for Samsung now or smthing like that devices cuz i ported it…
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combined of CVE-2026-49881 and…
 liuyun201990/strandhogg2
PoC of StrandHogg2 (CVE-2020-0096)
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
 niklashigi/apk-mitm
🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection
 bhathiya404/exploiting-stagefright-vulnerability-cve-2015-3864
Exploit implementation for Android Stagefright vulnerability CVE-2015-3864, enabling remote code execution and privilege escalation on Android 5.1.1…
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
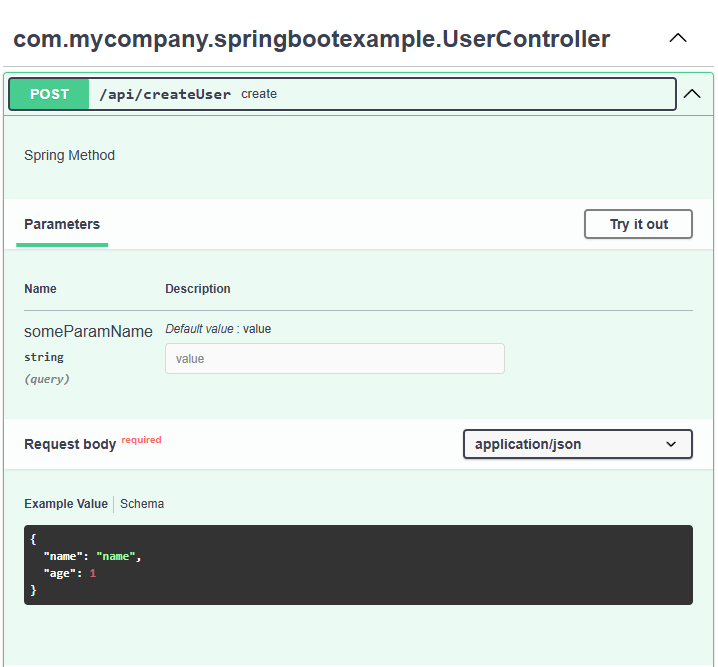 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 xtiankisutsa/twiga
A tool that enumerates Android devices for information useful in understanding its internals and for exploit development. It supports android 4.2 to…
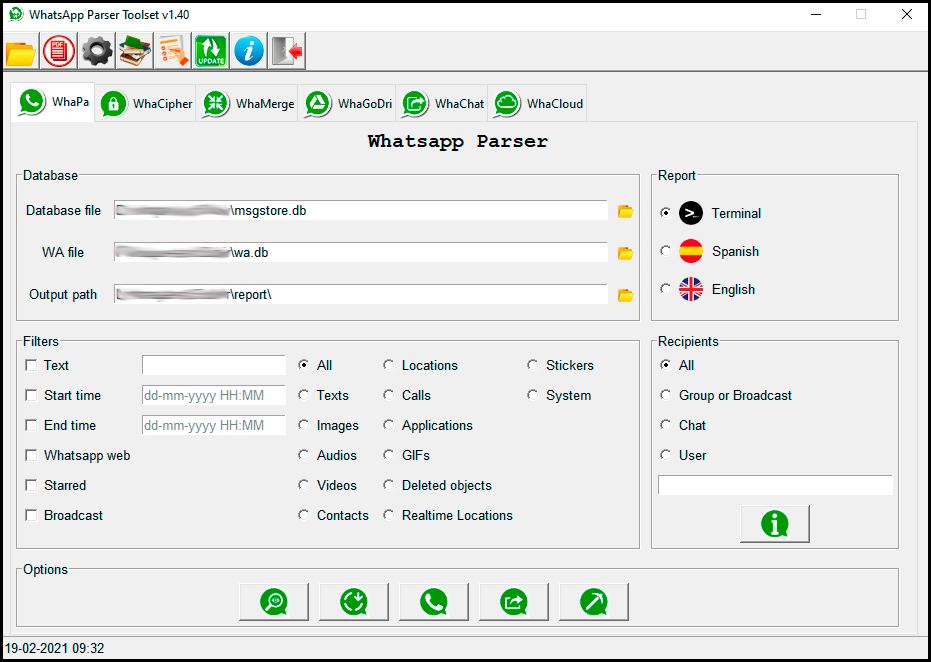 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 pjlantz/droidbox
Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
 p1gl3t/cve-2015-1474_poc
Proof-of-concept exploit for CVE-2015-1474, demonstrating a rogue parcel crash in Android SurfaceFlinger via deserialization, enabling privilege…