
IonStack-S22U
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
android-securitybinary-exploitationexploitation+3
93
sarabpal-dev/ionstack-s22uCVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 r0rt1z2/automatedroot
Root your MediaTek device with CVE-2020-0069
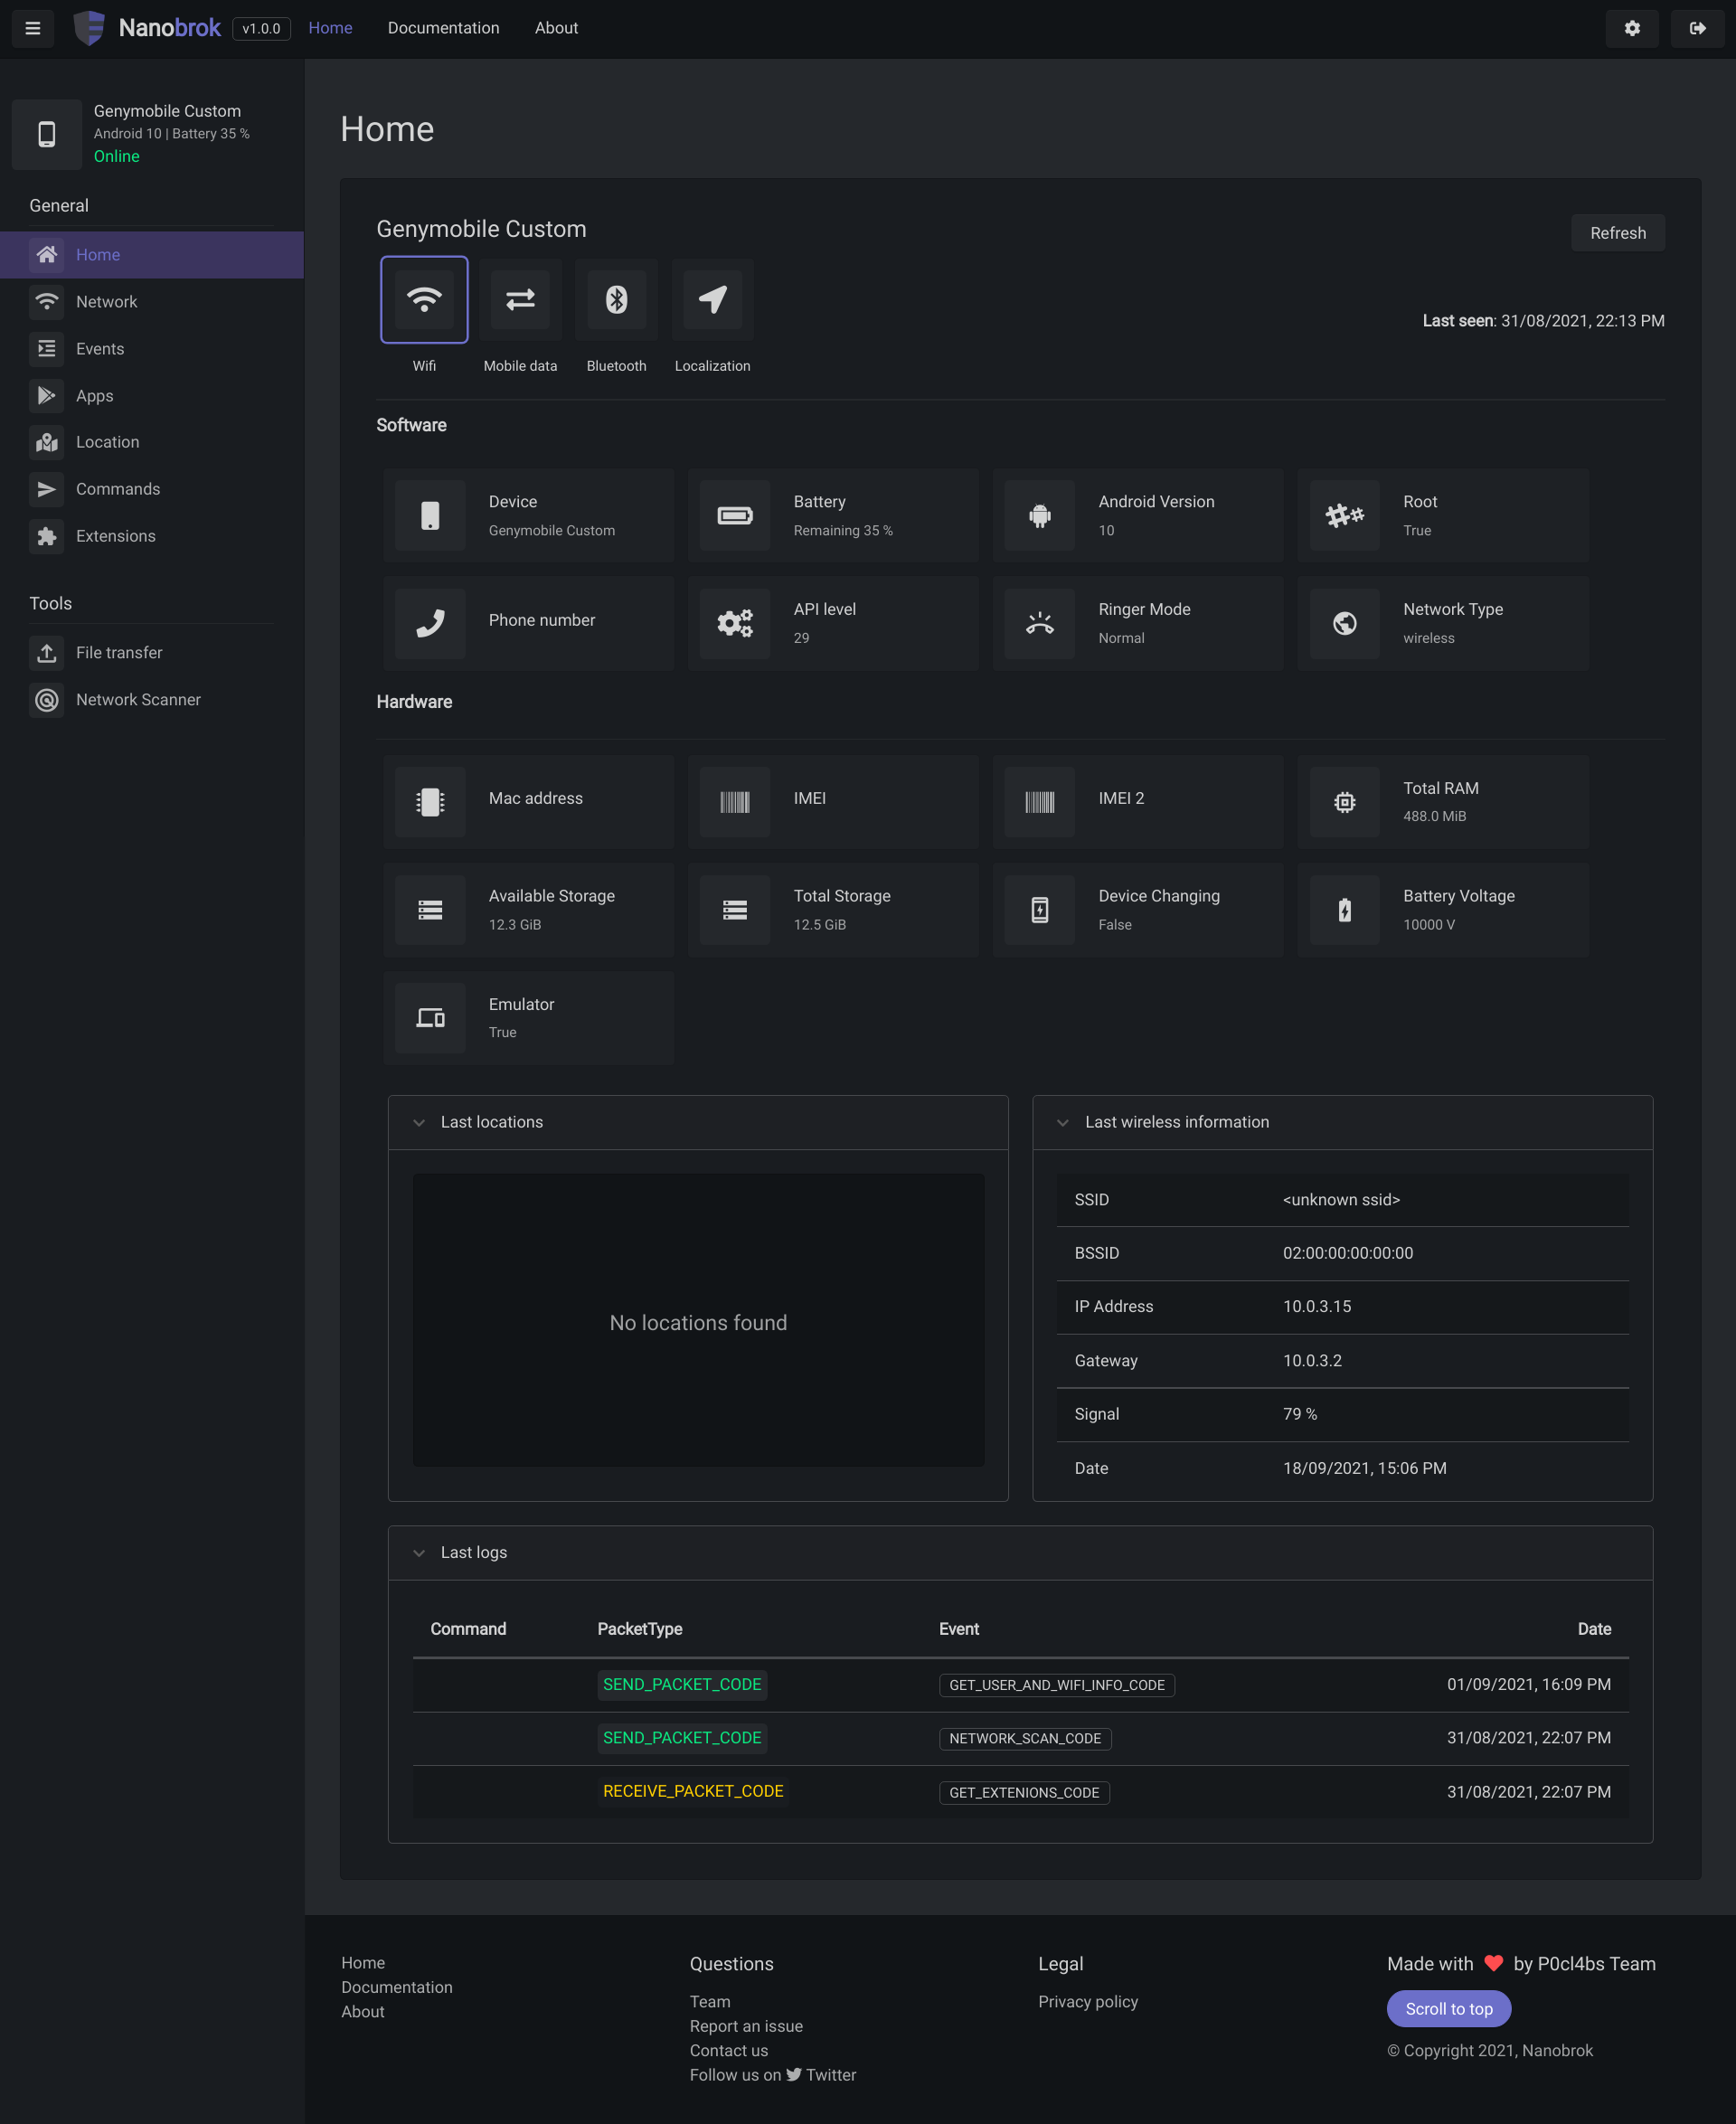 p0cl4bs/nanobrok
Web Service write in Python for control and protect your android device remotely.
 hamz-a/frida-android-libbinder
PoC Frida script to view Android libbinder traffic
 cakestwix/android-cve-2026-43499
Android version CVE-2026-43499 tester
 p2p3p/ghostlock-for-oneplus
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加设备。
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 woshimaniubi8/cve-2026-43499-root-kernelsu
基于内核漏洞CVE-2026-43499的本地提权适配,集成嵌入式 KernelSU.CVE-2026-43499+KernelSU越狱模式
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 wtrwx/smt878u-ionstack-poc
UNFINISHED/WIP - CVE-2026-43499 (IonStack/GhostLock) research POC for Samsung SM-T878U / gts7l. Trigger + geometry verified, NO working root yet.
 parallelbeings/cve-2019-14079
USB device fuzzing on Android Phone
 cuteaplane/ghostlock-for-oneplus15t
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加15T.
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
 linux-tools/vivo_iqoo_neo_9_root_research_on_cve-2025-21479
Android kernel root exploit for iQOO Neo9 (CVE-2025-21479, Adreno GPU SDS) providing arbitrary physical write, kernel cap bypass, and root daemon/su…