
framework_base_AOSP10_r33_CVE-2021-0513
 nanopathi/framework_base_aosp10_r33_cve-2021-0513
android-securityexploitationvulnerability-analysis
nanopathi/framework_base_aosp10_r33_cve-2021-0513 thampakon/cve-2023-35674
ช่องโหว่ CVE-2023-35674 *สถานะ: ยังไม่เสร็จ*
 sahalll/cve-2024-54916
Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…
 vino-theva/cve-2019-6447
This paper is about manual exploitation of android open port vulnerability found in ES file manager. This open TCP 59777 port allows the attacker to…
 uthrasri/frameworks_opt_net_wifi_cve-2021-0466
 nanopathi/packages_apps_managedprovisioning_cve-2021-39692
 febinrev/cve-2019-6447-esfile-explorer-exploit
ES File Explorer v4.1.9.7.4 Open port vulnerability exploit. CVE-2019-6447
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
 vinukalana/cve-2019-6447-android-vulnerability-in-es-file-explorer
This repository is developed to understand CVE-2019-6447
 sandarufdo/es-file-explorer-open-port-vulnerability---cve-2019-6447
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 nipund513/exploiting-uaf-by-ret2bpf-in-android-kernel-cve-2021-0399-
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 oopnv70-lab/ghostlock-apk
独立 APK:CVE-2026-43499 GhostLock 提权 + Shizuku shell 身份执行
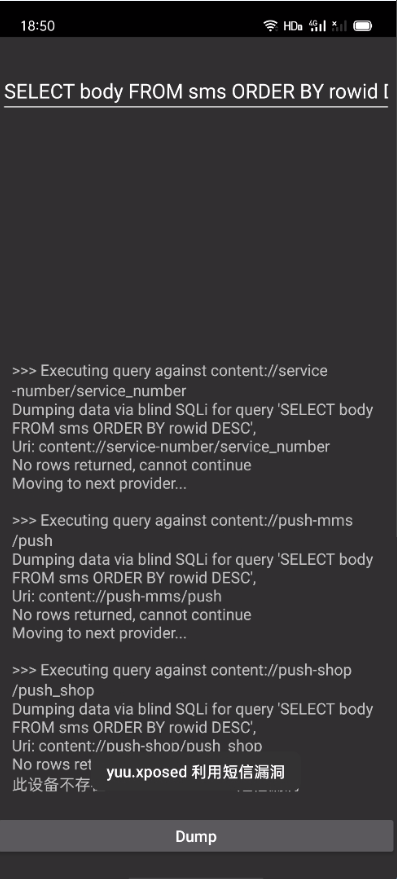 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案