
Ghost
 entysec/ghost
Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
android-securityexploitationpenetration-testing+2
3.4k
entysec/ghostGhost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
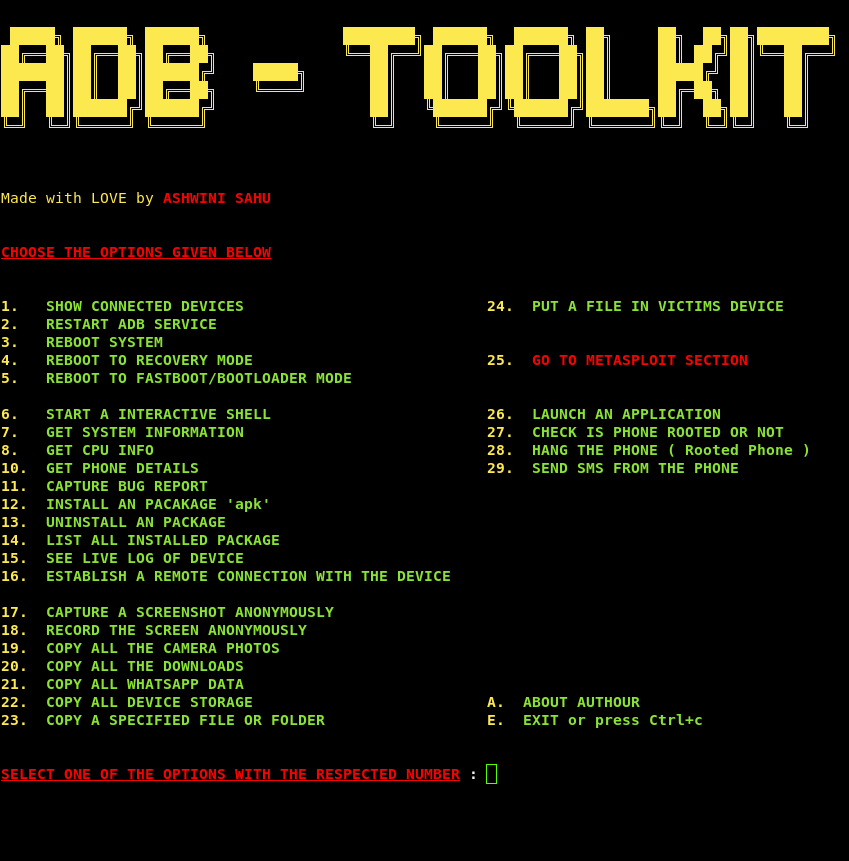 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
 1n3/reverseapk
Quickly analyze and reverse engineer Android packages
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 davidbuchanan314/nxloader
My first Android app: Launch Fusée Gelée payloads from stock Android (CVE-2018-6242)
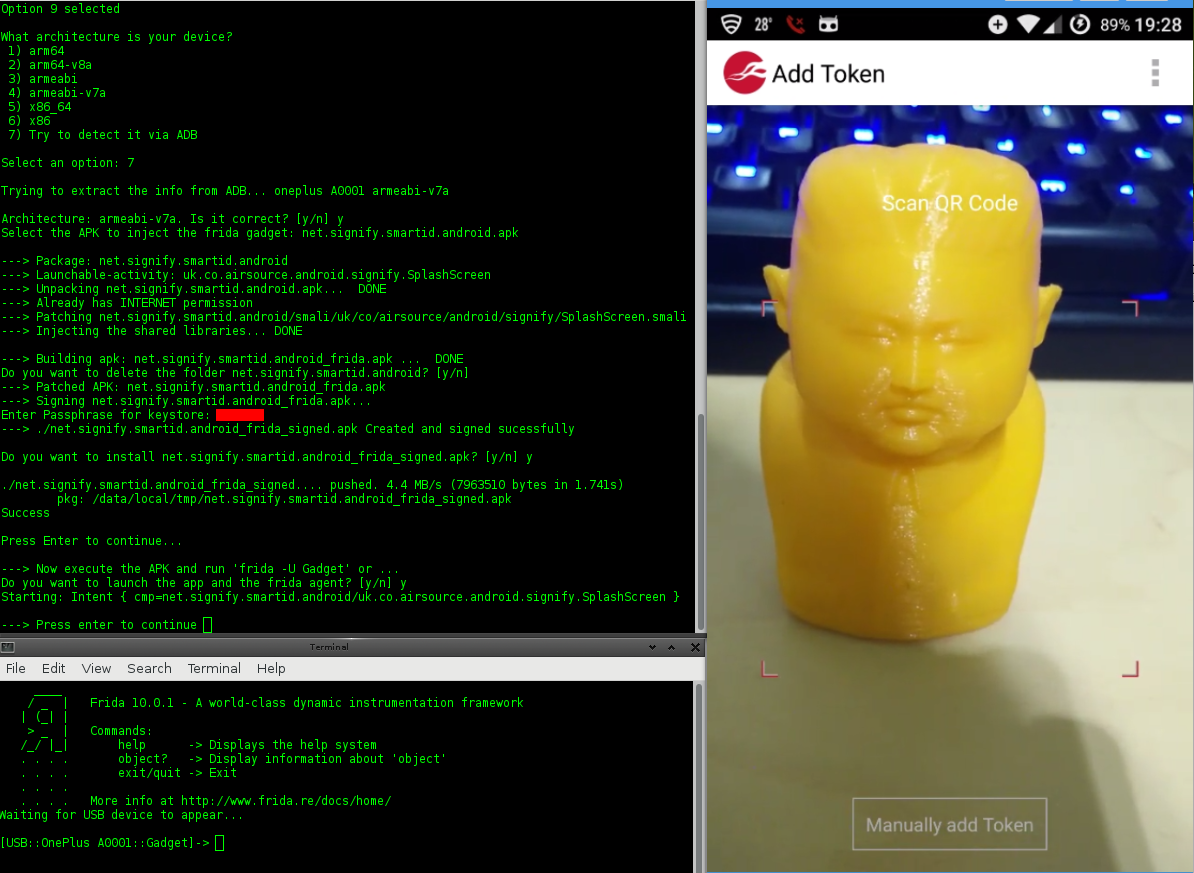 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment
 r0rt1z2/automatedroot
Root your MediaTek device with CVE-2020-0069
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 cuteaplane/ghostlock-for-oneplus15t
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加15T.
 ilgobbo00/cve-2023-6241-pixel7_adaptation
Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241
 xiaobailovesstirring/ghostlock-k419-adapter
GhostLock (CVE-2026-43499) adapter for 4.19.152-perf+ Android kernel
 aureliusivan/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694
 filipkarc/poc-ubuntutouch-pin-privesc
CVE-2022-40297 - Proof of Concept: Privilege escalation in Ubuntu Touch 16.04 - by PIN Bruteforce
 voidgguy/lenovo-a1000g-mt8317-a412_01_09_130907-kernel-3.4.0-root-cve-2016-5195
[AI-assisted] Root method for Lenovo IdeaTab A1000G (MT8317, kernel 3.4.0, Android 4.1) via CVE-2016-5195 (Dirty COW)
 aureliusivaninvenioptl/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694