file-notification-attacks

Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…

Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…

Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10

Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking

Extract the managed (.NET) assemblies out of a MAUI Android assembly store.

Proof-of-concept for CVE-2021-43530, a Universal XSS vulnerability in Firefox for Android caused by improper URL sanitization when processing QR code…

PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…

Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…

Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…

CVE-2023-27703 An Android version of pikpak version V1.29.2 element debugging interface leakage vulnerability

Public advisory & PoC for CVE-2026-26897 — Deep Link Bypass in EcoOnline EHS Android (com.airsweb.v10), fixed in 0.2.500

Proof-of-concept exploit for CVE-2022-1364 targeting Chromium-based Bromite on Android (arm_ChromePublic.apk), demonstrating a browser memory-safety…

Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…

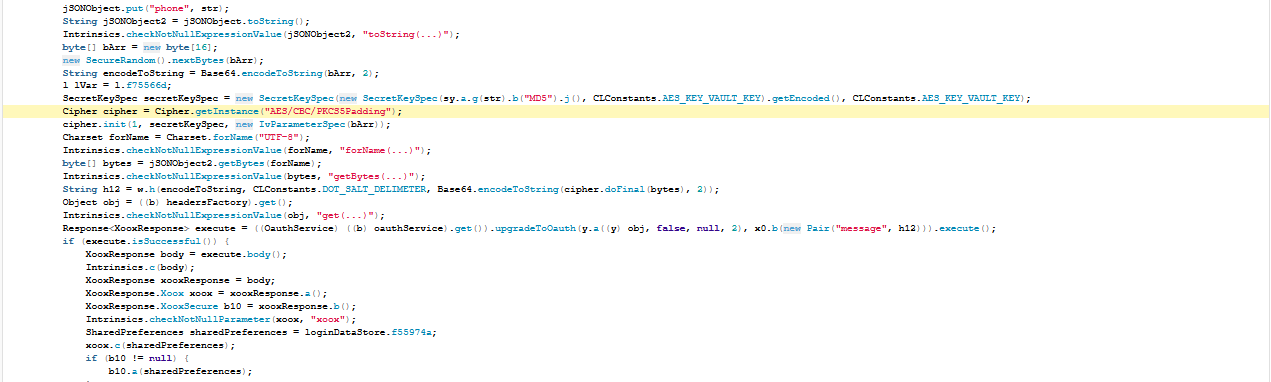
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…

Proof-of-concept exploit for Same-Origin Policy bypass in Samsung Internet Browser for Android, demonstrating a cross-origin data access…

A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.

CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…

Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)

ES File Explorer Open Port Vulnerability - CVE-2019-6447