
Mi8E5-Unlocker-by-CVE-2026-43499
 joehquak/mi8e5-unlocker-by-cve-2026-43499
Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English
android-securitybinary-exploitationexploitation+6
joehquak/mi8e5-unlocker-by-cve-2026-43499Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English
 jeboo/bypasslkm
Using CVE-2013-6282 to bypass Samsung kernel module authentication
 zachinio/cve-2020-0001
POC to run system component in an untrusted-app process
 irsl/cve-2022-20128
Android Debug Bridge (adb) was vulnerable to directory traversal attacks that could have been mounted by rogue/compromised adb daemons during an adb…
 betalphafai/cve-2015-6637
Proof-of-concept exploit for Android privilege escalation vulnerability CVE-2015-6637, demonstrating memory corruption to gain elevated privileges.
 anyone202/cybermeowfia-termux
Termux Privilege Escalation Tool & Root Manager - CVE-2026-43501
 roeeh/bootmodechecker
This app checks if you're vulnerable to CVE-2016-8467 and/or if your bootmode property has been tampered with.
 nccgroup/test_avb_key
Python utility to check if Android verified boot images (vbmeta) are signed with publicly known test keys, identifying misconfigurations in release…
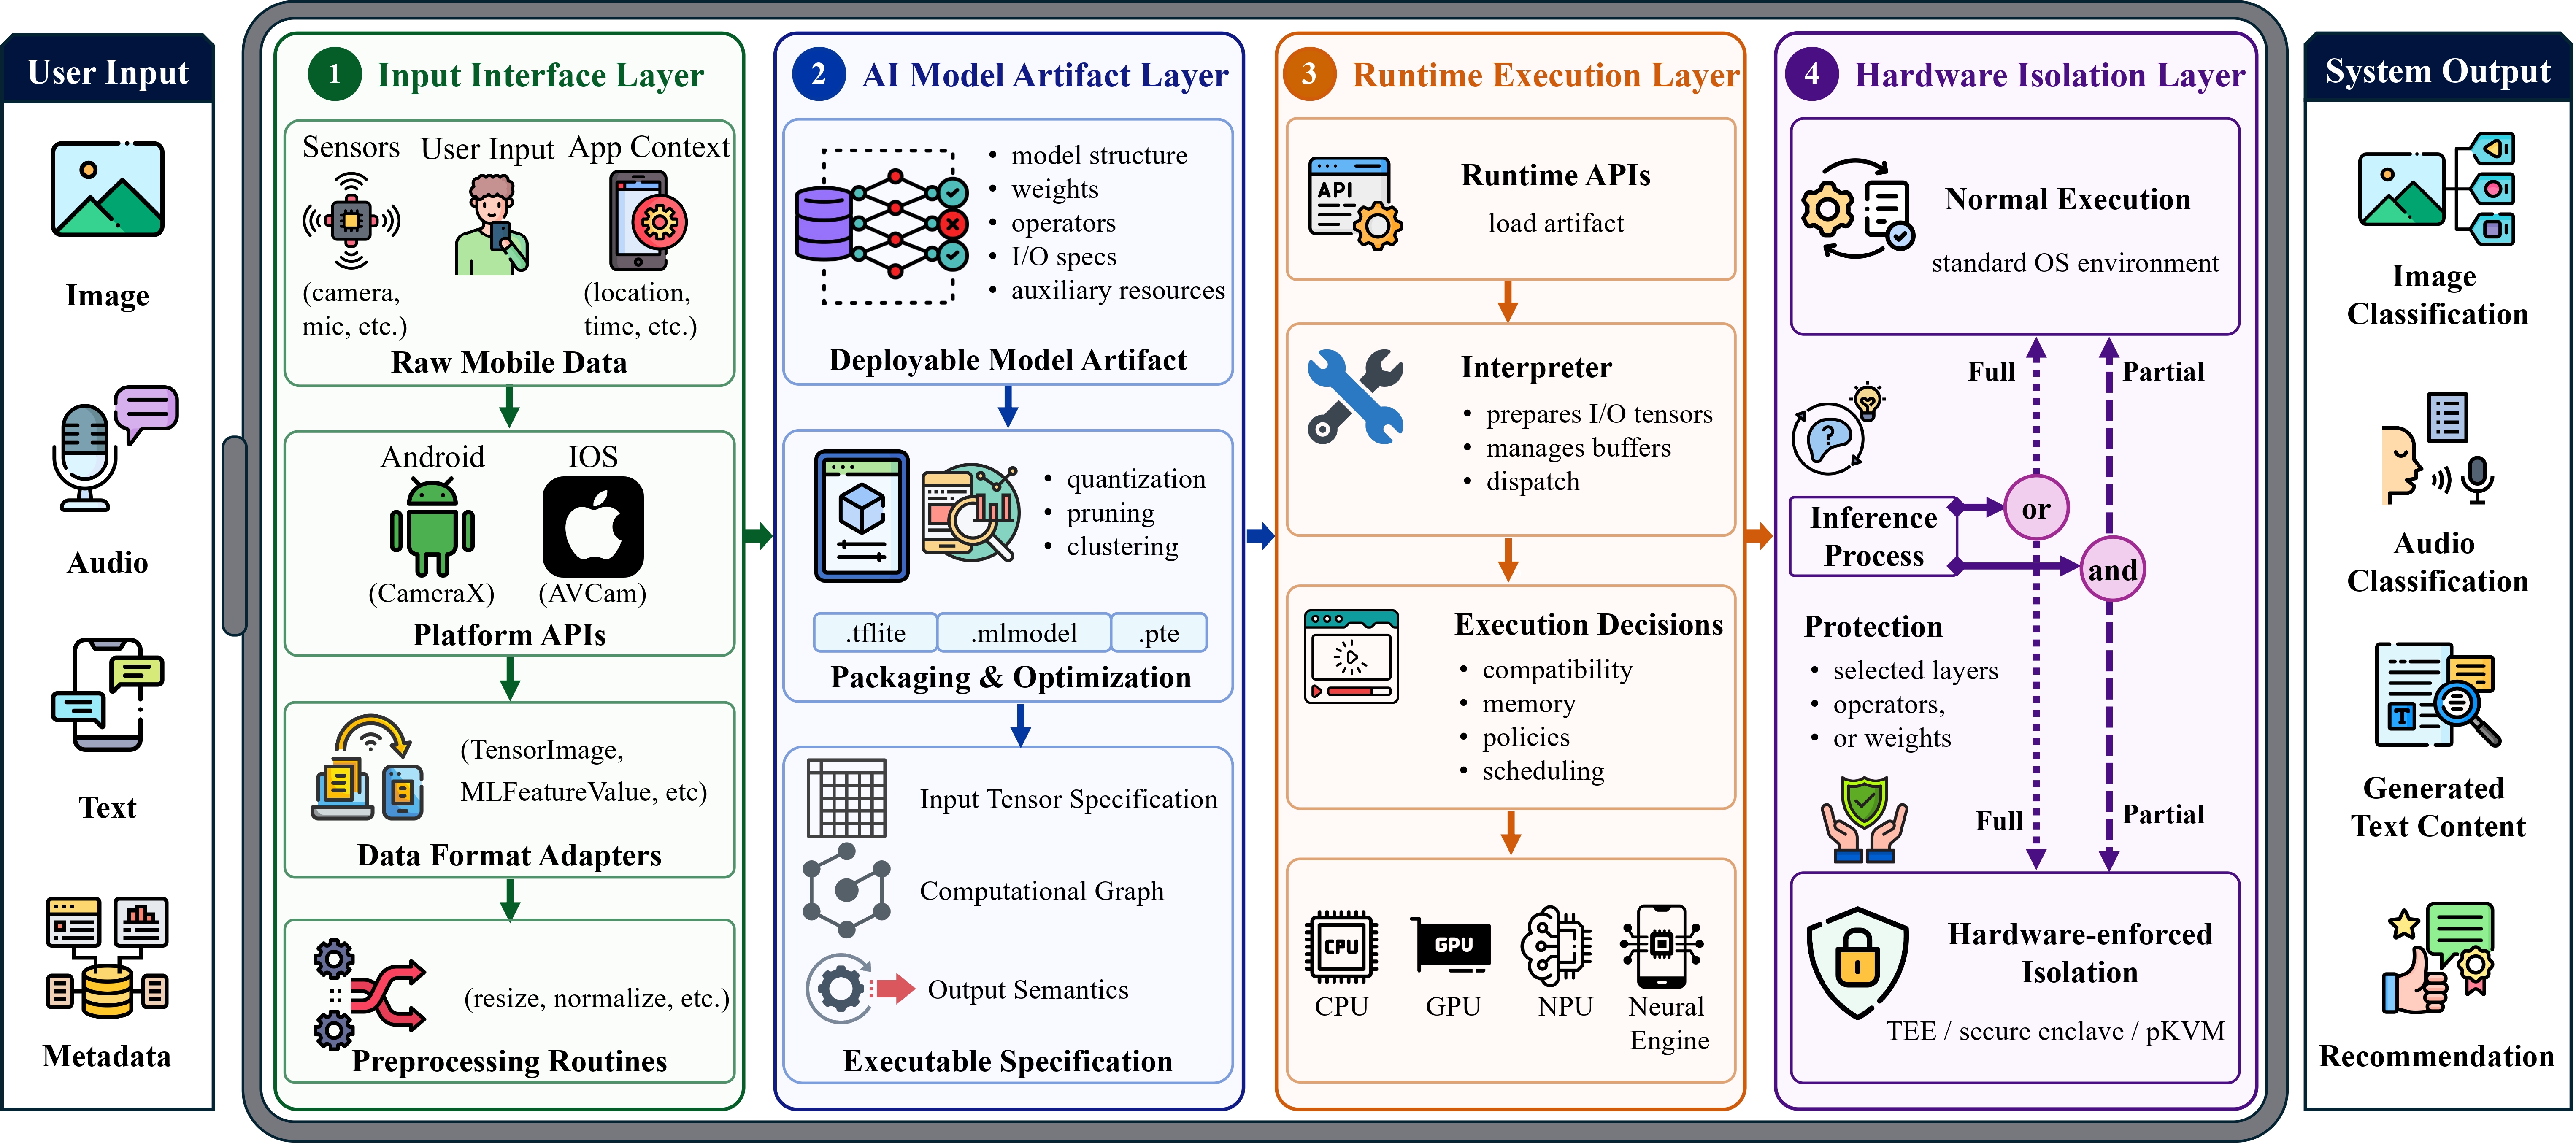 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 hhj4ck/cve-2016-2067
GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.
 nighthawkk/audioserver-voip-recorder
🔬 An advanced Android research tool for real-time VoIP audio capture (Uplink/Downlink) by dynamically hooking libaudioflinger.so. Tested and built…
 crackercat/servicecheater
PoC of CVE-2020-0108
 soralis0912/cve-2026-43499-aristotle-apk
Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…
 filipkarc/poc-ubuntutouch-pin-privesc
CVE-2022-40297 - Proof of Concept: Privilege escalation in Ubuntu Touch 16.04 - by PIN Bruteforce
 kudima/exploit_playground
Analysis of public exploits or my 1day exploits
 atorninja/cve-2019-2215
PoC and analysis of CVE-2019-2215, a use-after-free in Android Binder, with kernel instrumentation and exploit tuning for affected Samsung devices.
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 zychen027/cve-2026-43499_hw-clt-al01
Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.