
drozer
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
android-securityexploit-frameworksmobile-app-pentesting+3
reverseclabs/drozerThe Leading Security Assessment Framework for Android.
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 georgiaw/smartphone-pentest-framework
Repository for the Smartphone Pentest Framework (SPF)
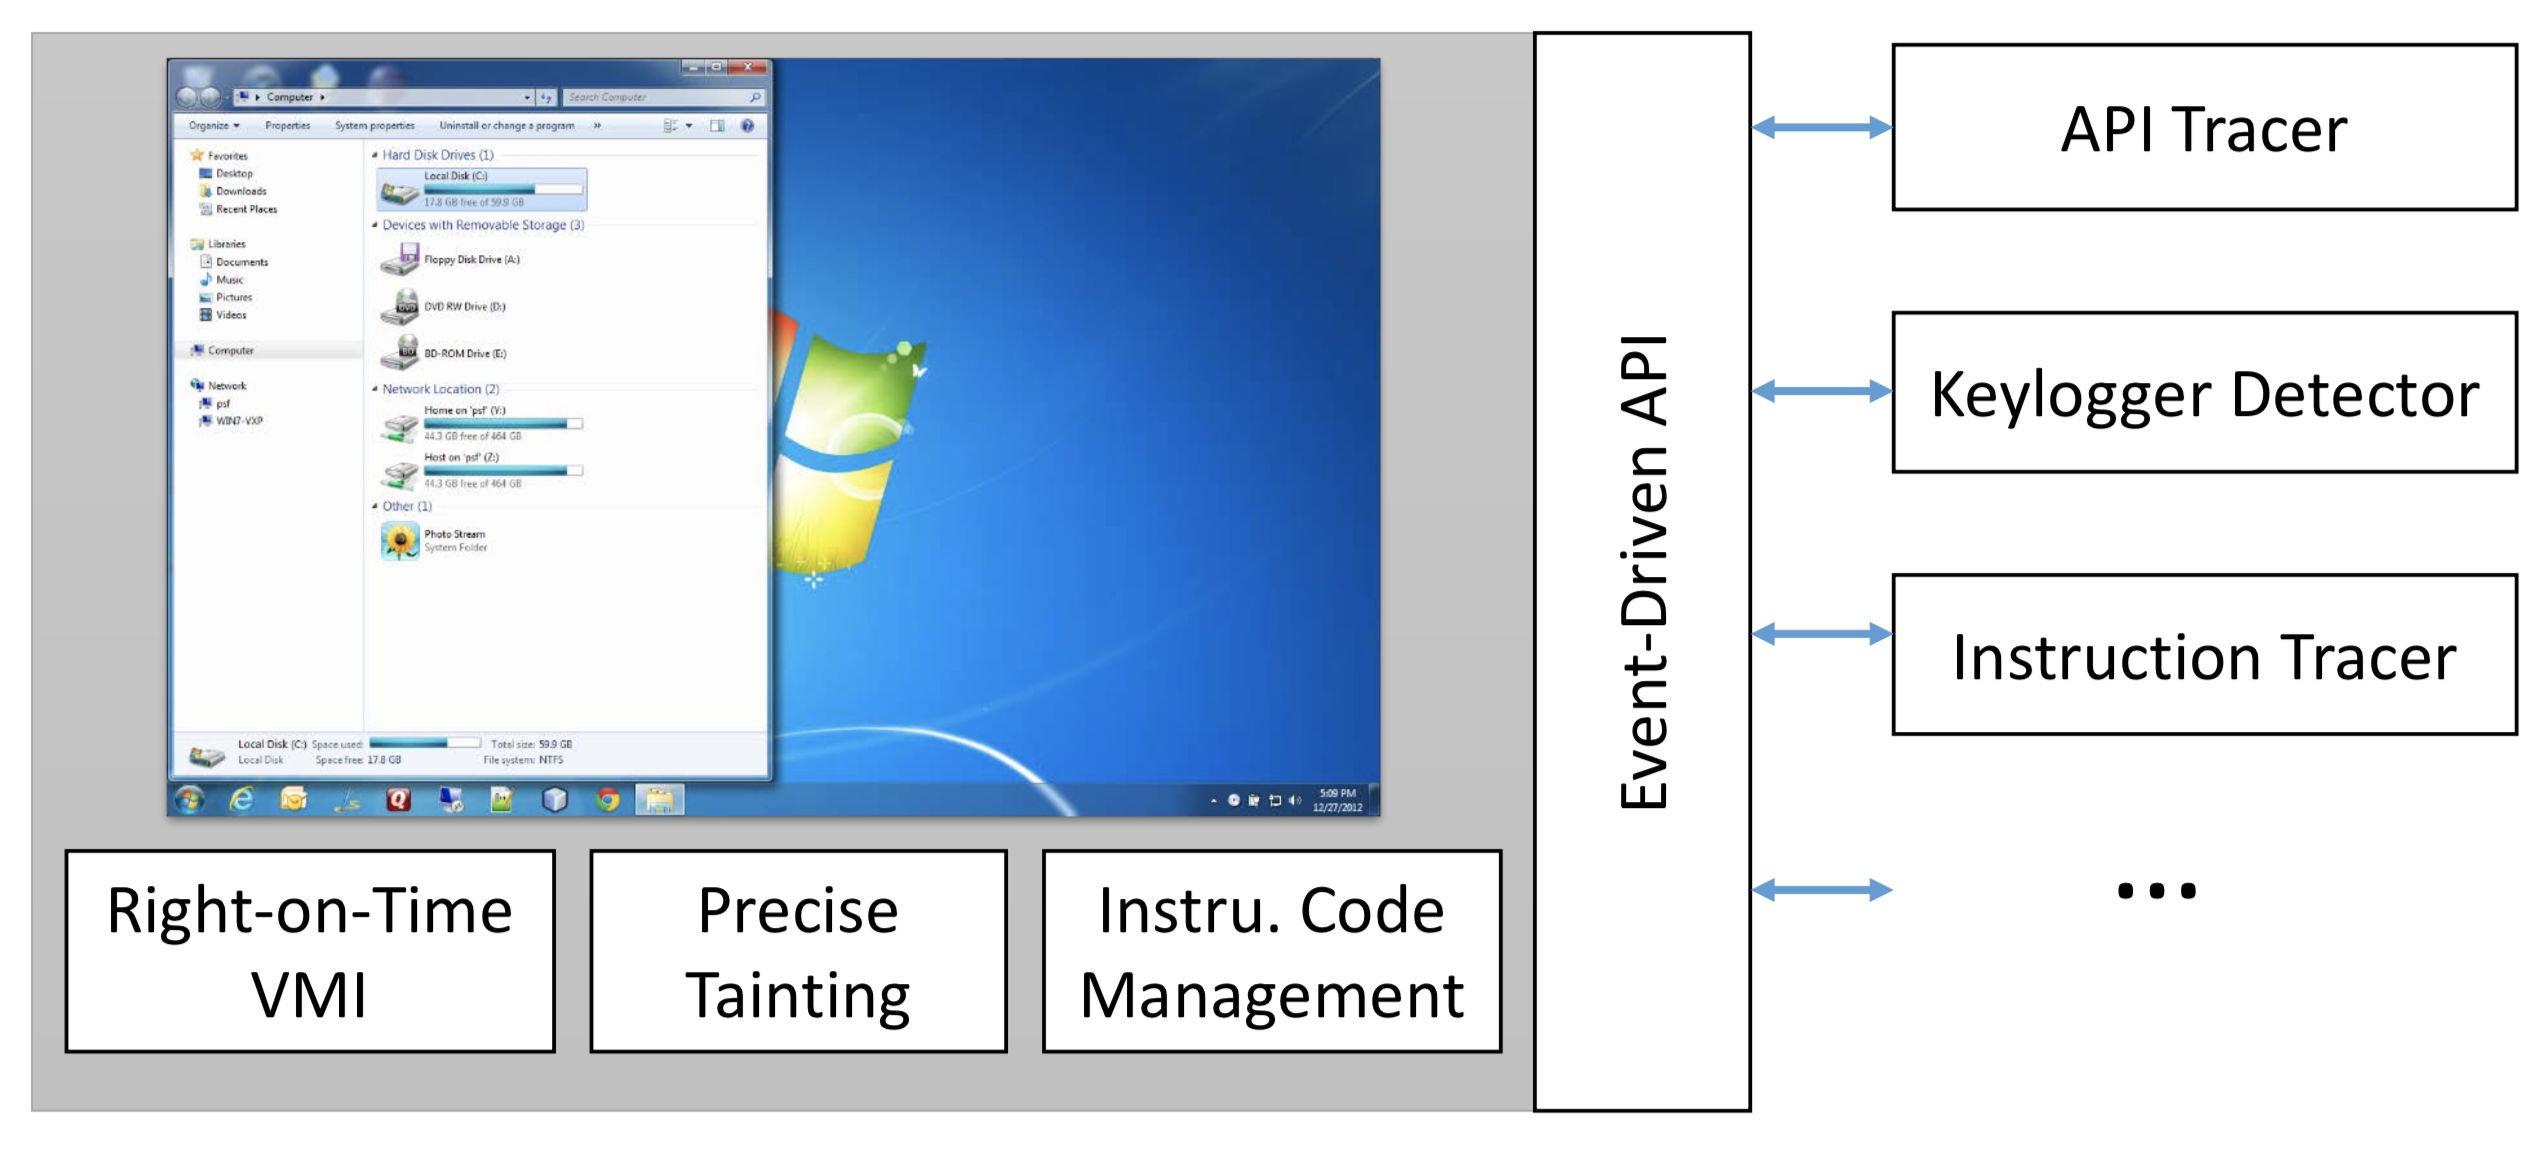 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 donctl/sandy
Release of the sandy framework.
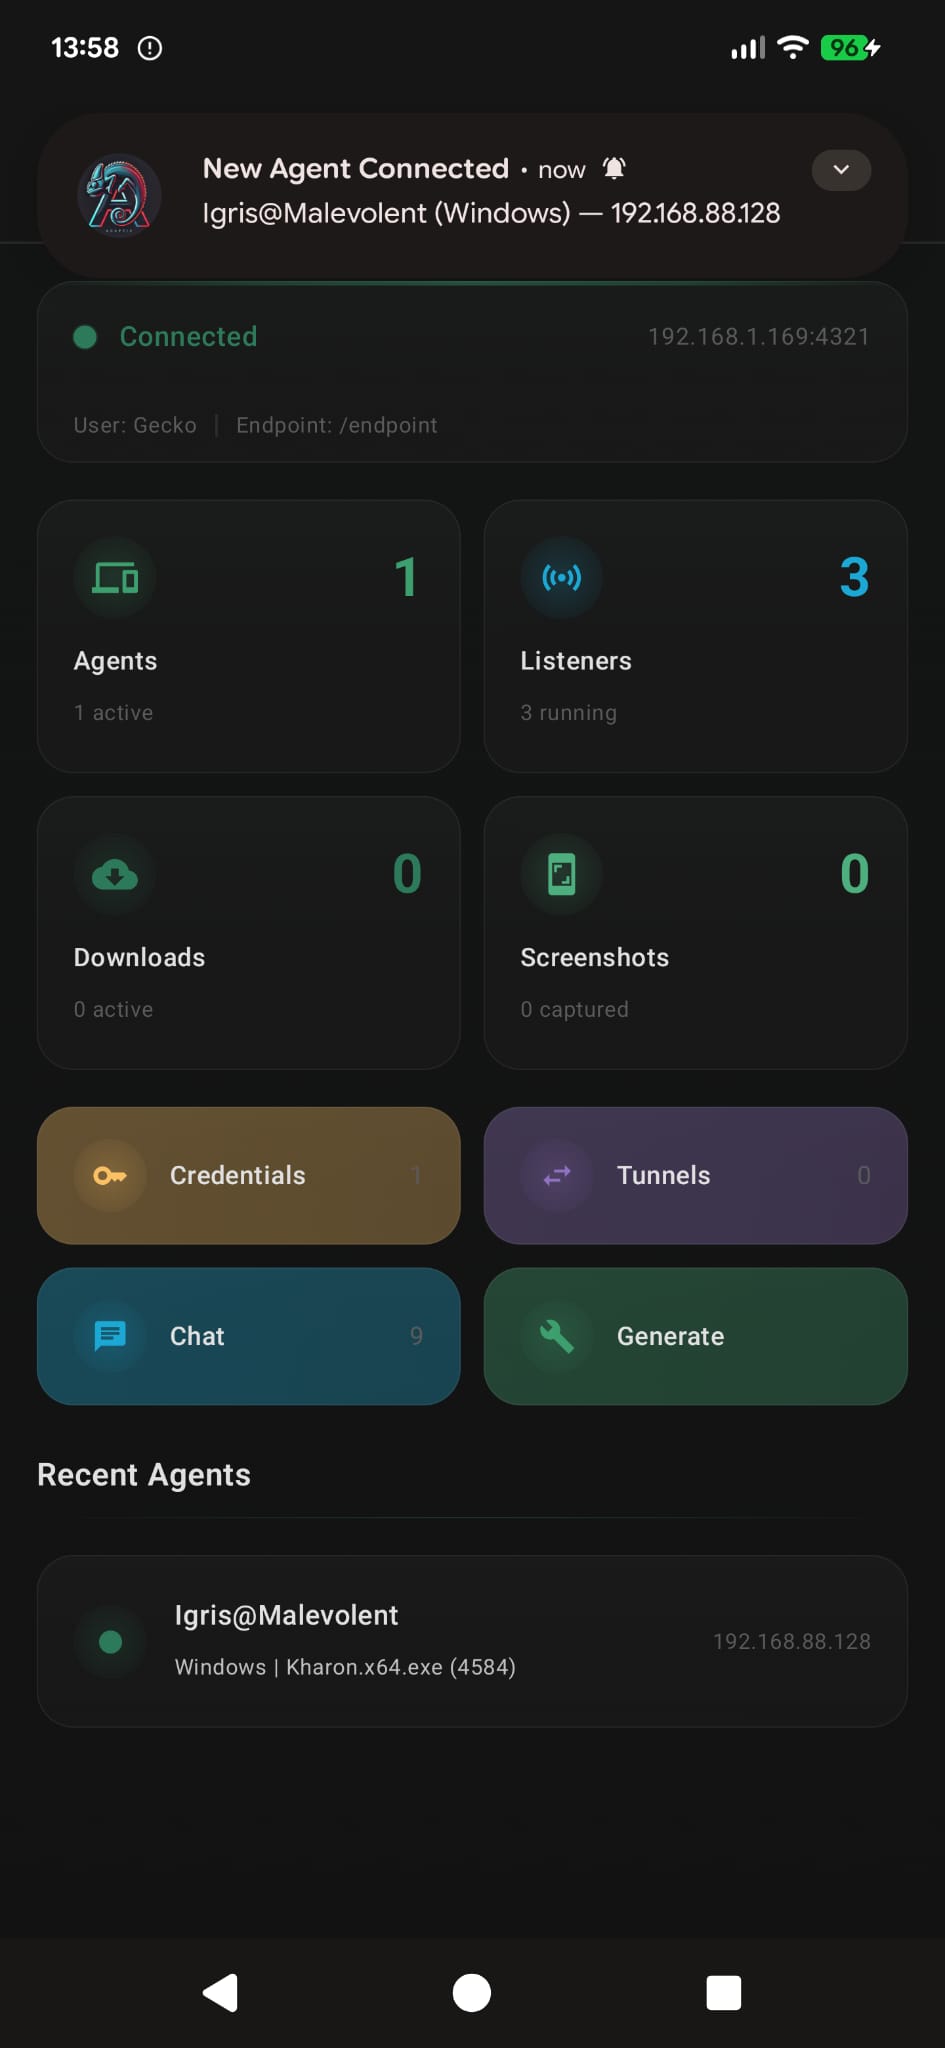 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 xiaobailovesstirring/cve-2025-48595-exploit
CVE-2025-48595 Android Framework Integer Overflow PoC - 优化版
 fevar54/cve-2025-48595-android-framework-integer-overflow-
PoC de CVE-2025-48595: desbordamiento de entero en multiples ubicaciones del Framework de Android.
 darioi/droidcarve
Android Reverse Engineering Framework