

Wallbreak
 supersonic/wallbreak
Exploit app for CVE-2021-39670 and CVE-2021-39690, two permanent denial-of-service vulnerabilities in Android's wallpaper system
android-securityeducationexploitation+2
16
supersonic/wallbreakExploit app for CVE-2021-39670 and CVE-2021-39690, two permanent denial-of-service vulnerabilities in Android's wallpaper system
 tamirzb/cve-2019-14041
PoC code for CVE-2019-14041
 ikoz/certpinningvulnerableokhttp
OkHttp sample app vulnerable to CVE-2016-2402
 pro-me3us/cve_2022_38181_raven
CVE-2022-38181 POC for FireTV 2nd gen Cube (raven)
 fusiondrive/cve-2026-43499-s24u
CVE-2026-43499 research port for Galaxy S24 Ultra SM-S928U1 DZF2 (COMPLETED)
 thomascannon/android-cve-2010-4804
Android Data Stealing Vulnerability
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
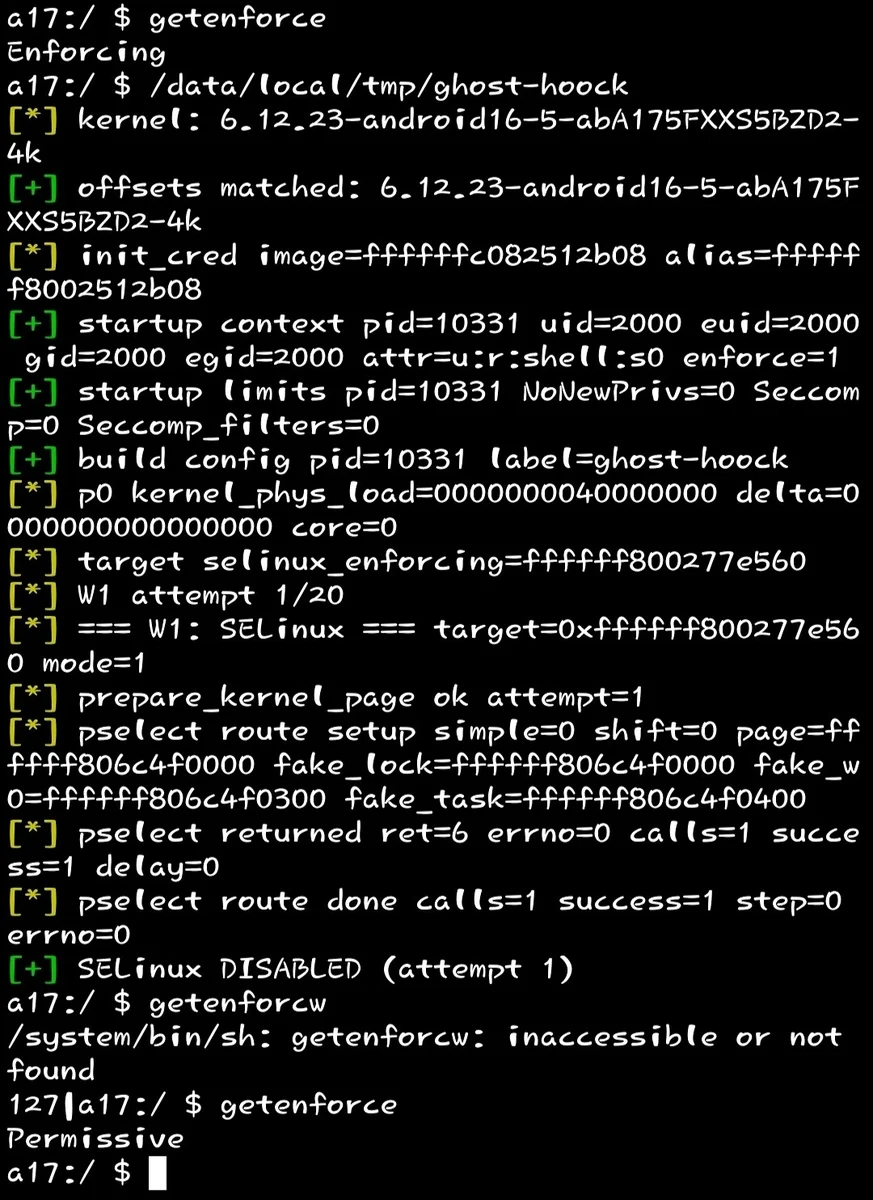 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 naheeju/poc-cve-2026-0073
Security research PoC for CVE-2026-0073: ADB authentication bypass verification
 vaginessa/cve-2020-0041-pixel-3a
Local privilege escalation exploit for Android Binder bug CVE-2020-0041 (Pixel 3a)
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 pro-me3us/cve_2022_38181_gazelle
CVE-2022-38181 POC for FireTV 3rd gen Cube (gazelle)
 szymonh/android-gadget
CVE-2022-20009 - Description and sample exploit for Android USB Gadgets
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
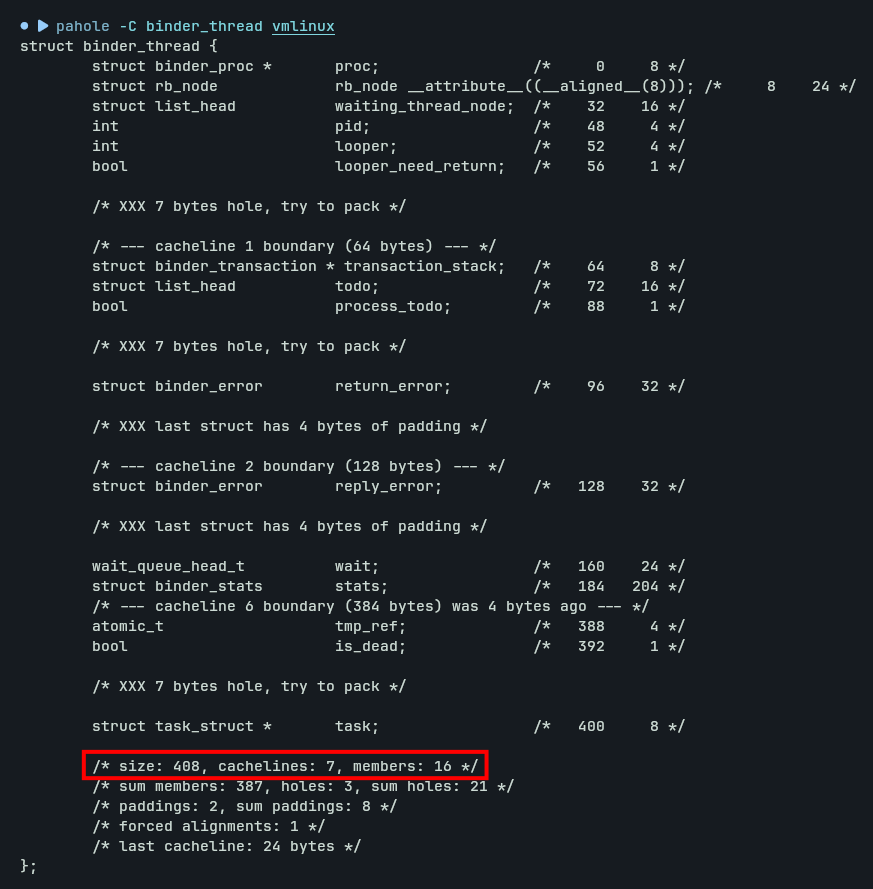 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 mouseos/aquos-r6-ghostlock
Temporary root exploit for Sharp AQUOS R6 A101SH S0029 using GhostLock CVE-2026-43499
 soralis0912/cve-2026-43499-warhol-root
Local privilege escalation exploit targeting CVE-2026-43499 for the Xiaomi 17T Pro (warhol) on Android 16 with MediaTek MT6993 SoC.