
ES-File-Explorer-Open-Port-Vulnerability---CVE-2019-6447
 sandarufdo/es-file-explorer-open-port-vulnerability---cve-2019-6447
ES File Explorer Open Port Vulnerability - CVE-2019-6447
android-securityexploitationinformation-gathering+2
sandarufdo/es-file-explorer-open-port-vulnerability---cve-2019-6447ES File Explorer Open Port Vulnerability - CVE-2019-6447
 nipund513/exploiting-uaf-by-ret2bpf-in-android-kernel-cve-2021-0399-
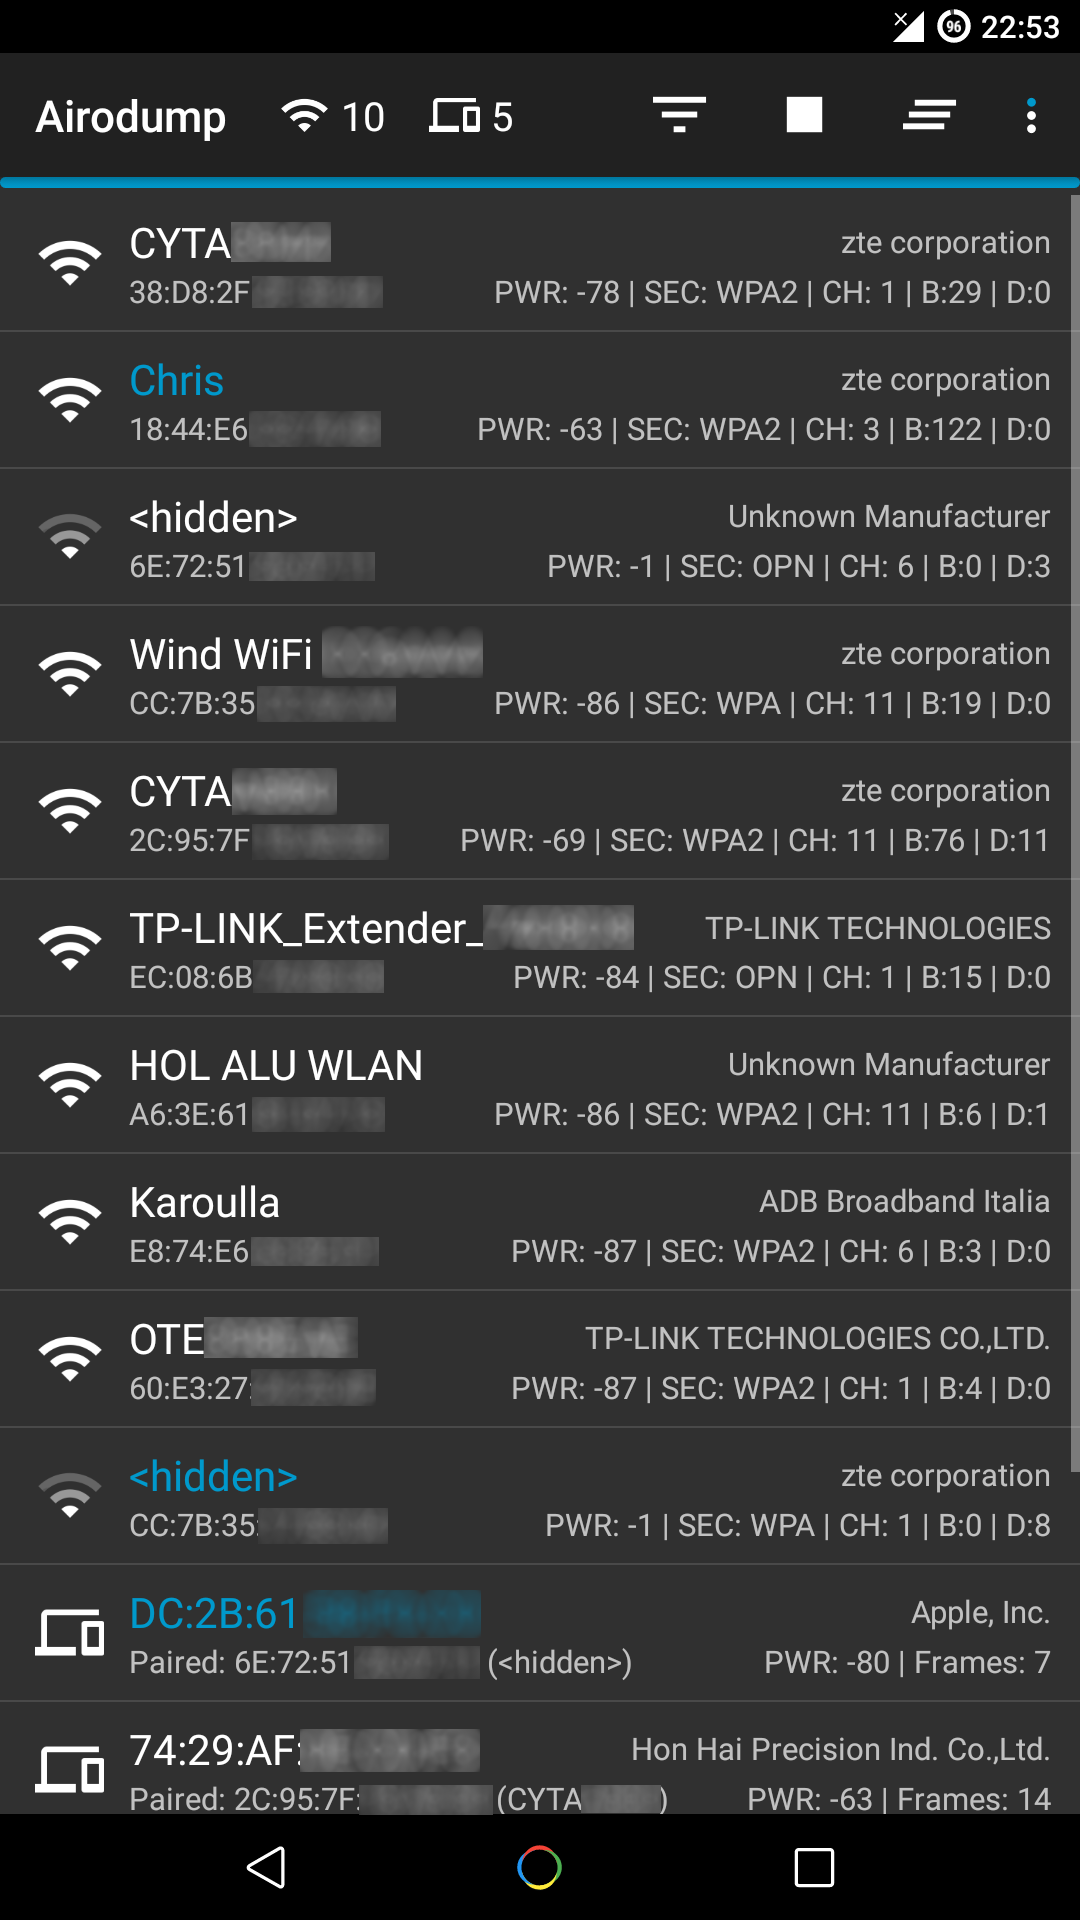 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
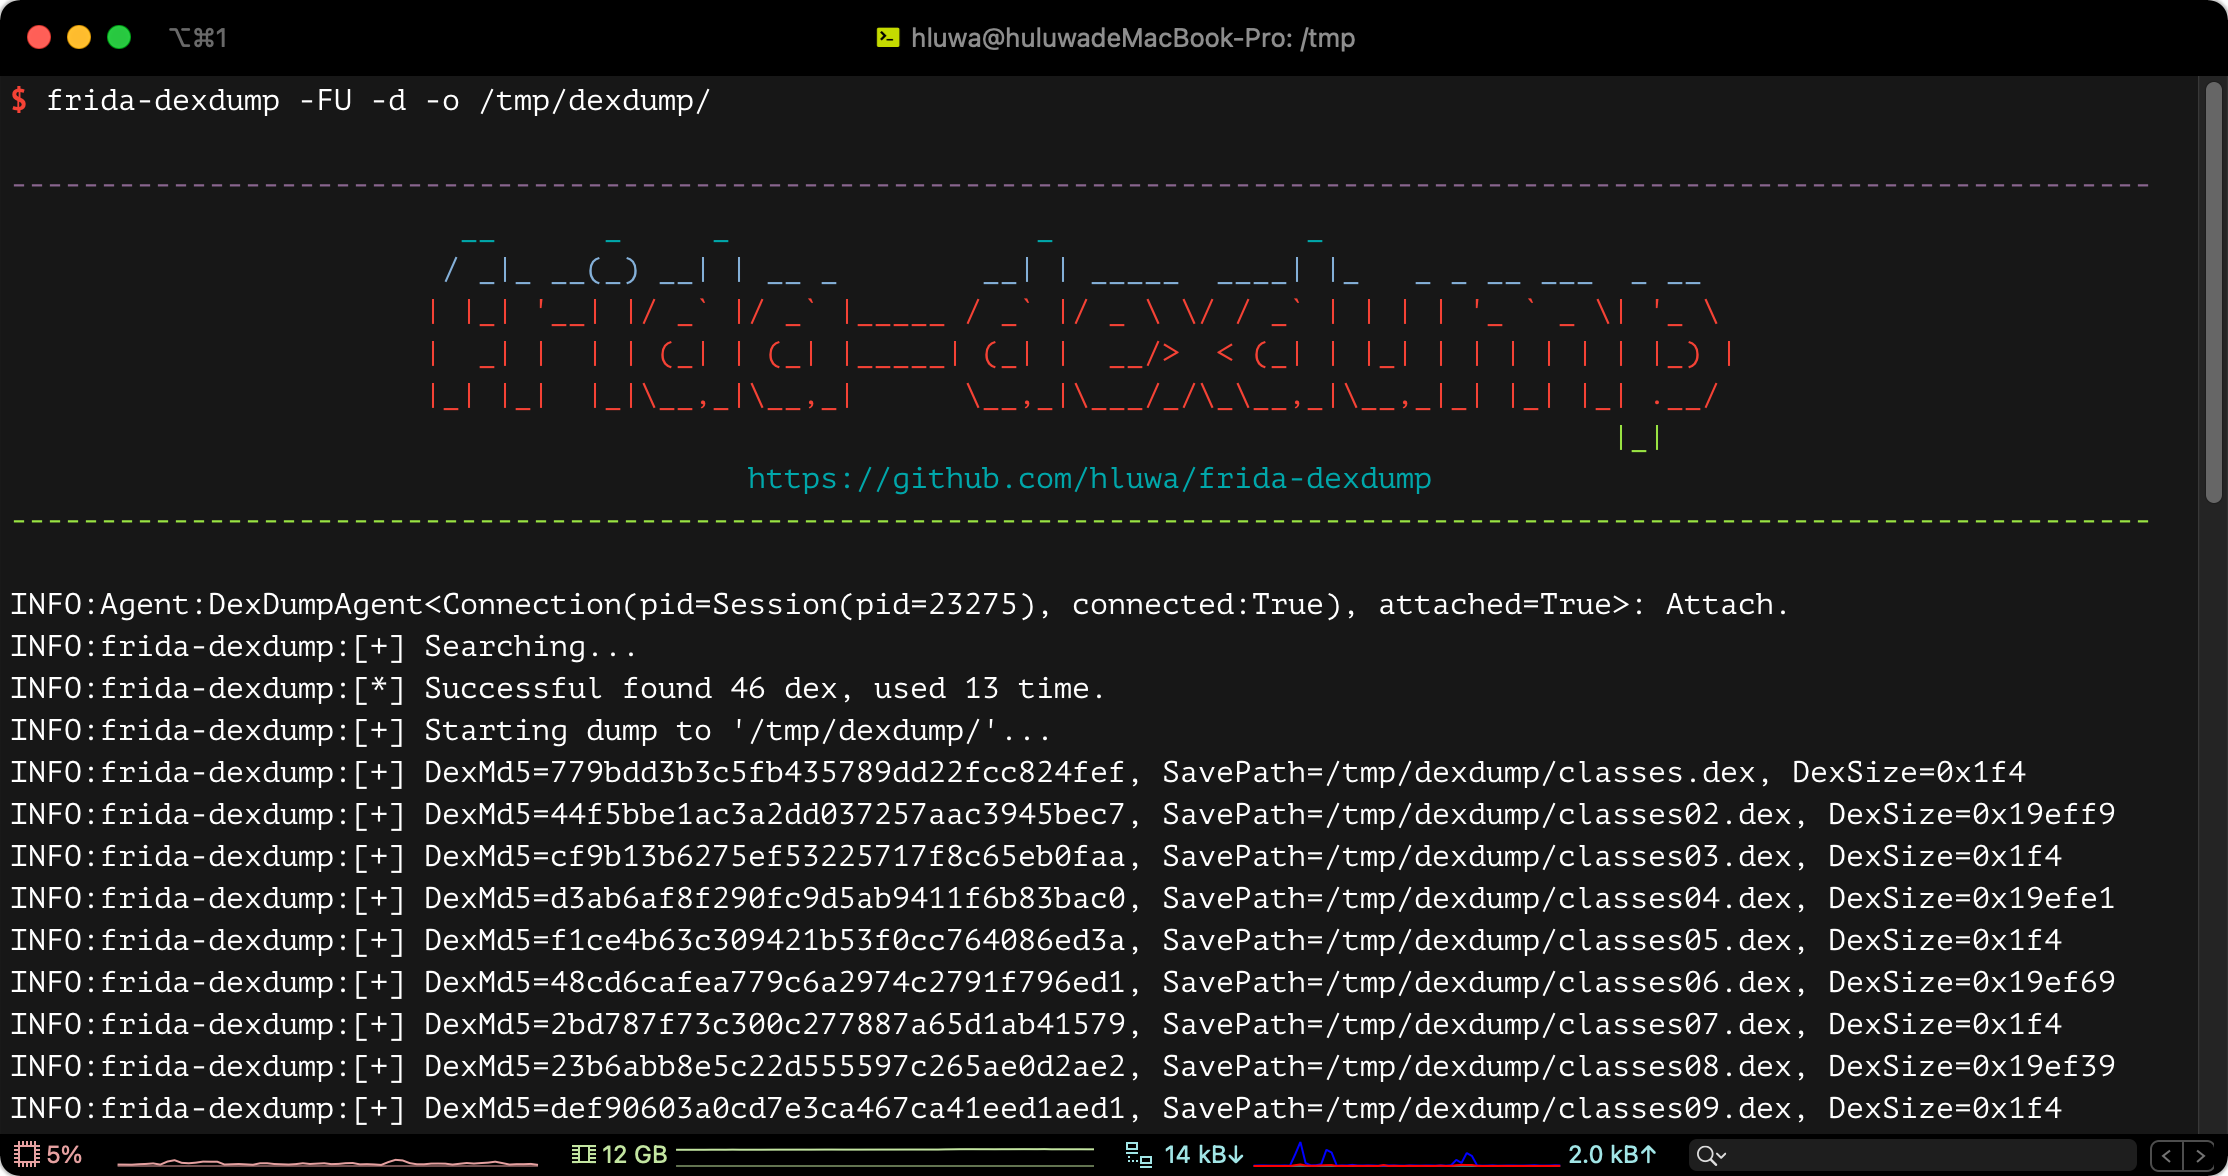 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
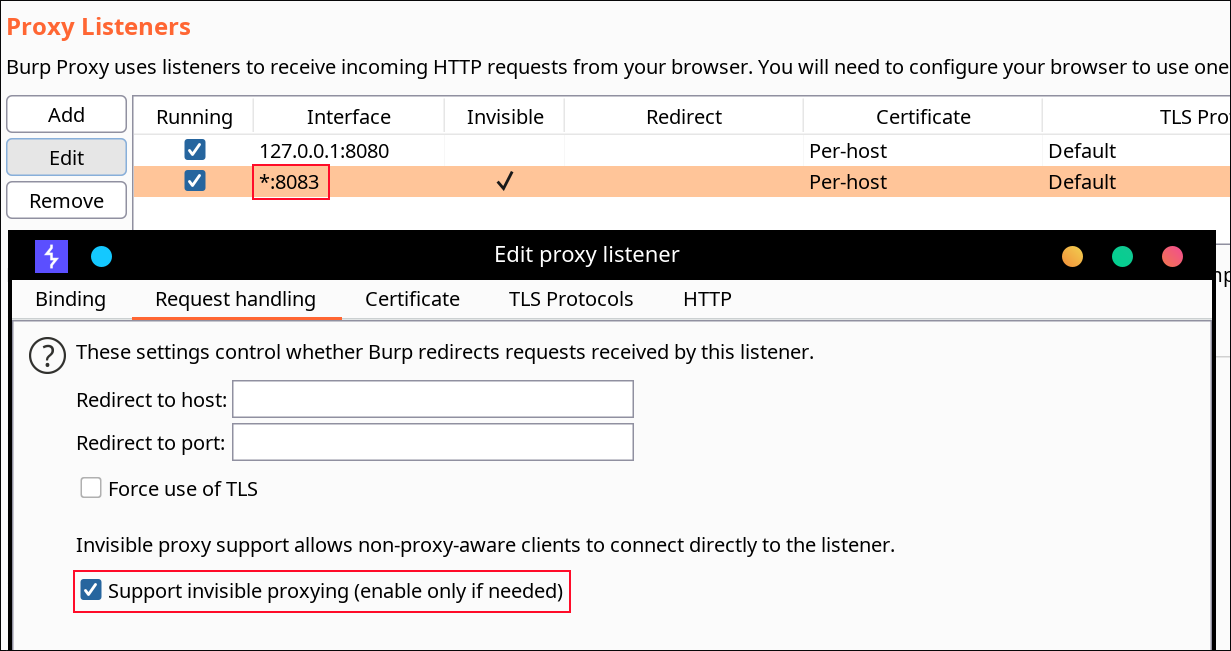 ptswarm/reflutter
Flutter Reverse Engineering Framework
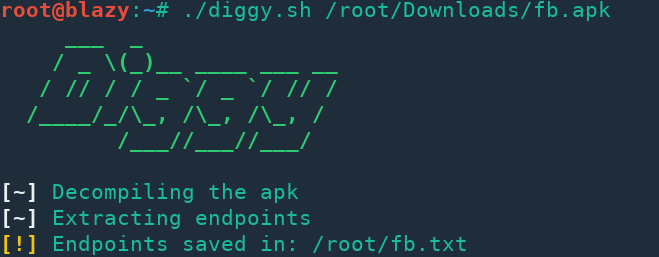 s0md3v/diggy
Extract endpoints from apk files.
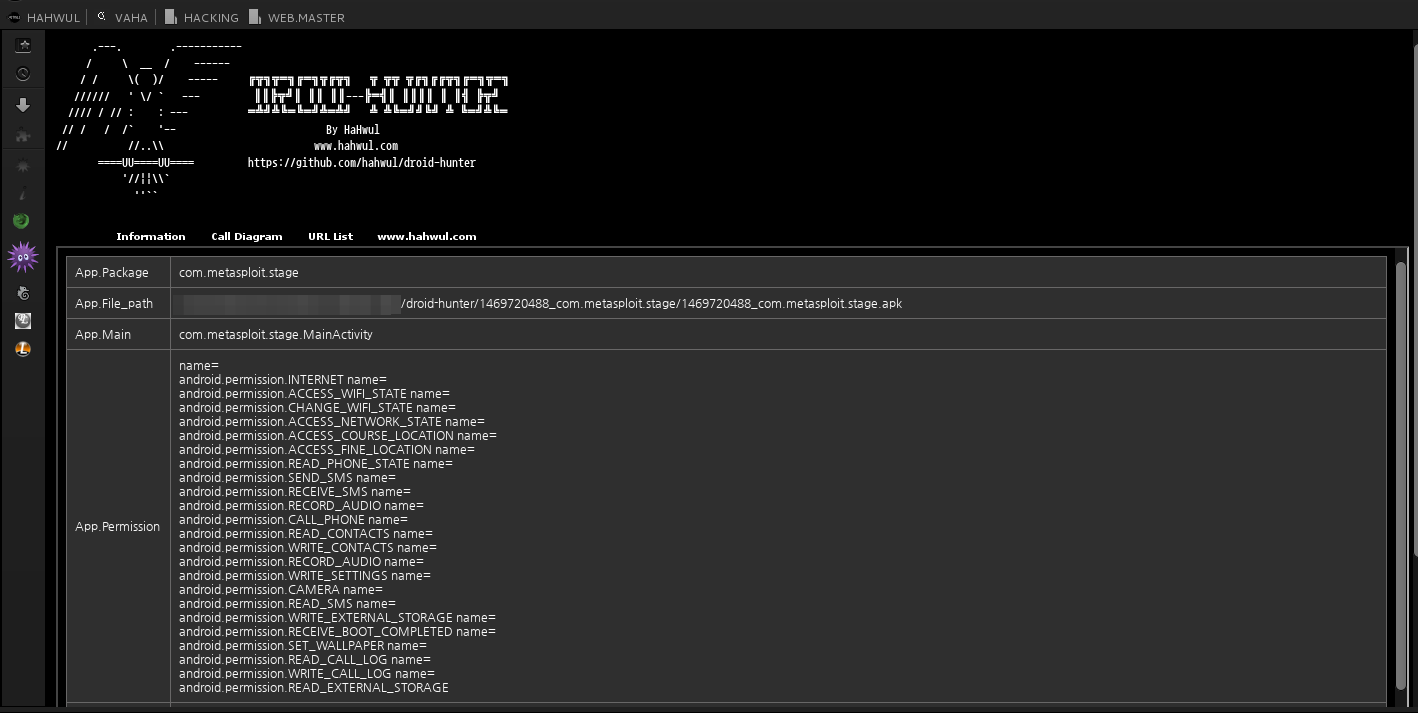 hahwul/droid-hunter
(deprecated) Android application vulnerability analysis and Android pentest tool
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 1ultimat3/badintent
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
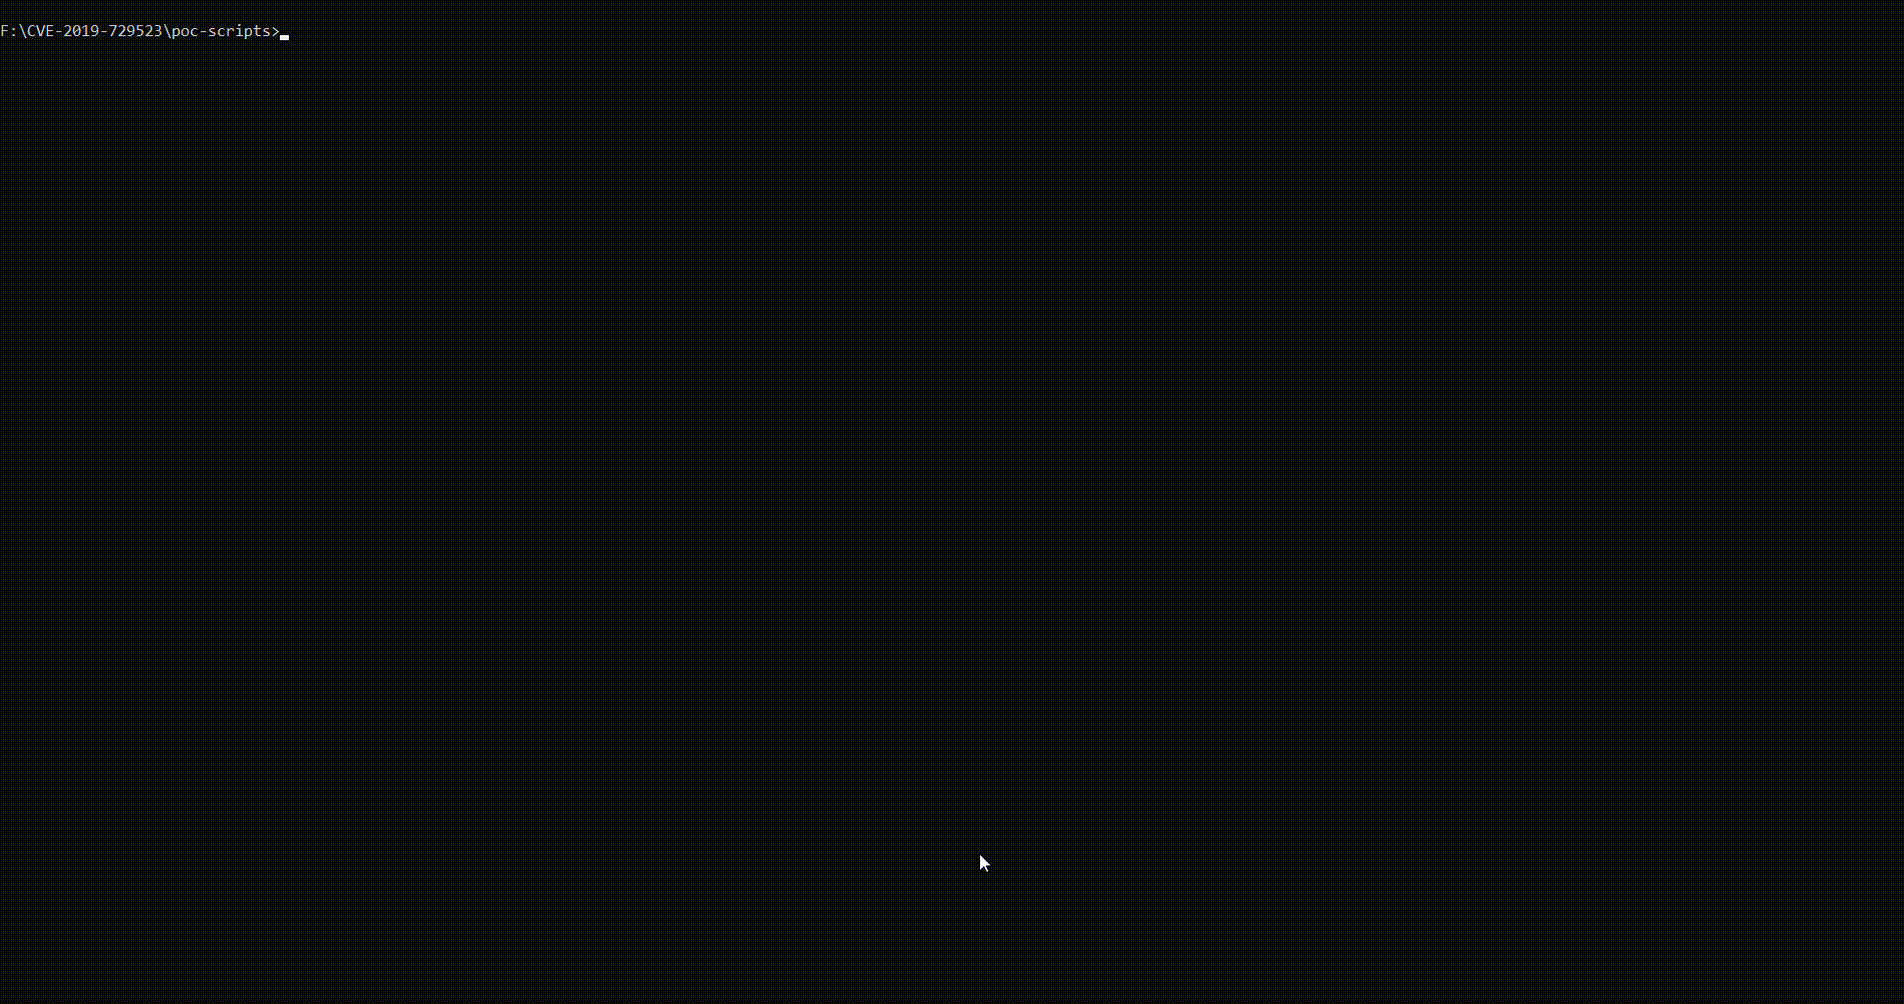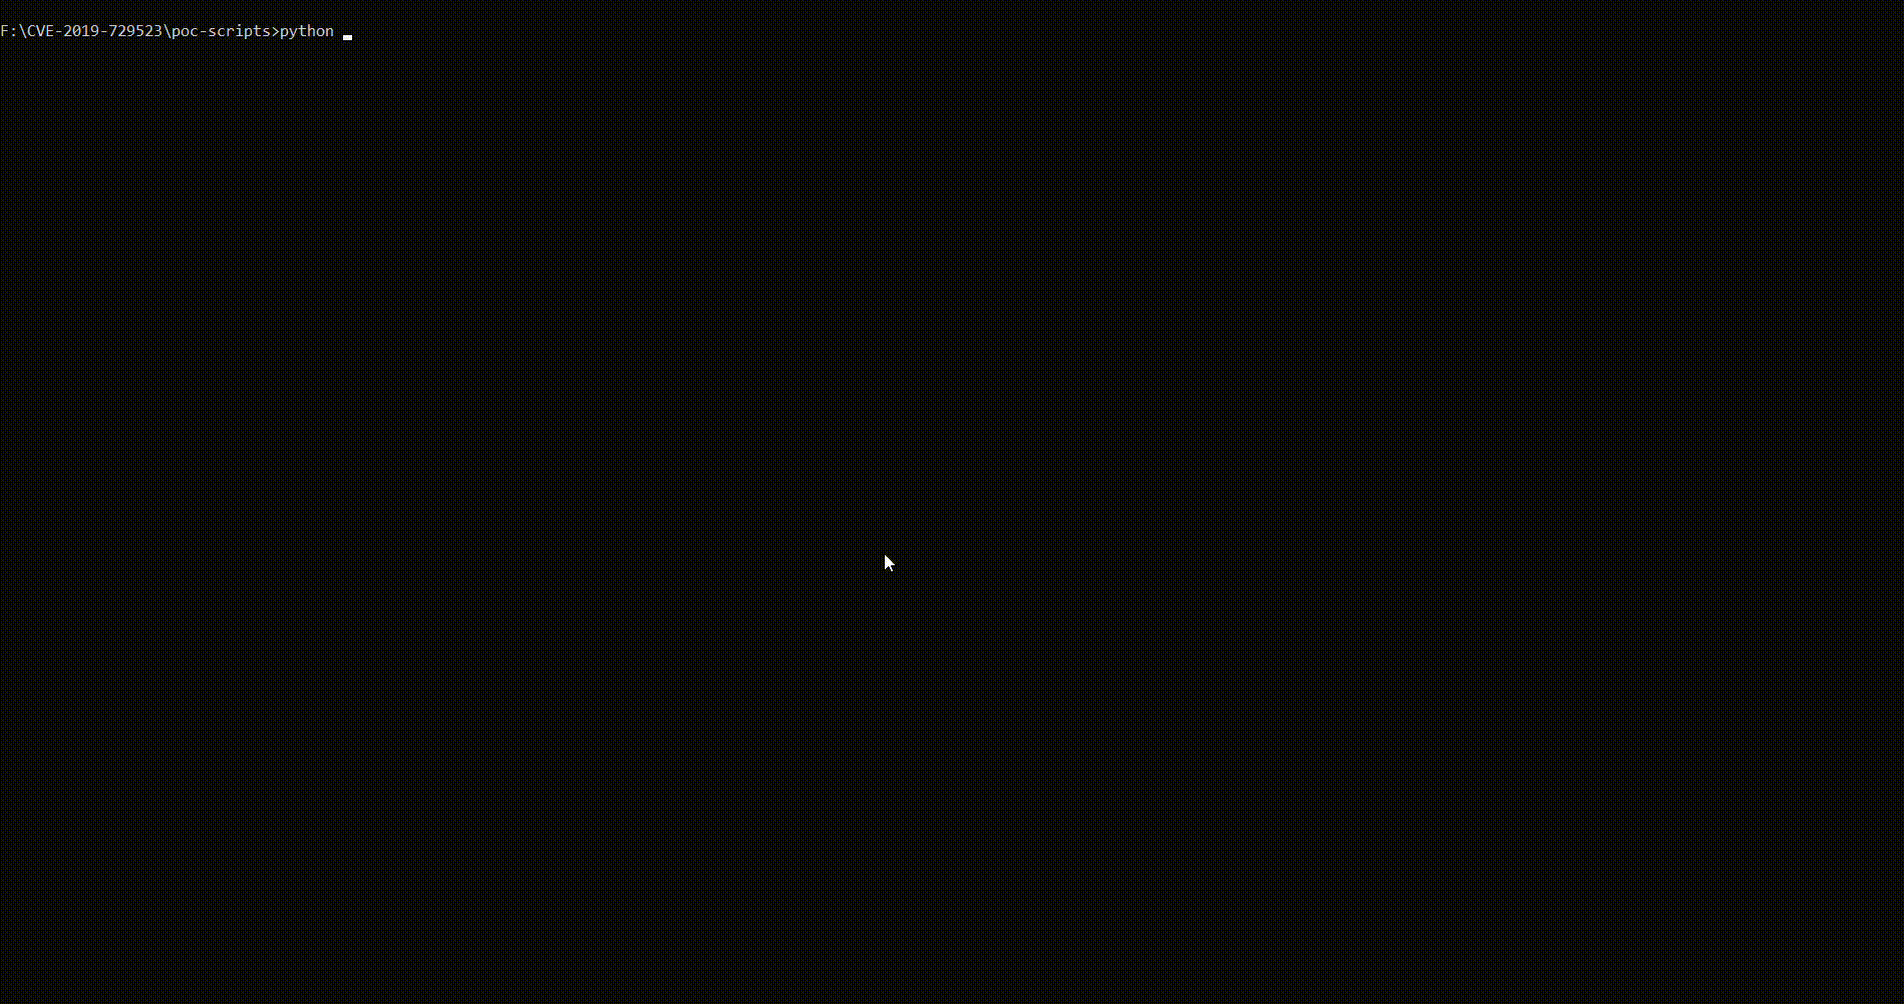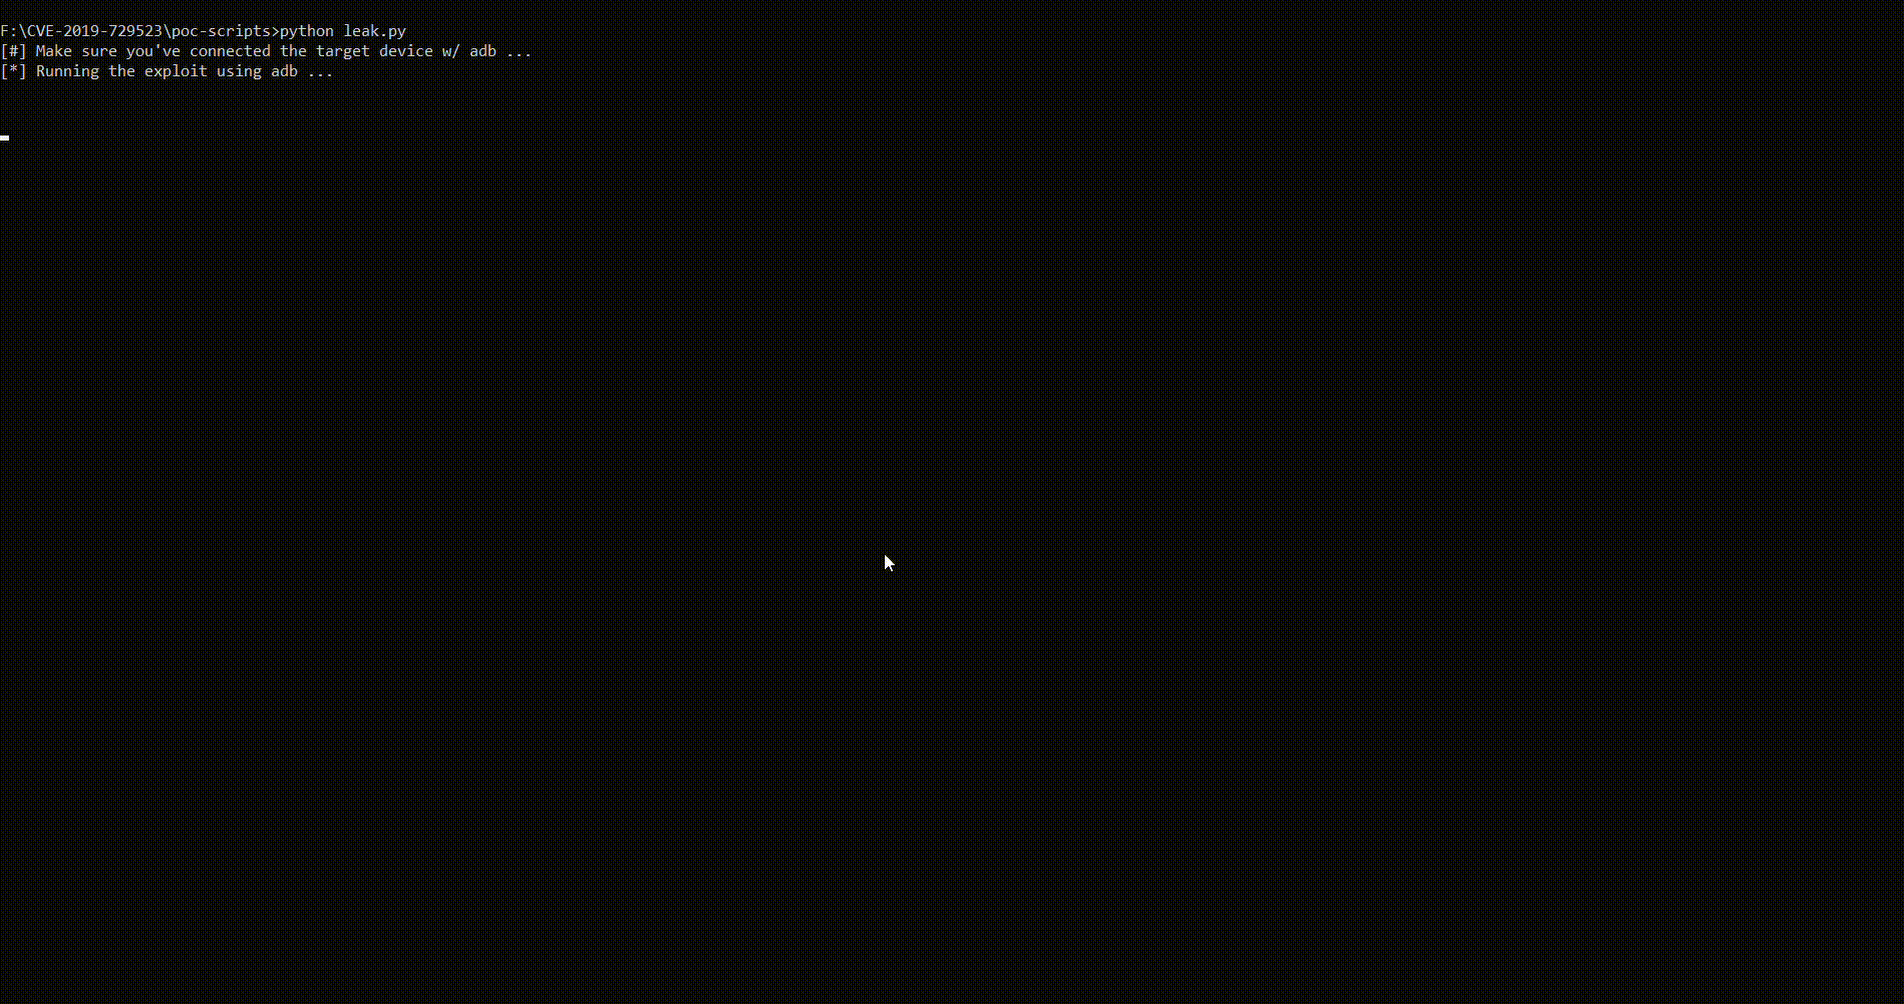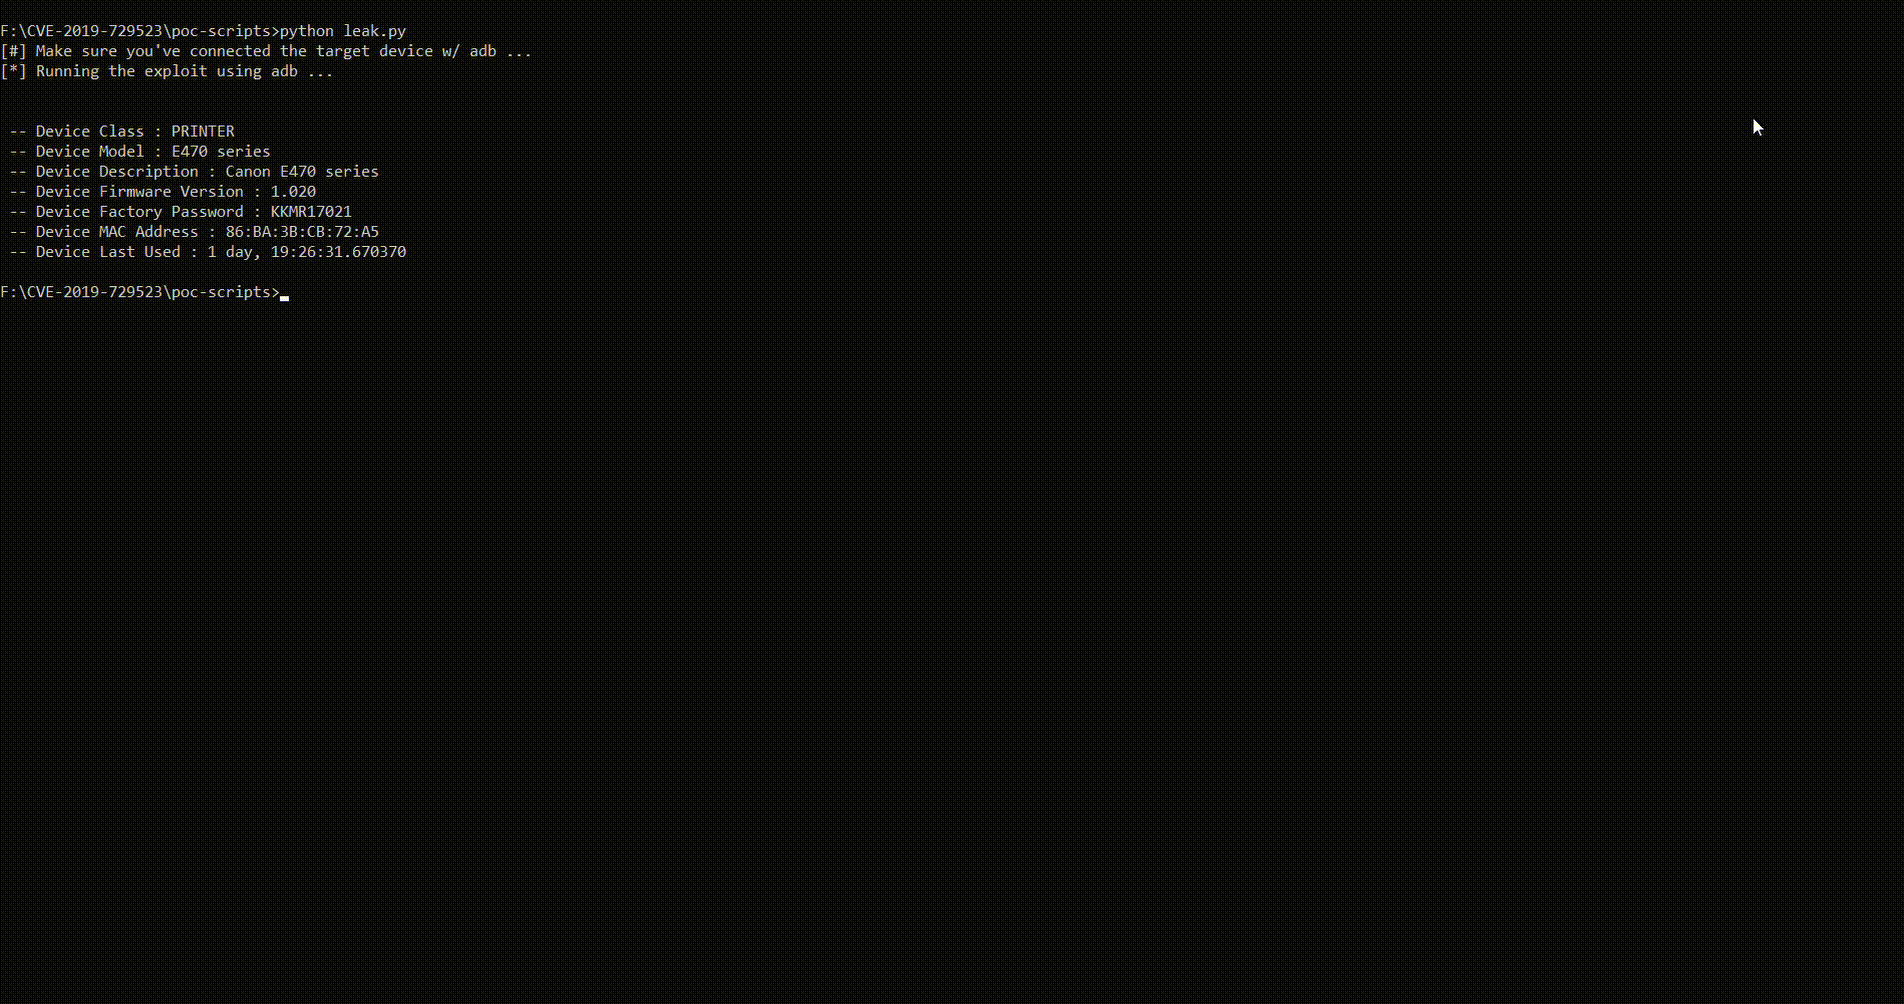 0x48piraj/cve-2019-14339
POC for CVE-2019-14339 Canon PRINT 2.5.5
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 pyyyc/honor-6.12.38-43499-research
Research repository documenting exploitation attempts of CVE-2026-43499 futex UAF on Honor YLP-W00 kernel 6.12.38, including PoC sources, kernel…
