
CVE-2025-48593
 ranasen-rat/cve-2025-48593
Technical analysis of a critical zero-click remote code execution vulnerability (CVE-2025-48593) affecting Android 13-16, detailing root cause,…
android-securitybinary-exploitationeducation+4
5
ranasen-rat/cve-2025-48593Technical analysis of a critical zero-click remote code execution vulnerability (CVE-2025-48593) affecting Android 13-16, detailing root cause,…
 devtint/cve-2026-0073
Weaponized proof-of-concept for CVE-2026-0073, an Android adbd authentication bypass enabling zero-click remote root access via Wireless ADB, with…
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 m4g1xx/cve-2024-36971
Poc for CVE-2024-36971
 kaitokidc500/cve-2024-23700-c2-server
Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 acloudinthebluesky/cve-2019-6447-es-file-explorer
Technical analysis and safety-conscious research harness for CVE-2019-6447 in ES File Explorer for Android
 huaguiqi/asus-i005-cve-2026-43499
CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked
 chirantar7004/android-passive-location-tracker
Location tracking app without location permissions! Makes use of CVE-2018-15835 which makes use of Android OS information leakage.
 jordelmir/elysium-vanguard-sentinel-audit
The official Sentinel Edition v7.11 - Hypervisor Detection & Kernel Memory Audit Suite for Honor Magic V2. Investigating CVE-2025-38352 and EL2 RKP…
 bobikl/cve-2026-43499-t807d
Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…
 sentinel-aidefense/cve-2026-0163-exp
CVE-2026-0163 Exploit
 happy0717/cve-2023-27703
CVE-2023-27703 An Android version of pikpak version V1.29.2 element debugging interface leakage vulnerability
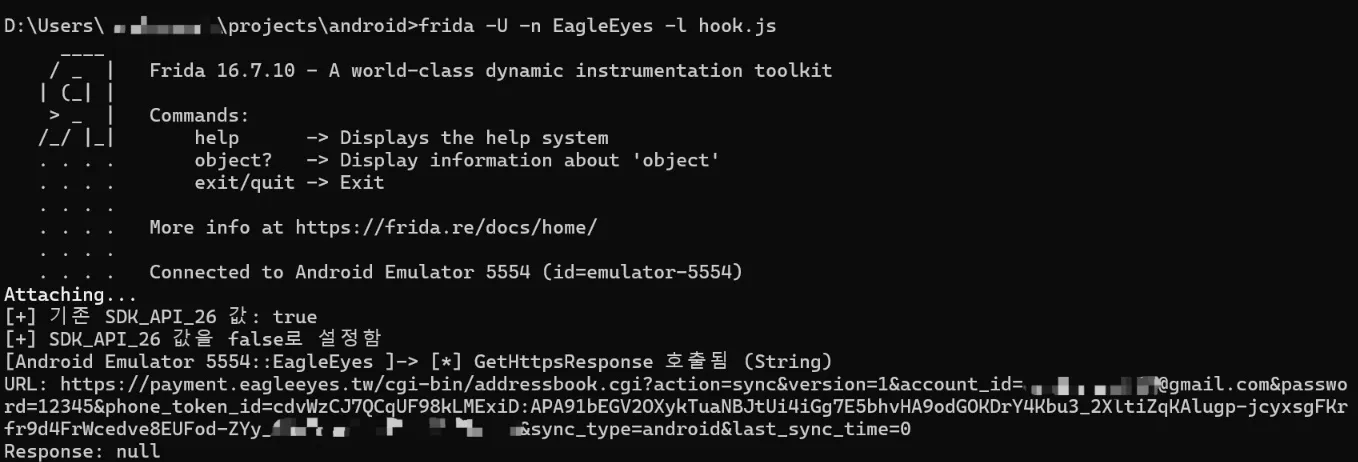 shinycolumn/cve-2025-46408
Improper Hostname Verification in EagleEyes Lite Android Application
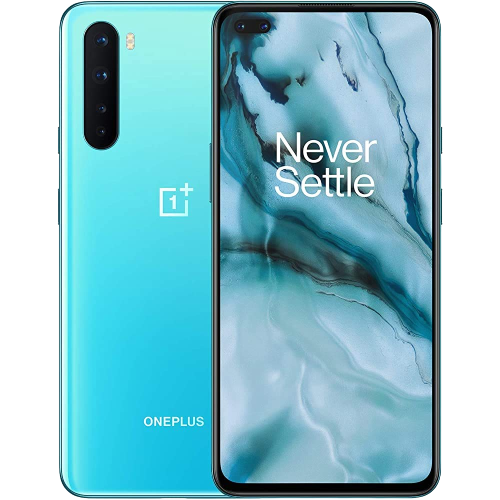 kimocoder/android_kernel_oneplus_avicii
OnePlus Nord (avicii) NeverSettle Kernel Source
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…