

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 bmax121/apatch
The patching of Android kernel and Android system
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
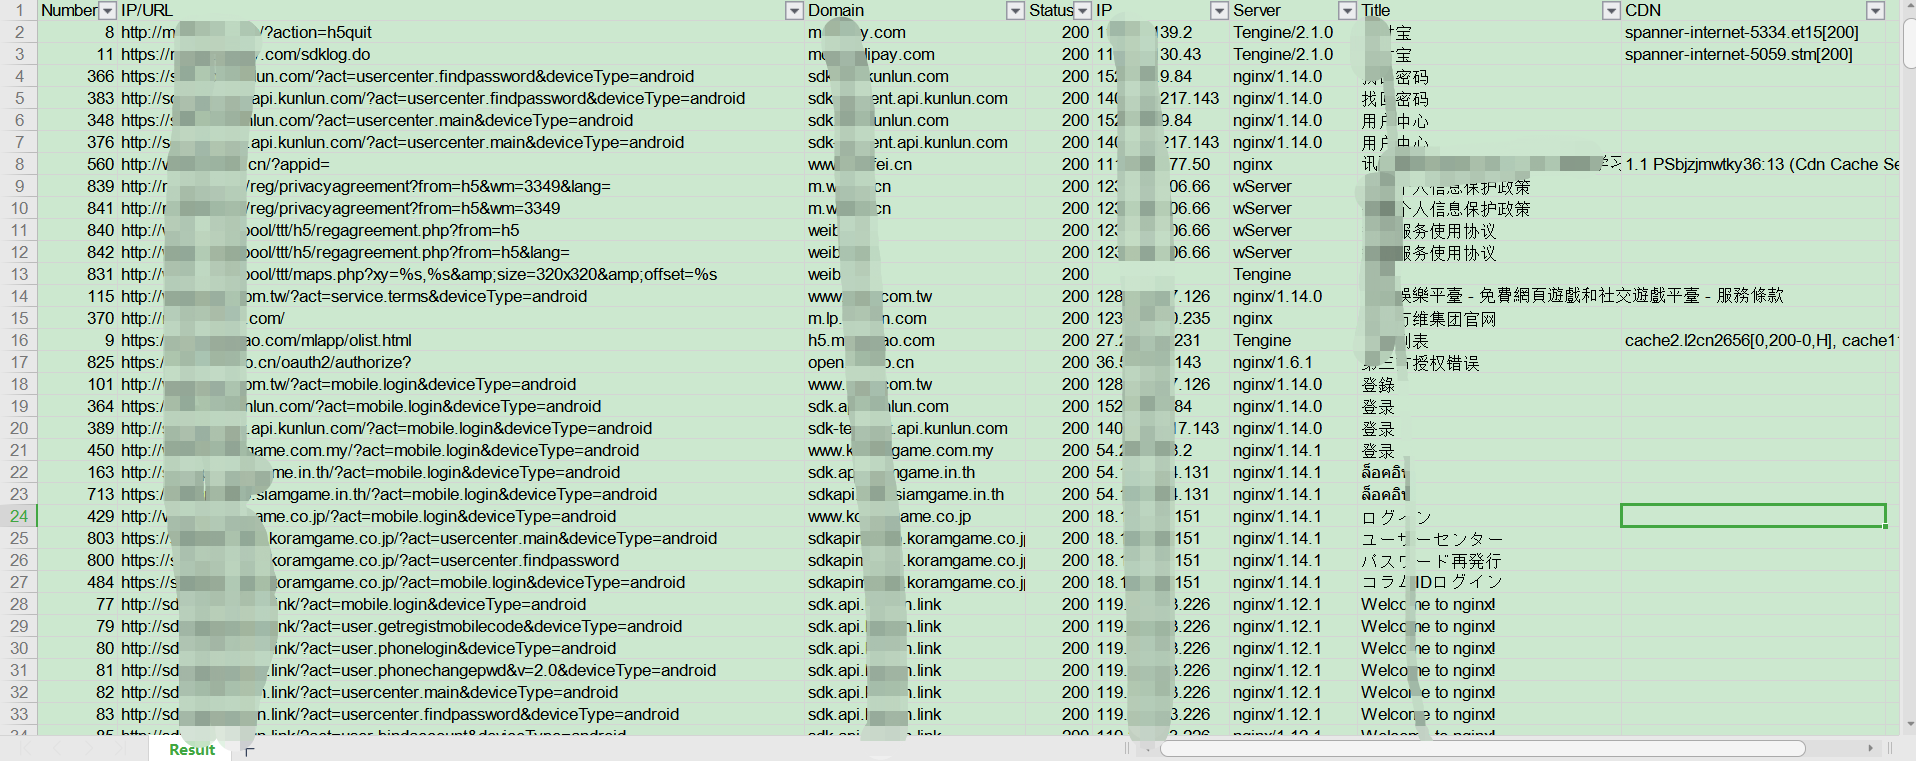 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 sultanahamer/opencontacts
Android contact manager that stores contacts in an isolated database, preventing other apps from accessing them. Provides call log and caller ID…
 frida/frida
Main repo for hosting release binaries
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 prey/prey-android-client
Android client for Prey: reliable device tracking and security tool