
ecapture
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
android-securitydatabase-securitydynamic-analysis-sandboxing+3
15.5k
gojue/ecaptureCapturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
 droid-ash/finalrun-agent
AI-driven CLI for testing Android and iOS apps using natural language. Generates, runs, and fixes end-to-end tests on emulators/simulators with…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 sloden1977-lang/root-zte-x1001
Magisk root guide for ZTE Blade X1001 (Android 15, Unisoc UMS9230) using CVE-2022-38694 exploit. Contributions and screenshots welcome.
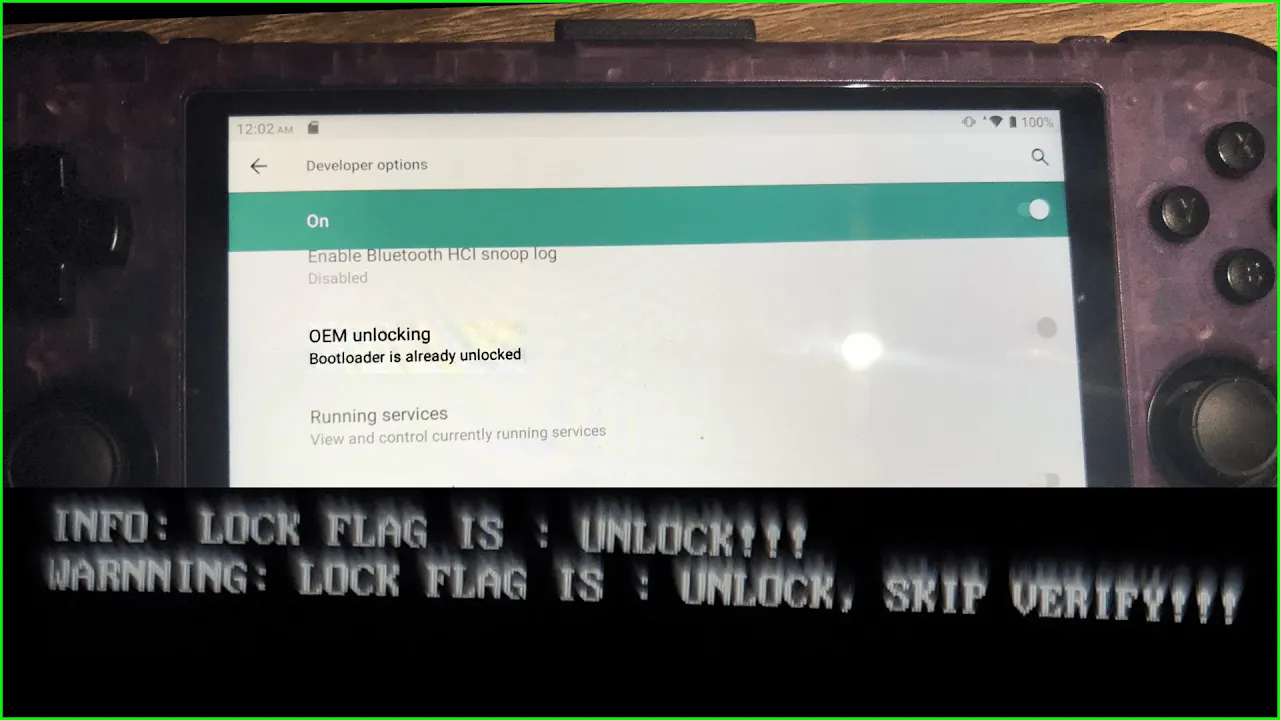 seriousattempts/bootloader_unlock_retroid_pocket_3plus
Bootloader unlock using CVE-2022-38694 for Retroid Pocket 3+
 r0rt1z2/automatedroot
Root your MediaTek device with CVE-2020-0069
 androidmalware/android_hid
Use Android as Rubber Ducky against another Android device