

r2frida
 nowsecure/r2frida
Radare2 and Frida better together.
android-securitybinary-analysisdebuggers+8
nowsecure/r2fridaRadare2 and Frida better together.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
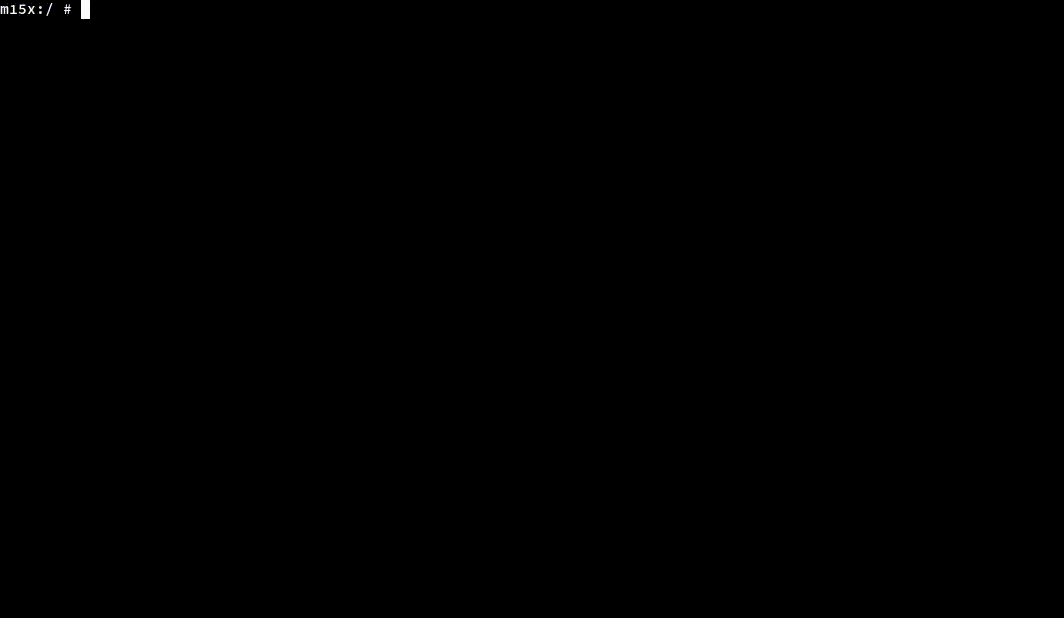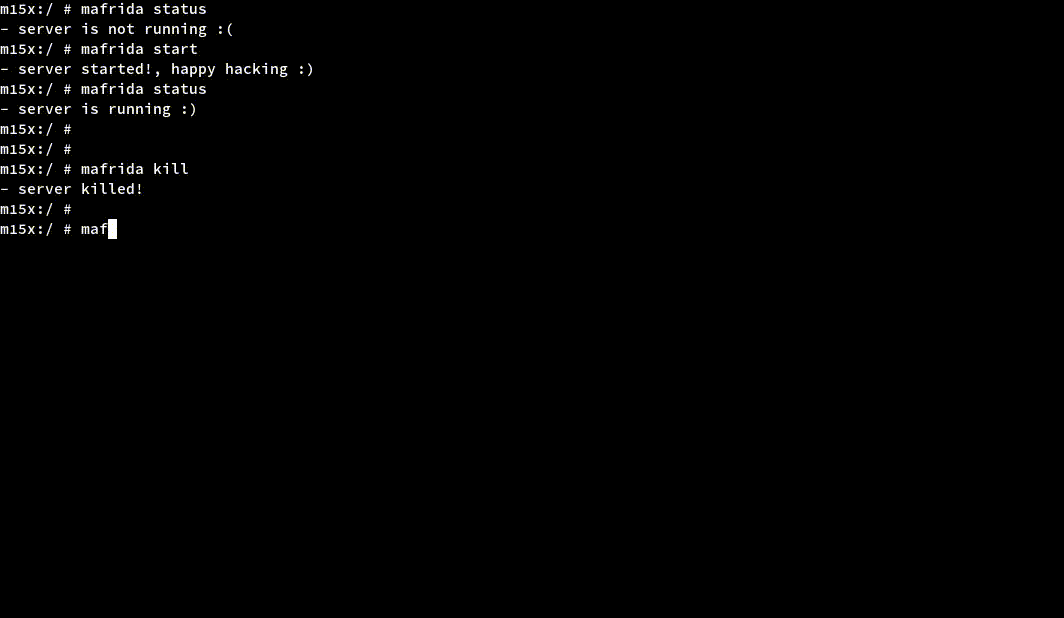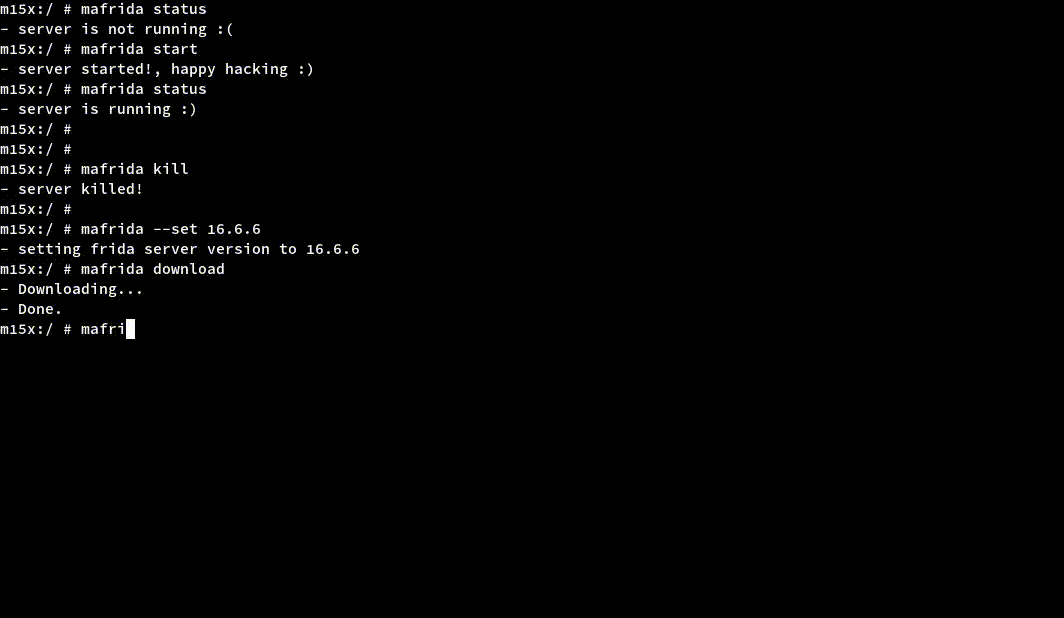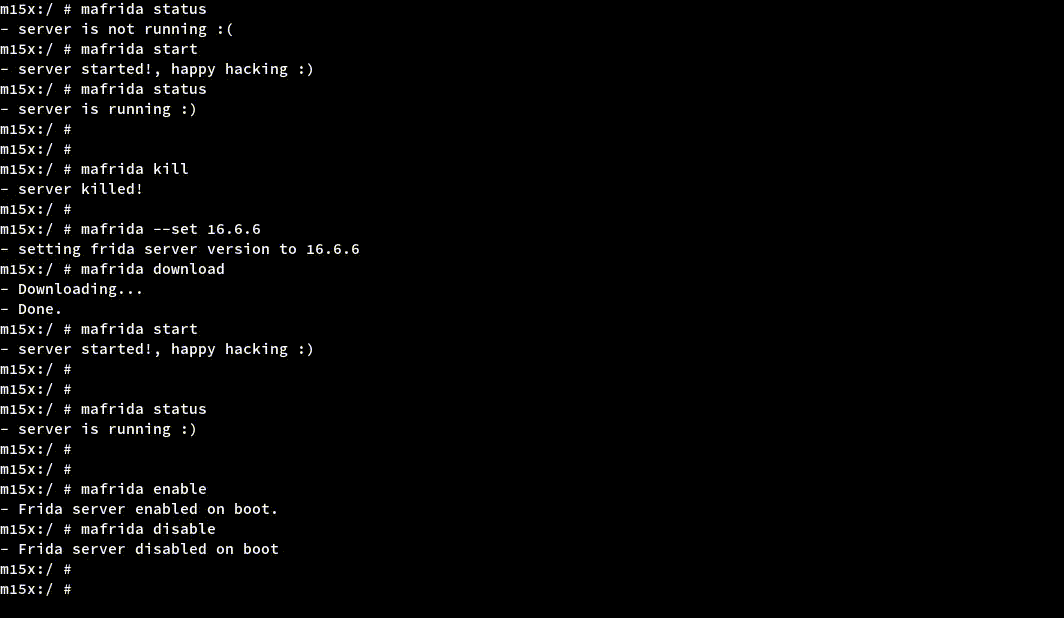 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
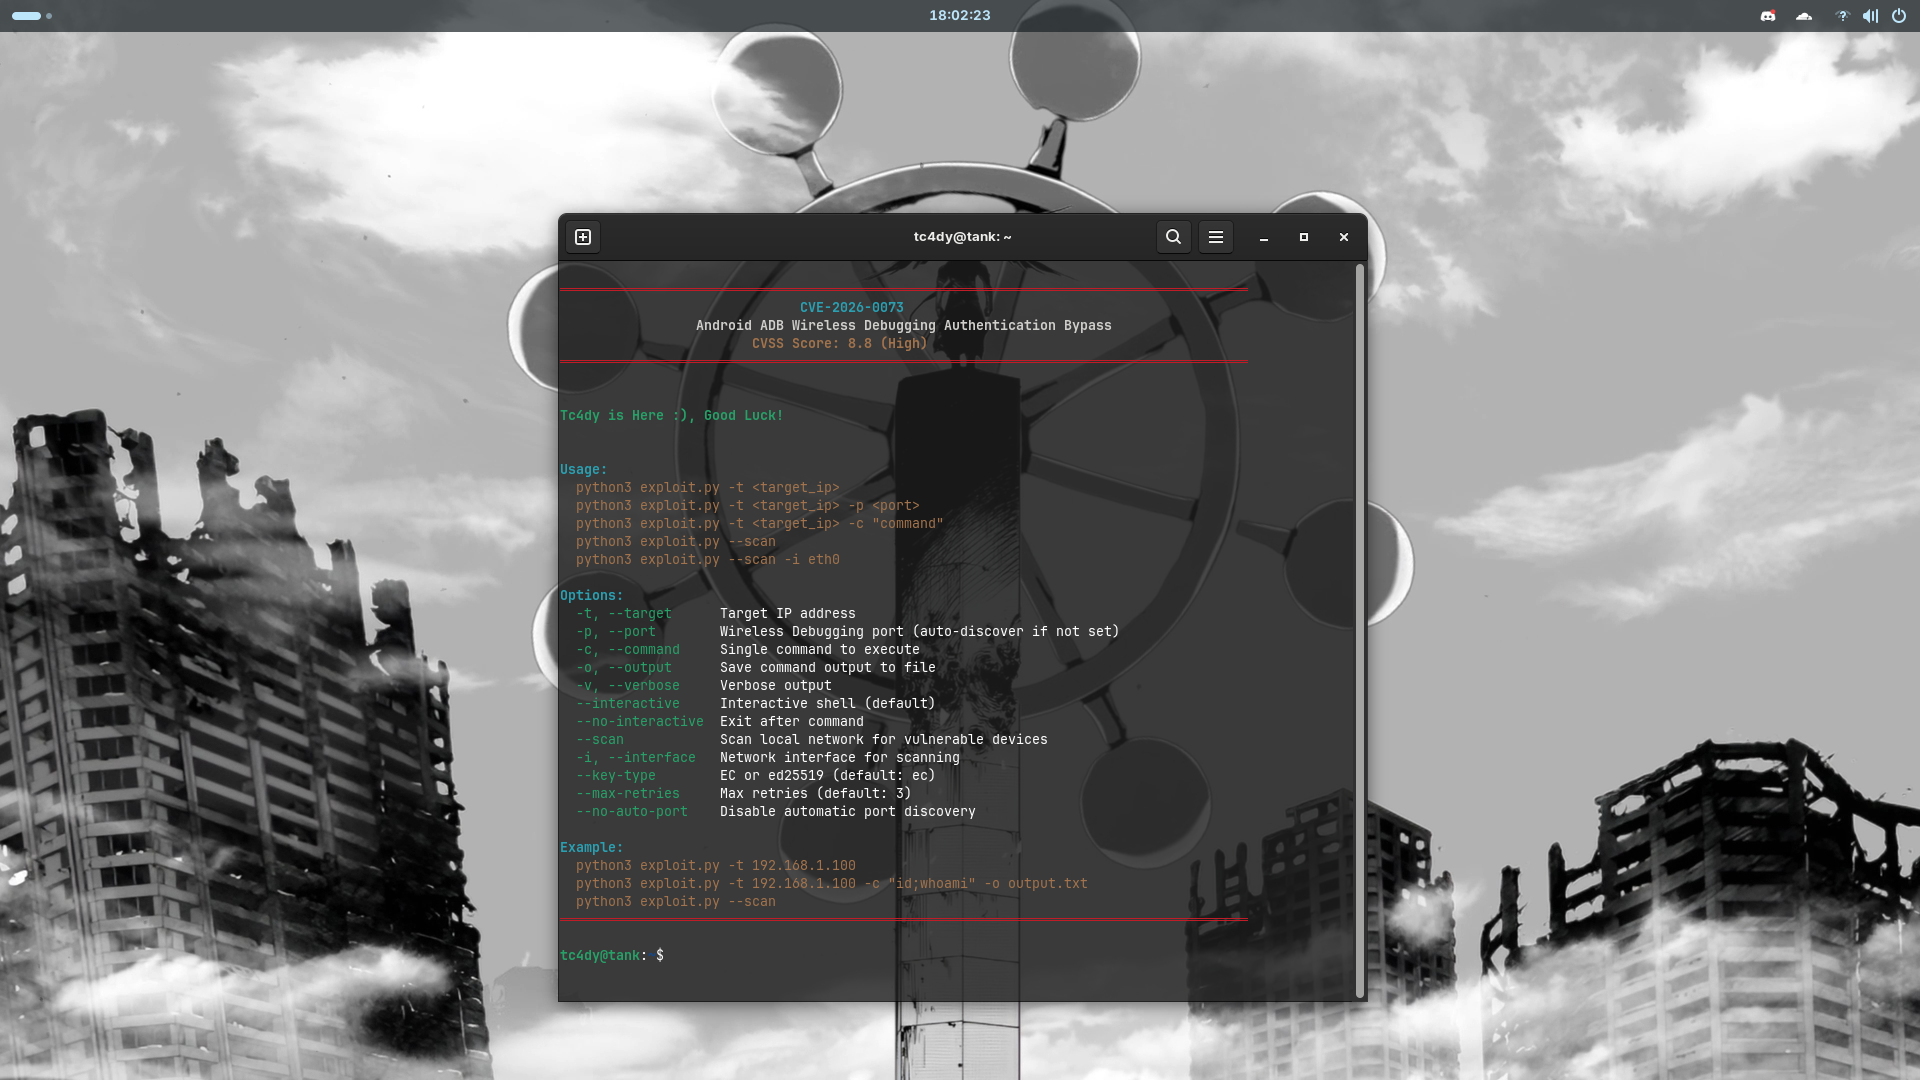 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 kaitokidc500/cve-2024-23700-c2-server
Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700
 hunt-benito/samsung-bixby-command-execution-cve-2026-21055-improper-component-export
Proof-of-concept exploit for CVE-2026-21055 demonstrating arbitrary command execution via improperly exported Android components in Samsung Bixby.…
 vikramaditya015/samsung-android-lpe
Poc for CVE-2026-20980, CVE-2026-20981, CVE-2026-20982
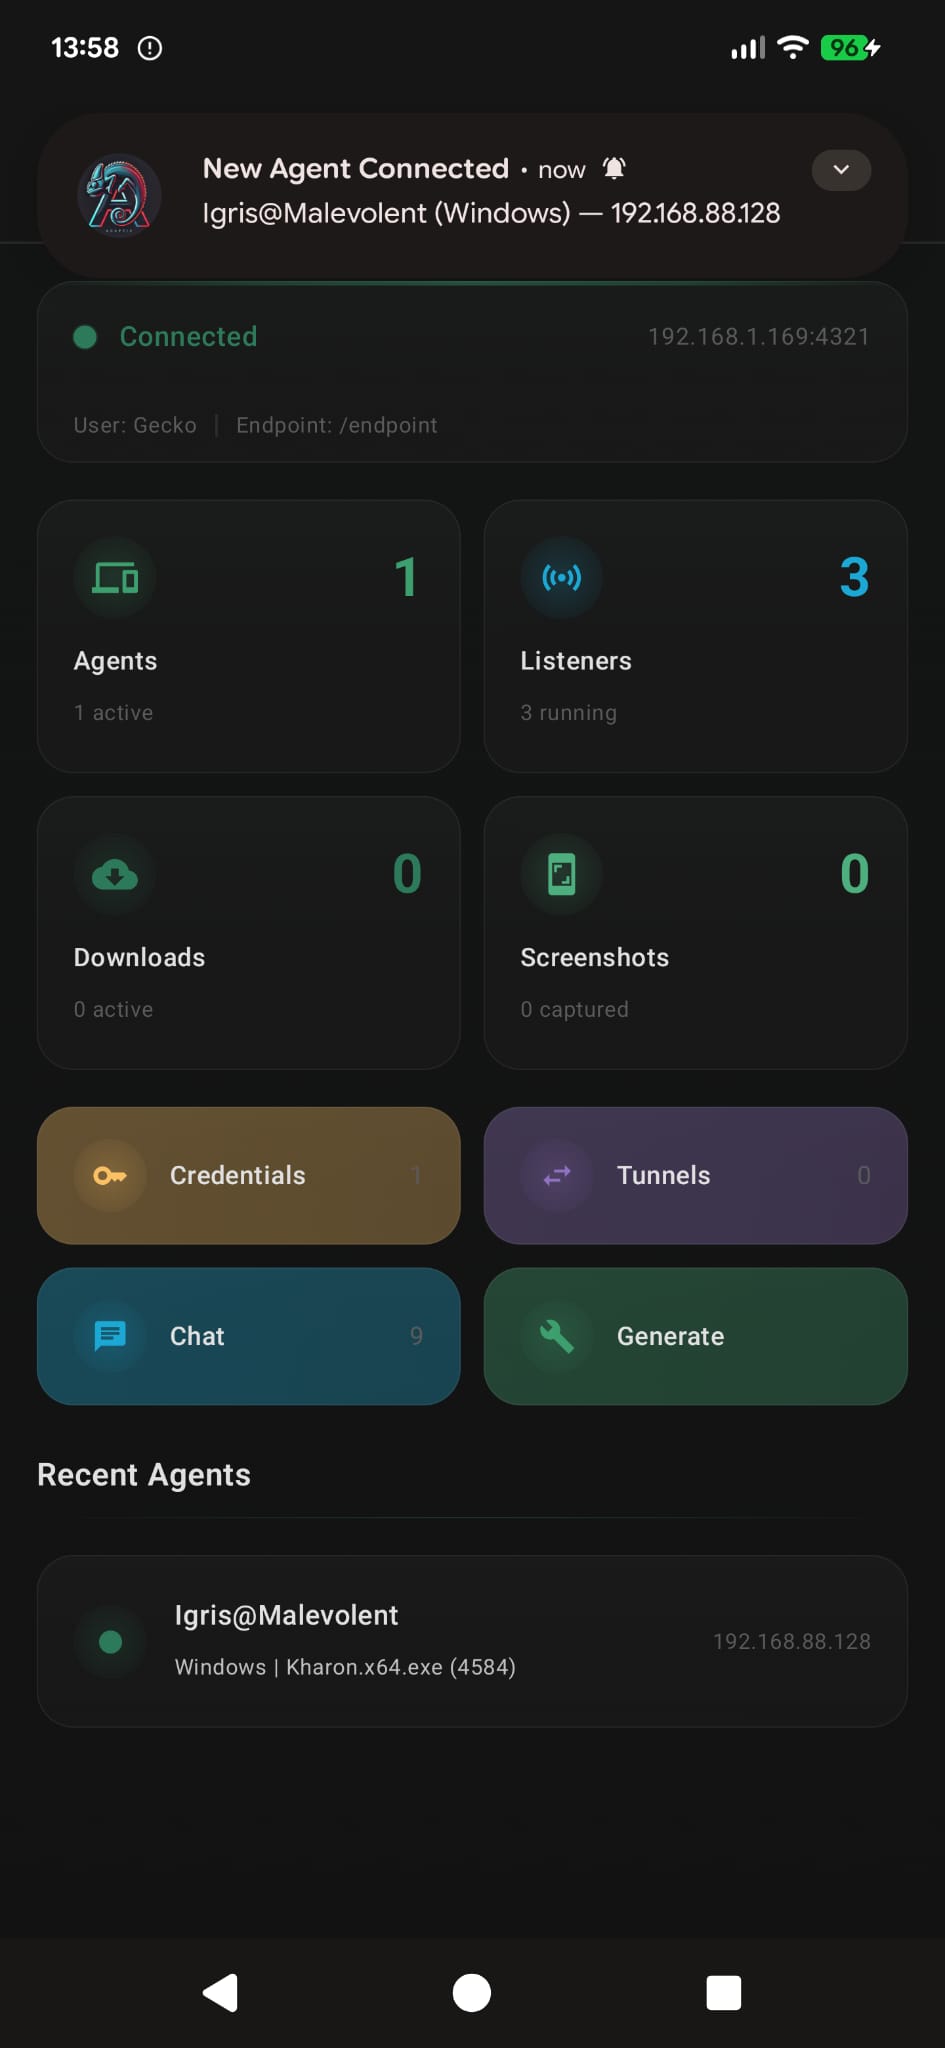 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
 kalibb/cve-2024-31317-deployer
Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 hackerronin/cve-2024-0044
a vulnerability affecting Android version 12 & 13
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…