CVE-2026-0073-Android-ADBD-bypass-POC

CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…

CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…

Android media framework vulnerability fix for CVE-2021-0509, addressing a use-after-free in audio flinger to prevent local privilege escalation.

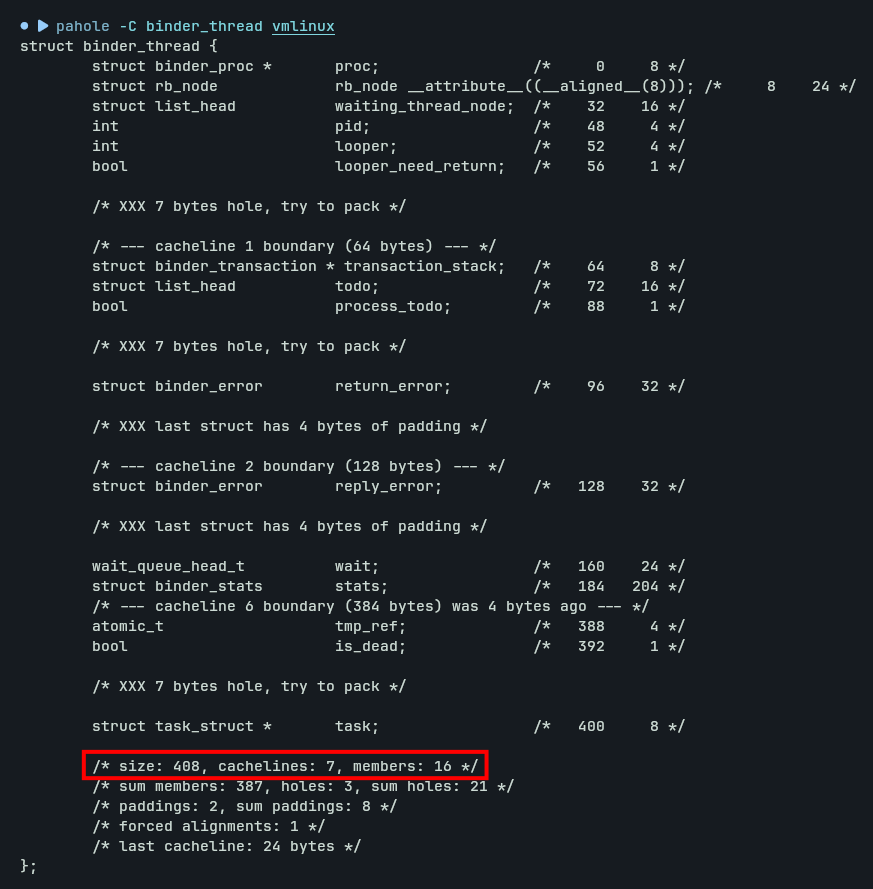
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.

HP Slate 7 2800 Android 4.1.1 rooting kit using CVE-2015-1805.

基于内核漏洞CVE-2026-43499的本地提权适配,集成嵌入式 KernelSU.CVE-2026-43499+KernelSU越狱模式

Description for CVE-2024-25466

Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…

Proof-of-concept exploit for CVE-2016-5195 (Dirty COW) targeting Android devices via ADB, demonstrating local privilege escalation through race…

Exploit for CVE-2020-0453 targeting Android NFC stack vulnerability, enabling local privilege escalation via crafted NFC packets.

Android AOSP 10 framework base repository containing the fix for CVE-2023-21097, a vulnerability in the Android framework that could lead to local…

Proof-of-concept exploit for CVE-2022-20007 targeting Android 10 (AOSP r33) framework base, demonstrating a local privilege escalation vulnerability…

CVE-2014-7911 vulnerability and CVE-2014-4322 vulnerability to get root privilege!

Local privilege escalation exploit for Android kernel vulnerability CVE-2020-0041, with portability across devices and kernel versions.

ES File Explorer Open Port Vulnerability - CVE-2019-6447

Proof-of-concept exploit for CVE-2019-2215, a use-after-free vulnerability in the Android binder driver enabling local privilege escalation on…

Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…

Exploit for CVE-2020-0041, an Android kernel privilege escalation vulnerability in the Binder driver, enabling local root access.

Android PackageInstaller source code with patch for CVE-2020-0418, a local privilege escalation vulnerability. Provides patched AOSP10 code for…