
CVE-2024-0044
 hackerronin/cve-2024-0044
a vulnerability affecting Android version 12 & 13
android-securityexploitationmobile-app-pentesting+3
62 years ago
hackerronin/cve-2024-0044a vulnerability affecting Android version 12 & 13
 re13orn/cve-2024-0044-exp
利用 CVE-2024-0044 Android 权限提升下载任意目标App沙箱文件。
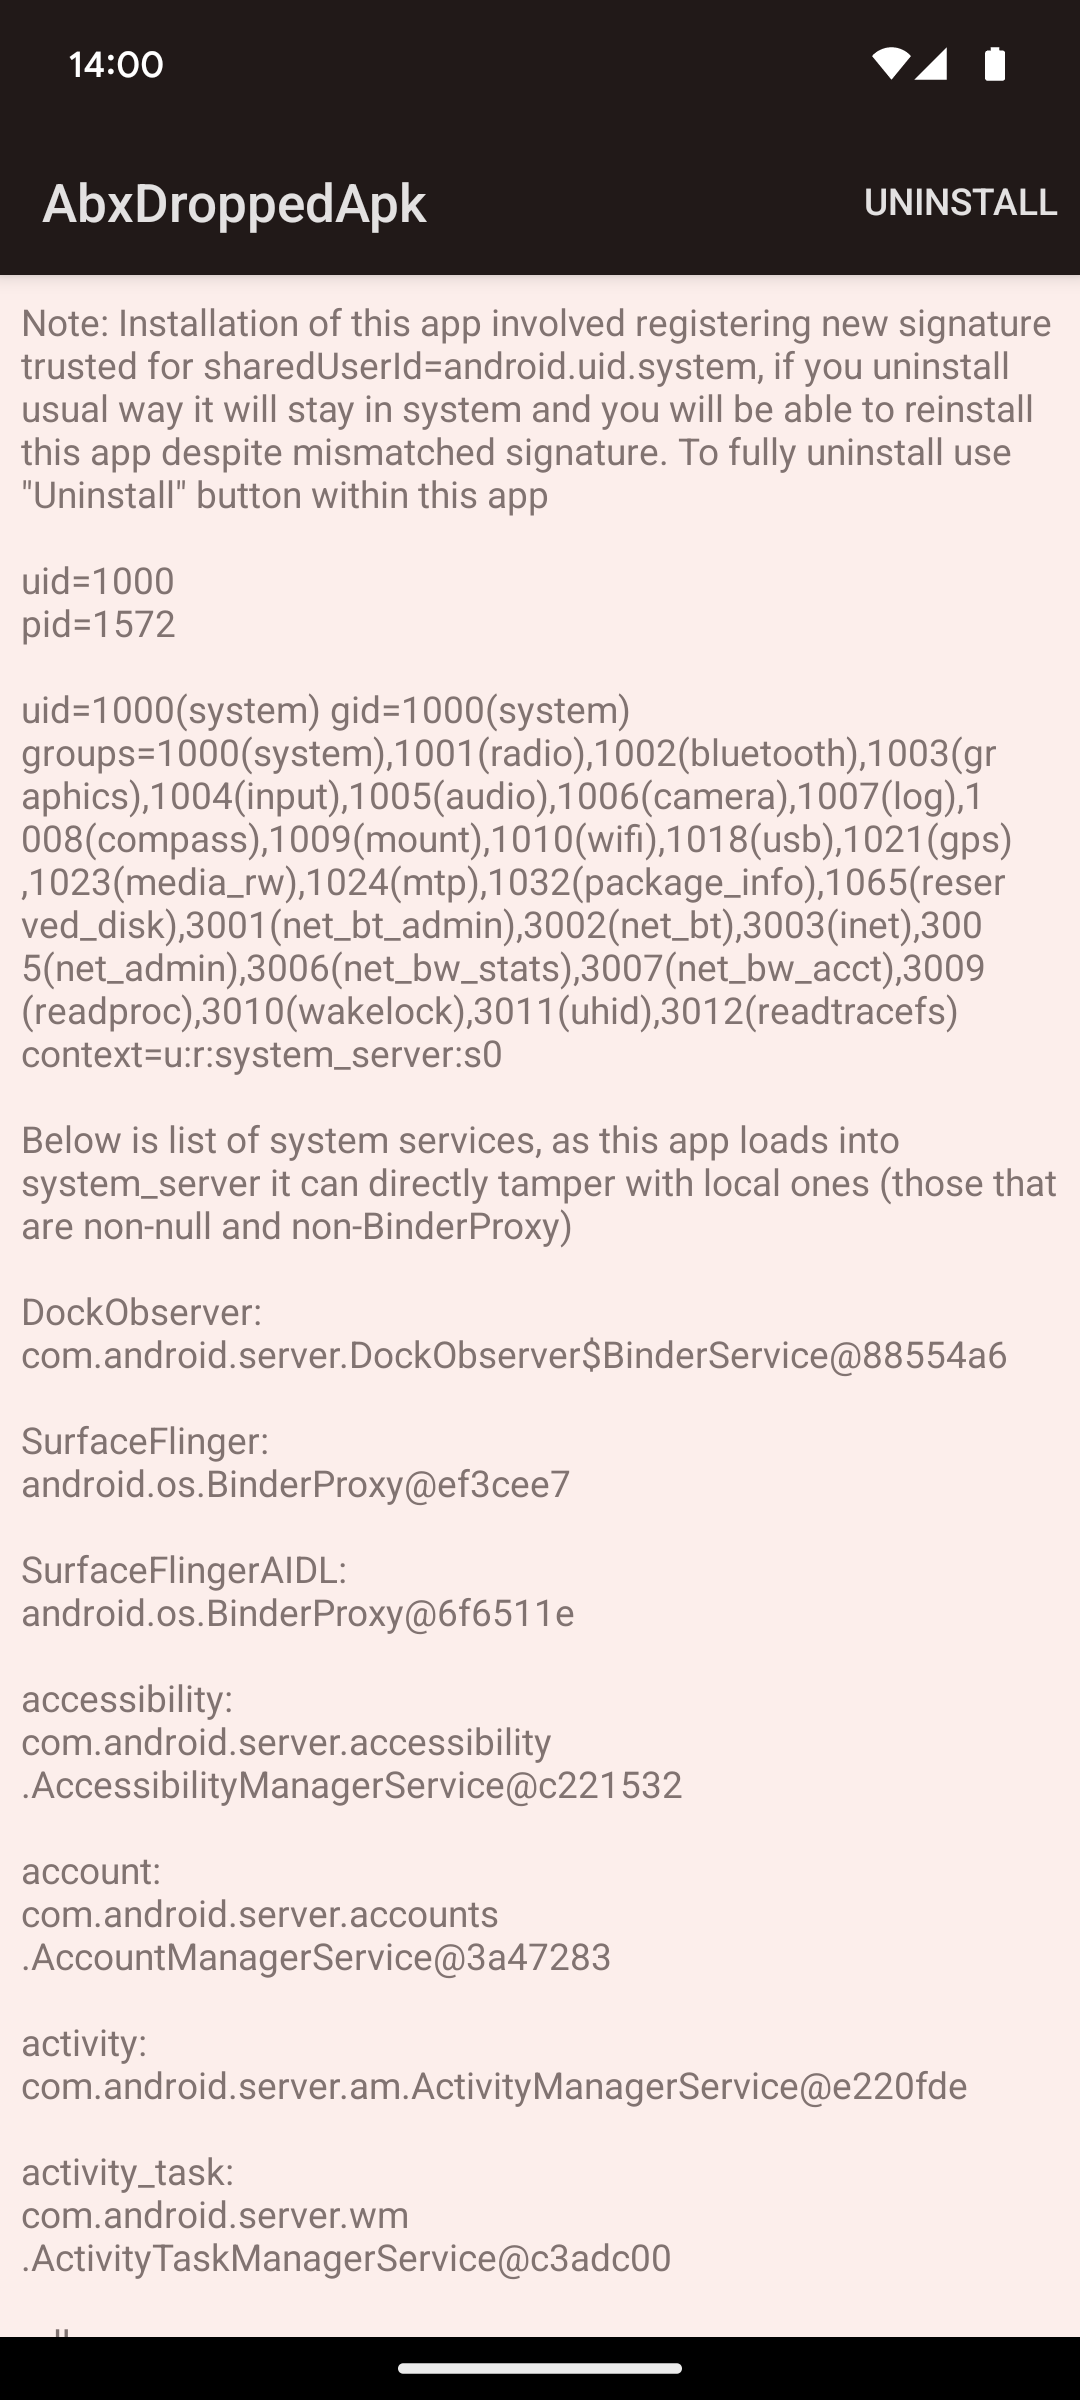 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 rifting/zygotroller
Remove Android profile owners/family link with CVE-2024-31317
 vnescape/zygote-cve-2024-31317
This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.
 kai2er/cve-2024-0044-exp
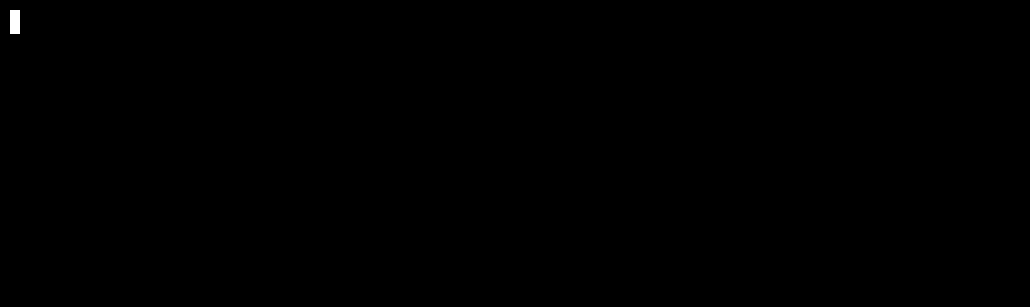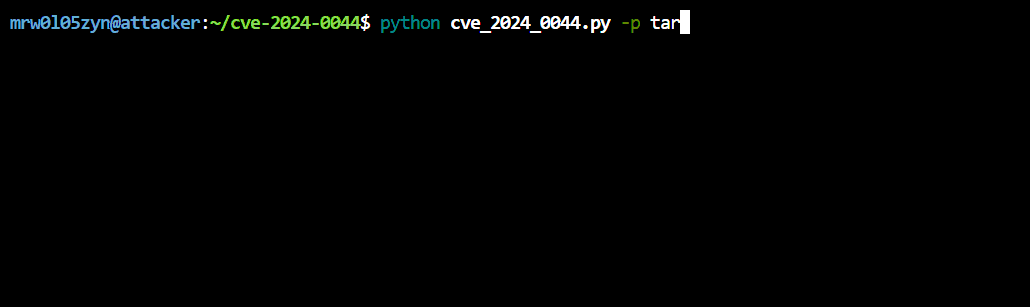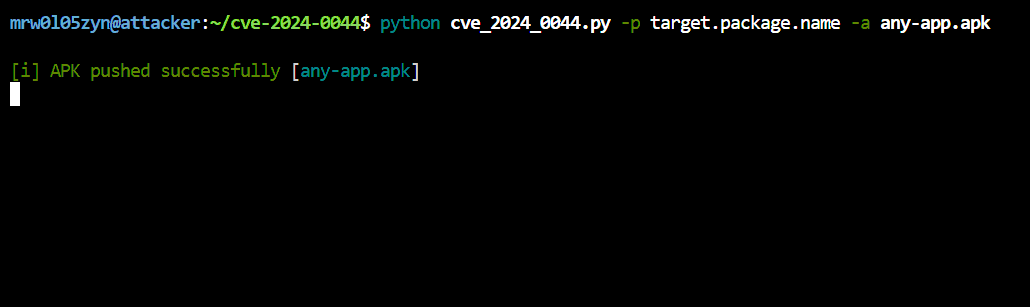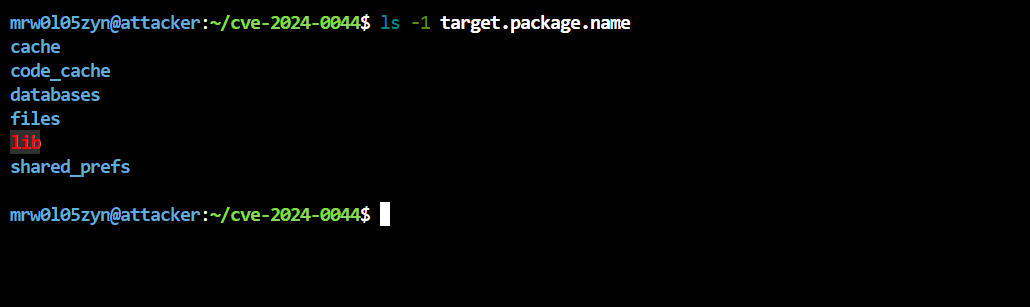
利用CVE-2024-0044 在Android12、13 没有root'下进行数据备份 用法./CVE-2024-0044-EXP.sh <package_name>
 mmiszczyk/cve-2024-33352
BlueStacks privilege escalation through VM backdooring
 fixedoctocat/cve-2024-25466
Description for CVE-2024-25466
 gitamans/zygoteexploitdemo
Educational demonstration of CVE-2024-31317 Zygote Injection Vulnerability on Android
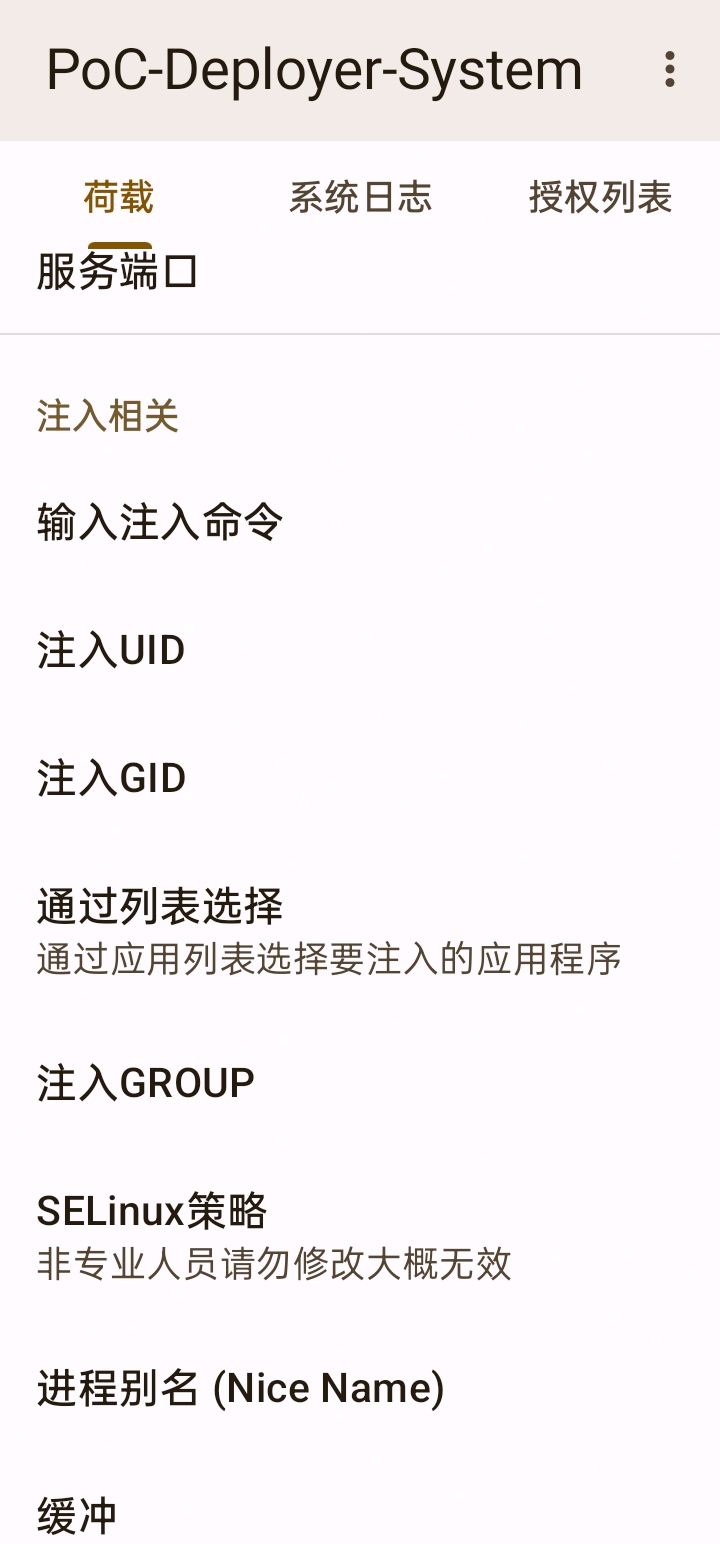 wqry085/poc-deployer-system
Quick tool for utilizing CVE-2024-31317 on Android
 k4ran909/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 hunter24x24/cve_2024_0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 fcy10012/cve-2024-31317-deployer
CVE-2024-31317 Android Zygote命令注入漏洞研究与部署工具 | Android 9-13 漏洞利用框架
 agg23/cve-2024-31317
Detailed discussion of Zygote vulnerability CVE-2024-31317