seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

Android Chromium fork with built-in ad blocking, anti-fingerprinting mitigations, DNS-over-HTTPS, and hardened privacy and security defaults.

Privacy and security hardened Chromium build providing the WebView and default browser for GrapheneOS, with OS-level hardening and compatibility…

Hardened Chromium/Bromite fork for Android, Windows and Linux with built-in ad blocking, anti-fingerprinting mitigations and privacy-focused patches.

Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10

Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.

Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…

A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.

GhostLock One-Tap Execution App (CVE-2026-43499)

GhostLock (CVE-2026-43499) root + KernelSU LKM for the Lenovo TB365FC (ZUXOS / Android 16, kernel 5.15.170)

Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…

Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)

One-click temporary KernelSU root (late-load) for Samsung Galaxy via DirtyFrag (CVE-2026-43284). No Shizuku/PC/ADB.

Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.

Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…

Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…

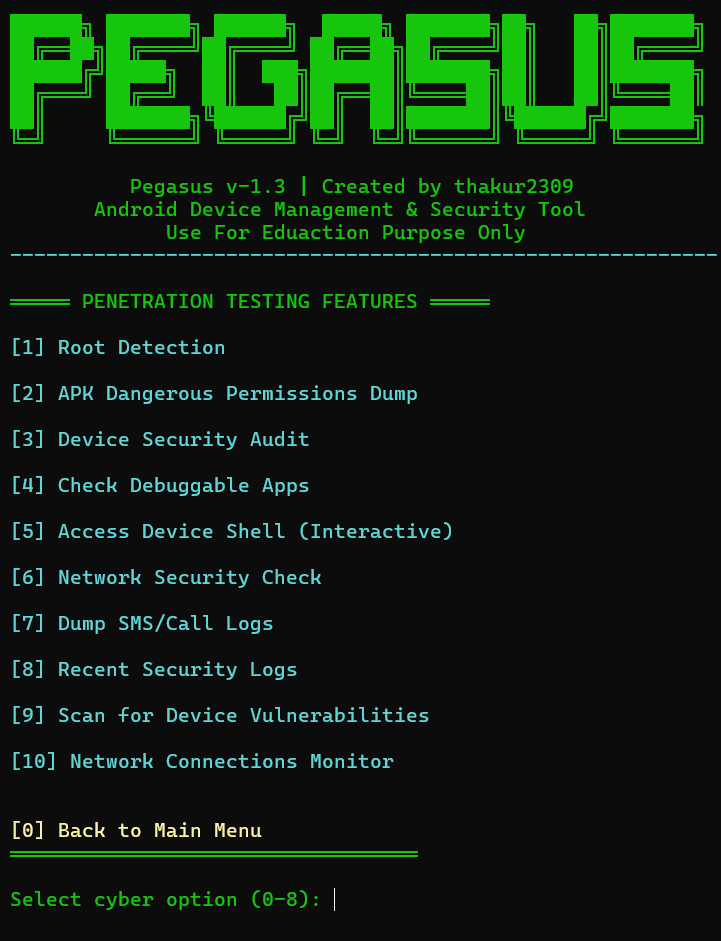
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…