

Securiscan
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
ai-securityapi-securityapi-security-testing+8
vighnesh91/securiscanStandard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 anthropics/defending-code-reference-harness
Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize
 oksuzkayra/gaia
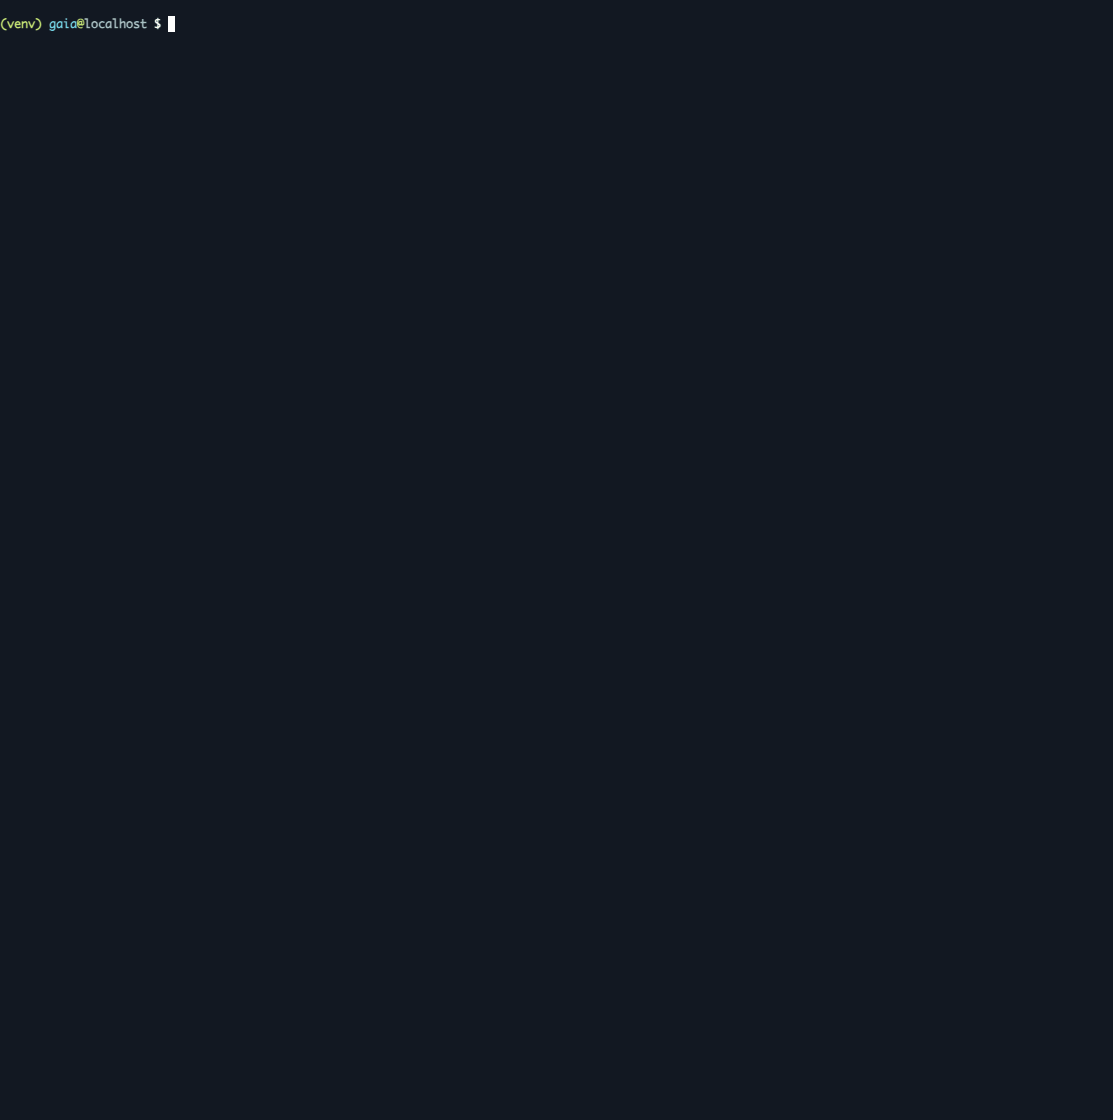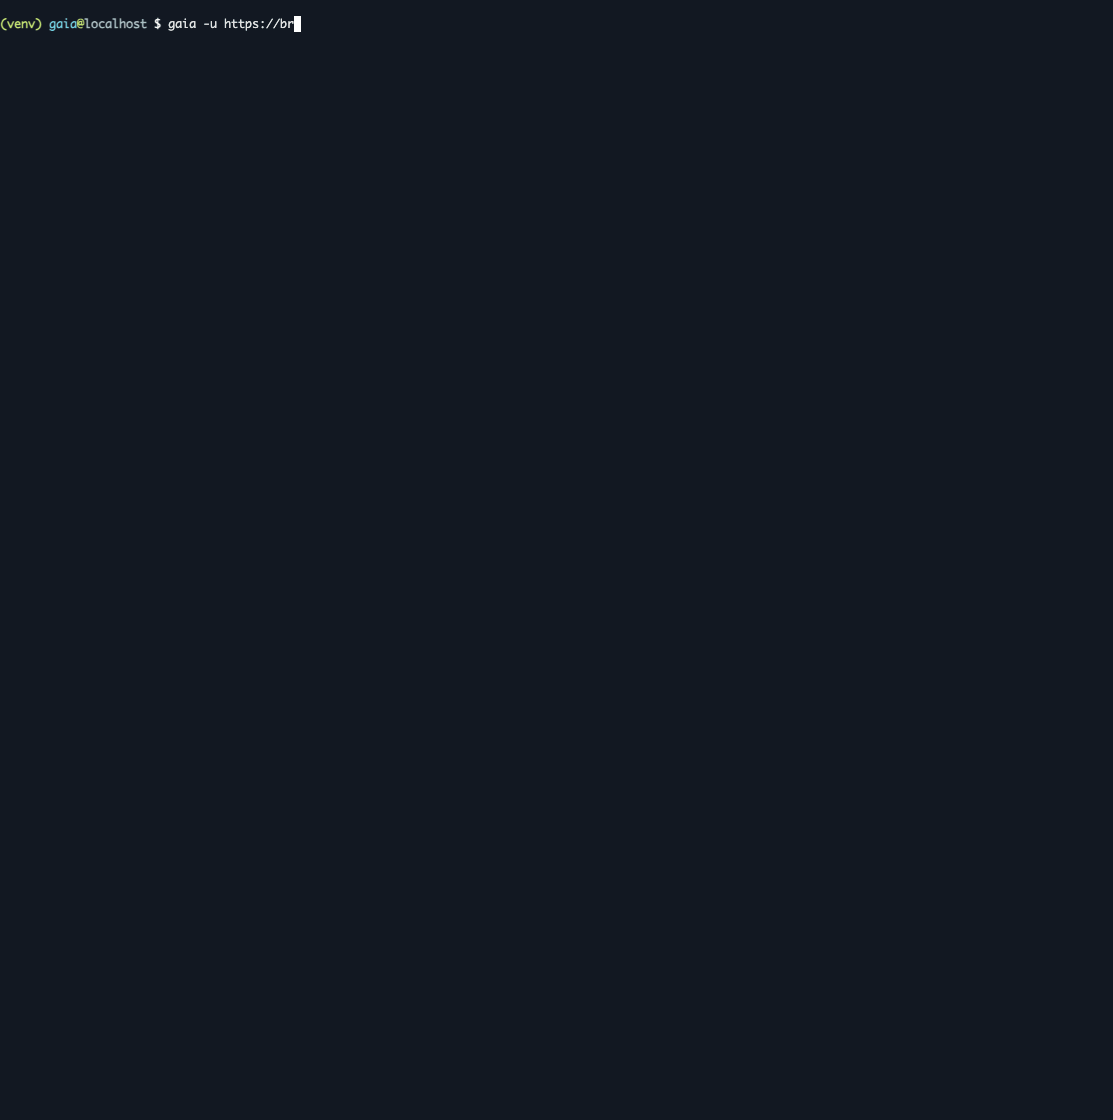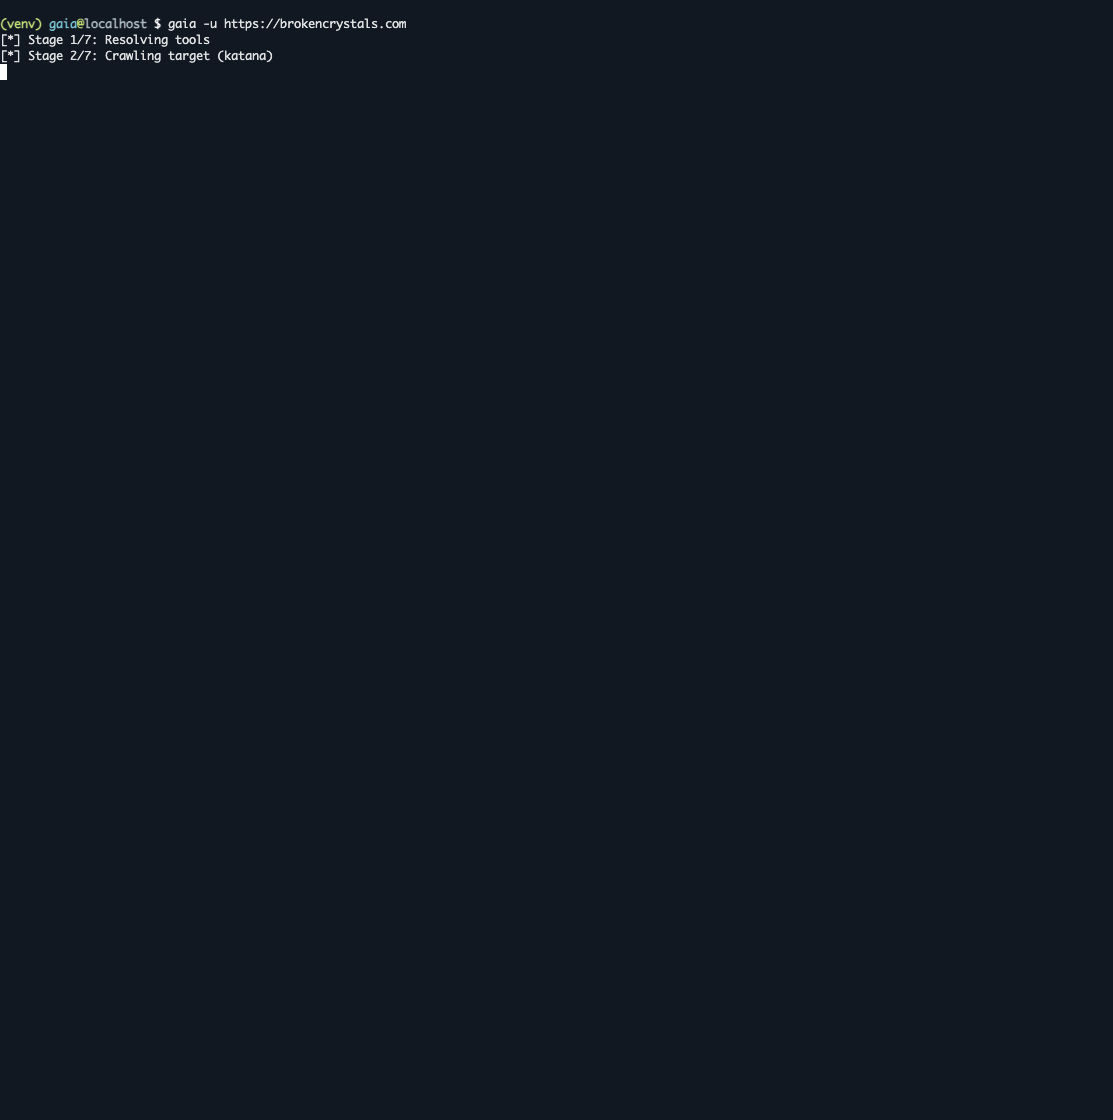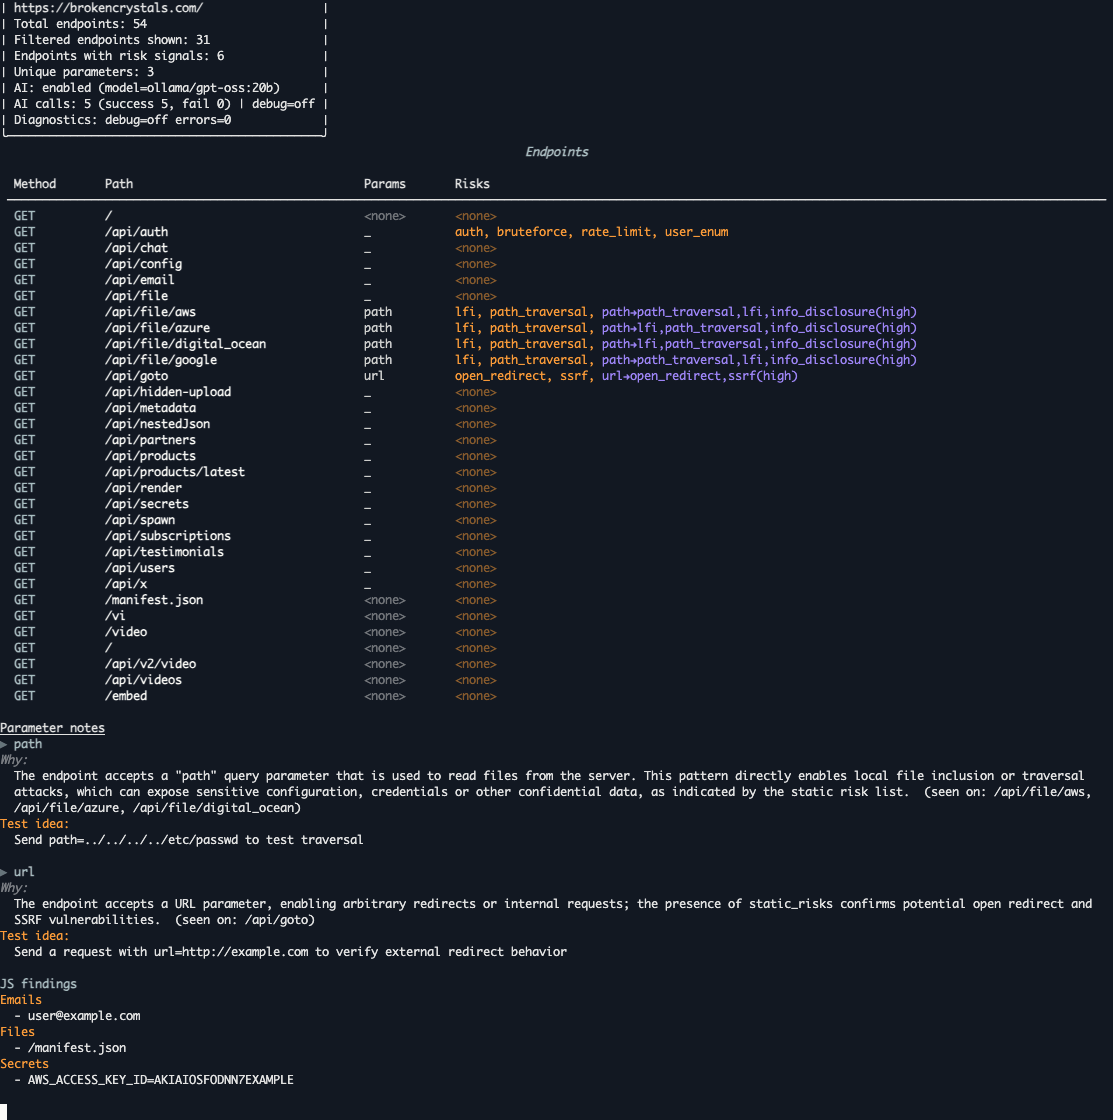
Attack surface discovery and AI-assisted triage for security researchers. Endpoint & parameter mapping with actionable testing hints.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
 vigil-xy/agent-scanning
Unified dashboard to monitor, govern, and audit AI agents in real-time. Enforce budgets, detect policy violations, and export compliance reports for…
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 pvharmo2/gha-lab-733c168b88
Reproduces CVE-2026-44246, a prompt injection vulnerability in nnU-Net's GitHub Actions triage agent, demonstrating how issue content is inlined into…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 foxirain/linux-kernel-codex-harness-v2
Provenance-aware Linux kernel vulnerability research harness used in the investigation of CVE-2026-53075
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 bkuan001/halo-record
Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
 mangod12/onealert
AI-powered SOC for OT/ICS networks — 6 autonomous agents, MITRE ATT&CK mapping, Suricata/Zeek ingestion, human-in-the-loop response, 330+ tests.…