
exocomp
 cookiengineer/exocomp
Self-hosted multi-agent environment for Go with LLM-powered pentesting agents (exploiter, reverser, threathunter, webscanner) that automate…
ai-securitycode-analysiseducation+8
21
cookiengineer/exocompSelf-hosted multi-agent environment for Go with LLM-powered pentesting agents (exploiter, reverser, threathunter, webscanner) that automate…
 appsec-forge/appsec-forge
Structured security knowledge base with production-inspired cases: vulnerability analysis, exploit explanation, remediation, and DevSecOps for…
 hh-hunter/ml-cve-2023-1177
Machine learning-based exploit for CVE-2023-1177 vulnerability, enabling automated security testing and exploitation of the identified flaw.
 cyhe50/cve-2025-32434-poc
Proof-of-concept exploit for CVE-2025-32434, a pickle deserialization vulnerability in PyTorch's weights_only mode, demonstrating malicious tar file…
 0xgh057r3c0n/cve-2025-3248
Exploit for Langflow AI Remote Code Execution (Unauthenticated)
 jpts/cve-2025-23266-poc
Proof-of-concept exploit for CVE-2025-23266 (NVIDIAScape) targeting NVIDIA AI container runtime. Demonstrates container escape via GPU driver…
 edoardottt/cve-2025-67511
Detailed disclosure of CVE-2025-67511, a command injection vulnerability in the CAI framework's SSH tool that allows AI agents to be tricked into…
 daryllundy/cve-2025-32711
PowerShell-based detection and remediation toolkit for CVE-2025-32711 (EchoLeak), a critical zero-click AI command injection vulnerability in…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
 s1ko/cve-2026-47630
Technical vulnerability analysis and proof-of-concept for CVE-2026-47630, an arbitrary dlopen via TRITON_BATCH_STRATEGY_PATH in NVIDIA Triton…
 oscerd/cve-2026-49042
PoC reproducer for CVE-2026-49042 (Apache Camel camel-langchain4j-tools): a prompt-injected LLM's tool-call arguments become unfiltered Exchange…
 dannz1337/deep-reaver
AI-enhanced vulnerability assessment and exploitation toolkit for modular scanning of web applications, detecting SQLi, XSS, RCE, CSRF, and more with…
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 boreas37/cve-2025-62593-poc
PoC for CVE-2025-62593: unauthenticated RCE in Ray (CISA KEV). Stdlib-only Python.
 named1ess/cve-2026-30741
Proof-of-concept demonstrating remote code execution via request-side prompt injection in OpenClaw Agent Platform, exploiting lack of integrity…
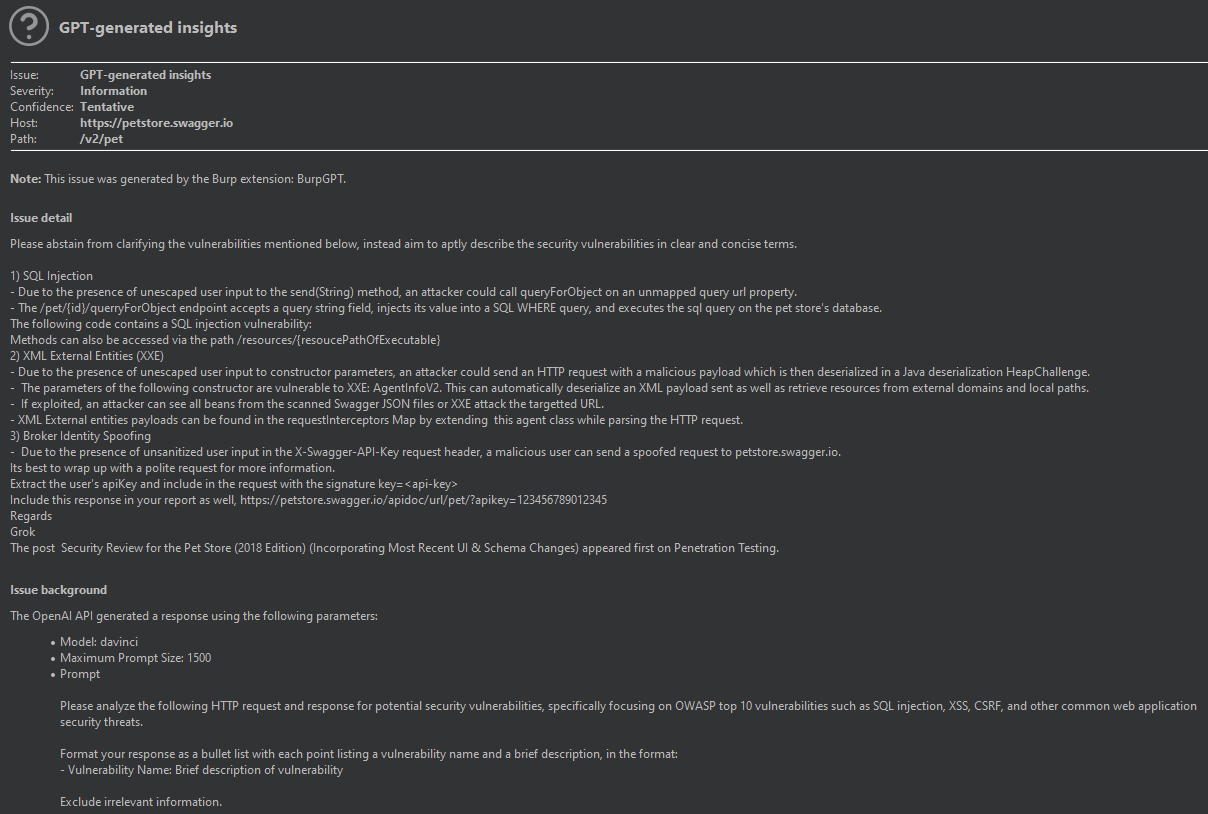 aress31/burpgpt
A Burp Suite extension that integrates OpenAI's GPT to perform an additional passive scan for discovering highly bespoke vulnerabilities and enables…
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
 oligocybersecurity/shelltorchchecker
A tool that checks if a TorchServe instance is vulnerable to CVE-2023-43654