
system_prompts_leaks
 asgeirtj/system_prompts_leaks
Curated collection of extracted system prompts from major AI chatbots including Claude, ChatGPT, Gemini, Grok, and Copilot. Updated regularly with…
ai-securitycurated-resourceseducation+3
70.5k
asgeirtj/system_prompts_leaksCurated collection of extracted system prompts from major AI chatbots including Claude, ChatGPT, Gemini, Grok, and Copilot. Updated regularly with…
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 togg53192-cmd/jailbreaks
Curated collection of LLM jailbreak prompts and bypass techniques, documenting adversarial inputs that circumvent AI model safety guardrails.
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 protectai/ai-exploits
A collection of real world AI/ML exploits for responsibly disclosed vulnerabilities
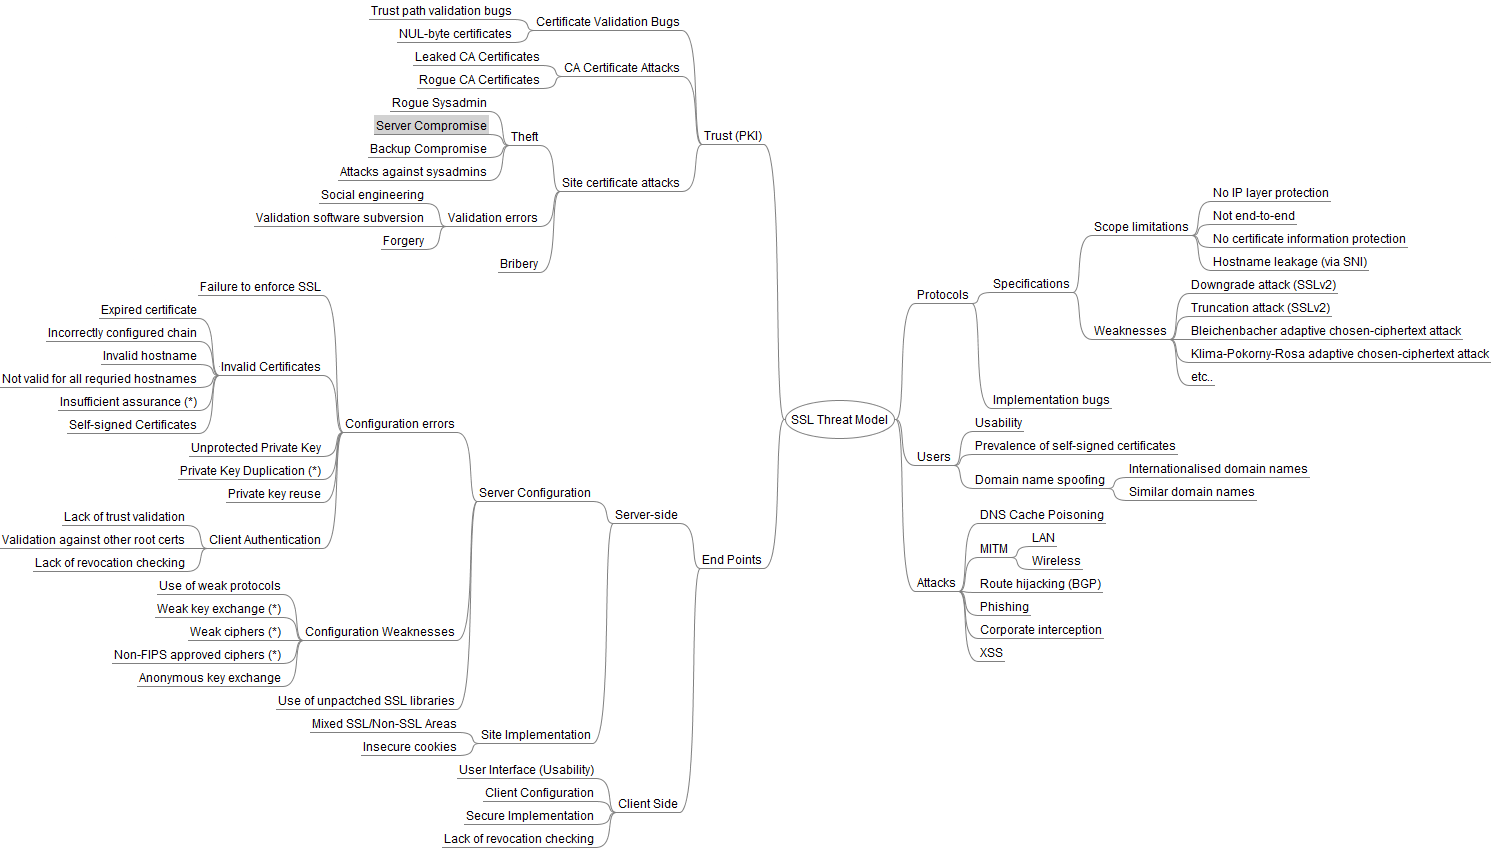 taleliyahu/threat_model_examples
A collection of real-world threat model examples across various technologies, providing practical insights into identifying and mitigating security…
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
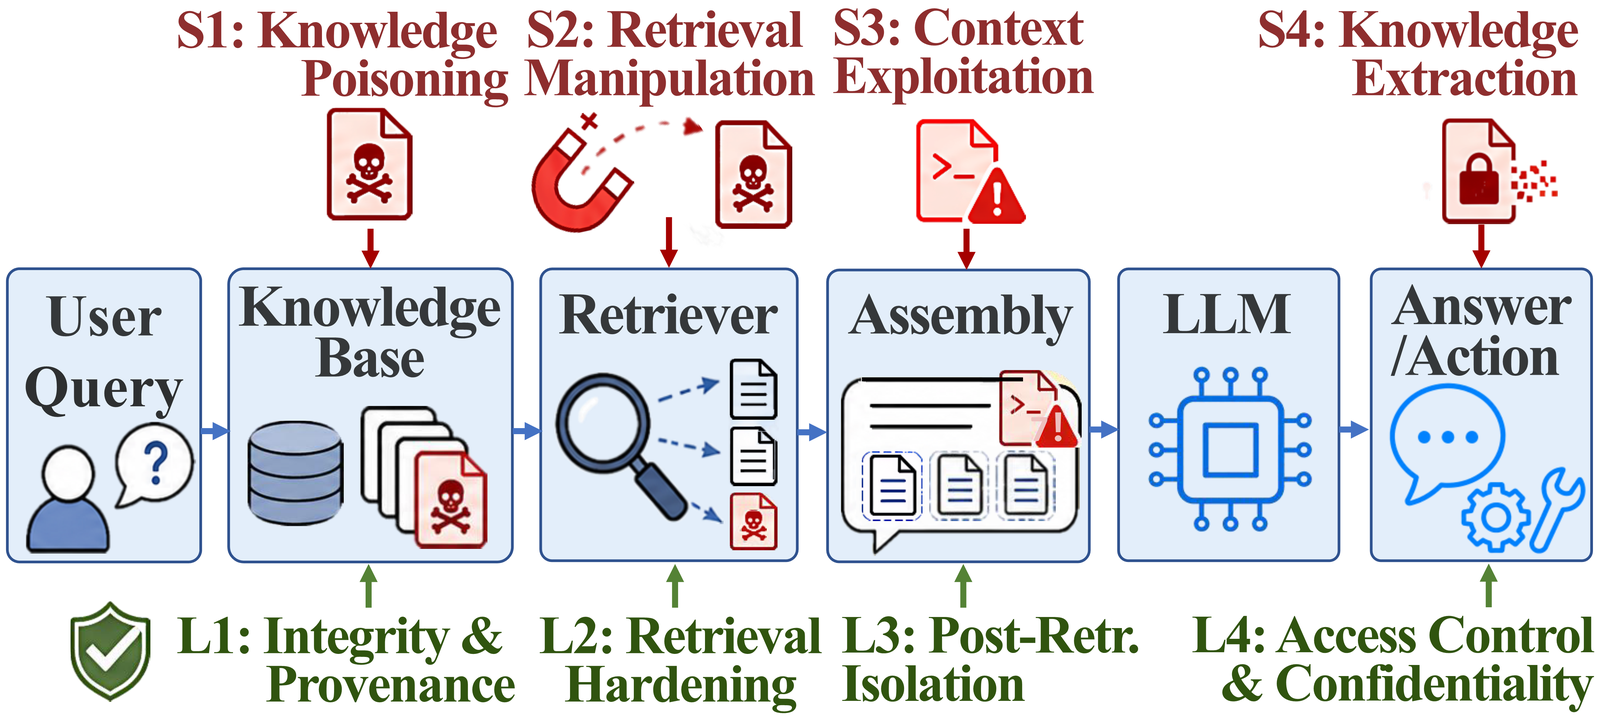 treeai-lab/awesome-rag-security
Curated collection of research papers on retrieval-augmented generation security, organized by the SLOT taxonomy covering knowledge poisoning,…
 horkimhab/llm-prompt-injection-resources
A curated collection of resources for learning and researching LLM prompt injection attacks, defenses, and security.
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
 gmh5225/llm-attack-prompt
Jailbreaks,Prompt Leaks,Prompt Injection,LLM Attack.Large language model attack prompt collection
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
 nanashibx2/bx2-writeups
Cybersecurity writeups, walkthroughs, and technical notes by Nanashi Bx2.
 jianshuod/ipi-exposure-signal
Research pipeline for detecting latent indirect prompt-injection exposure signals in agentic LLMs via hidden-state probing, including trace…
 backbay-labs/hush
Portable security rules for the action boundary of AI agents