

AIDebug
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
ai-securitybinary-analysisdebuggers+7
16
anpa1200/aidebugEvidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 happytotoro116/ghidra-llm-pipeline
Deterministic PyGhidra extraction, triage, and local LLM compiler-backend pipeline for C reimplementation.
 ph4ntom-rev/ph4ntom-ida-bridge
Secure local REST, CLI, MCP, and agent bridge for IDA Pro 9.x
 saiteja-erukude/cve-2026-47117-openmed-rce
OpenMed < 1.5.2 unauthenticated RCE via PII privacy-filter model loading and trust_remote_code=True
 iceman2050/chatml-role-token-probe
Fire ChatML/Mistral/Llama control-token literals at your self-hosted agent stack and prove role-forgery before an attacker does (CVE-2026-61732).
 binzhwang/actguard
Pre-execution action-auditing defense that detects and masks indirect prompt injection in tool-using LLM agents using embedding retrieval and…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 gmh5225/aisa-scanner
AISA-Scanner is an AI-powered autonomous vulnerability scanner that maps CVEs to metasploit exploits, MITRE, CEH, and SANS, delivering intelligent,…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 rbidou/llm-forensics
Weight-level LLM forensics: diff model weights, detect fine-tunes, merges and disguised derivatives, and surface tokens a fine-tune promotes or…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 gmh5225/ida_plugin_pcodegpt
IDA Pro plugin that uses OpenAI GPT-3.5/GPT-4 to automate reverse engineering tasks such as function naming, code explanation, and decompiled…
 dannz1337/deep-reaver
AI-enhanced vulnerability assessment and exploitation toolkit for modular scanning of web applications, detecting SQLi, XSS, RCE, CSRF, and more with…
 hh-hunter/ml-cve-2023-1177
Machine learning-based exploit for CVE-2023-1177 vulnerability, enabling automated security testing and exploitation of the identified flaw.
 trailofbits/privacyraven
Privacy testing library for deep learning systems, enabling assessment of susceptibility to membership inference, model extraction, and model…
 abraxas/loom-skill-plant
A Loom registry admin can rewrite a skill document that has no group owner. The next full deploy of an agent that already lists that skill copies the…
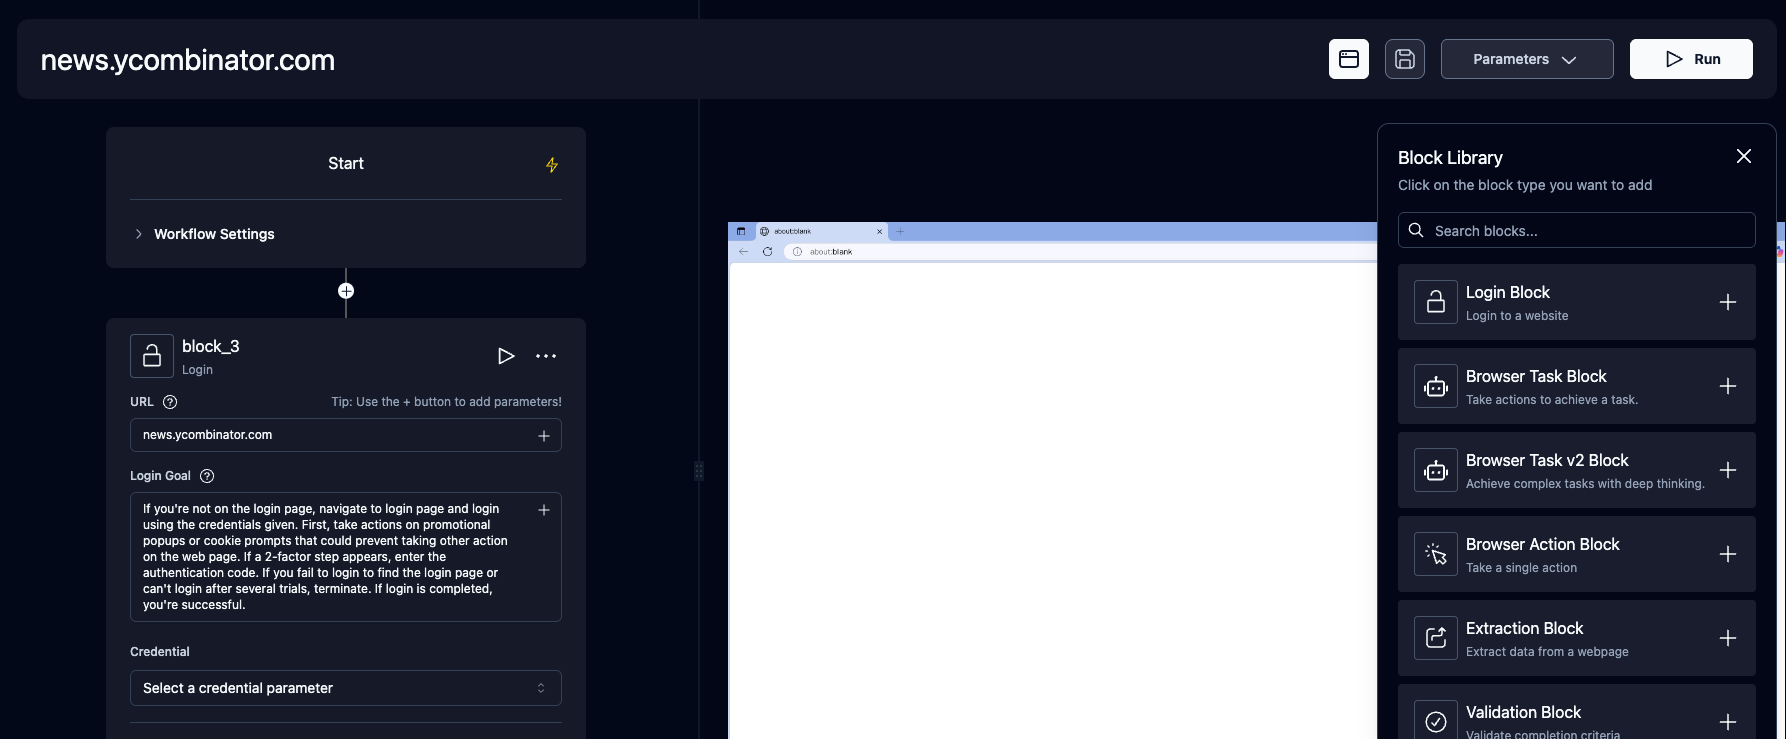 skyvern-ai/skyvern
Automate browser based workflows with AI