
bitcoder-v2-research
 bytepro-ai/bitcoder-v2-research
Research repository documenting LLM generalization ceilings in code security vulnerability detection, with cross-evaluation across synthetic and…
ai-securitycode-analysiseducation+5
1
bytepro-ai/bitcoder-v2-researchResearch repository documenting LLM generalization ceilings in code security vulnerability detection, with cross-evaluation across synthetic and…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 nanda-rani/safe
A contextual security auditing system for research artifacts
 sushant-me/agentic-workflow-injection
Reproducible vulnerable and fixed GitHub Actions fixtures for agentic workflow injection (CVE-2026-44246), with measured detector coverage and…
 unknownhl/deepguard
Code for ACL 2026 (main) paper "DeepGuard: Secure Code Generation via Multi-Layer Semantic Aggregation"
 vinsontang1/dcvd
The code in "DCVD: Dual-Channel Cross-Modal Fusion for Joint Vulnerability Detection and Localization"
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
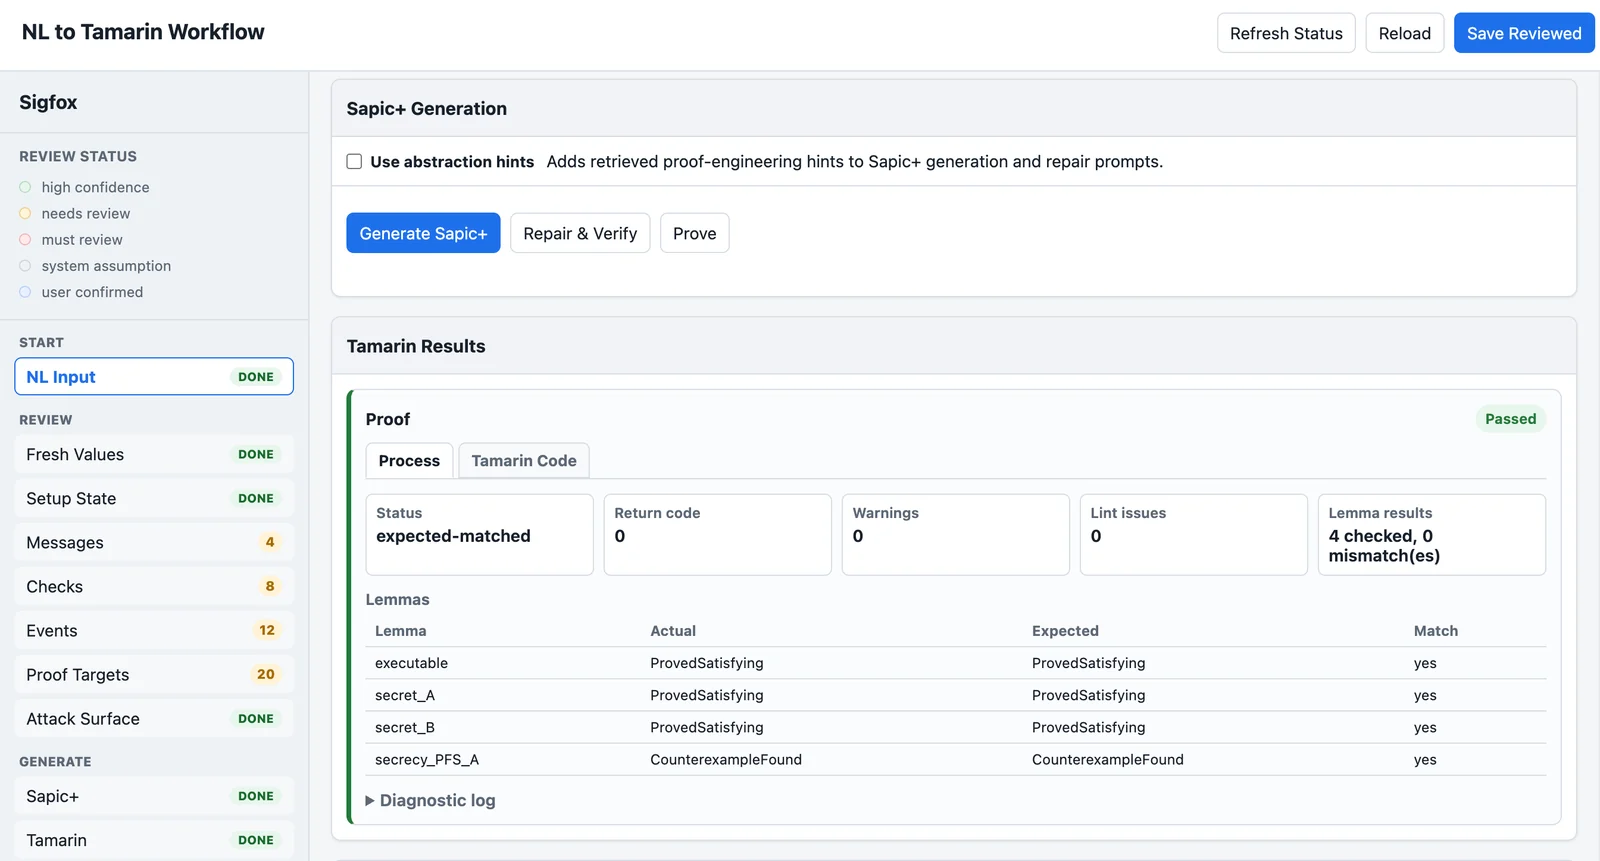 laplace1002/tamarinagent
Human-in-the-loop UI that converts natural-language or C/C++ protocol descriptions into a reviewable Protocol IR, then generates Sapic+/Tamarin…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 razi-interactive/claude-project-scanner
Read-only safety scanner for Claude Code projects. Catches CVE-2025-59536, statusLine injection, prompt injection, and more.
 perufitlife/dotclaude-security
Scan a repo's .claude/ config (settings.json hooks, MCP servers, env, allowed-tools) for the RCE & API-key-exfiltration footguns (CVE-2025-59536,…
 rootdirective-sec/cve-2026-33626-lab
Docker Compose lab reproducing CVE-2026-33626 SSRF in LMDeploy's vision-language image loader. Compares vulnerable (0.12.0) and patched (0.12.3)…
 useaitechdad/openclaw-technical-analysis
This technical research and review is for educational purposes on public code and constitutes Fair Dealing under the Copyright Act (Canada).
 gmh5225/malicious-code-detection-bugu
AI-based malicious code detection and obfuscation system with microservices for detection, packing, and code confusion, plus user and admin services.
 centisgood/duo-agentflow-auditor
AI Code Security — four agents that catch what SAST misses in AI-generated code. Built on GitLab Duo Agent Platform.
 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 qybaihe/bla
Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and…