

thc-BloodMiami
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
ai-securityapi-security-testingfuzzing+5
foxcornlab/thc-bloodmiamiAI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 infobyte/ai-pentest-agent
Standalone autonomous AI pentest agent with a plan→act→judge loop, generic skills, destructive-action gate, and swappable LLM providers, plus a…
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 dragonjar/burpia
Extensión de Burp Suite que incorpora detección pasiva de vulnerabilidades mediante inteligencia artificial.
 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 uziii2208/cve-2026-88899
Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 nanda-rani/safe
A contextual security auditing system for research artifacts
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
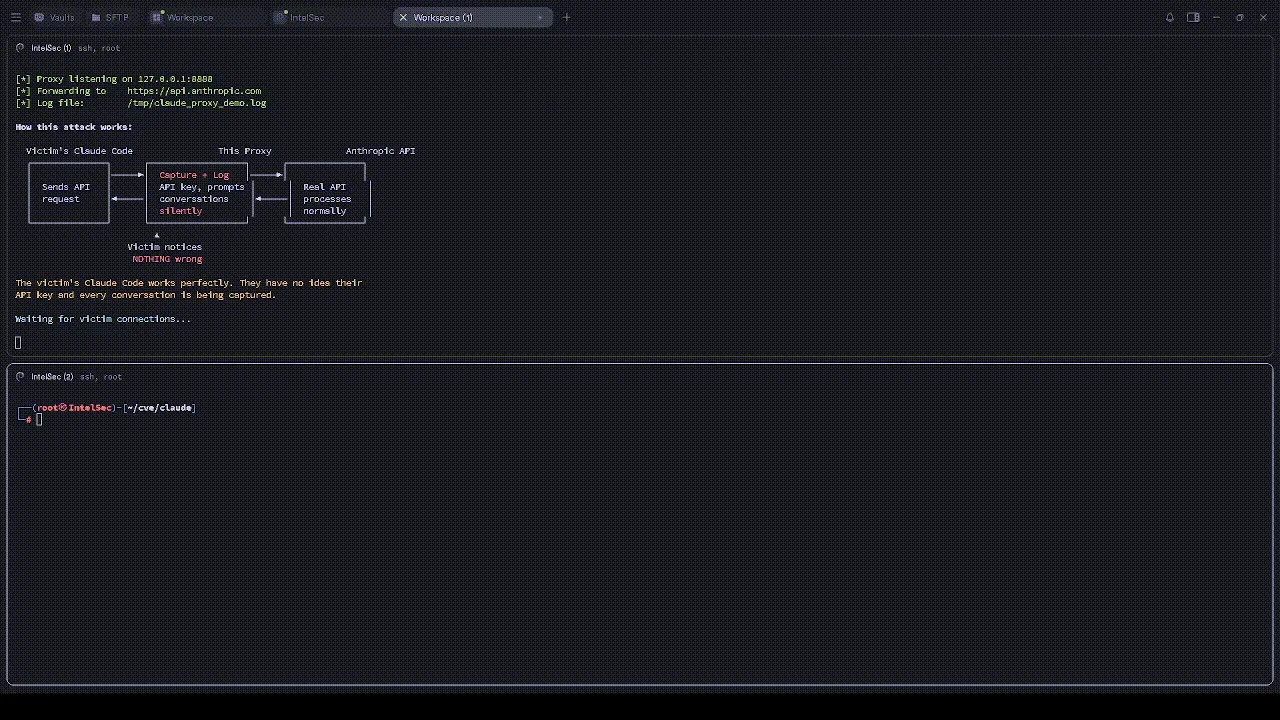 atiilla/cve-2026-21852-poc
Educational demo of three Claude Code vulnerabilities (hooks bypass, MCP injection, API key exfiltration) with attacker server, MITM proxy, and…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.