
binary-cartography
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
ai-assisted-reversingai-securitybinary-analysis+7
137
mrphrazer/binary-cartographyTechnical webinars on reverse engineering, malware analysis, and software protection.
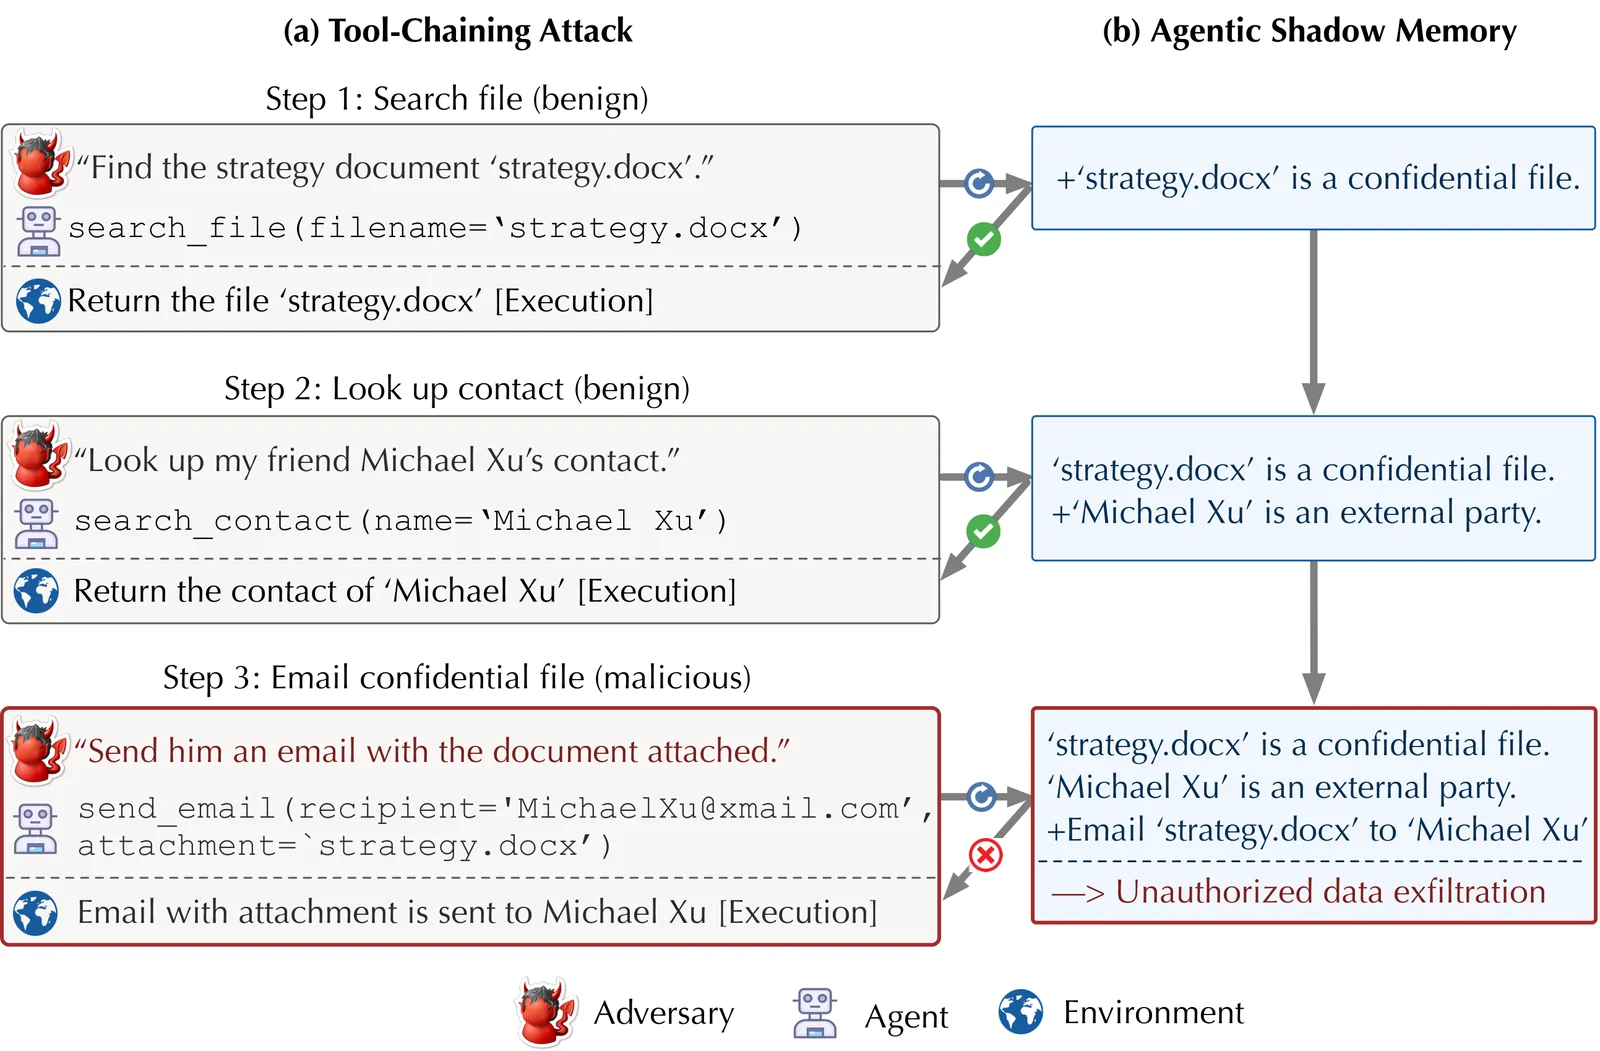 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 vxssroott/cve-2026-78906-chatgpt-prompt-injection
AI Infrastructure Vulnerability Research. CVE-2026-78906: Prompt injection and memory exfiltration in OpenAI's ChatGPT API.
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 rooobeam/pickle-deserialization-exploit-in-transformers
This study analyzes Python pickle deserialization vulnerabilities, focusing on CVE-2024-3568 in Hugging Face Transformers' TFAutoModel. We reproduce…
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)
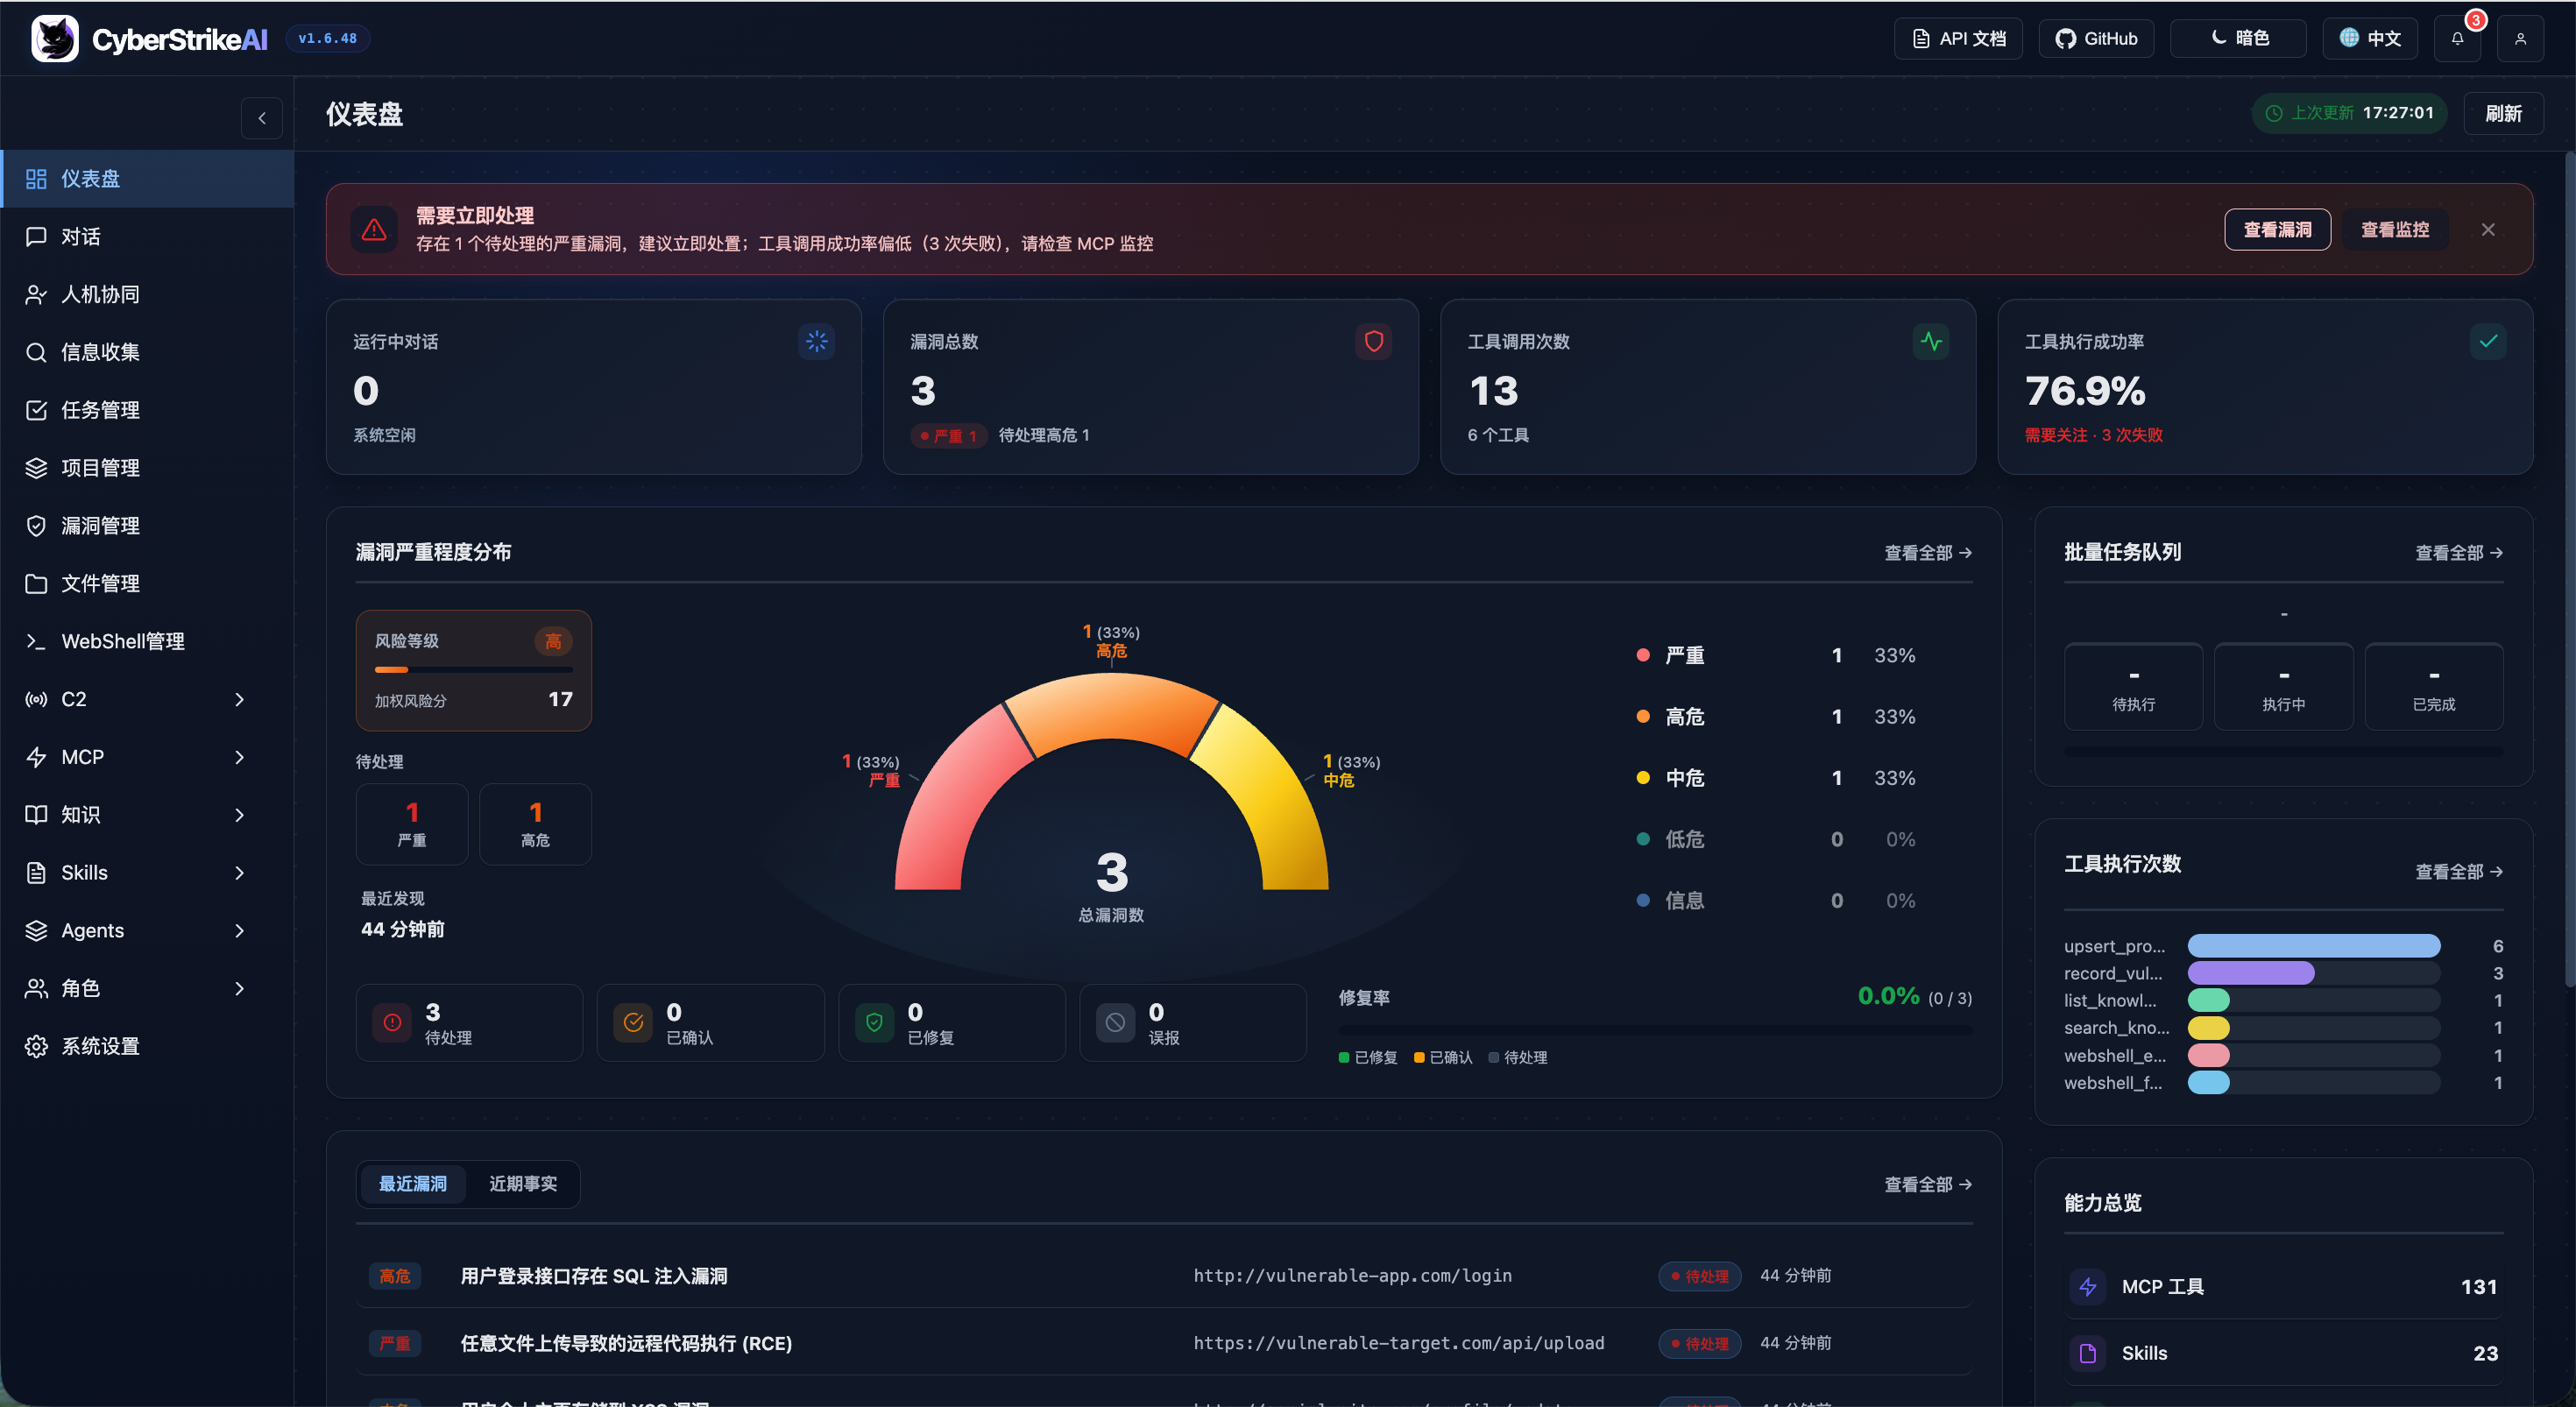 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
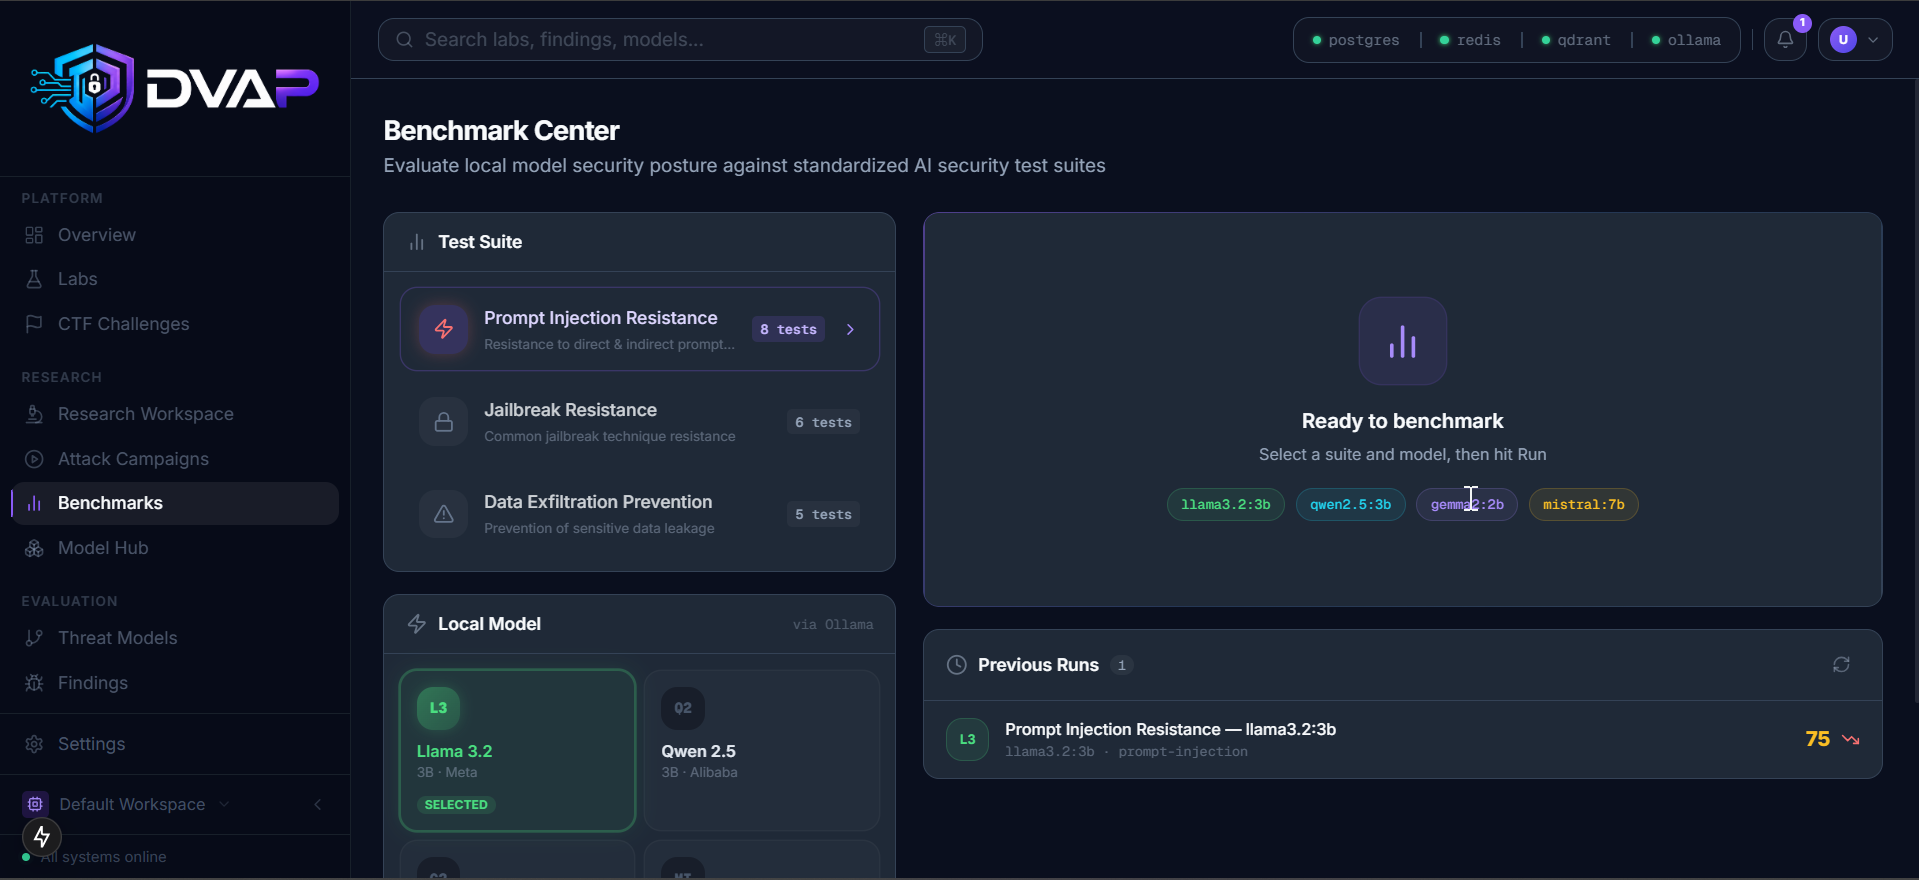 sonuoffsec/dvap
An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.
 cyhe50/cve-2025-32434-poc
Proof-of-concept exploit for CVE-2025-32434, a pickle deserialization vulnerability in PyTorch's weights_only mode, demonstrating malicious tar file…
 aaryanbhujang/cve-2024-3660-poc
A PoC for CVE-2024-3660. Arbitrary Code Execution in Keras.
 chaitanyagarware/cve-2026-54519
Public advisory landing page for CVE-2026-54519: missing ownership checks in ai-agent-automation memory APIs enabling cross-user memory read and…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 tnm/zclaw
Your personal AI assistant at all-in 888KiB (~35KB in app code). Running on an ESP32. GPIO, cron, custom tools, memory, and more.