

autorun-audit
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
ai-securitycode-analysisconfiguration-auditing+6
ag3ntsc4rn/autorun-auditFind code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 tridents10/vader-pro-vdr
AI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…
 gmh5225/llm-guard-service
A service to provide protection against prompt injection, jailbreak attacks, and harmful content when interacting with AI services..
 safedep/gryph
Security layer for AI coding agents. Works with Claude Code, Cursor, Windsurf, Gemini CLI, OpenCode, Pi Agent and more.
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
 niffyhunt/codeguard-copilot
AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
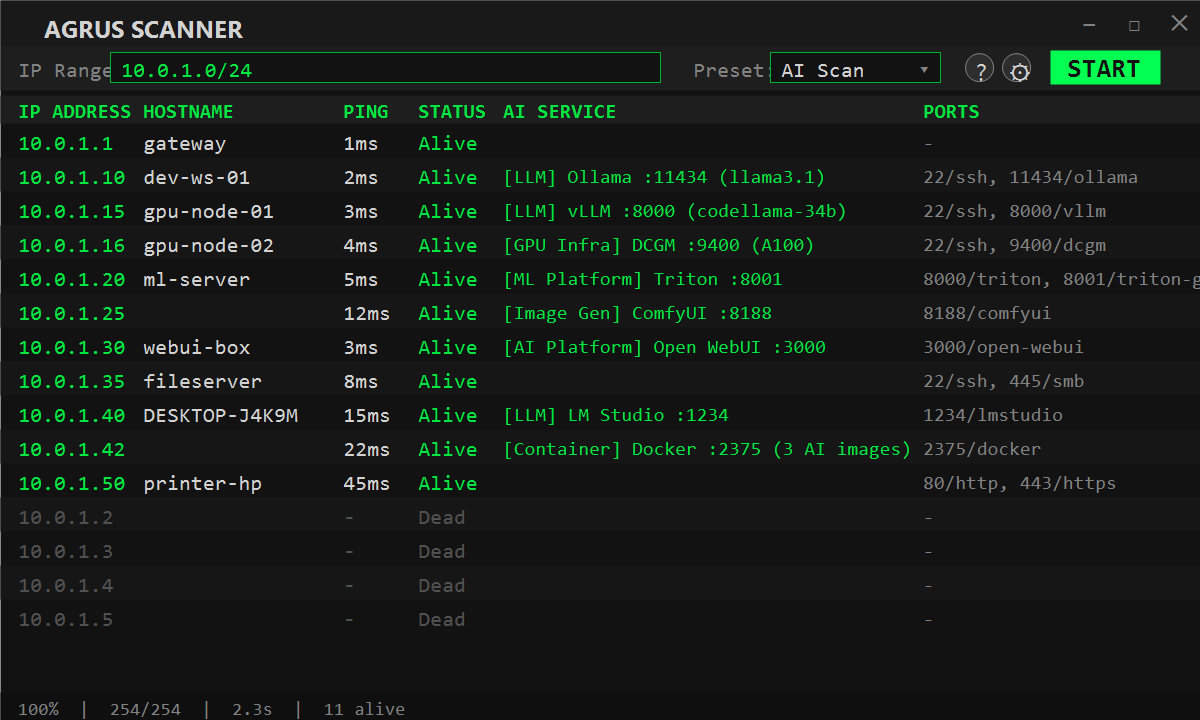 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 atomburstofficial/geiger
Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…