
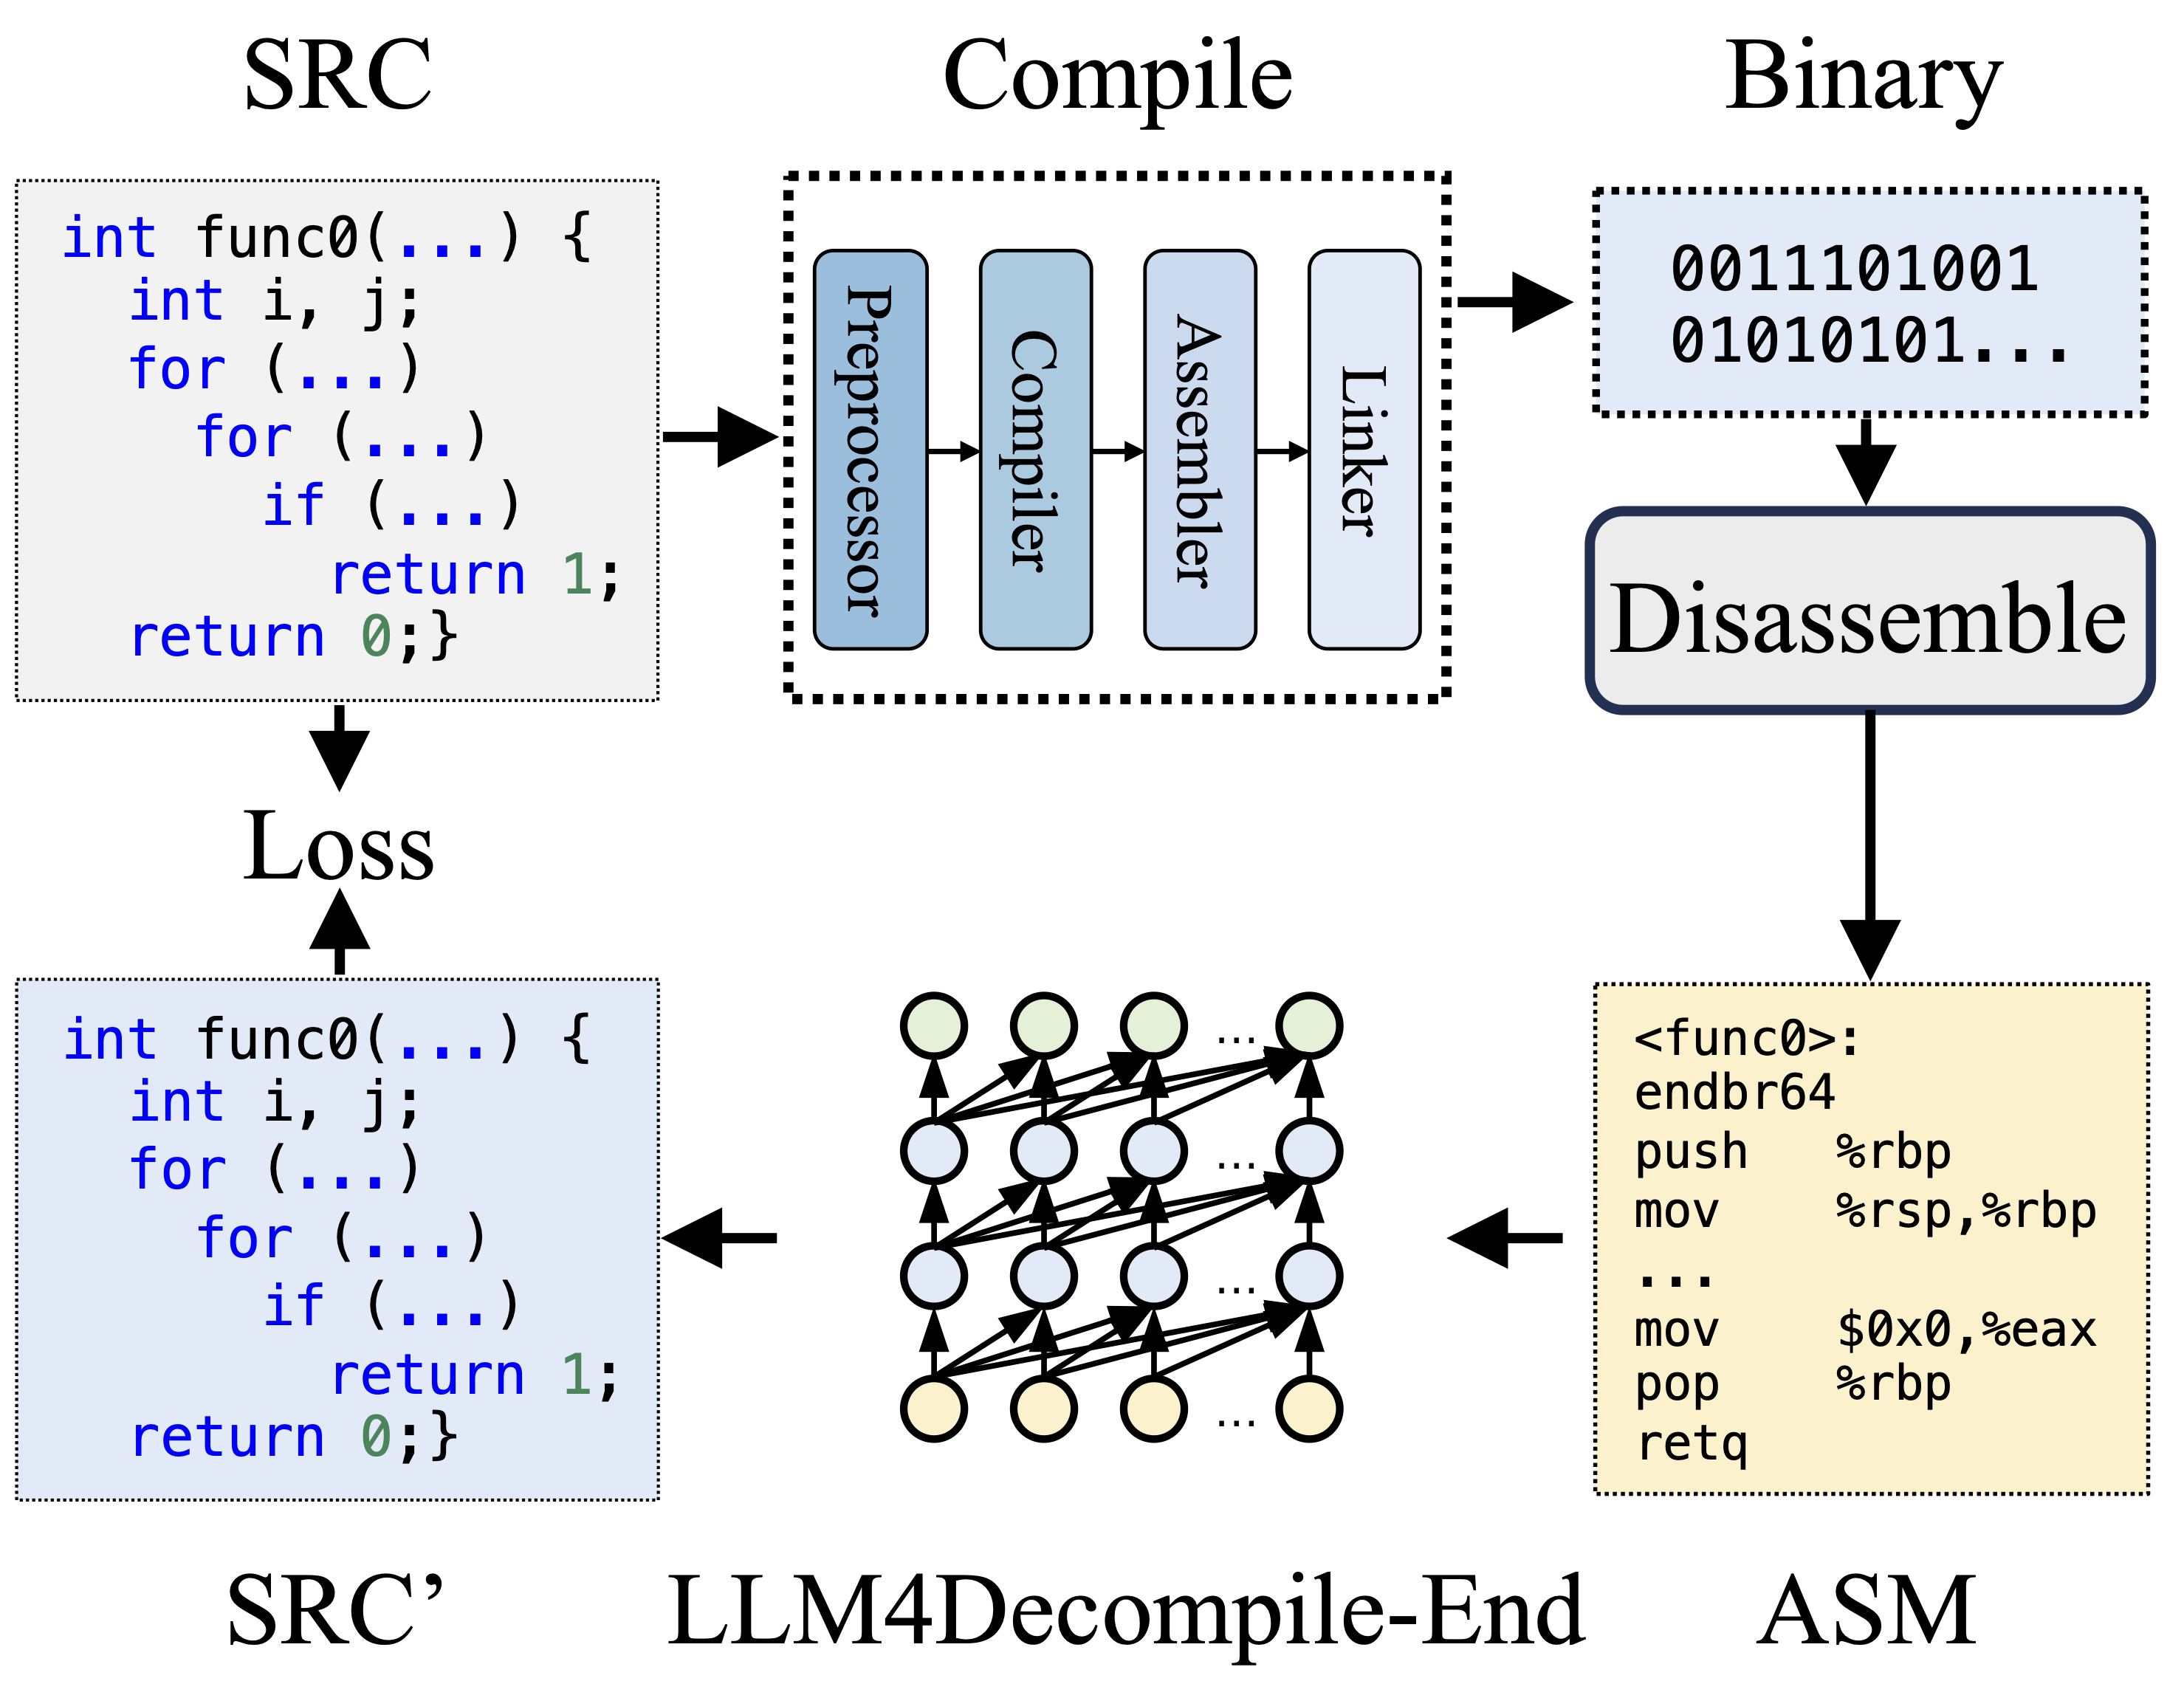
LLM4Decompile
 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
ai-assisted-reversingbinary-analysismachine-learning+1
7.0k
albertan017/llm4decompileReverse Engineering: Decompiling Binary Code with Large Language Models
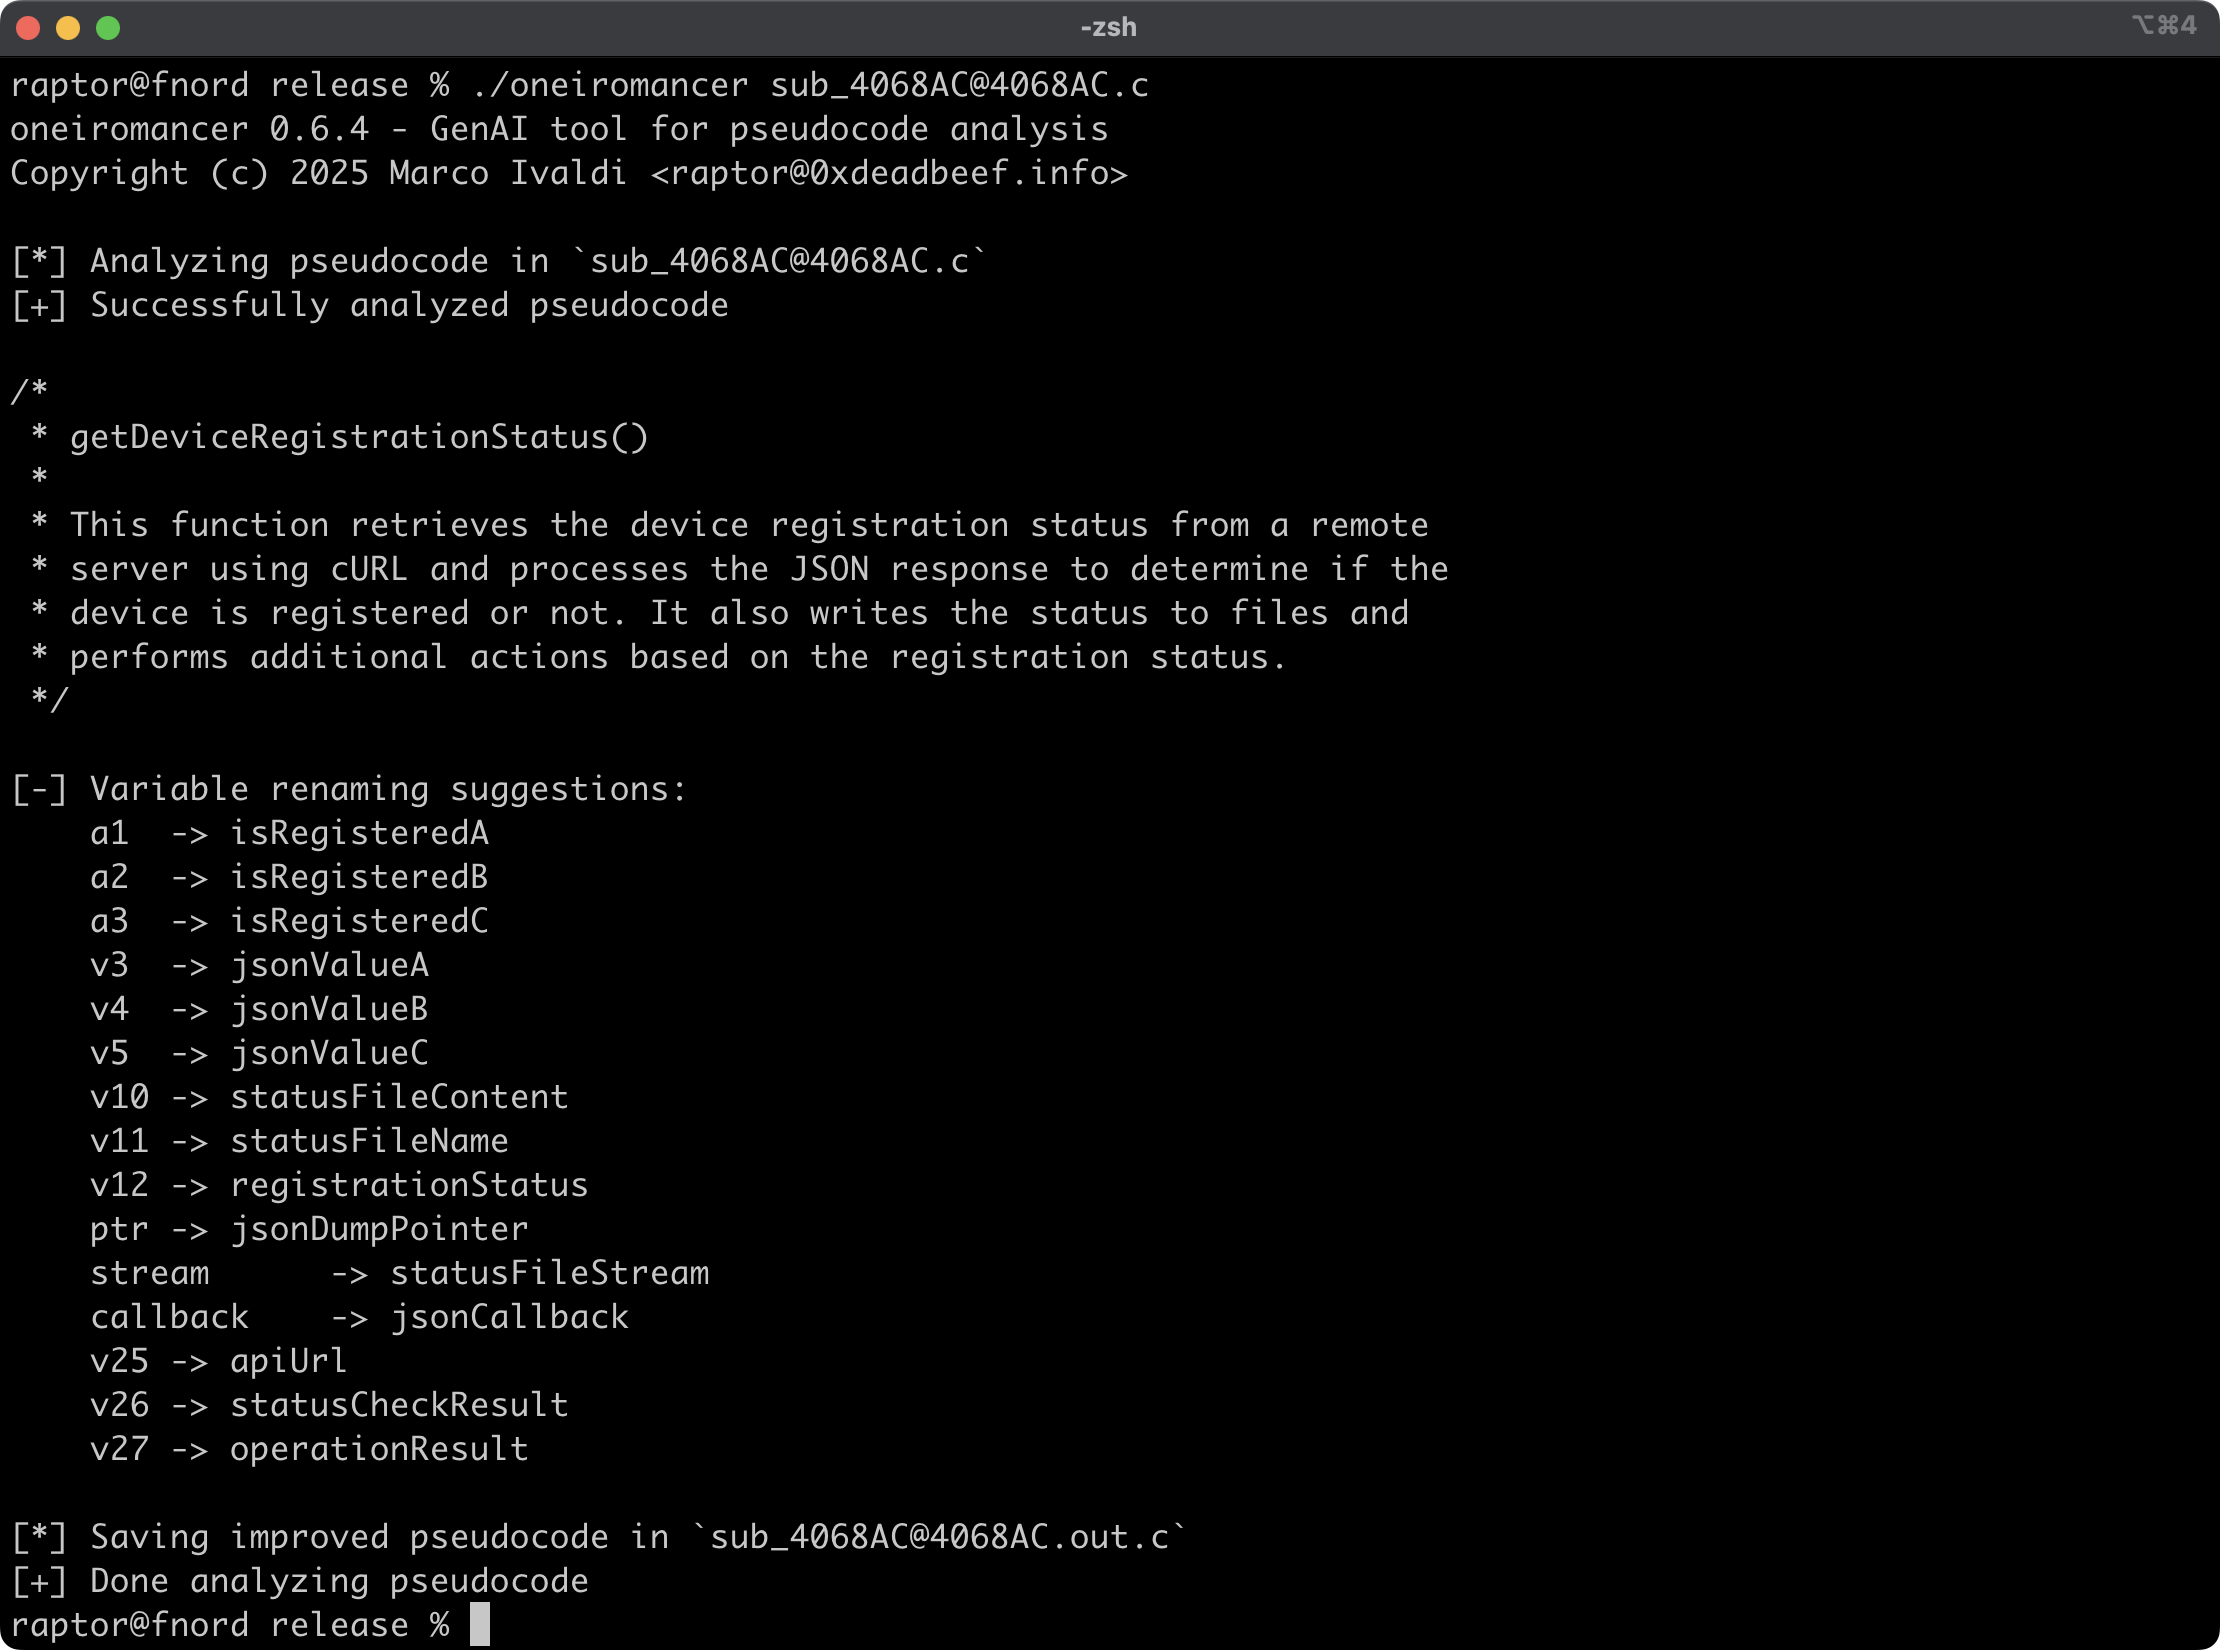 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
 vulhunt-re/vulhunt
Vulnerability detection framework by Binarly's REsearch team
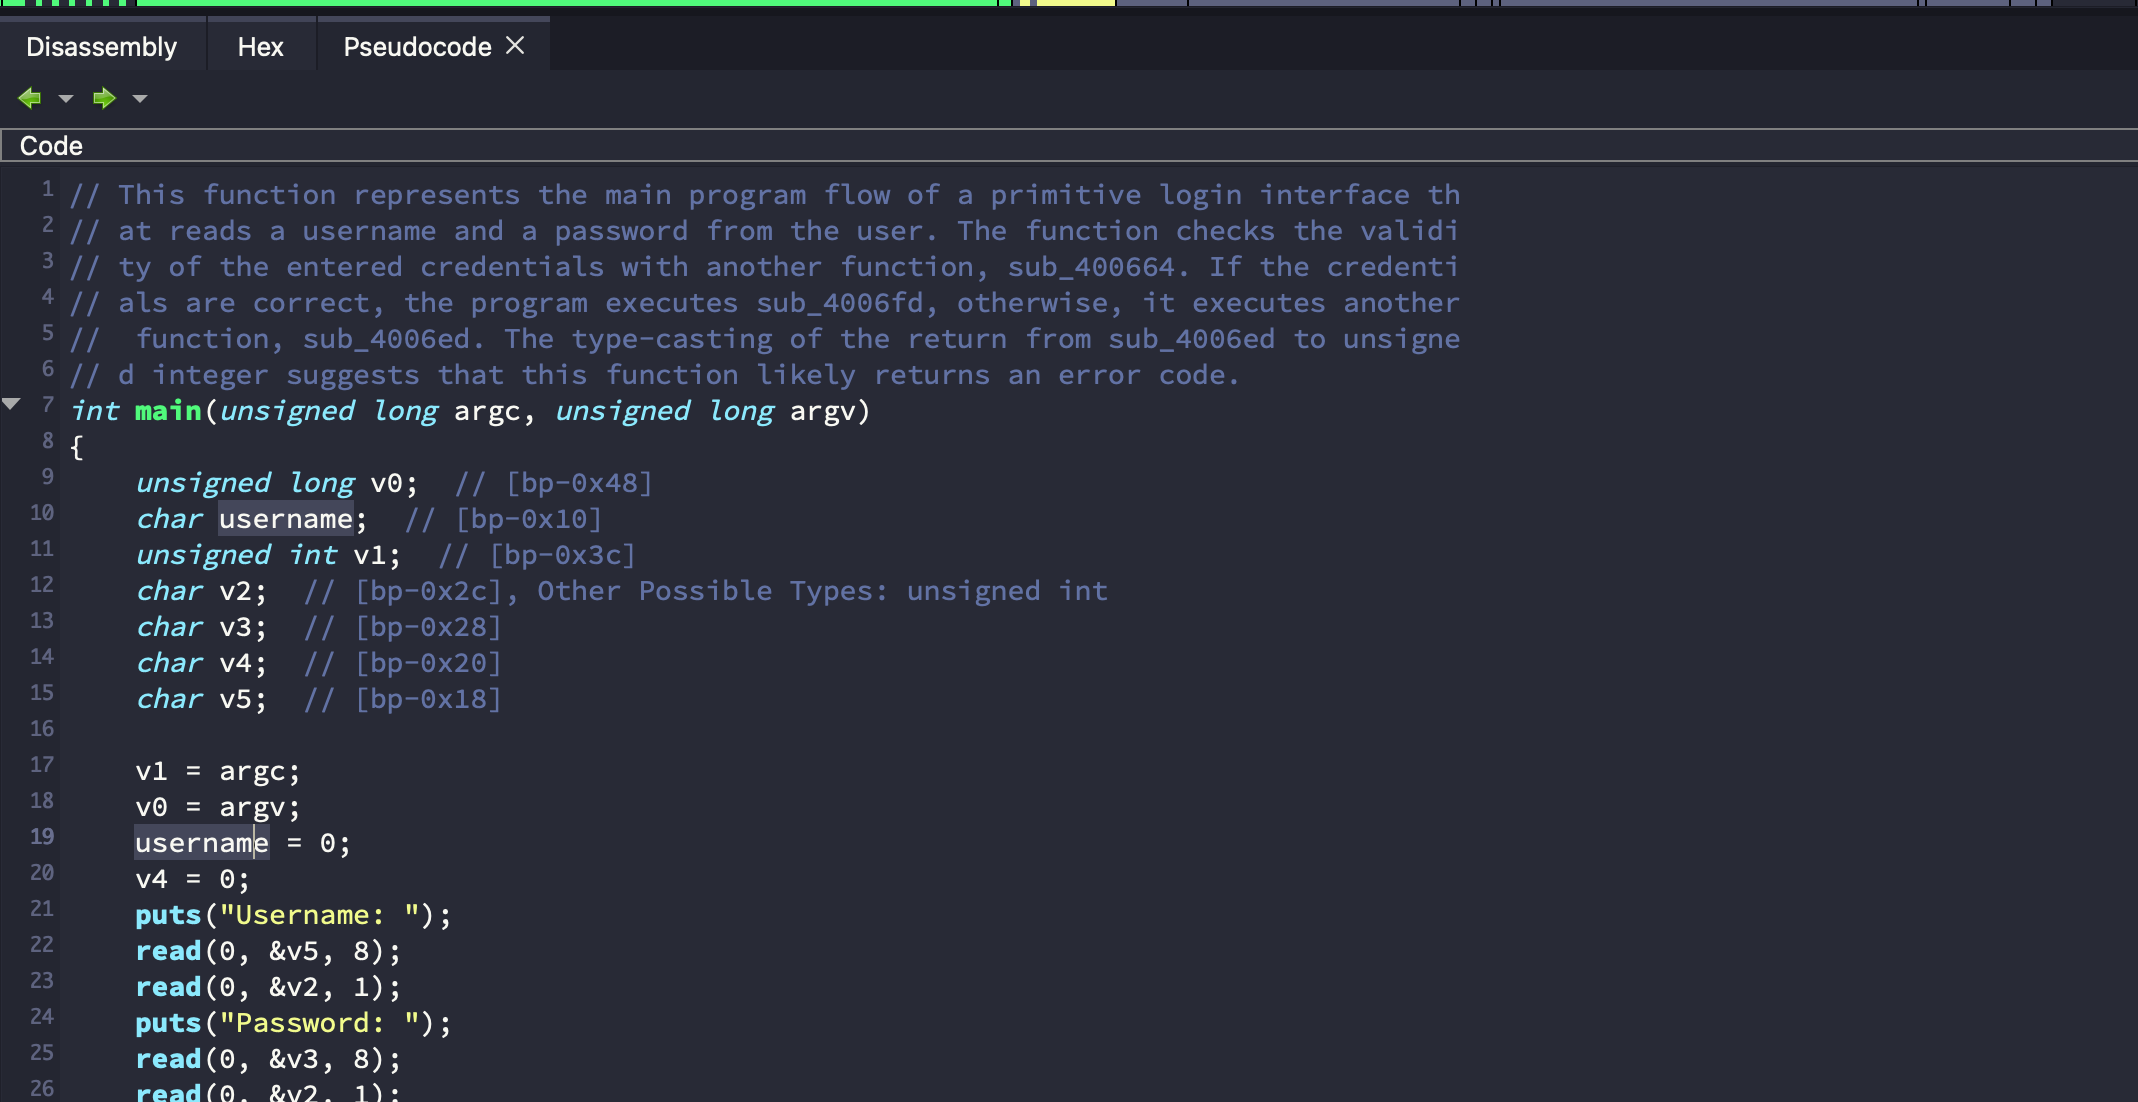 mahaloz/daila
A decompiler-agnostic plugin for interacting with AI in your decompiler. GPT-4, Claude, and local models supported!
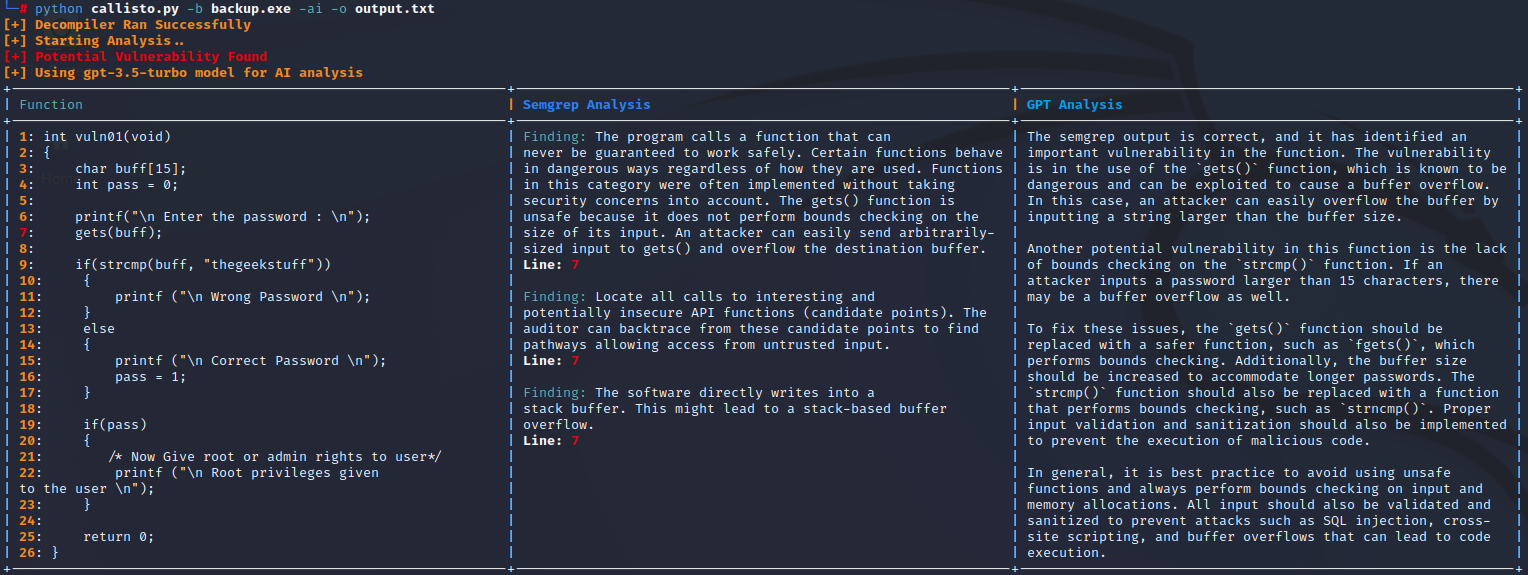 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
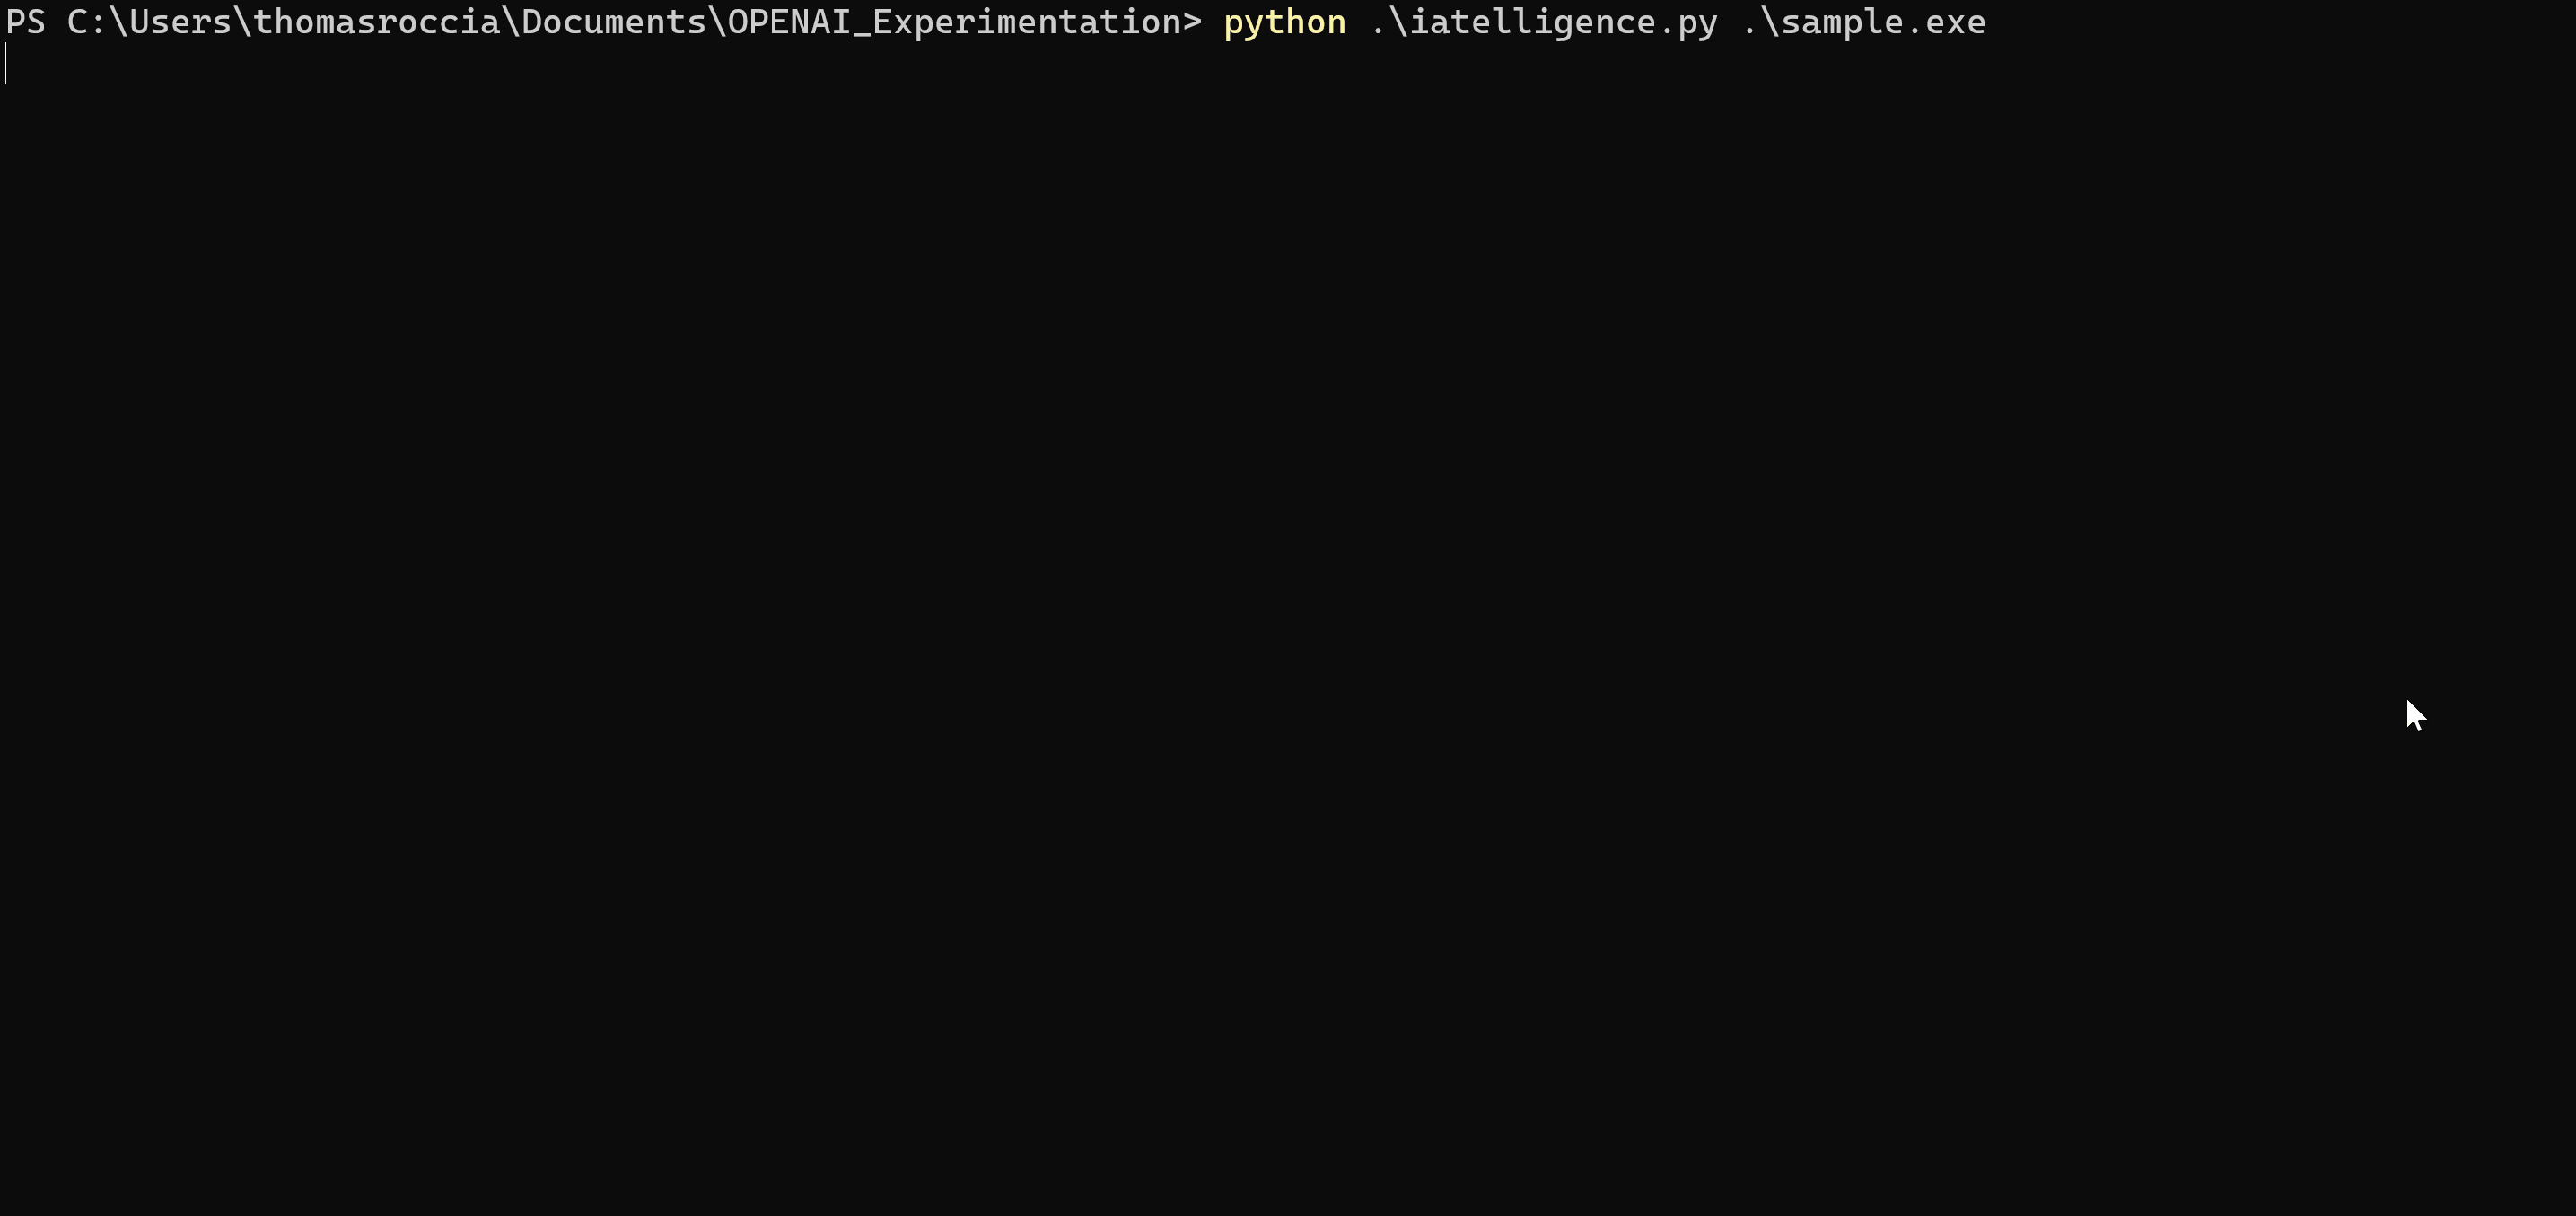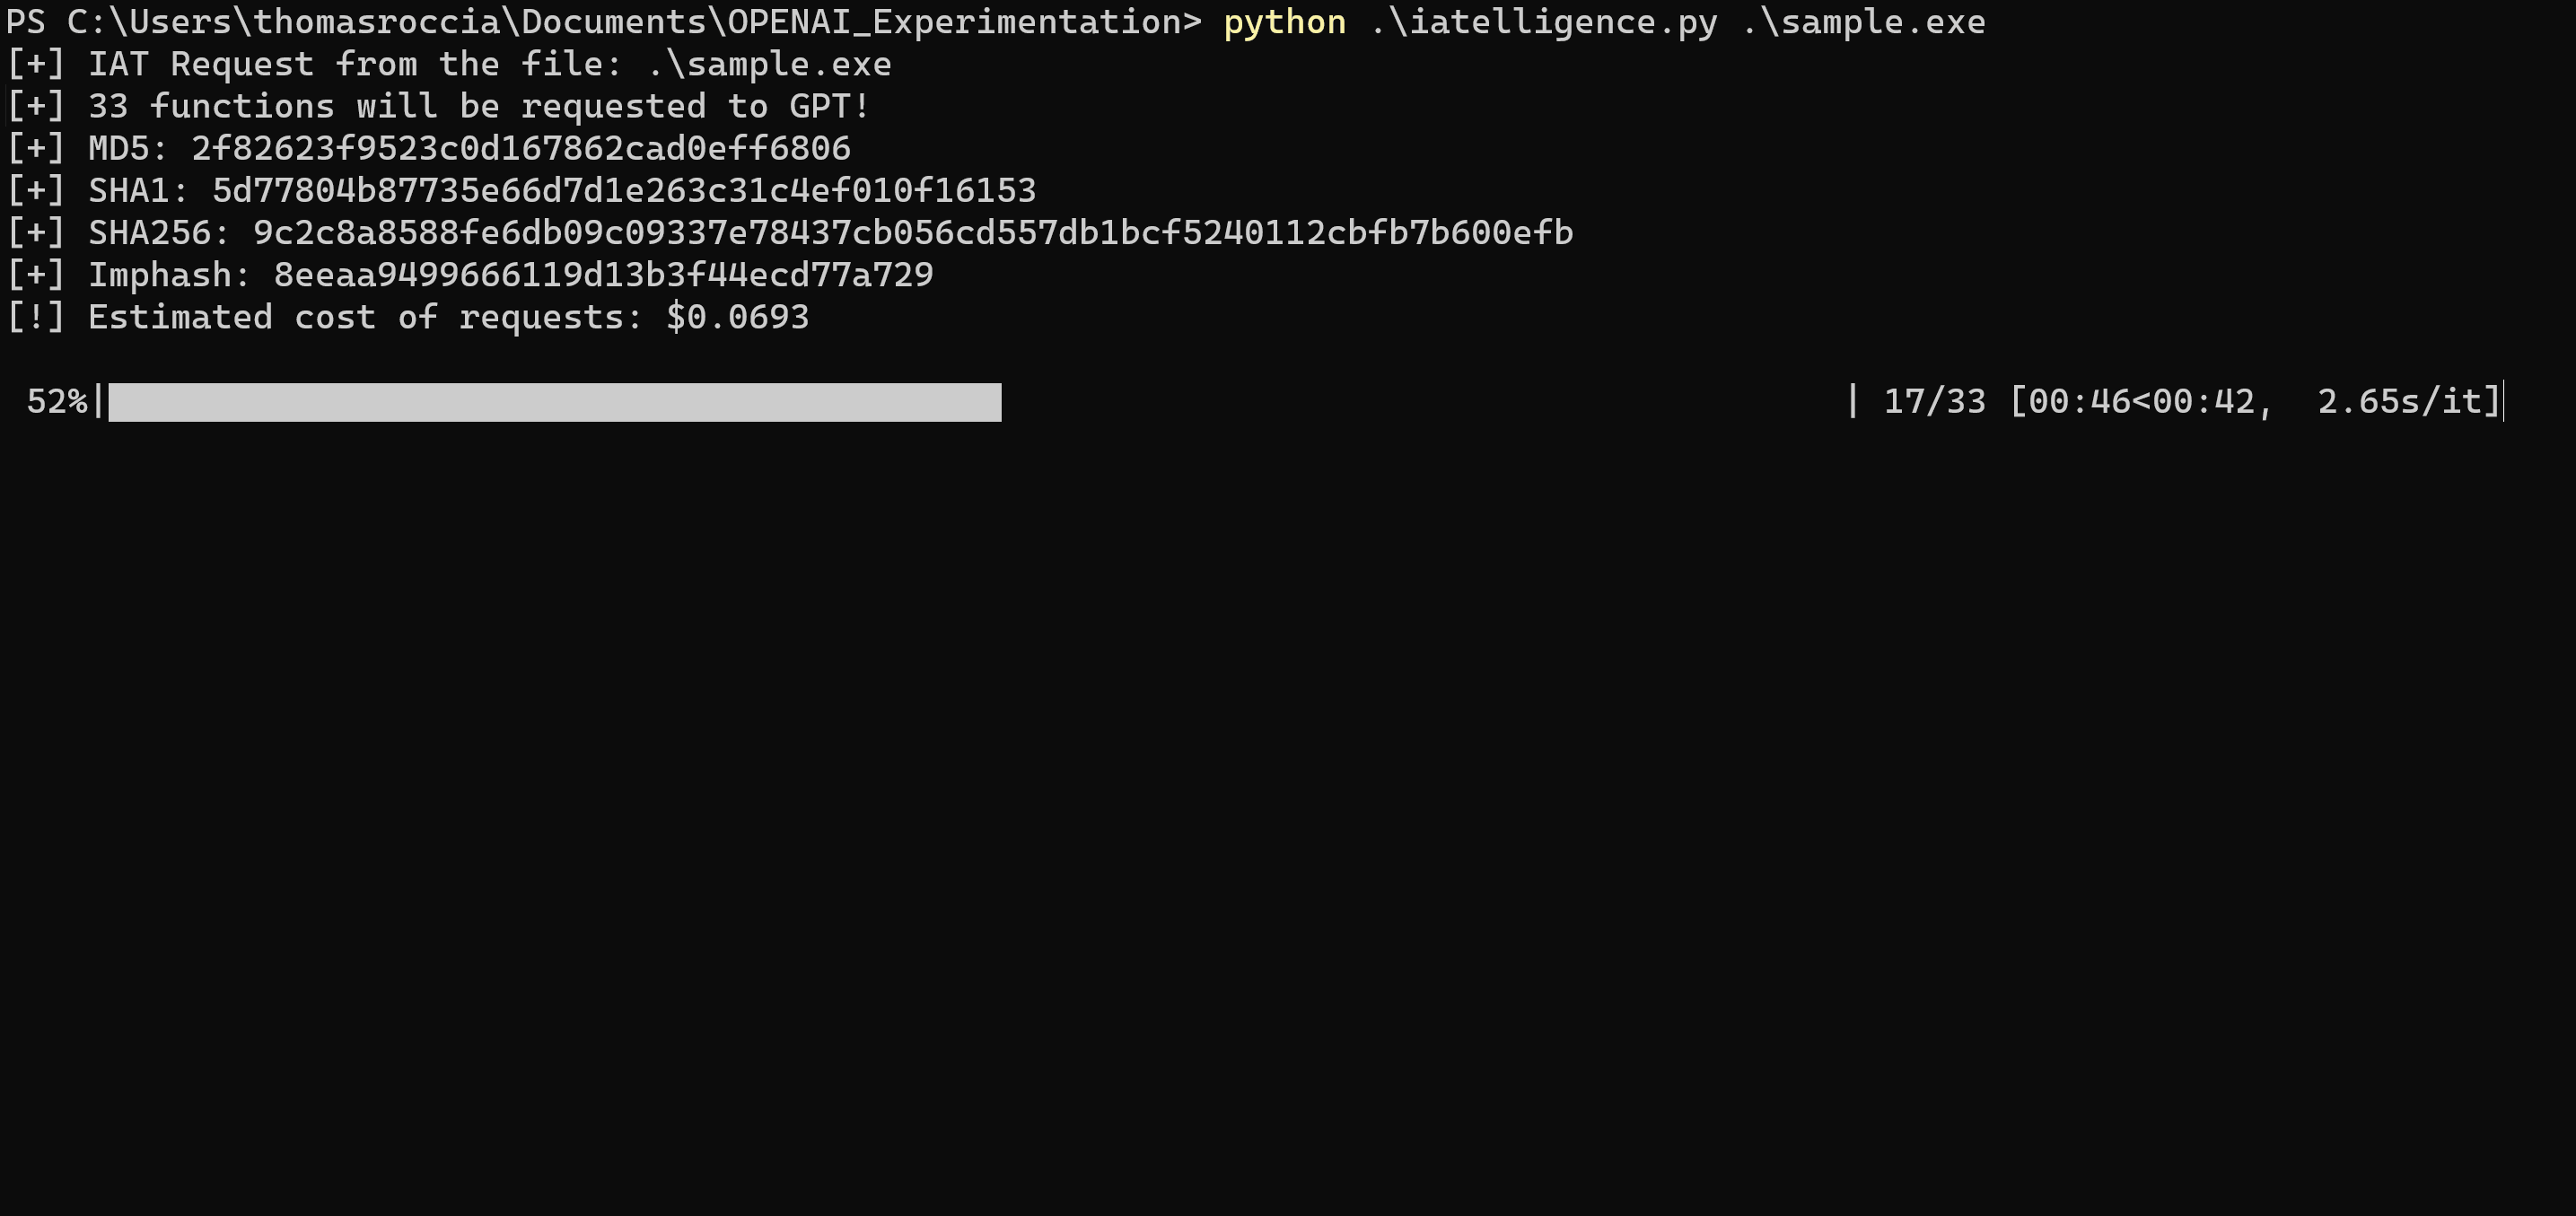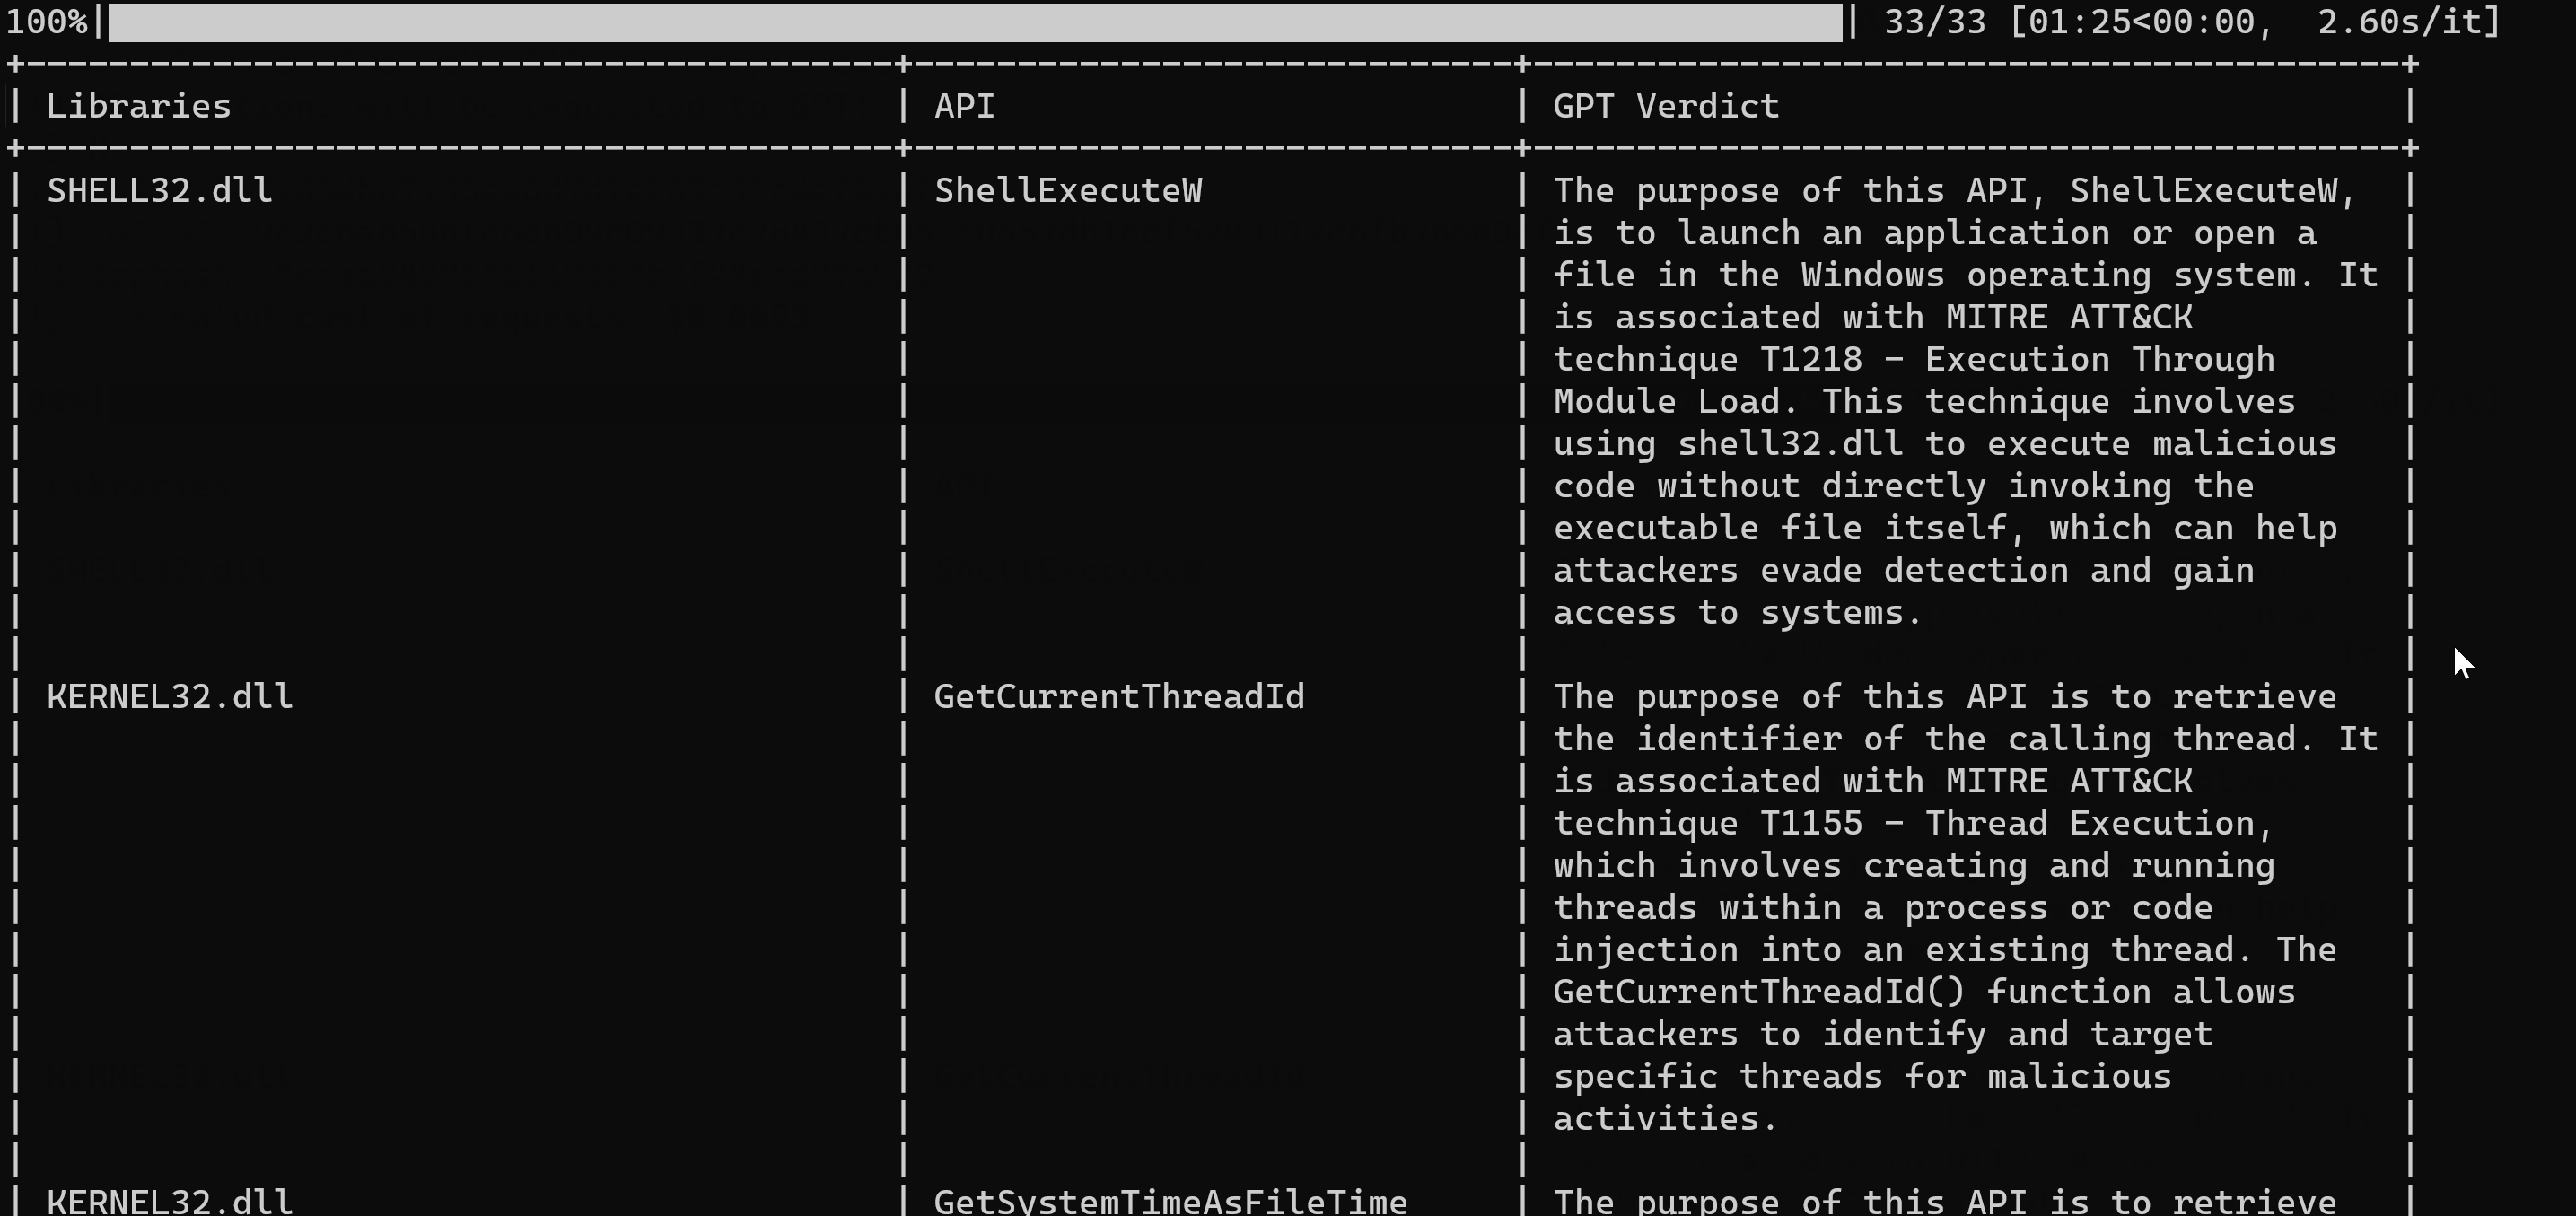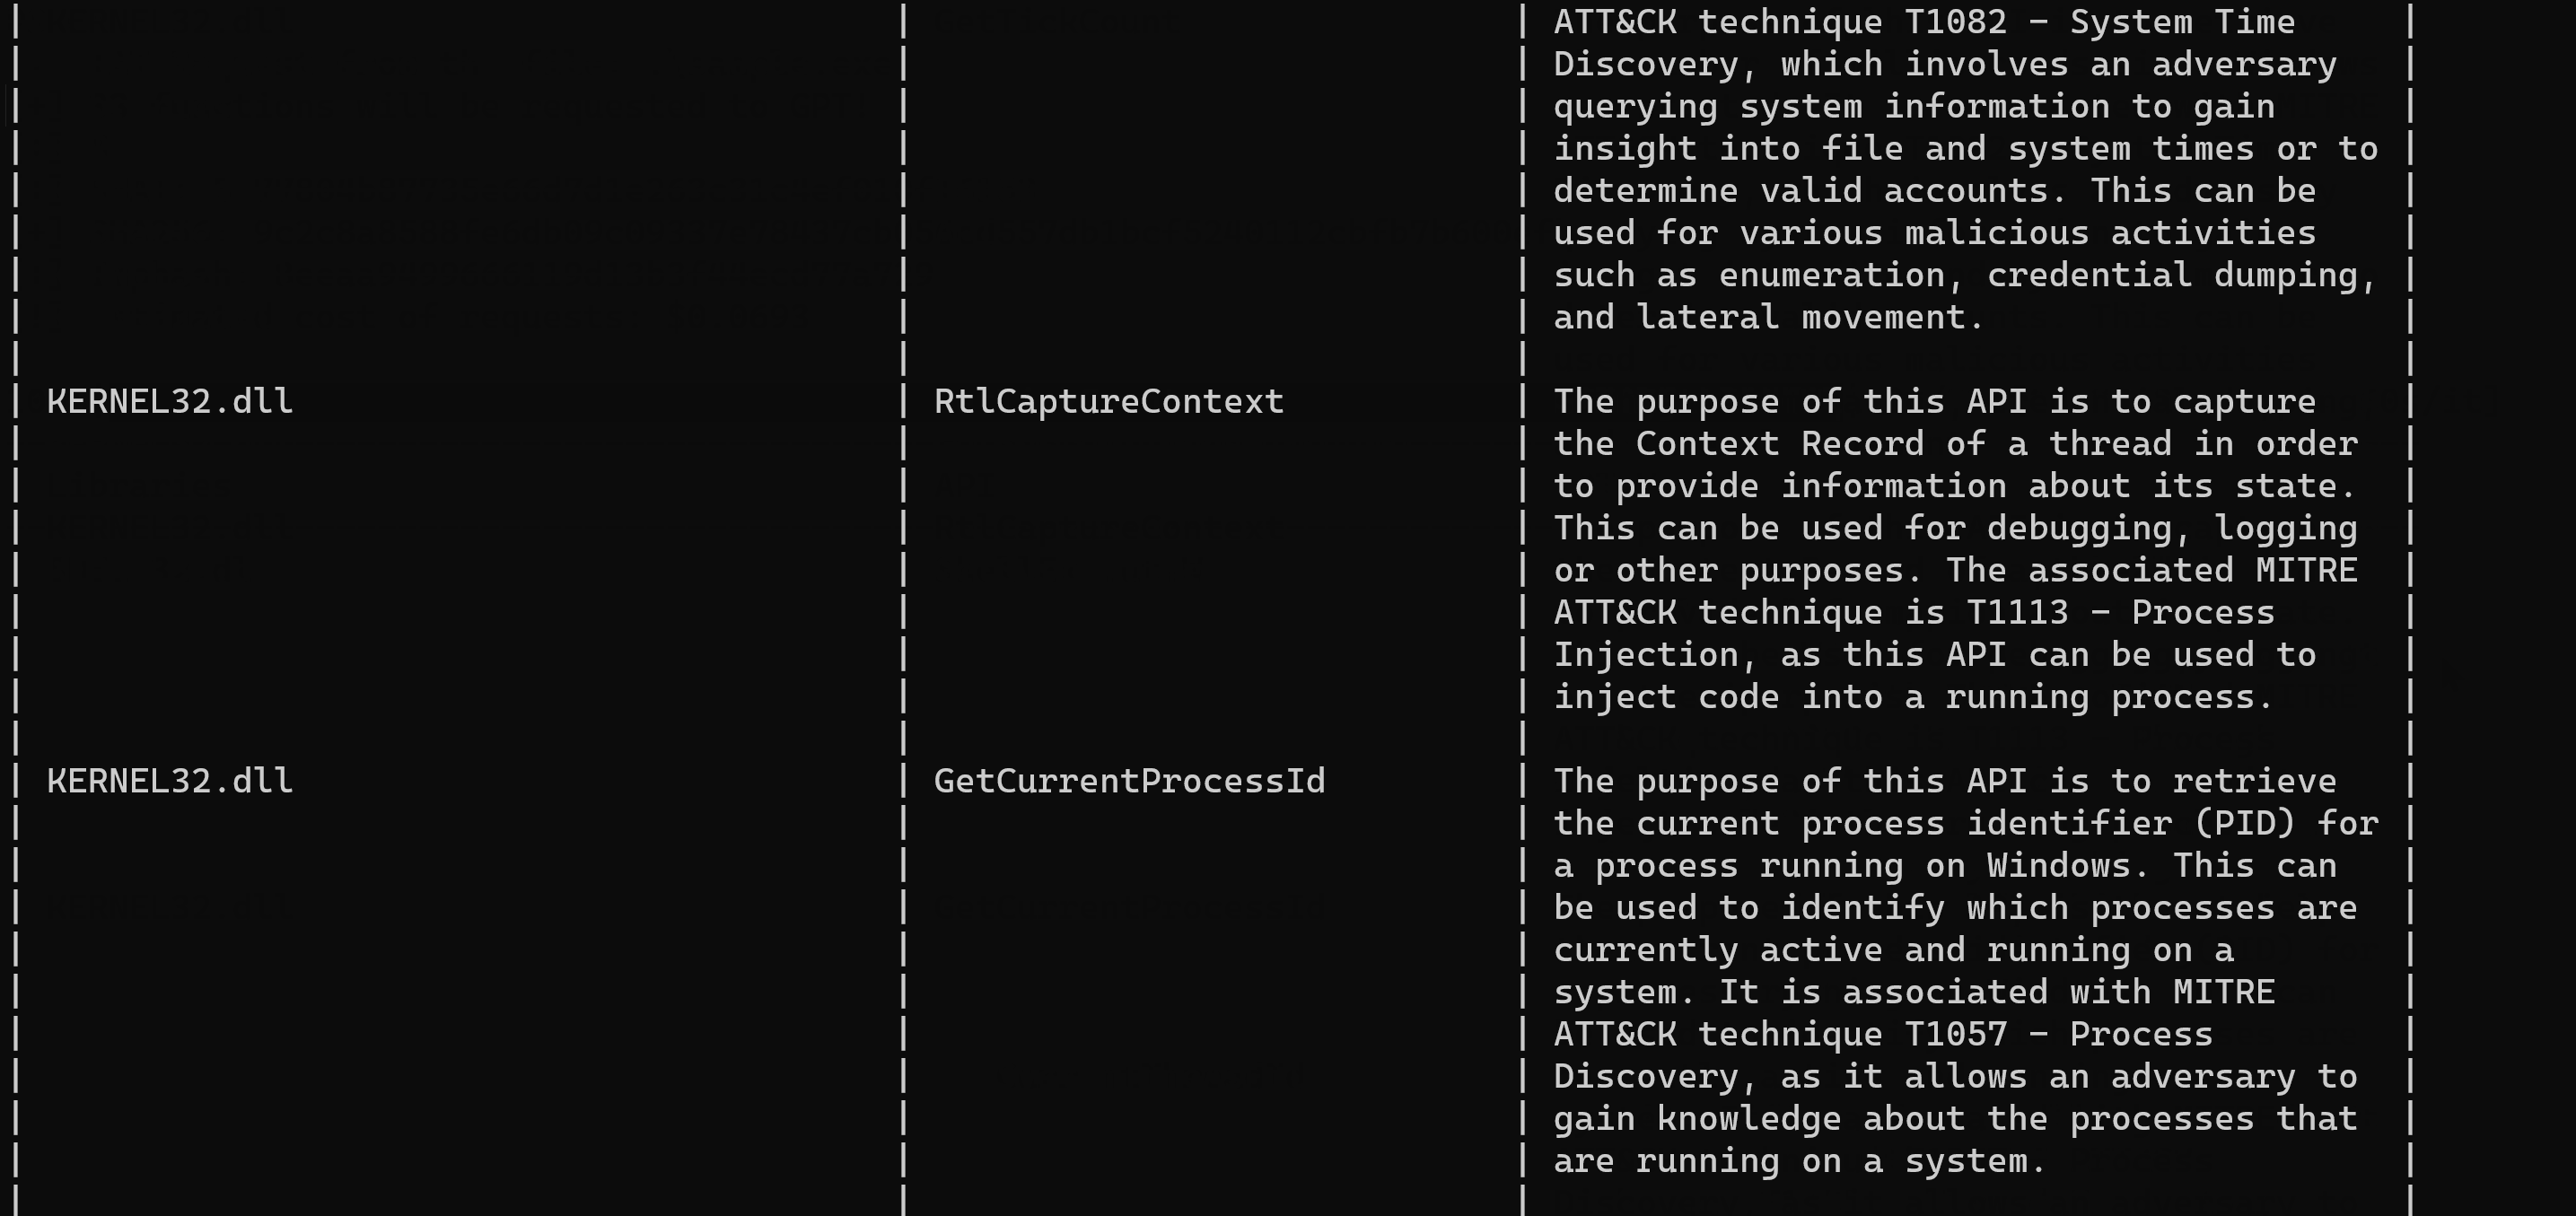 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 dnakov/r2d2
🤖🏴☠️ radare2 plugin for GPT-4 🦜. Solve crackmes automatically 🪄
 cpkt9762/ida-cli
Headless IDA Pro MCP server for AI-assisted binary analysis, powered by idalib
 evm-sec/high-pcode
Output high level Pcode (PcodeAST) in Ghidra
 binref/agent
Language Model Agent Instructions for Binary Refinery
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…
 20urc3/sekiryu
Comprehensive toolkit for Ghidra headless.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy