

skills
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
ai-assisted-reversingcode-analysiscurated-resources+8
7.2k
trailofbits/skillsTrail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
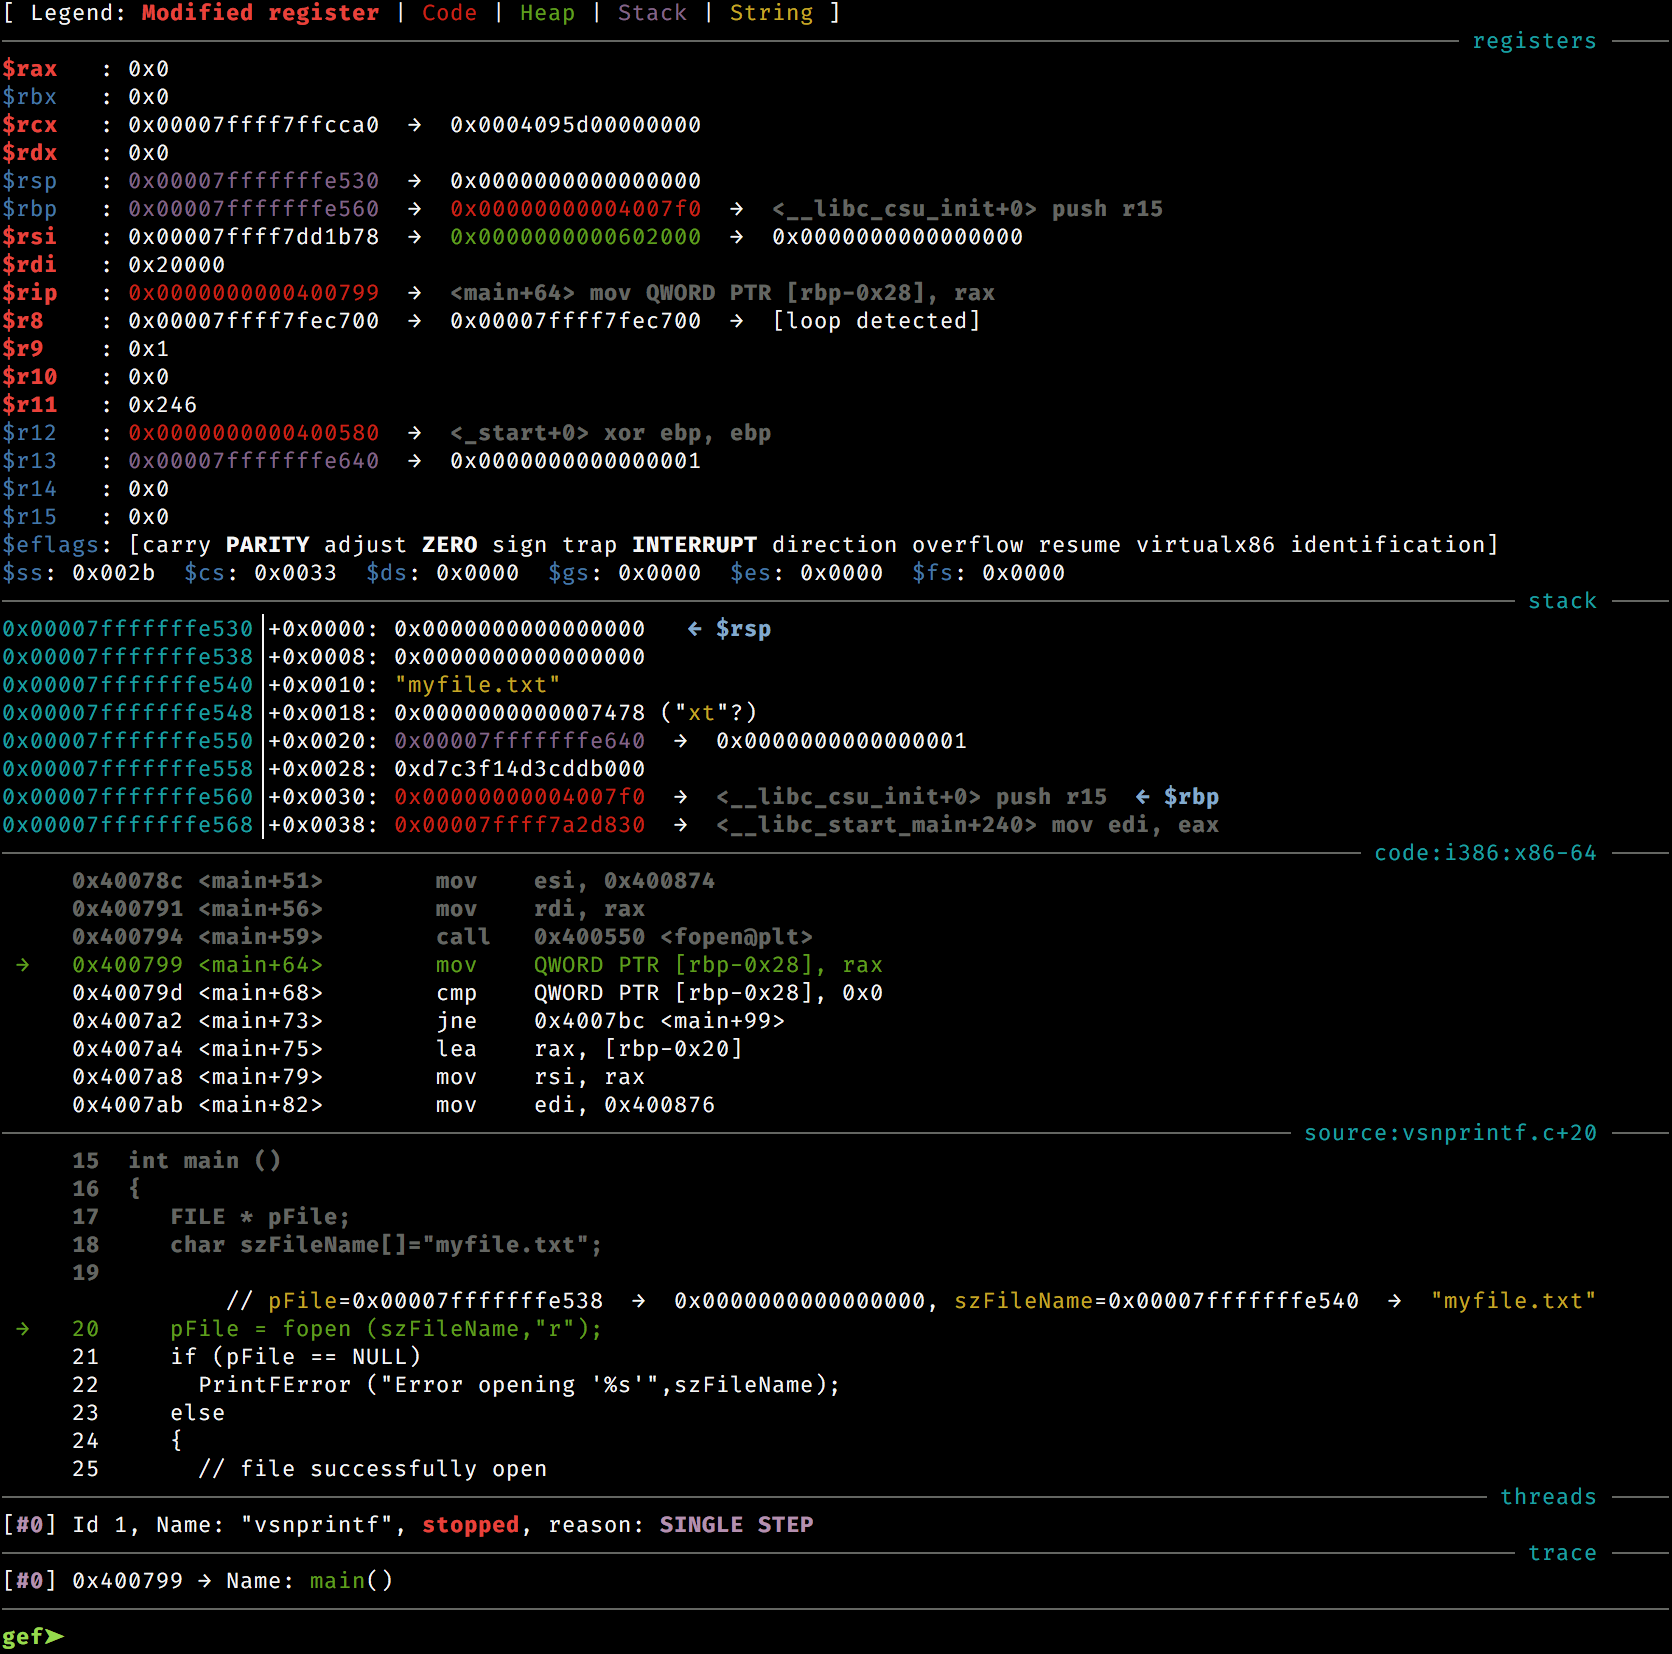 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 lauriewired/ghidramcp
MCP Server for Ghidra
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
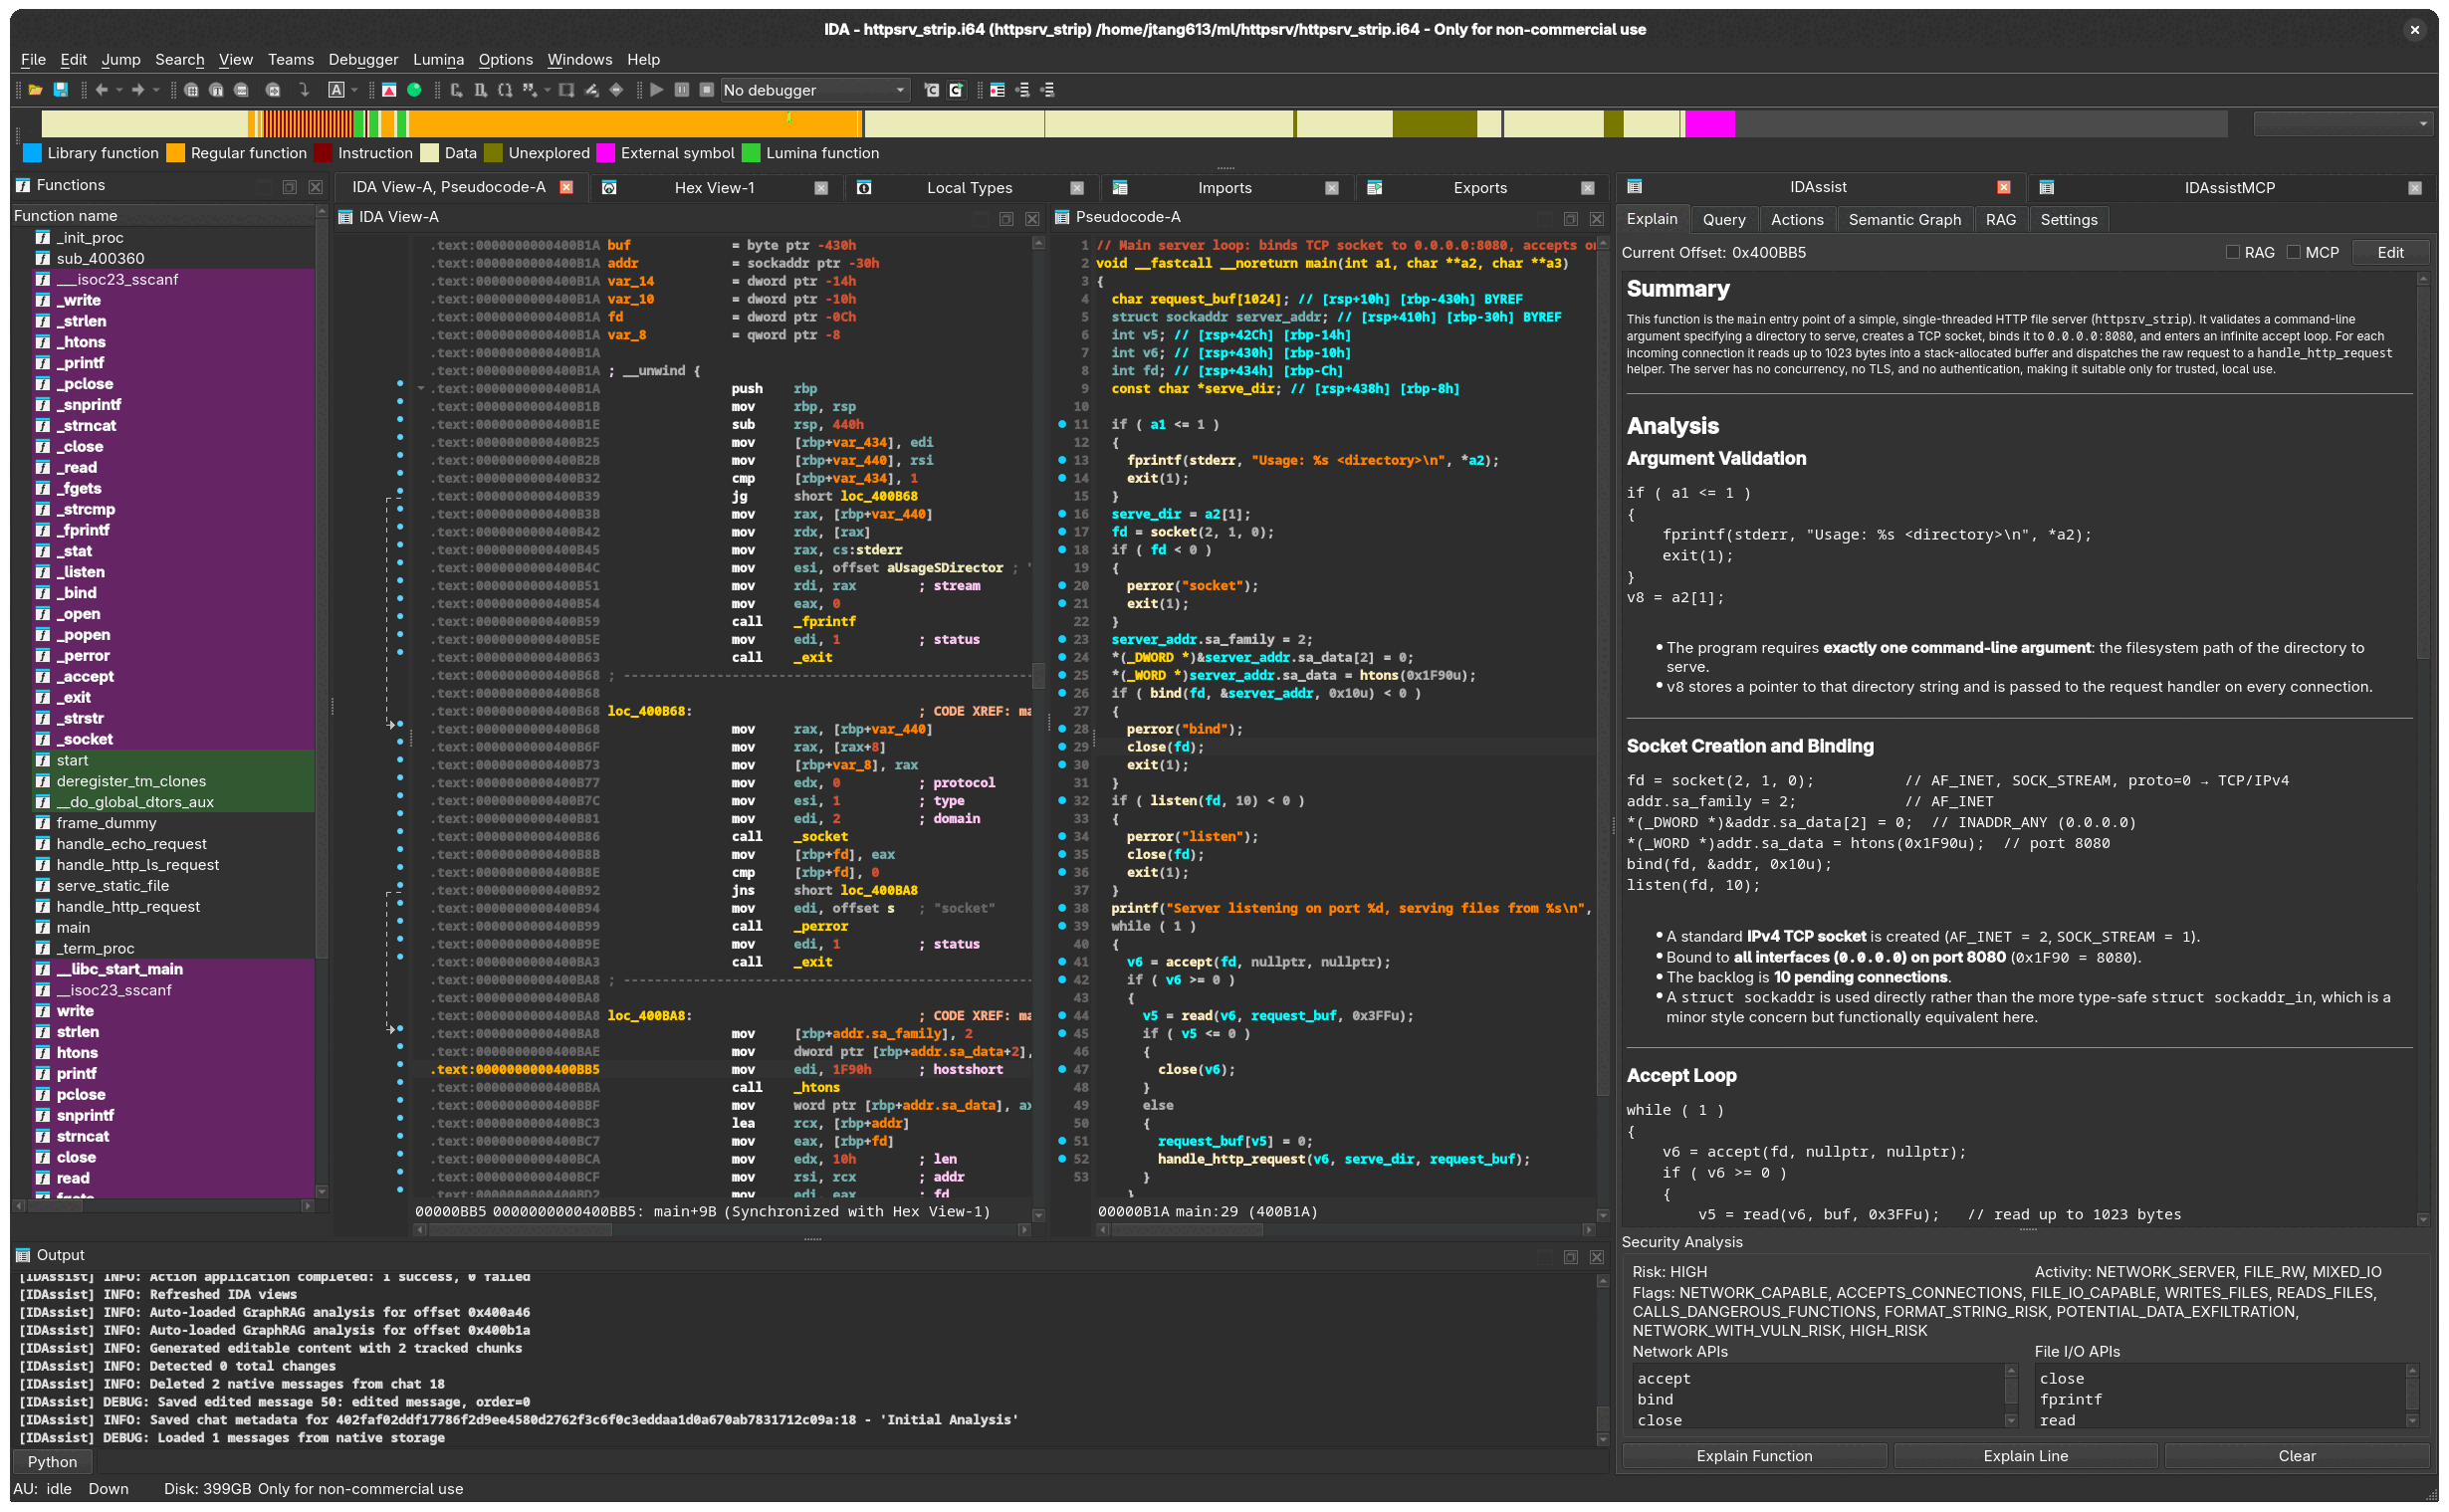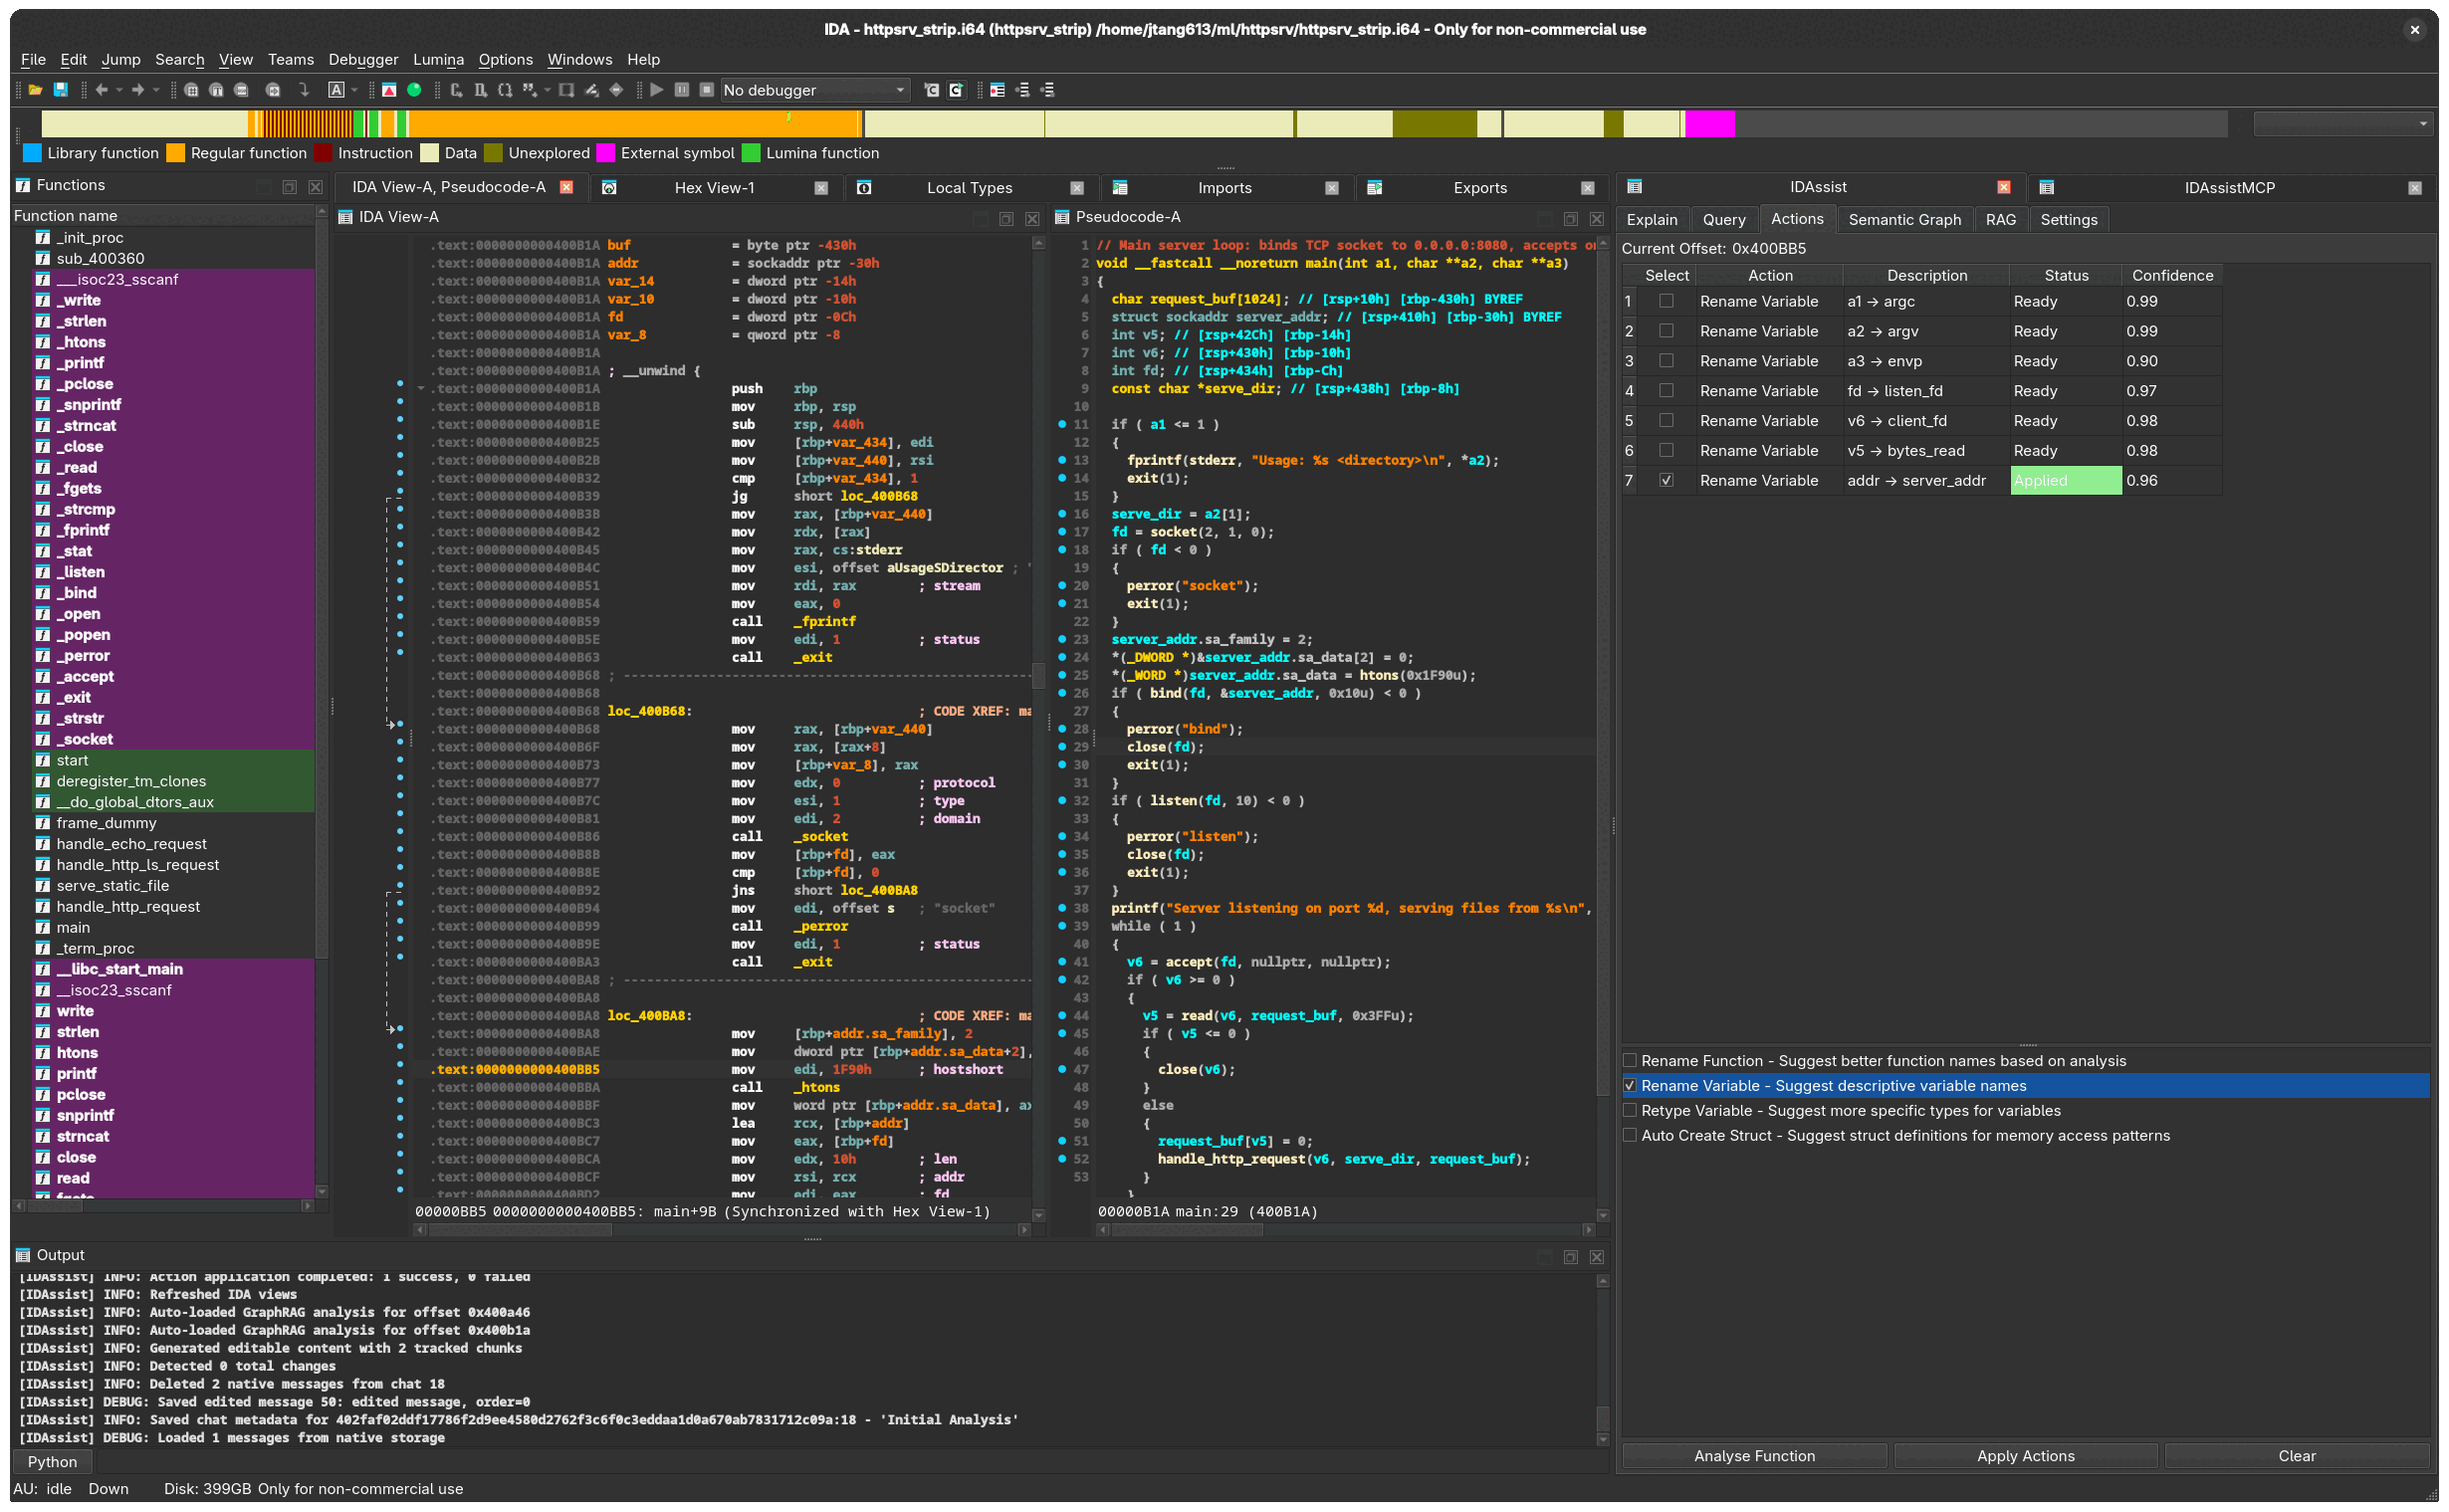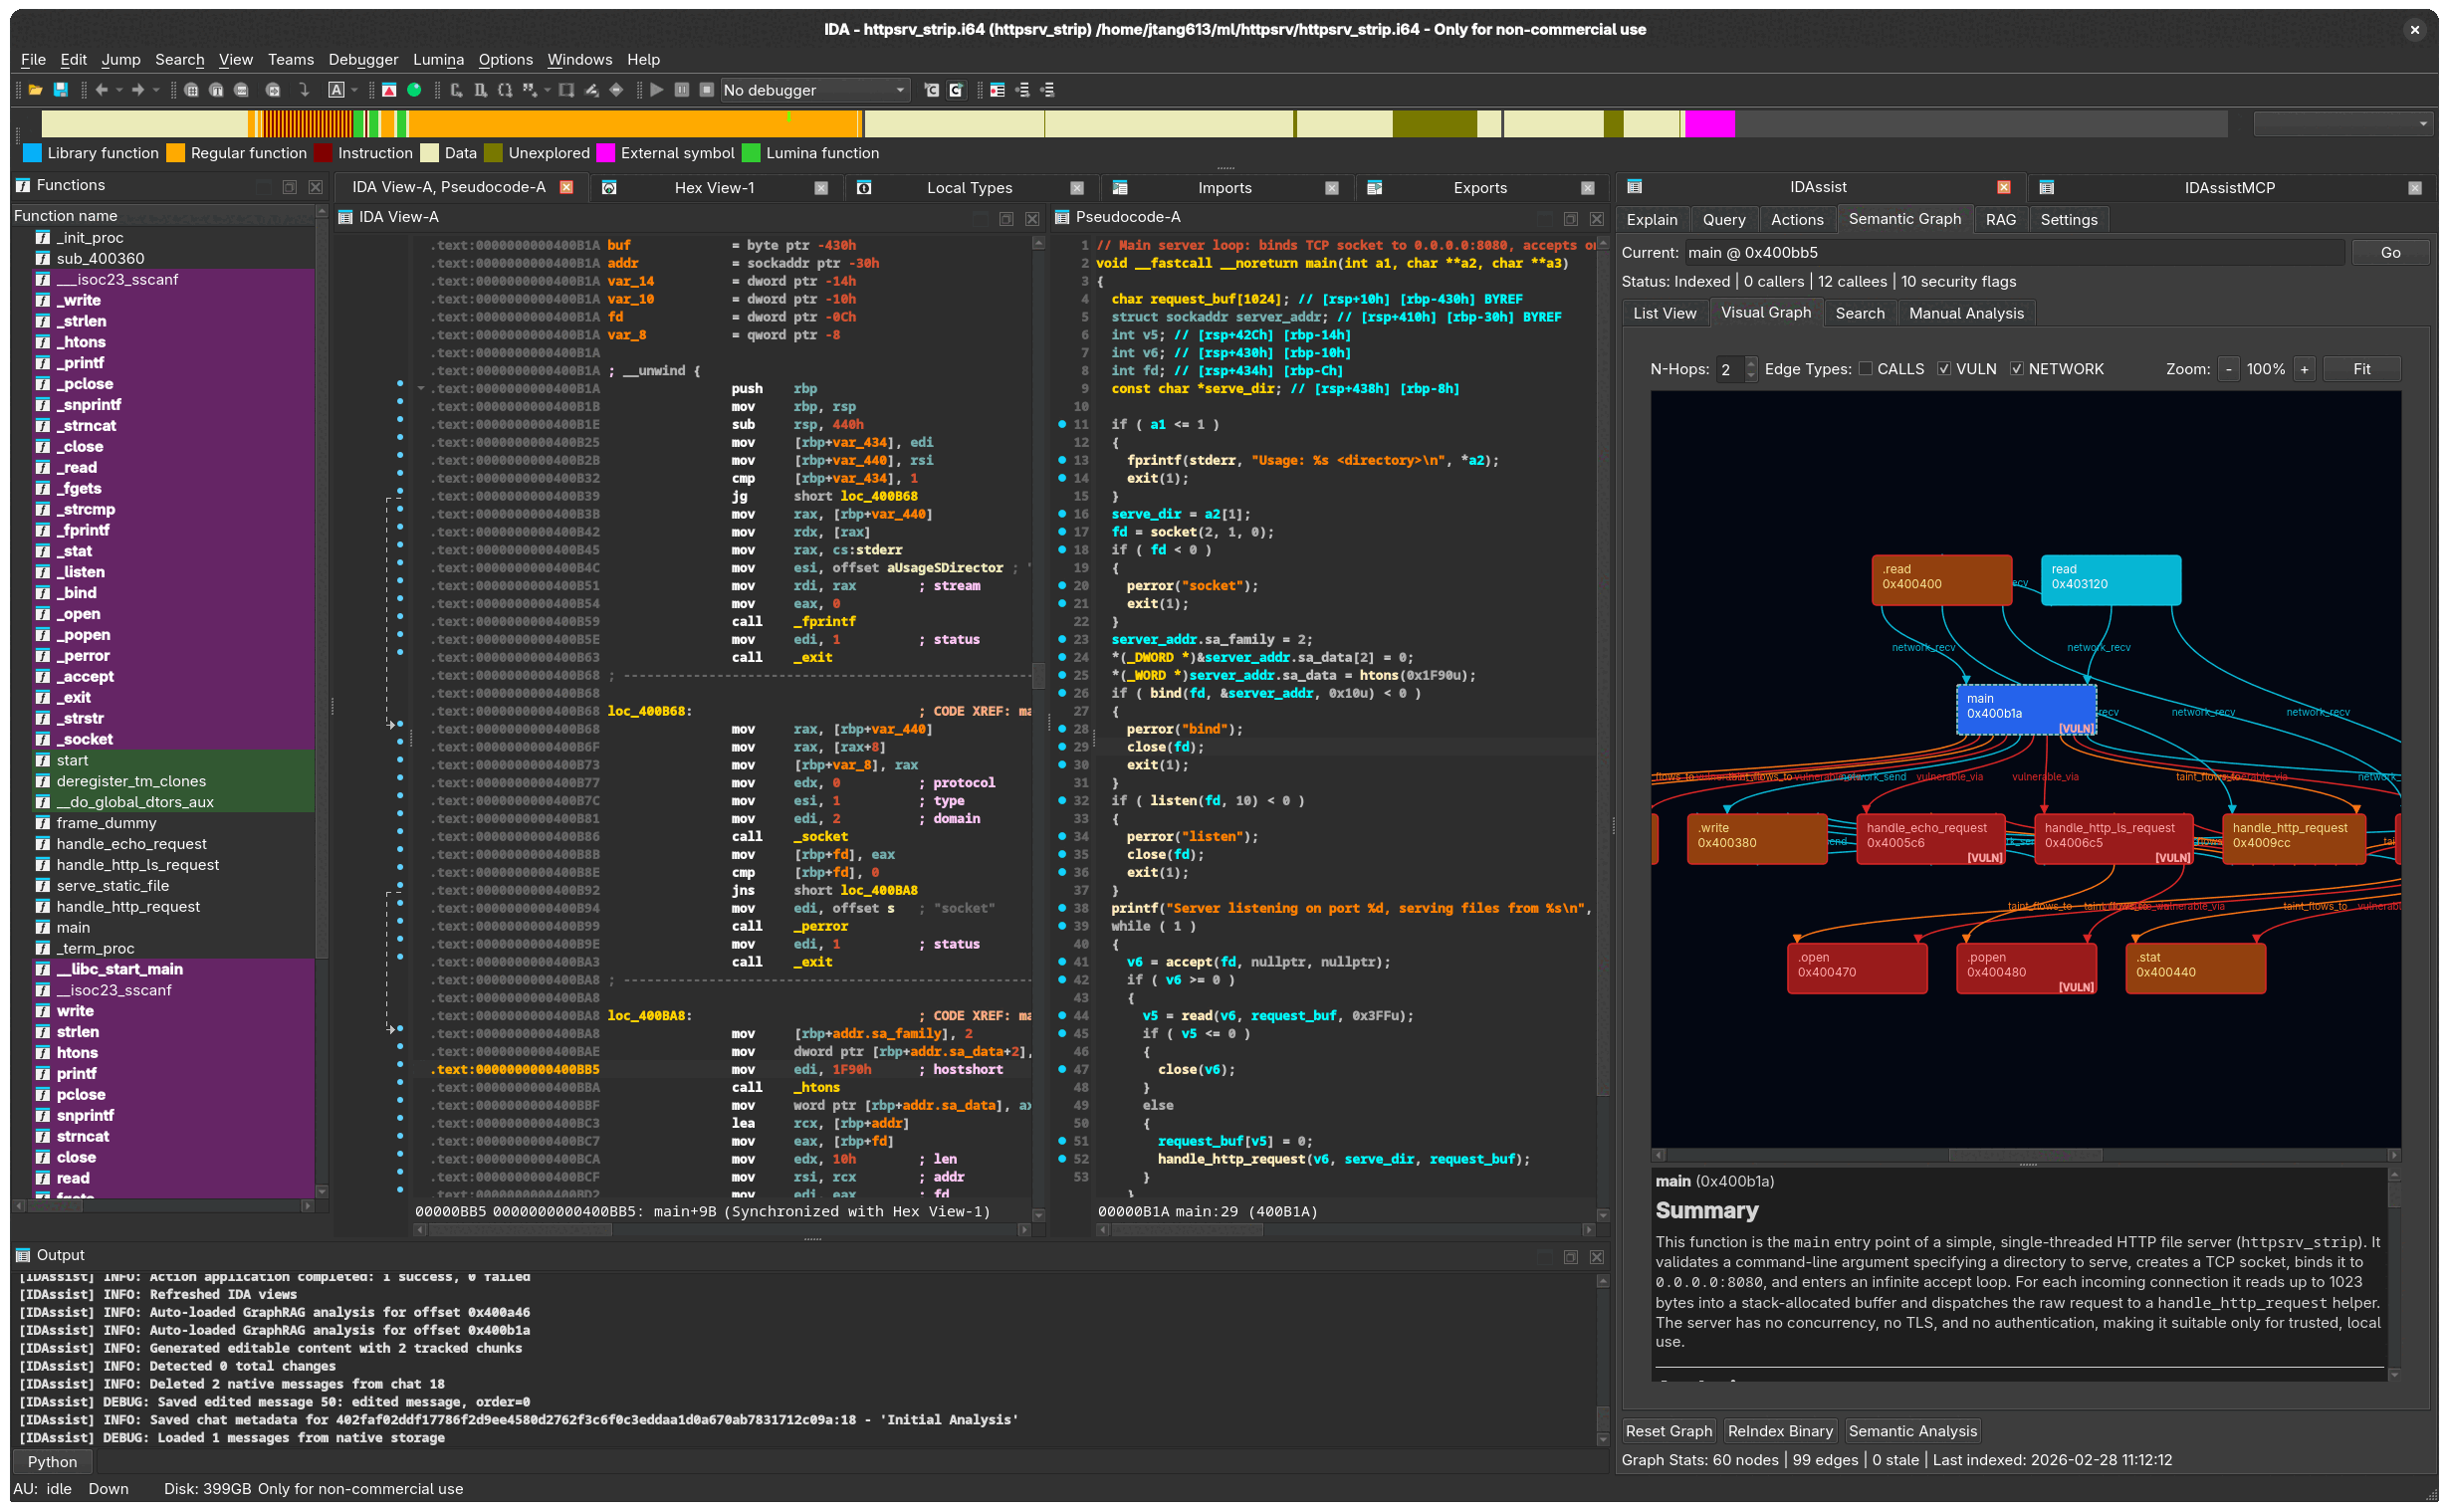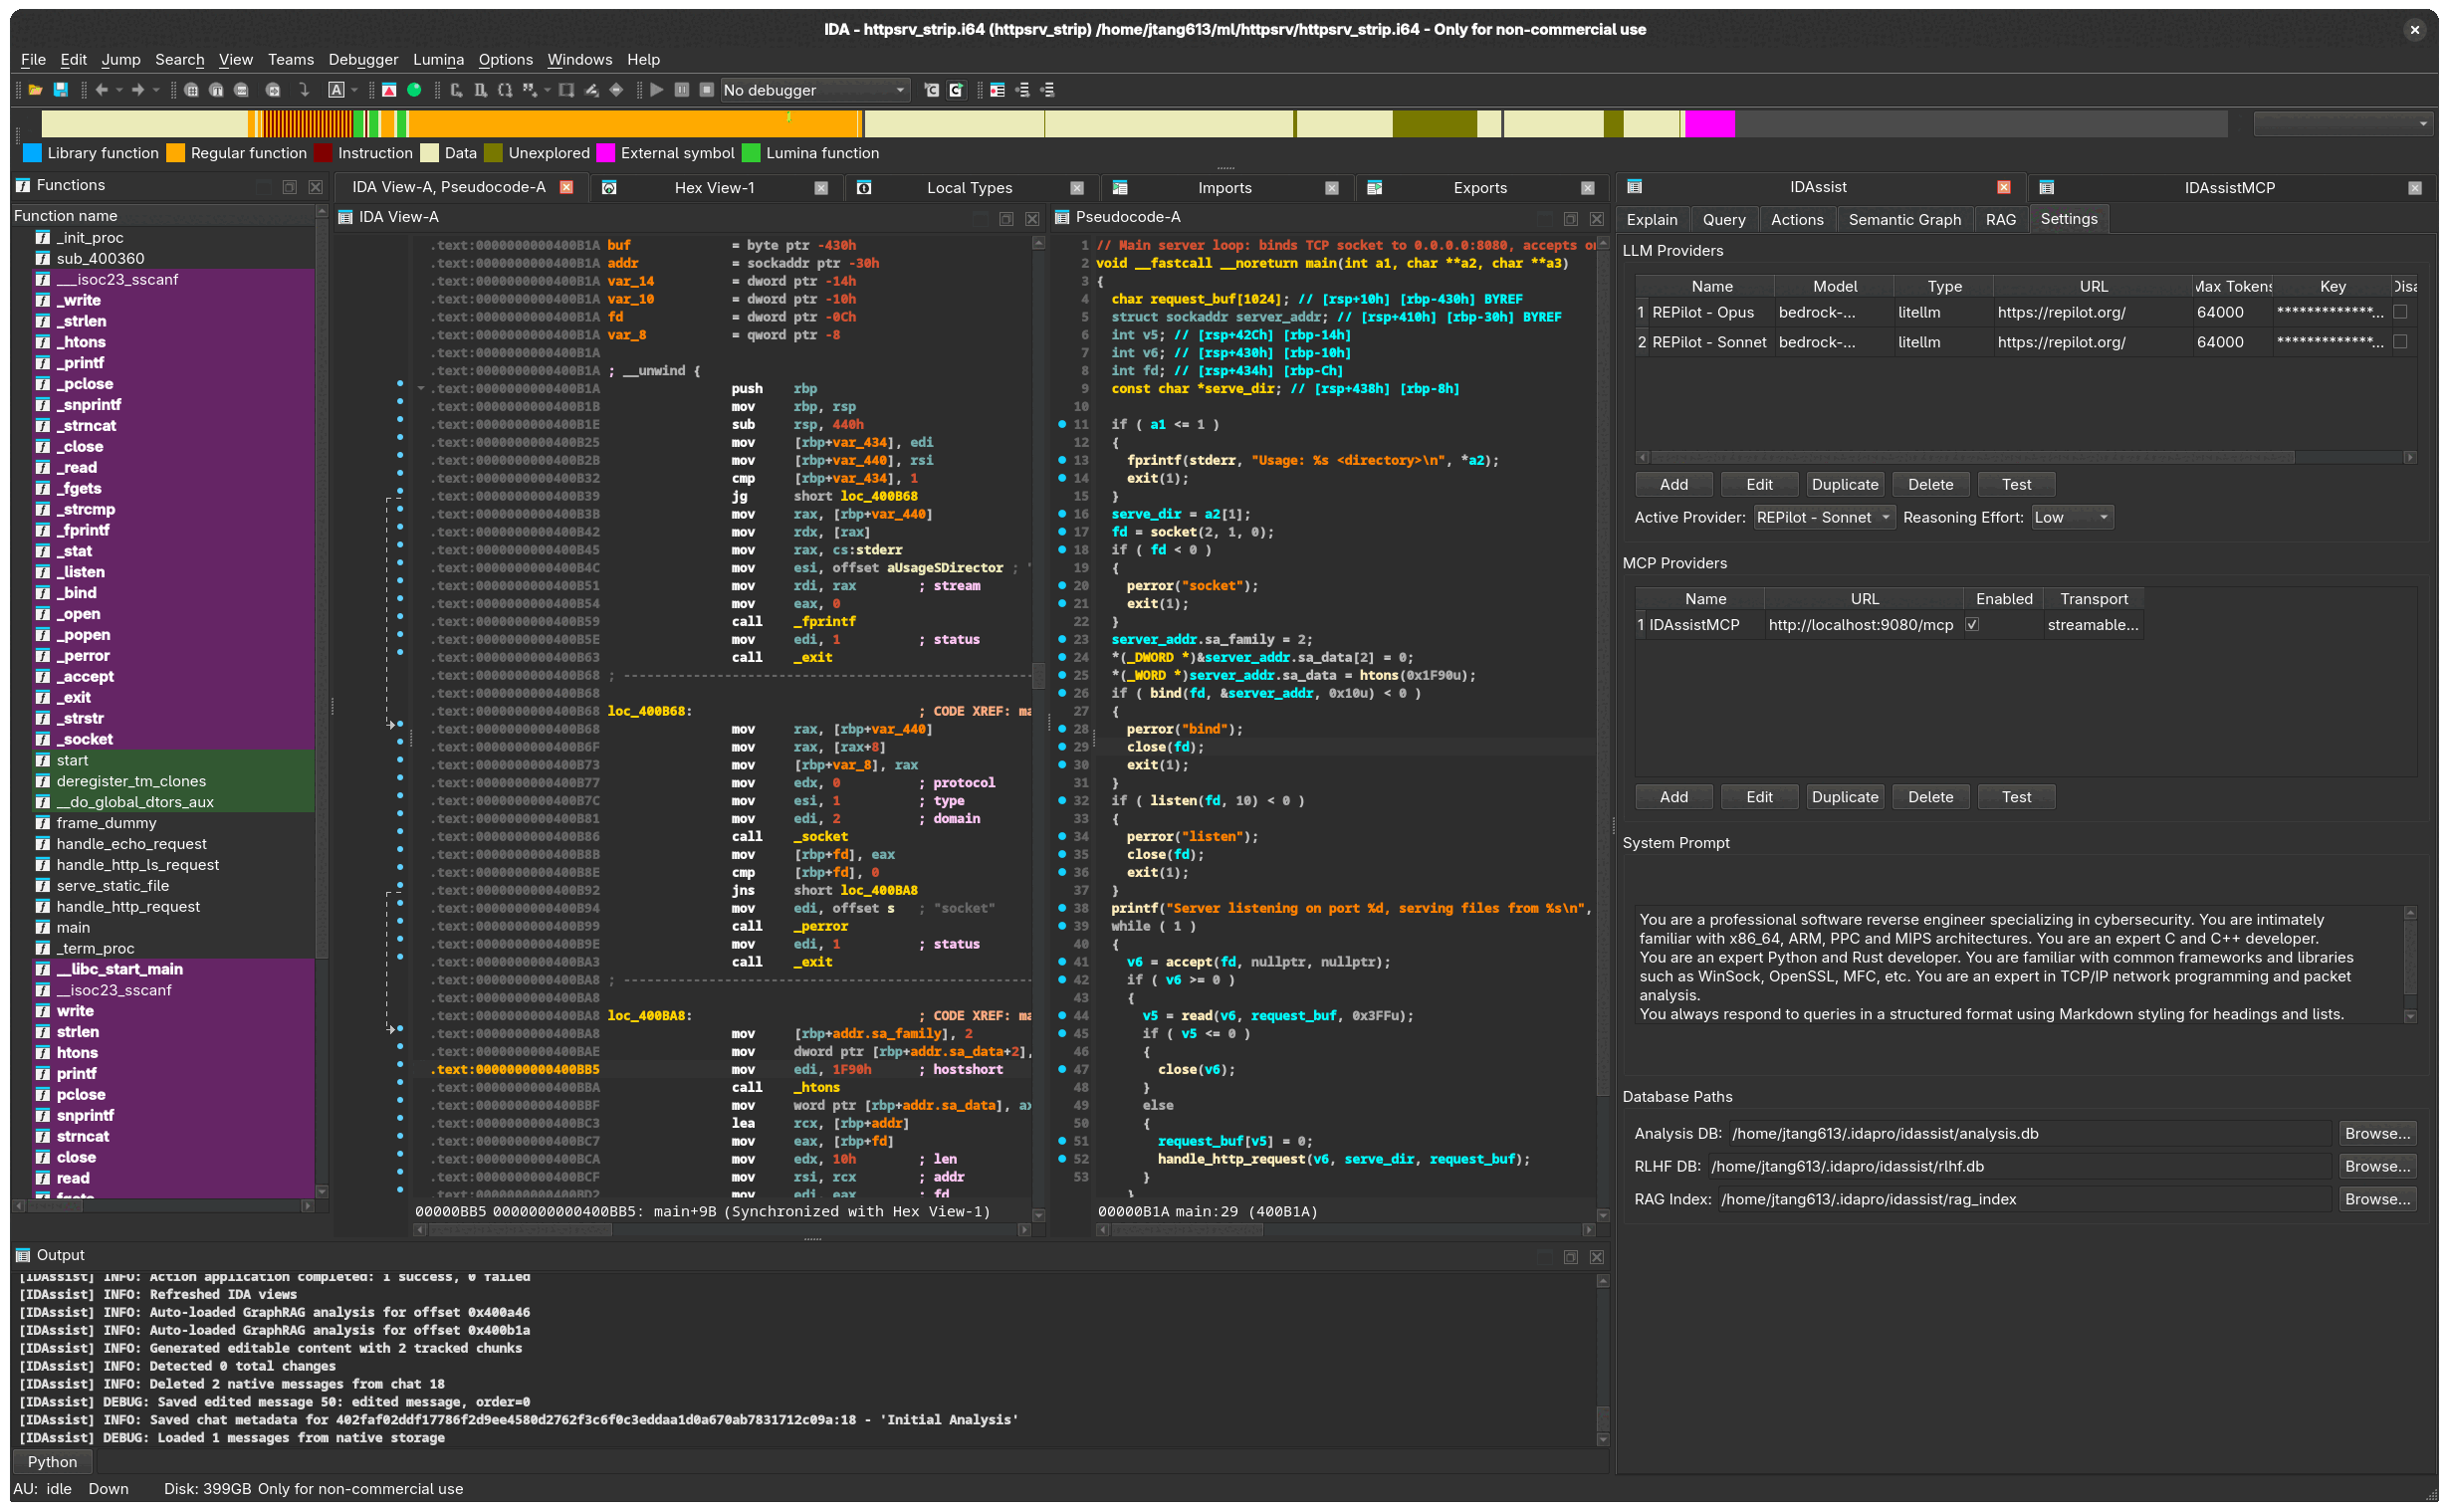 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 allthingsida/idasql
Vibe Reverse Engineer with IDA SQL: An interface for IDA in SQL via live virtual tables
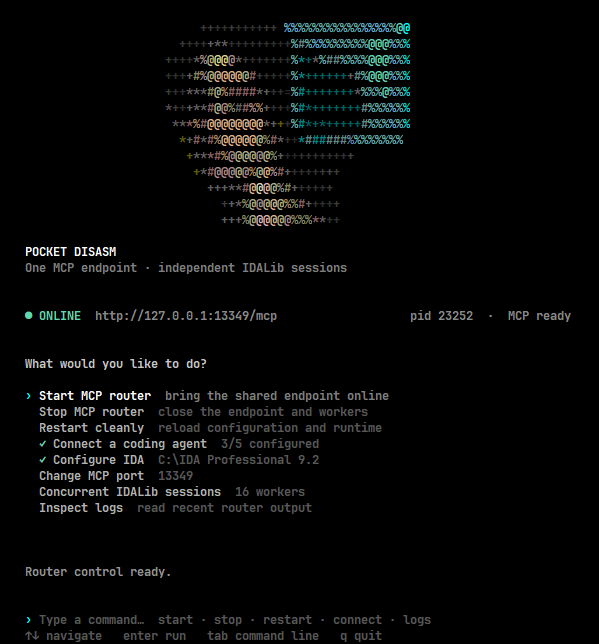 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
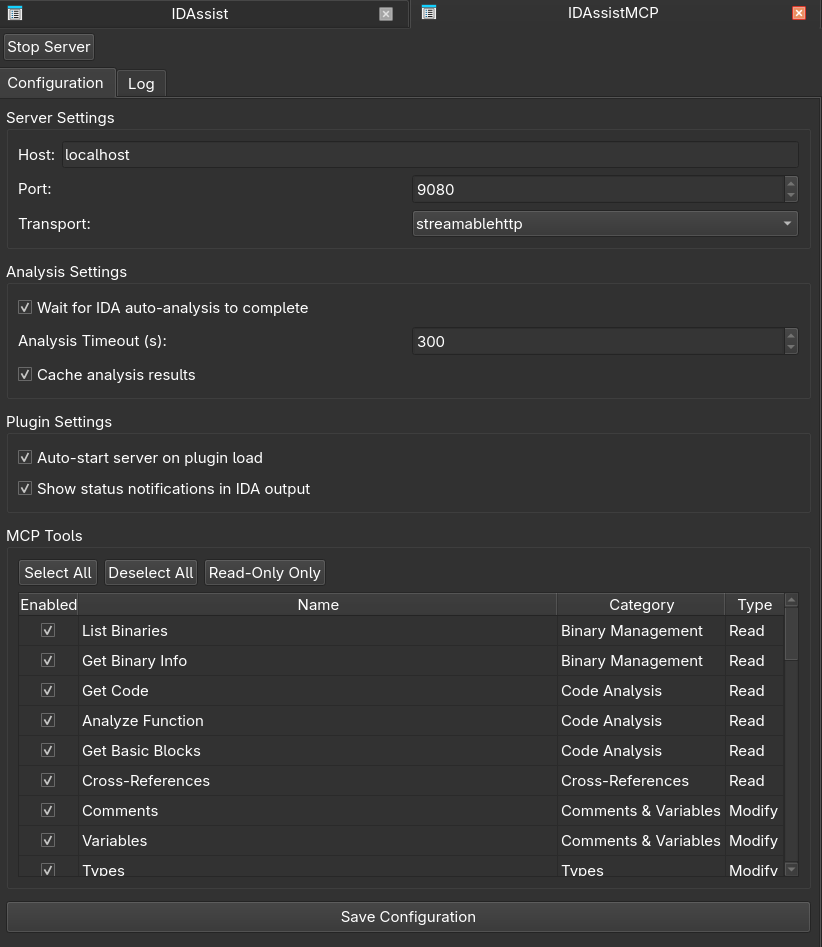 symgraph/idassistmcp
Standalone MCP server plugin for IDA Pro.
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
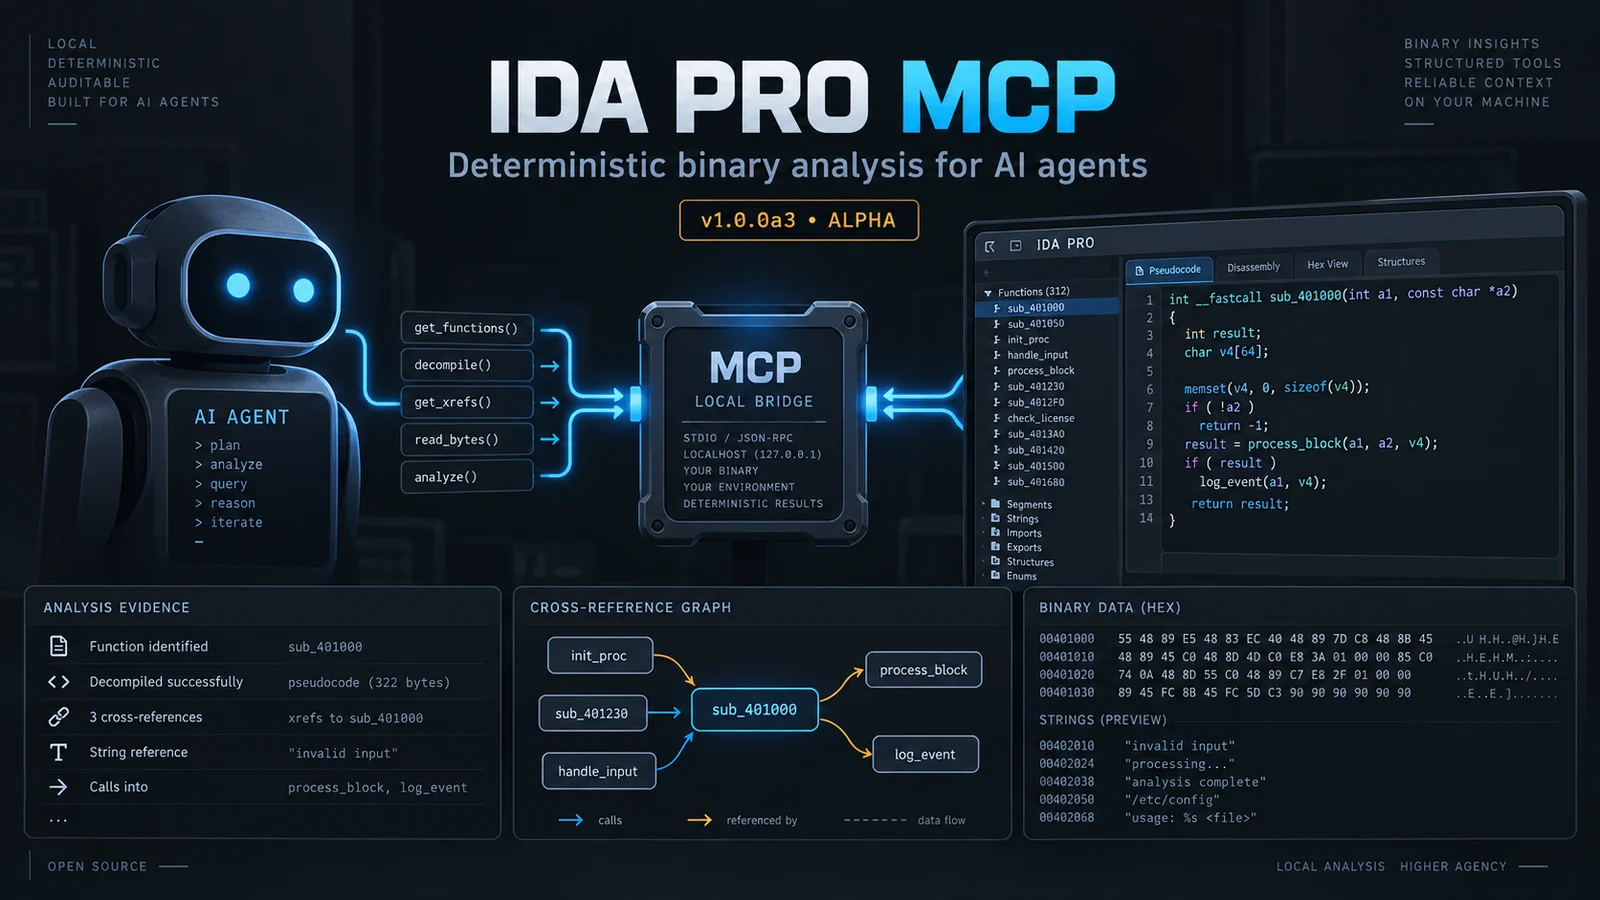 grecandrei/ida-pro-mcp
Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP