

Lockbit3.0-MpClient-Defender-PoC
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
adversarial-attackexploitationmalware-analysis+2
175
sh0ckfr/lockbit3.0-mpclient-defender-pocLockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
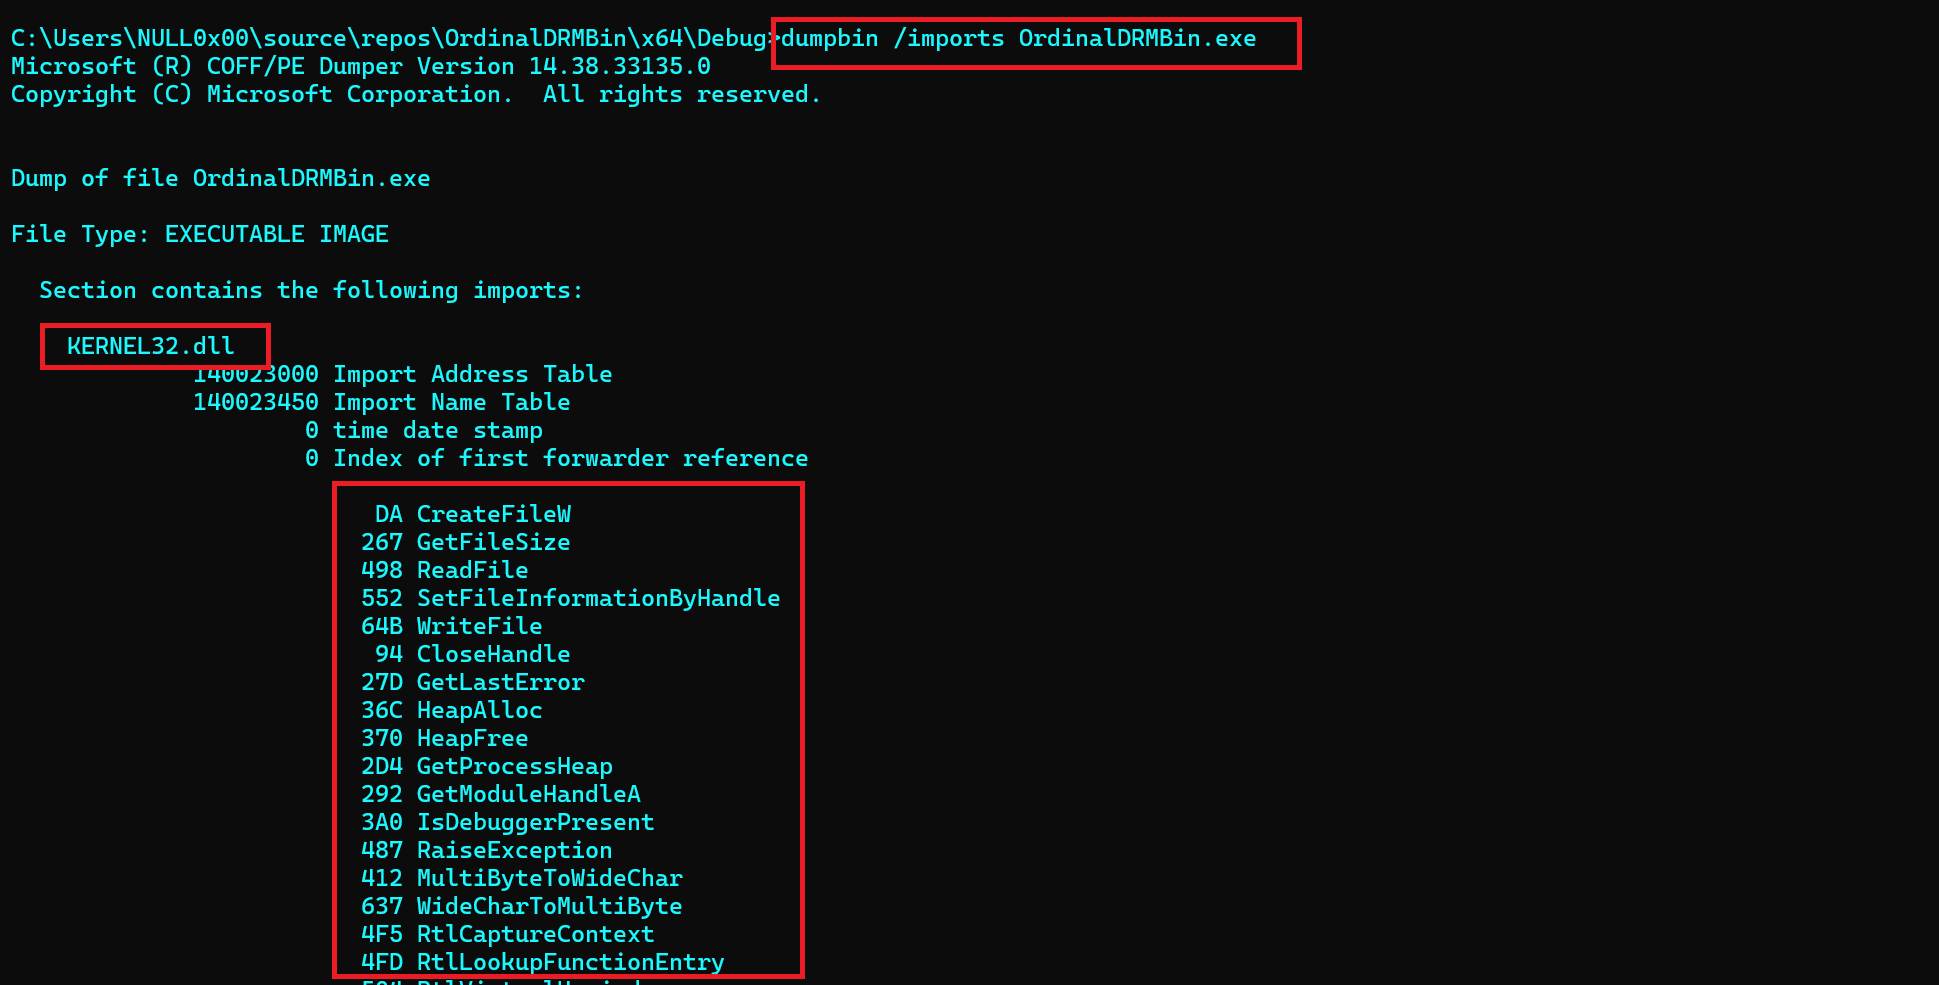 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
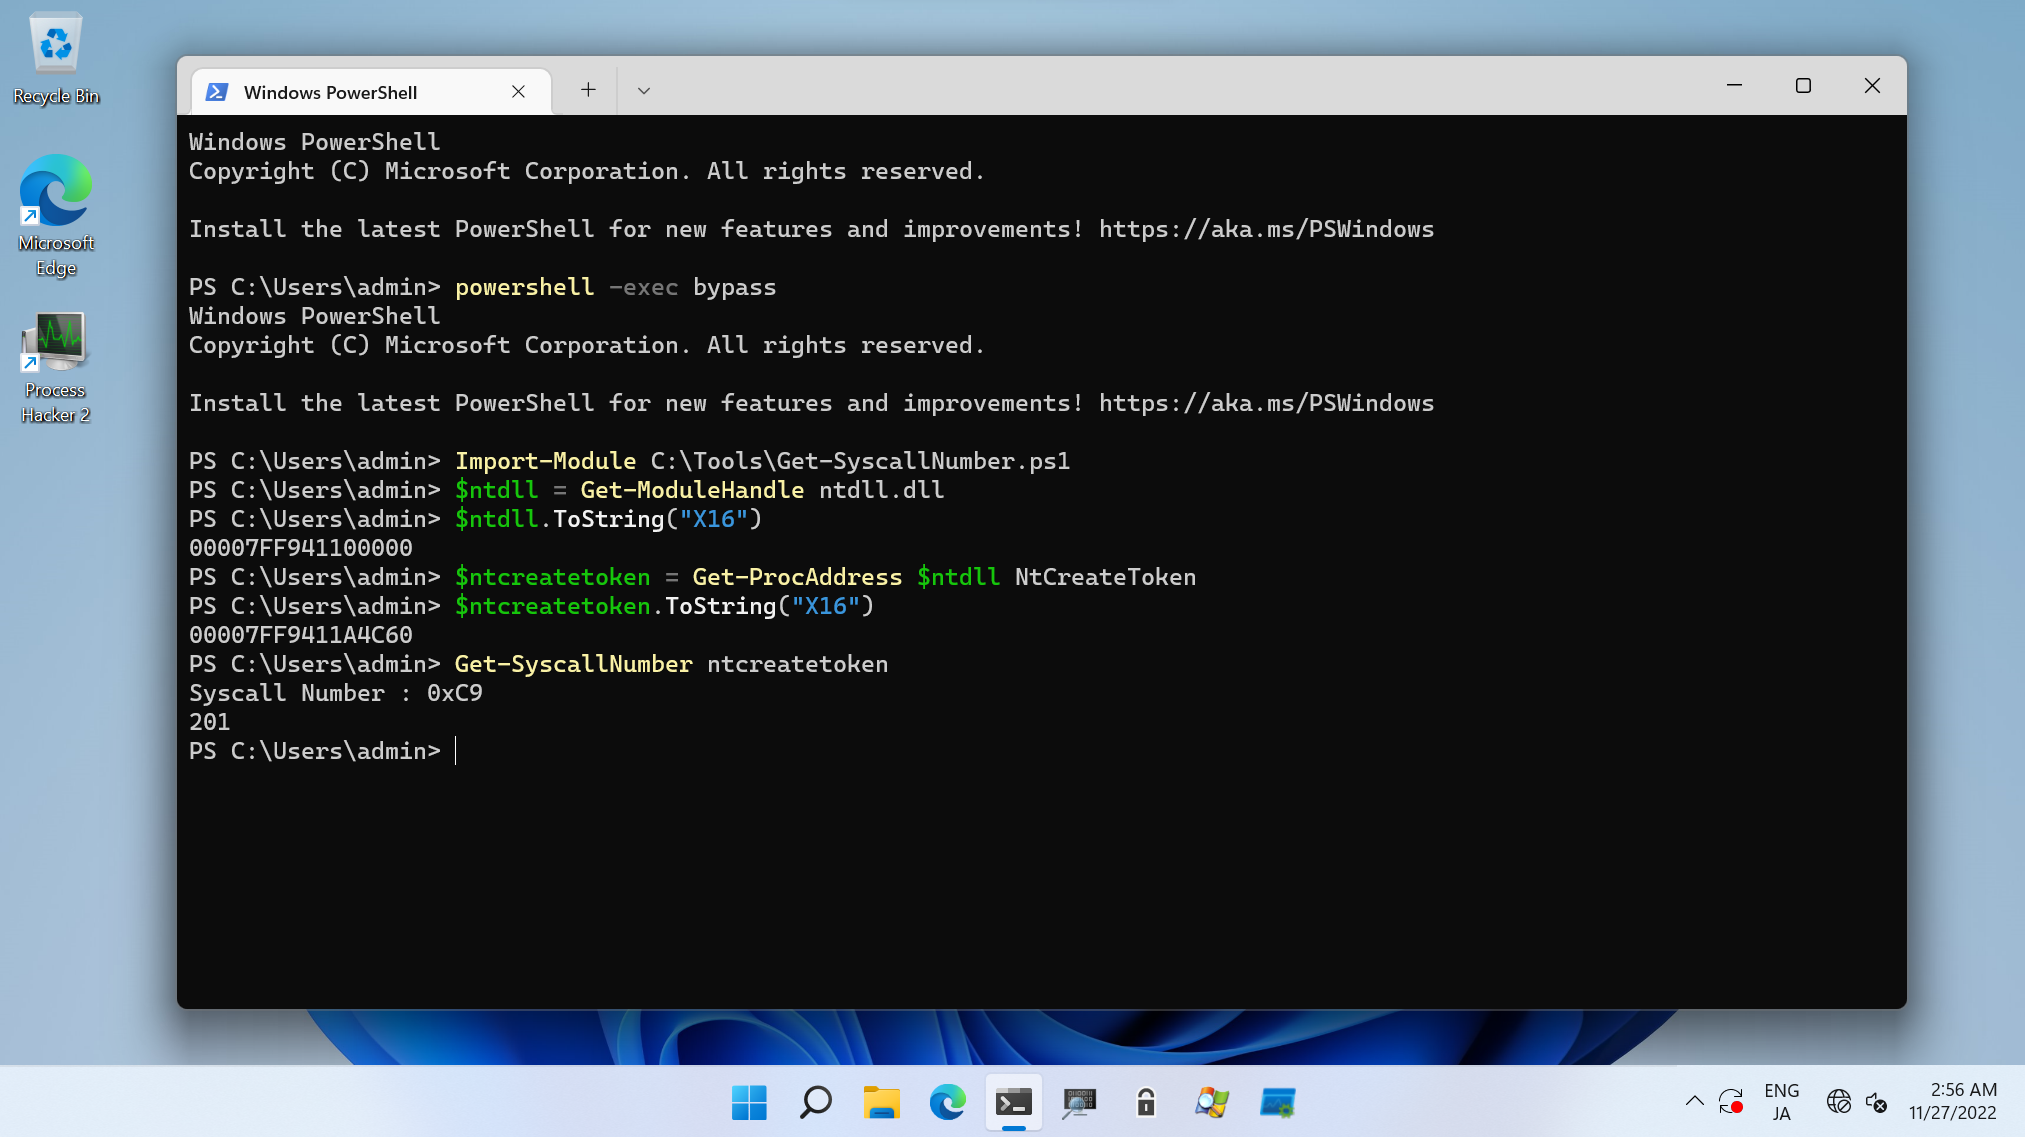 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 sensepost/impersonate
A windows token impersonation tool
 sleepthegod/windows
Windows And Ways To Break It
 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.