

EtwSessionHijacking
 nul0x4c/etwsessionhijacking
A Poc on blocking Procmon from monitoring network events
adversarial-attackids-ips-evasionpost-exploitation+1
111
nul0x4c/etwsessionhijackingA Poc on blocking Procmon from monitoring network events
 loosehose/dutchoven
Application-scoped Windows network brownouts in native C and BOF form
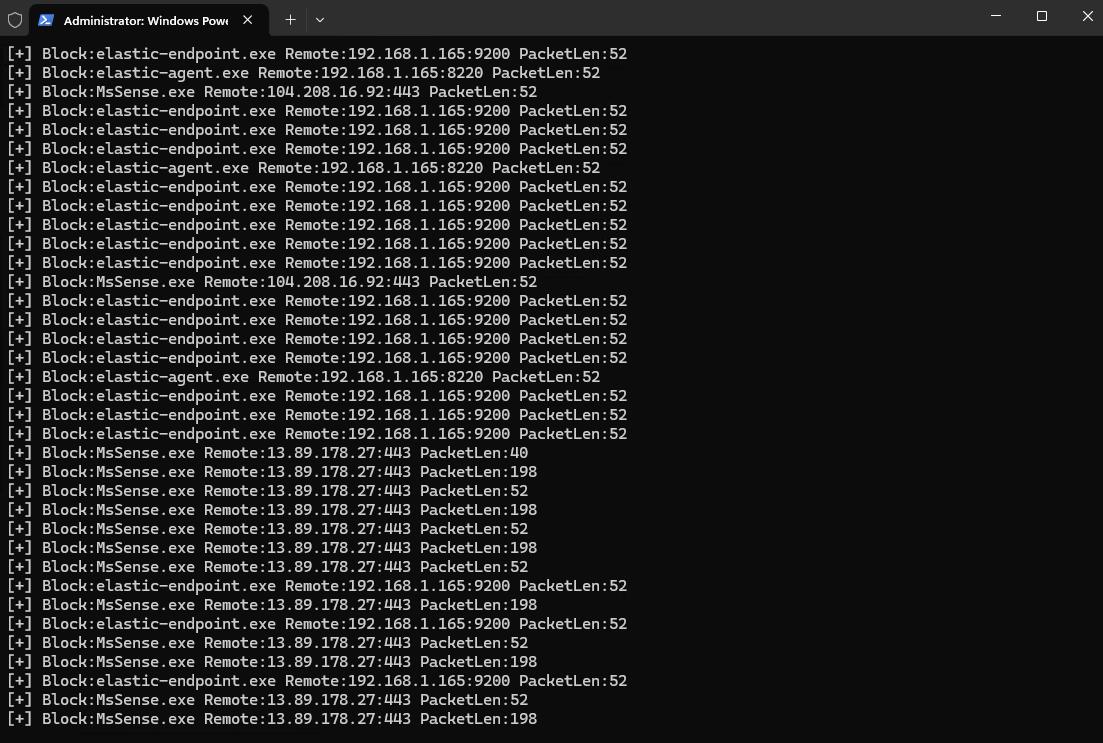 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 saadahla/filelesspeloader
Loading Remote AES Encrypted PE in memory , Decrypted it and run it
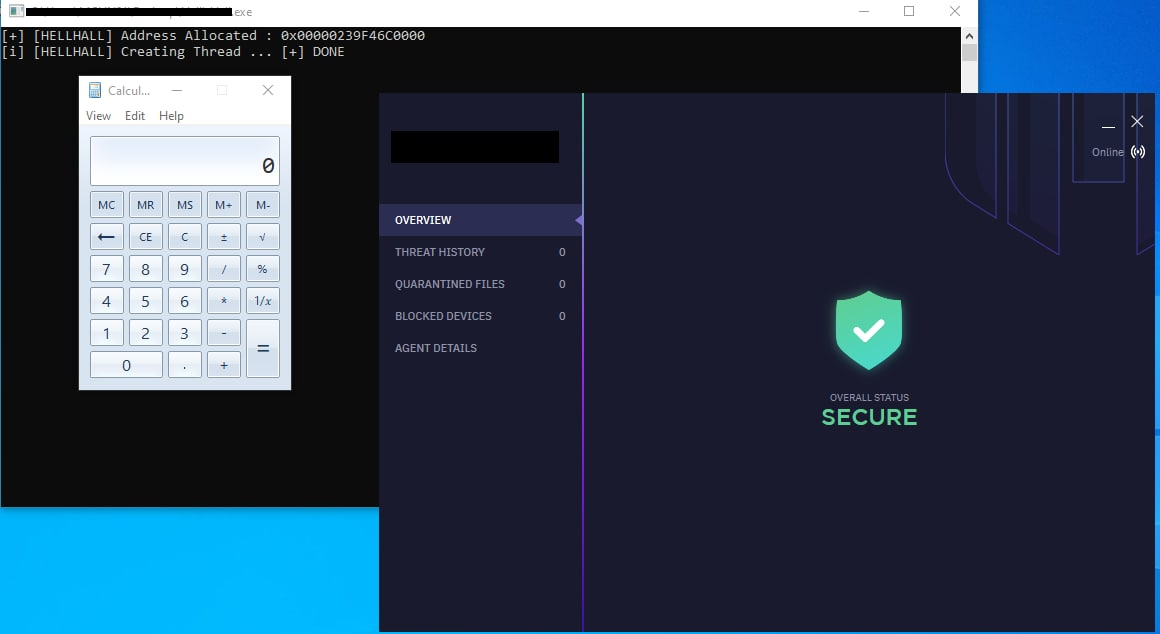 maldev-academy/hellhall
Performing Indirect Clean Syscalls
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
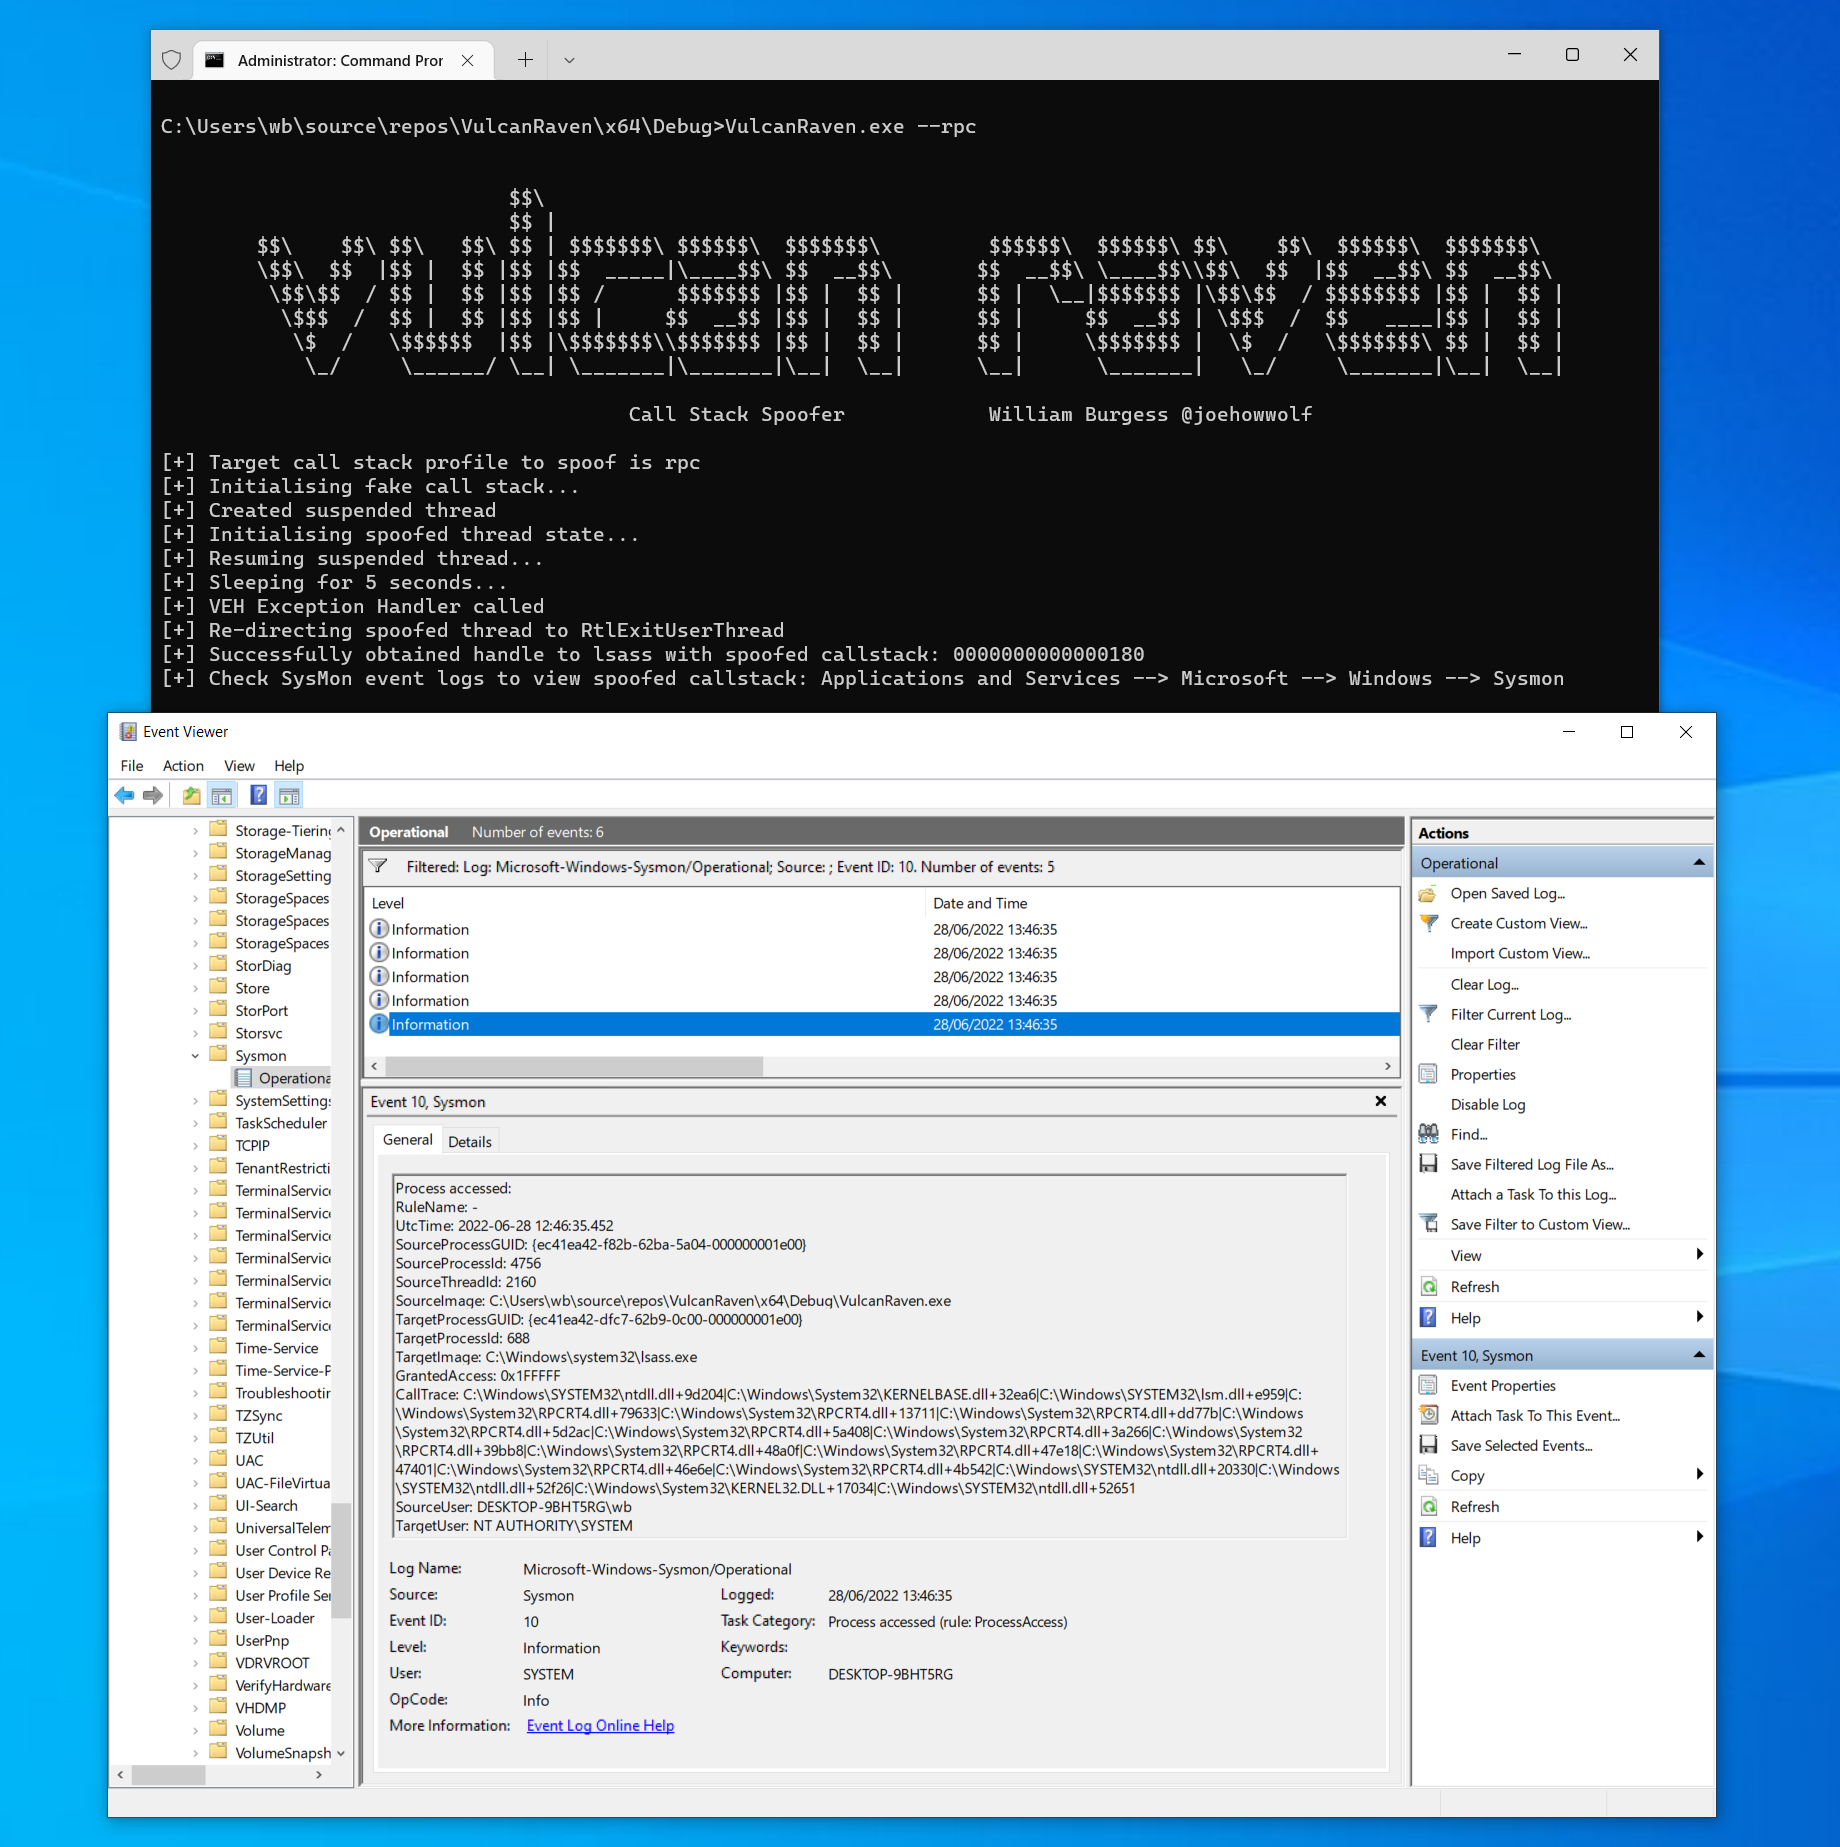 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 rsmudge/unhook-bof
Remove API hooks from a Beacon process.
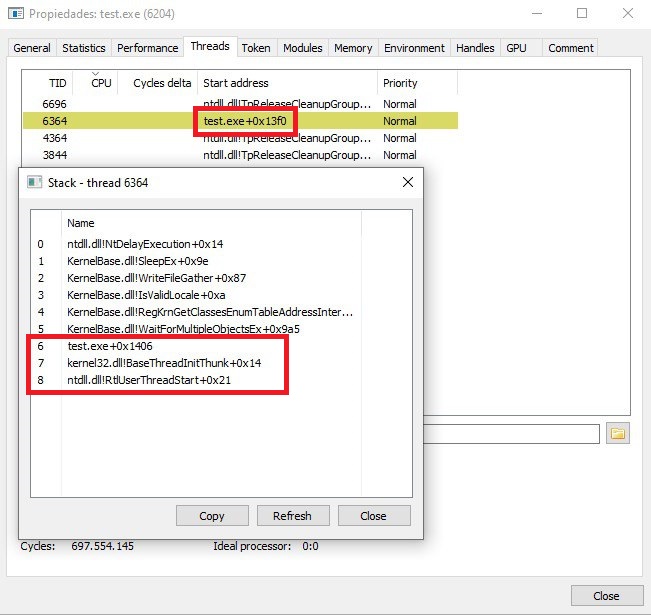 kudaes/unwinder
Call stack spoofing for Rust
 saadahla/unhookingpatch
Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 mr-un1k0d3r/amsi-etw-patch
Patch AMSI and ETW