
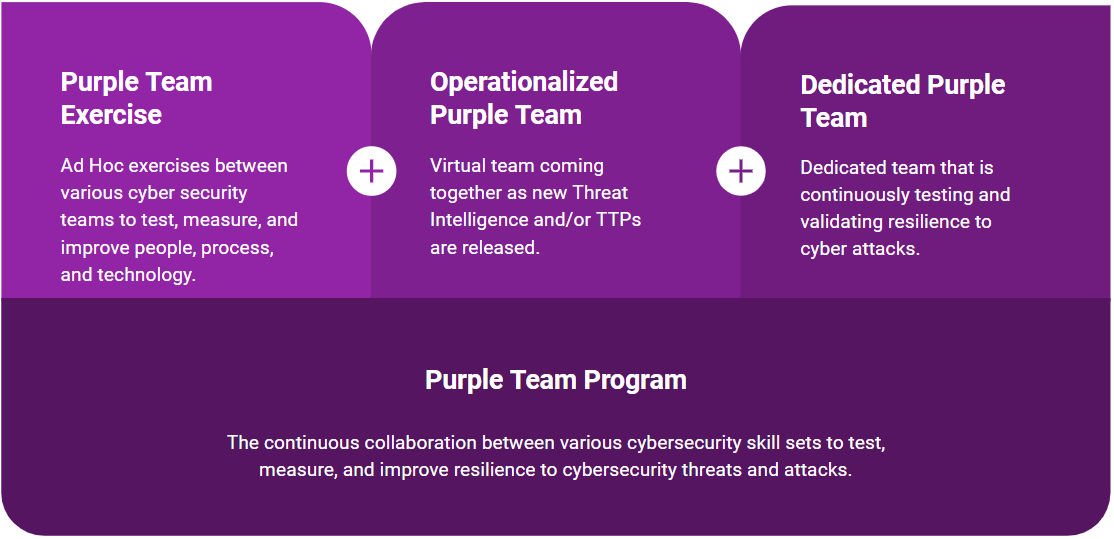
purple-team-exercise-framework
 scythe-io/purple-team-exercise-framework
Purple Team Exercise Framework
adversarial-attackai-securitycloud-security+5
828
scythe-io/purple-team-exercise-frameworkPurple Team Exercise Framework
 phil-fan/fs-attack
Implementation of the paper "Rethinking Latency Denial-of-Service: Attack the LLM Serving Framework, Not the Model"
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
 jisung-pacific/hdi-graphrag-attack
Research implementation of Hop-Decayed Influence (HDI) and the 3S attack framework, exposing structural auxiliary indexing vulnerabilities in…
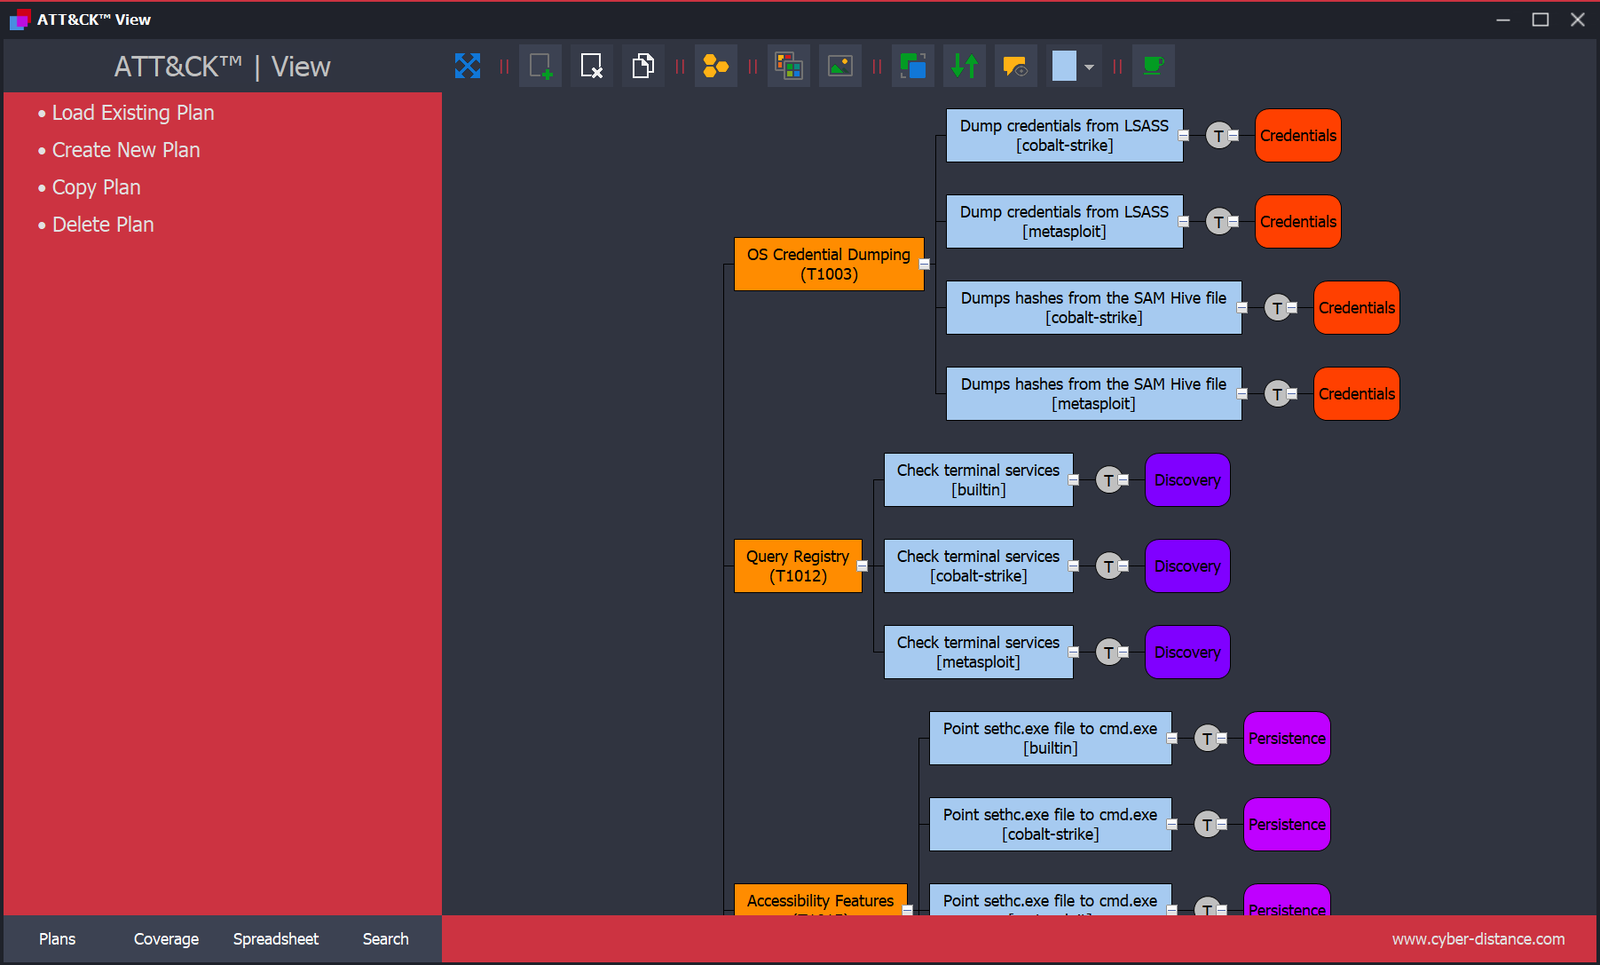 nshalabi/attack-tools
SQLite relational data model for MITRE ATT&CK plus an adversary emulation planning tool, enriched with Red Canary ATOMIC tests and APT3 emulation…
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 alex66366/odpure
Black-box input-stage purification defense that neutralizes backdoor attacks on object detectors via corruption, diffusion reconstruction, and DBSCAN…
 cchio/deep-pwning
Metasploit for machine learning.
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
 azure/pyrit
The Python Risk Identification Tool for generative AI (PyRIT) is an open source framework built to empower security professionals and engineers to…
 albert-y1n/piforge
Open framework for RL-based prompt injection red teaming, with a shared trainer, curriculum learning, and benchmarks like AgentDojo, InjecAgent, and…
 suraj-ranganath/stealthrl
StealthRL: RL framework for adversarially paraphrasing AI text to stress-test detector robustness.
 nishitvp/better_opts_attacks
Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…
 phkhanhtrinh23/agas
LLM-driven agentic group shilling attack framework that manipulates black-box collaborative-filtering recommender rankings using adaptive multi-role…
 96kihyun/batch_jailbreak
This repository contains the official implementation of the paper "[Safety in Batches? Understanding and Mitigating Safety Failures in Batch…
 microsoft/pyrit
Open-source framework for red-teaming generative AI systems: automate attack prompts, score model responses, and audit behavior to identify security…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 azzzzliao/aegis-audio-defense
Defense framework that keeps audio-language models frozen and adds a mid-layer risk gate with late-layer safety adapters to block audio jailbreaks at…