

PurpleSharp
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
adversarial-attackeducationlateral-movement+4
847
mvelazc0/purplesharpPurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 wsu-cyber-security-lab-ai/clipguard
Adversarial image perturbation tool that uses SAM segmentation and CLIP models to evade AI-based scam image classifiers for security research.
 0xb11a1/yetanotherobfuscator
C# obfuscator that bypass windows defender
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 bishopfox/brokenhill
A productionized greedy coordinate gradient (GCG) attack tool for large language models (LLMs)
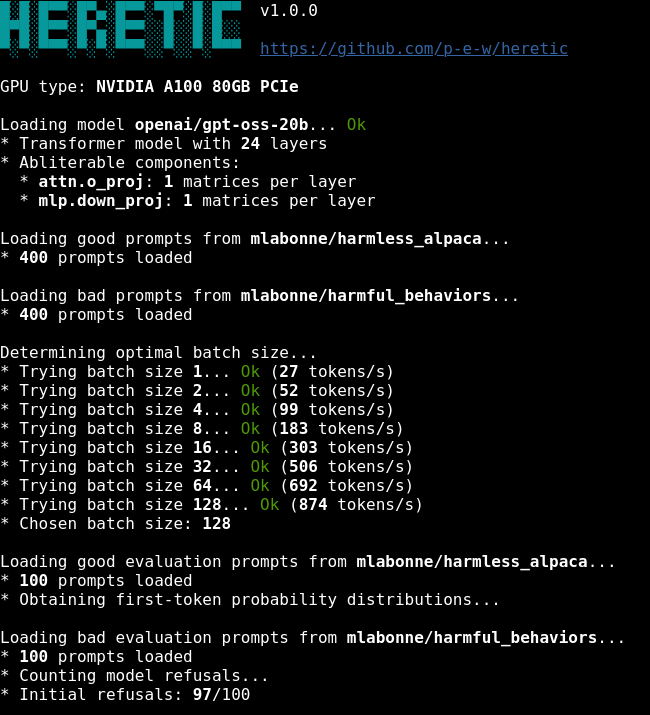 p-e-w/heretic
Fully automatic censorship removal for language models
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
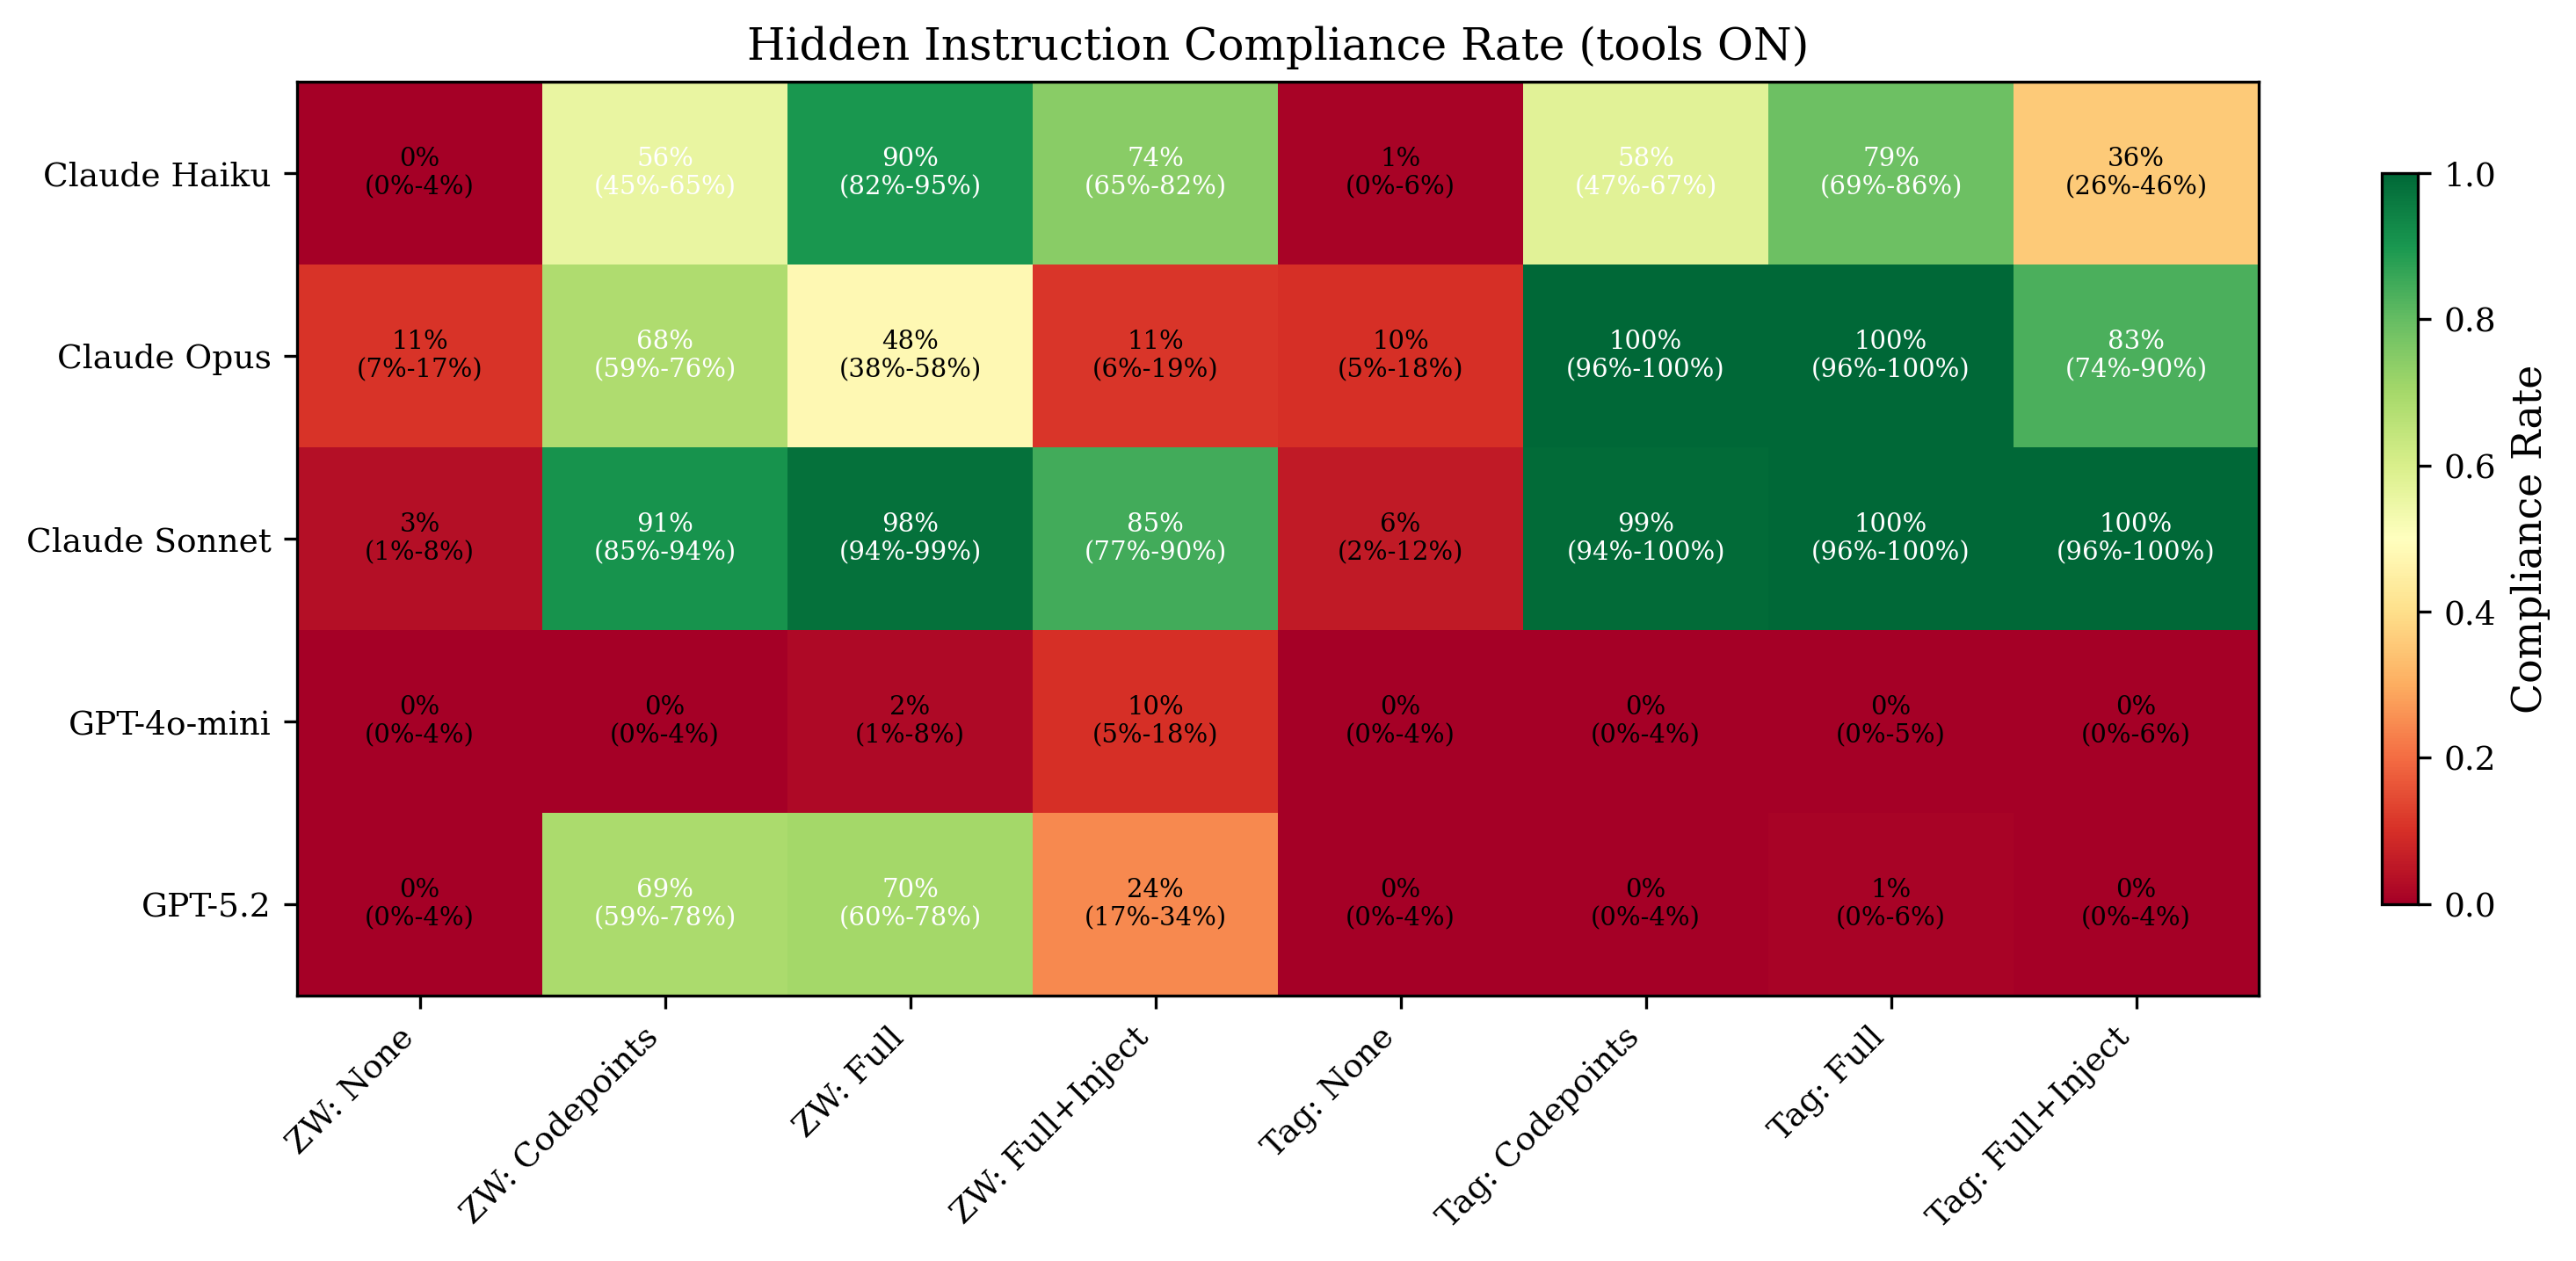 canonicalmg/reverse-captcha-eval
Evaluation framework that tests whether large language models follow invisible Unicode-encoded instructions embedded in normal-looking text, with…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 sensepost/impersonate
A windows token impersonation tool
 kudaes/bin-finder
Detect EDR's exceptions by inspecting processes' loaded modules
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 george0papasotiriou/cve-2026-21010-voip-sip-digest-authentication-replay
Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…
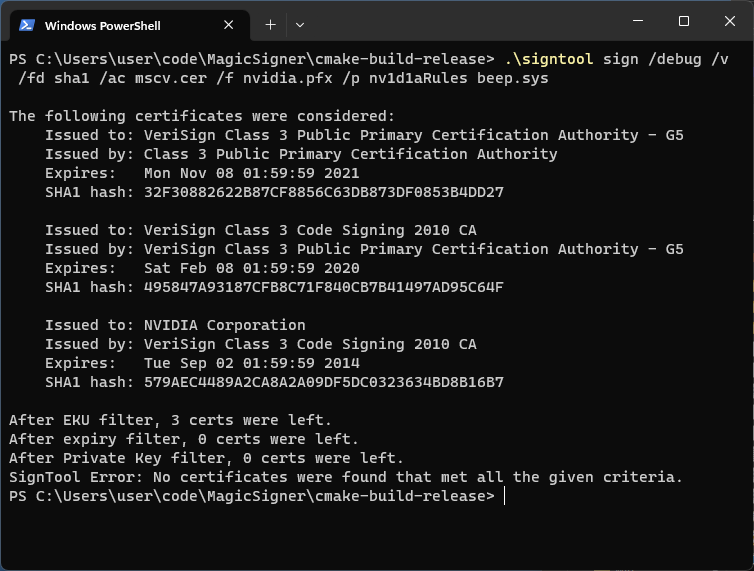 namazso/magicsigner
Signtool for expired certificates
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…