

EtwSessionHijacking
 nul0x4c/etwsessionhijacking
A Poc on blocking Procmon from monitoring network events
adversarial-attackids-ips-evasionpost-exploitation+1
111
nul0x4c/etwsessionhijackingA Poc on blocking Procmon from monitoring network events
 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 saadahla/filelesspeloader
Loading Remote AES Encrypted PE in memory , Decrypted it and run it
 maldev-academy/hellhall
Performing Indirect Clean Syscalls
 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)
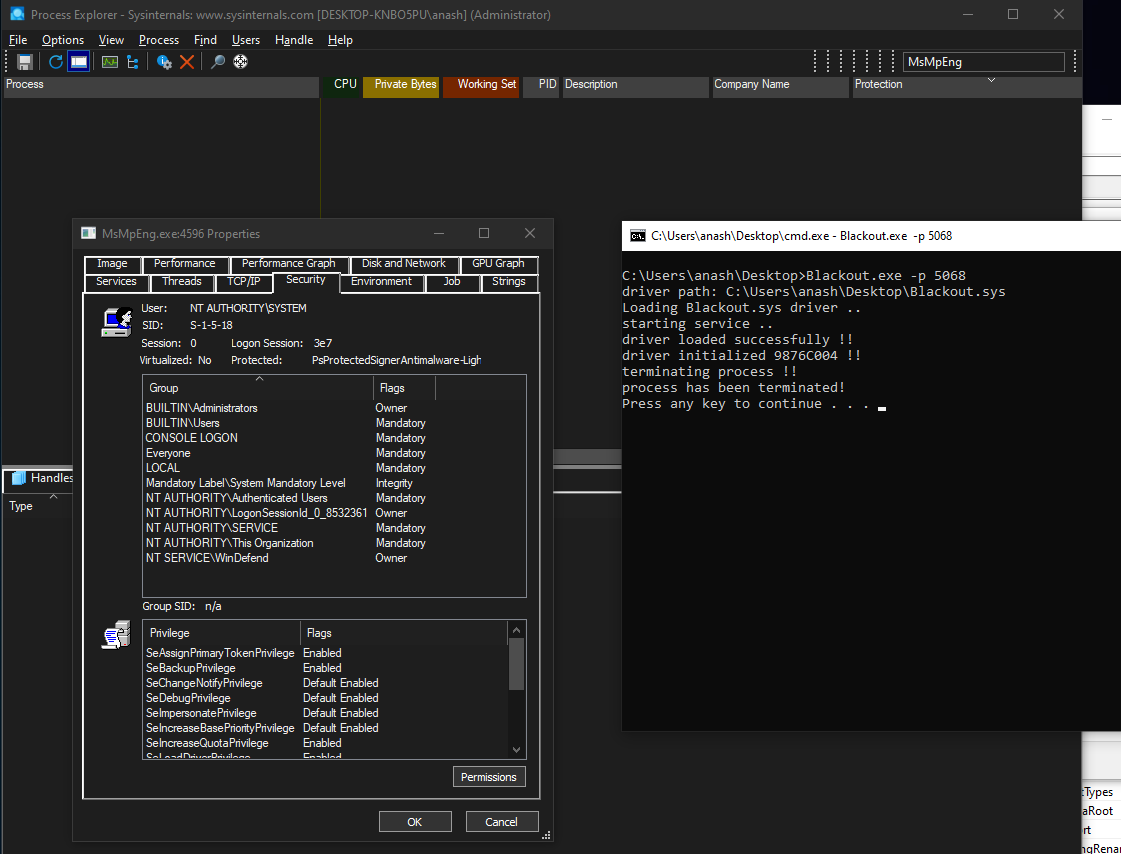 zeromemoryex/blackout
kill anti-malware protected processes ( BYOVD )
 rasta-mouse/crystal-kit
Evasion kit for Cobalt Strike
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
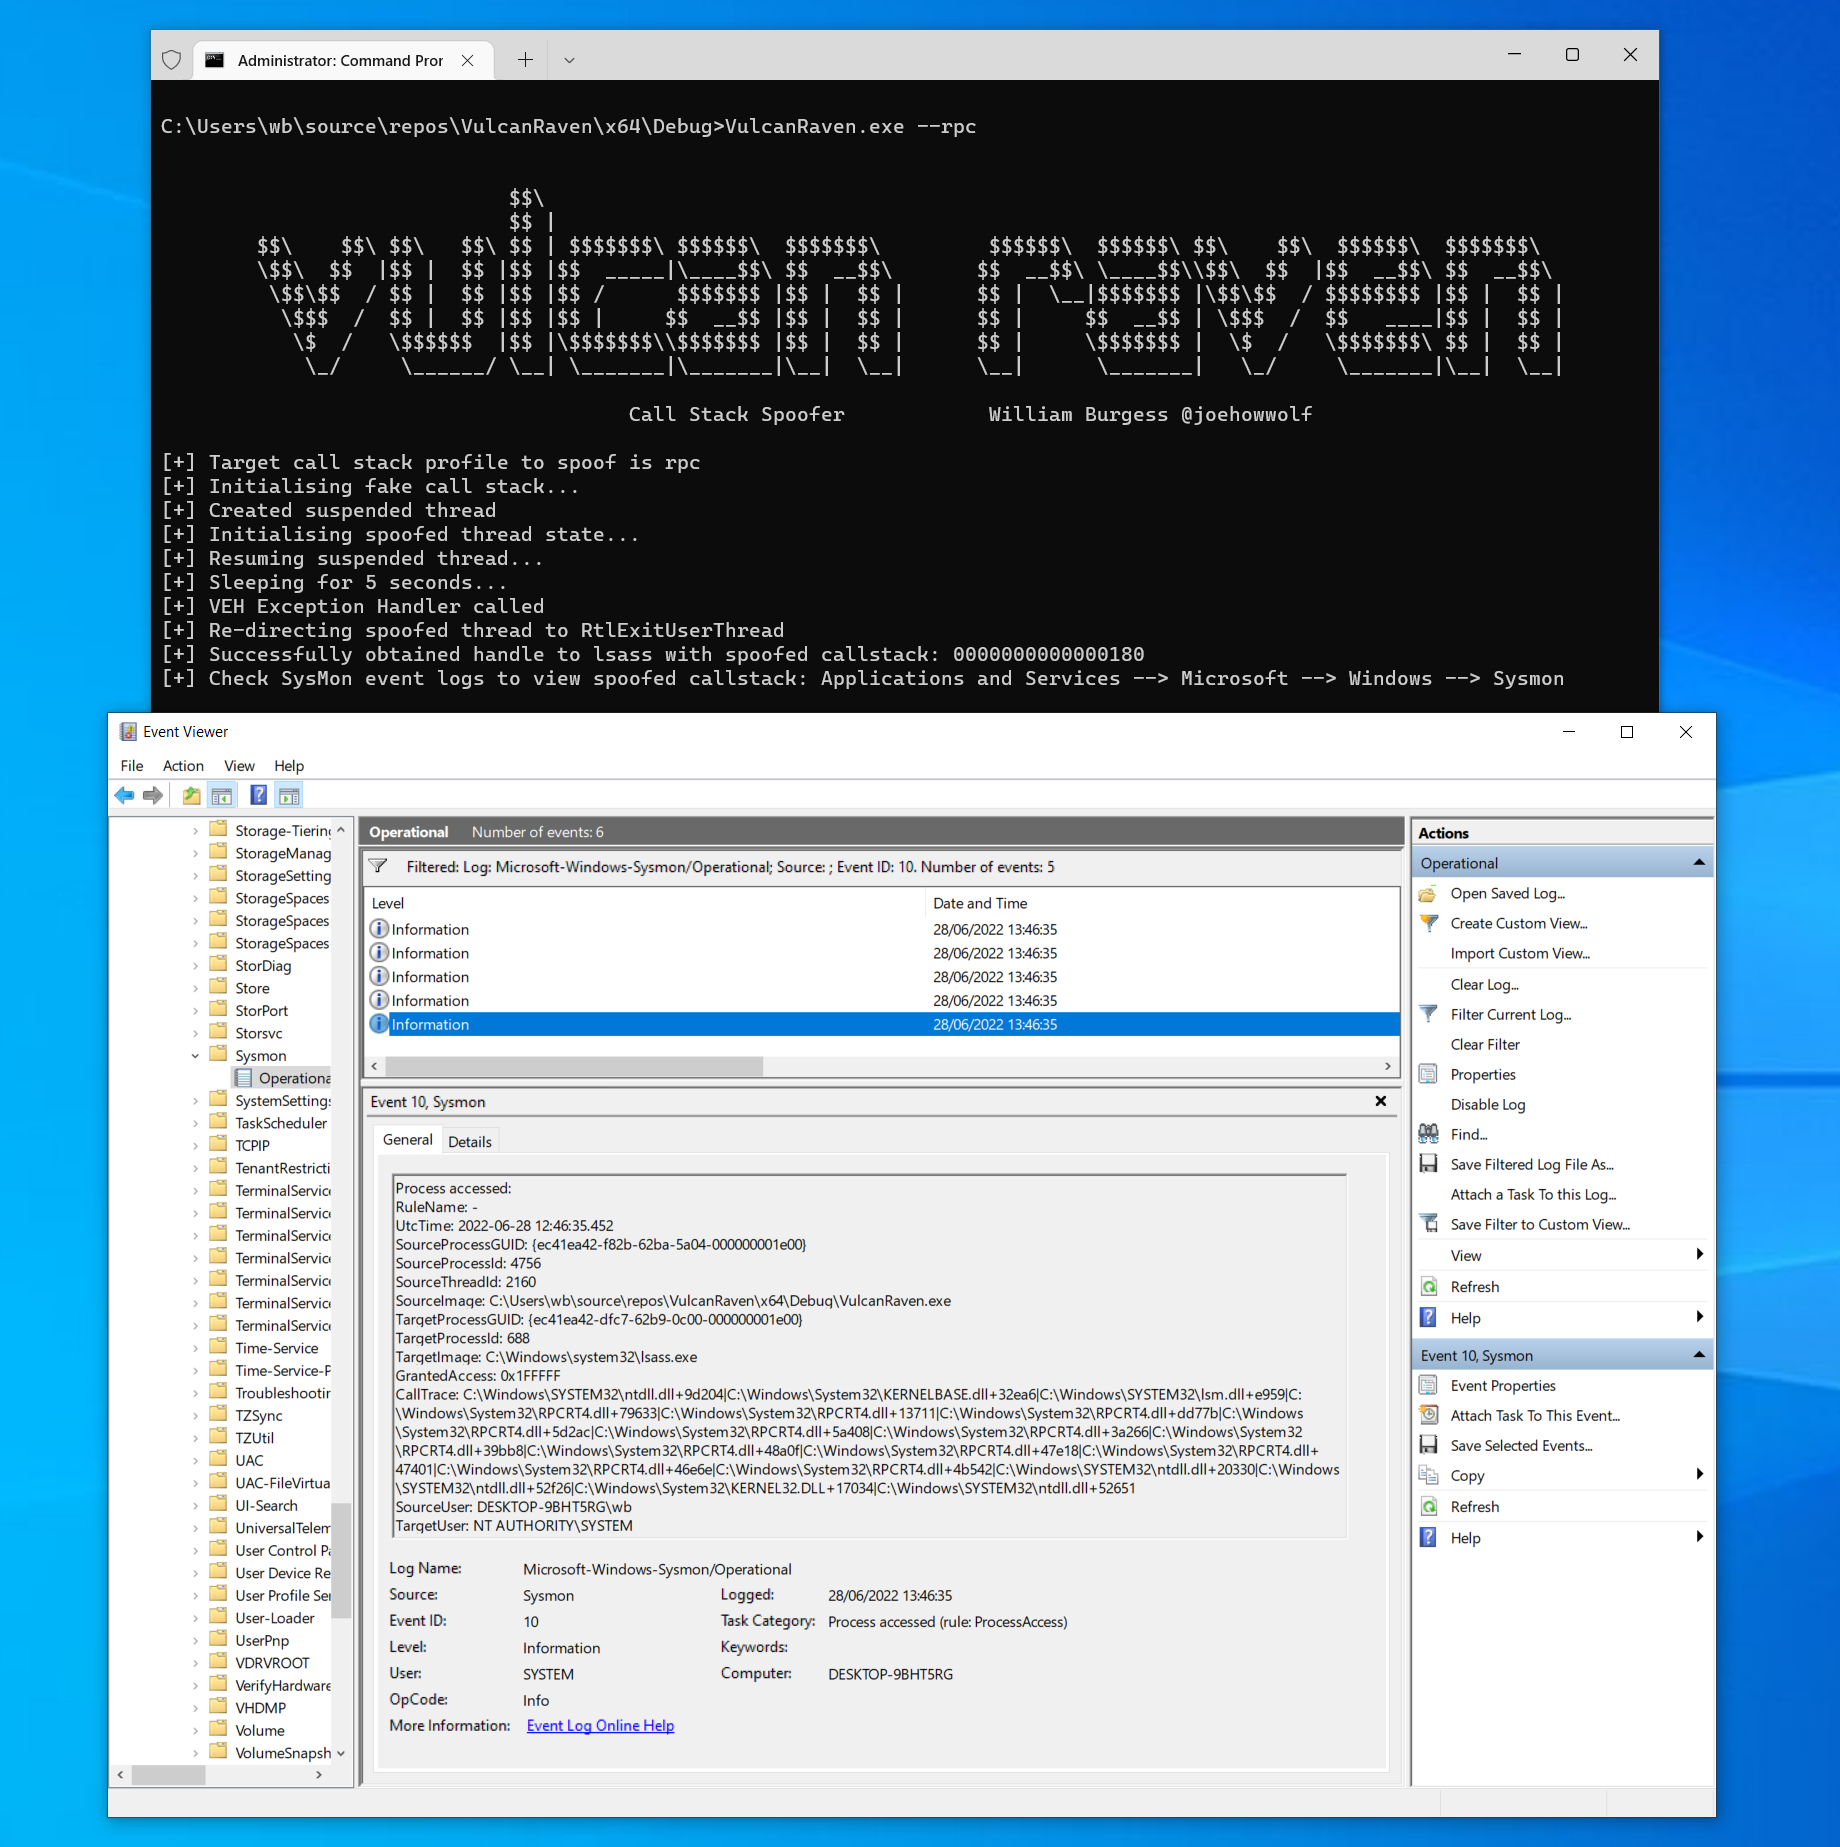 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
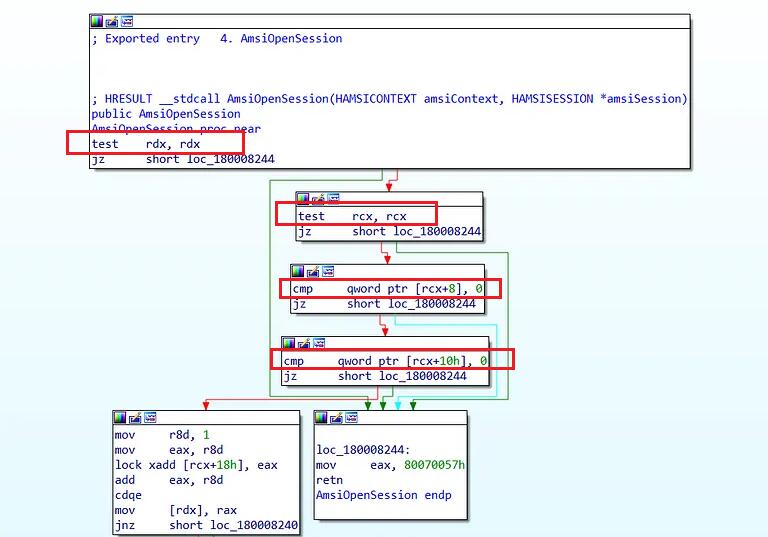 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
 rsmudge/unhook-bof
Remove API hooks from a Beacon process.
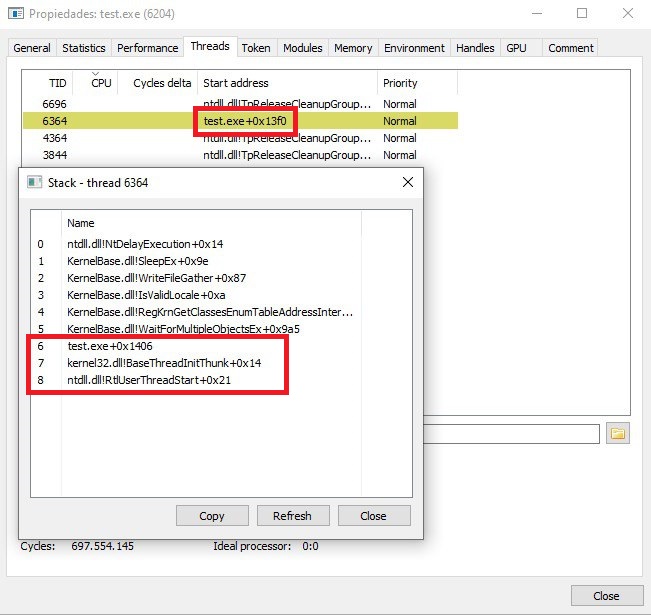 kudaes/unwinder
Call stack spoofing for Rust
 saadahla/unhookingpatch
Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys