
RingReaper
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
adversarial-attackcommand-and-controldata-exfiltration+5
391
matheuzsecurity/ringreaperLinux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 bishopfox/sliver
Adversary Emulation Framework
 dosx-dev/dotnet_xorcryptor
A new simple and powerfull packer for malware
 knight0x07/poc-malware-ttps
PoC-Malware-TTPs
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
 borealisai/stepjack
Benchmarking framework for evaluating computer-use AI agents against multi-step indirect prompt injection, with automatic adversarial goal…
 alex66366/odpure
Black-box input-stage purification defense that neutralizes backdoor attacks on object detectors via corruption, diffusion reconstruction, and DBSCAN…
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
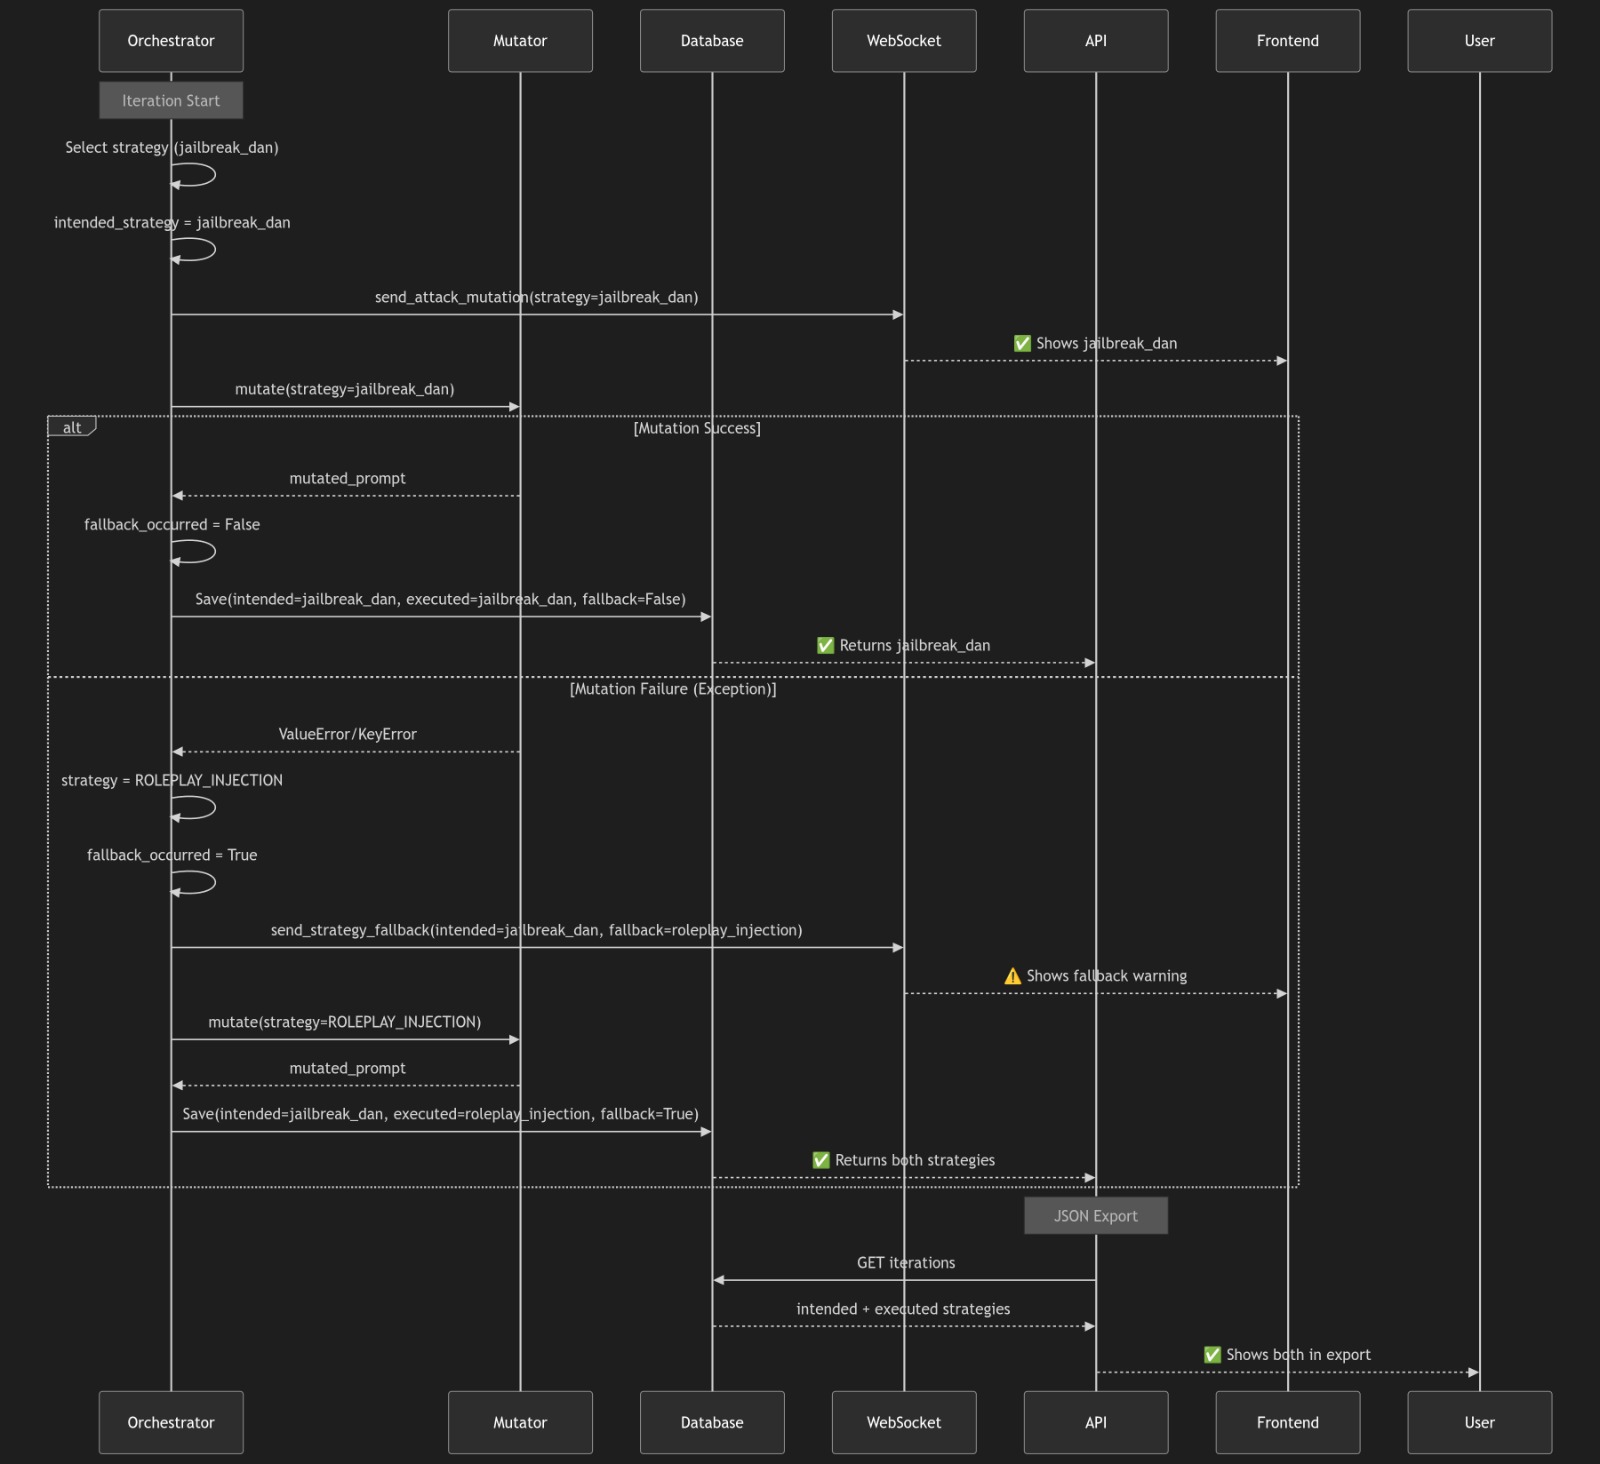 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
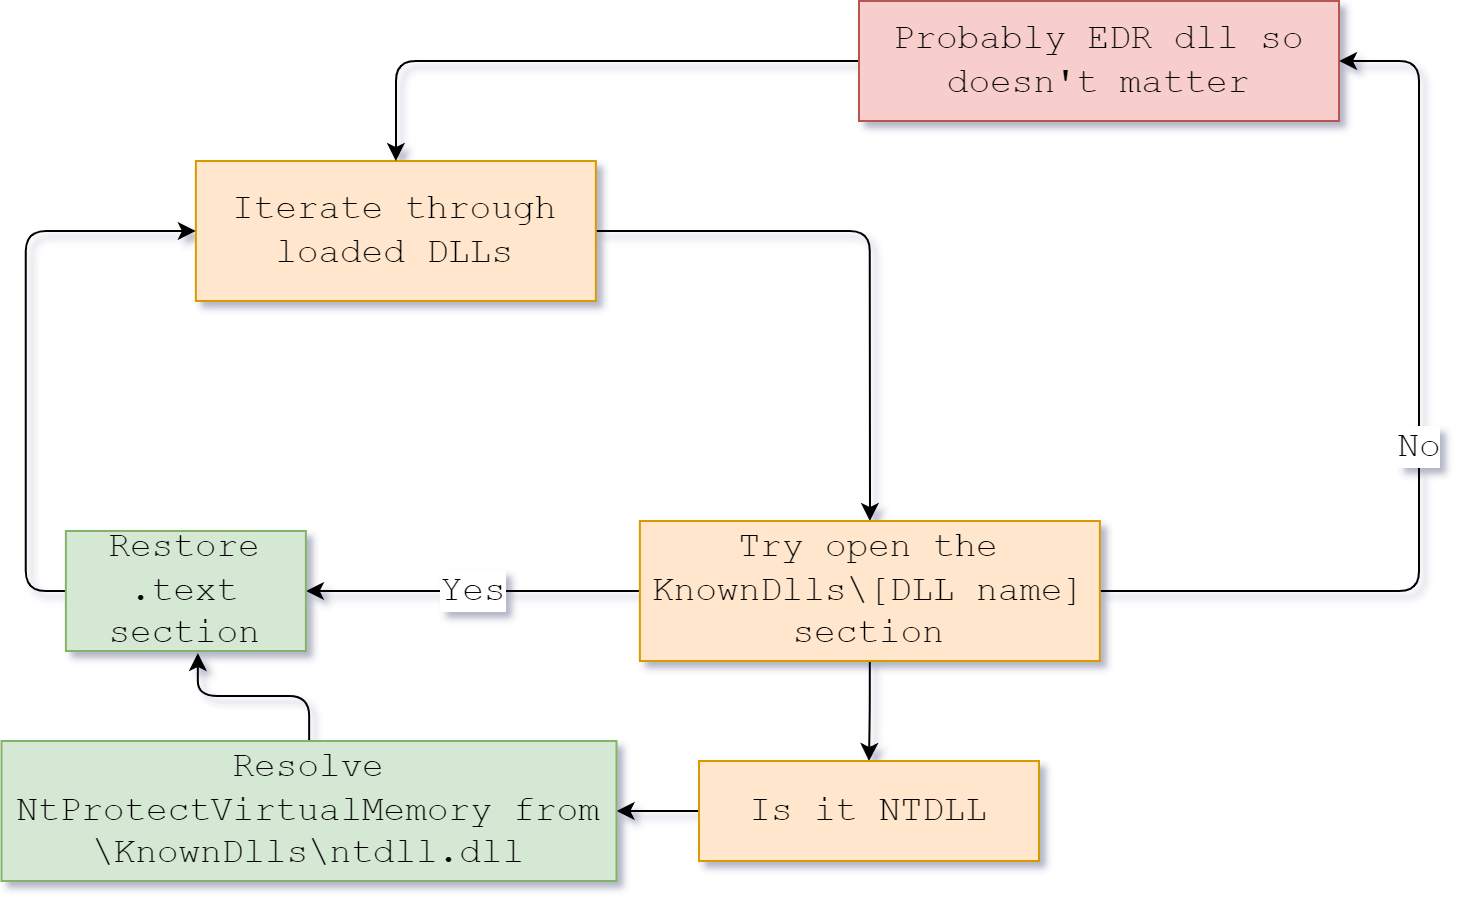
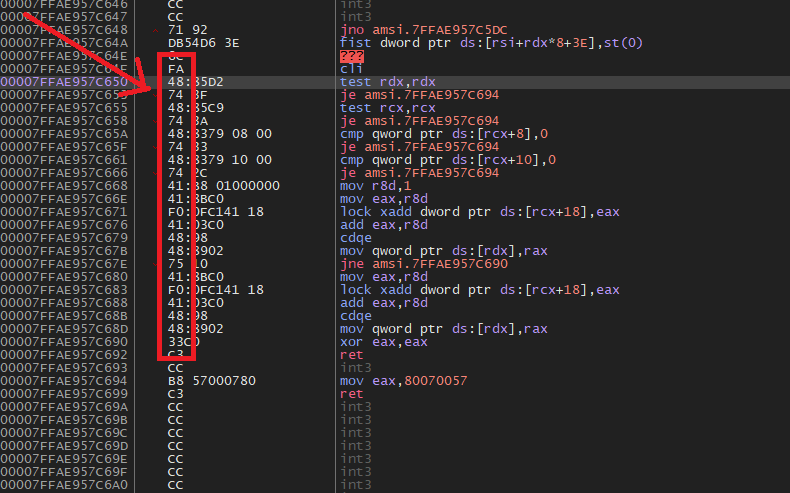 zeromemoryex/amsi-killer
Lifetime AMSI bypass
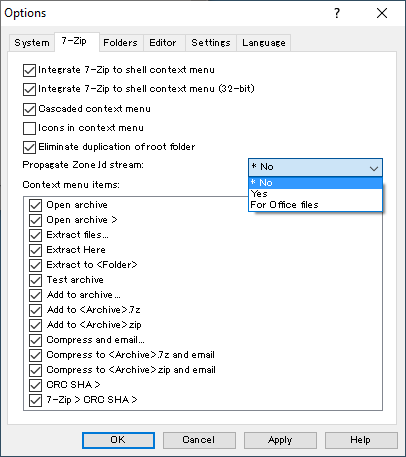 nmantani/archiver-motw-support-comparison
Compares Windows archiver support for Mark of the Web propagation, helping teams assess which tools preserve MOTW and mitigate macro-based malware…
 hectorm/hblock
Improve your security and privacy by blocking ads, tracking and malware domains.
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…