
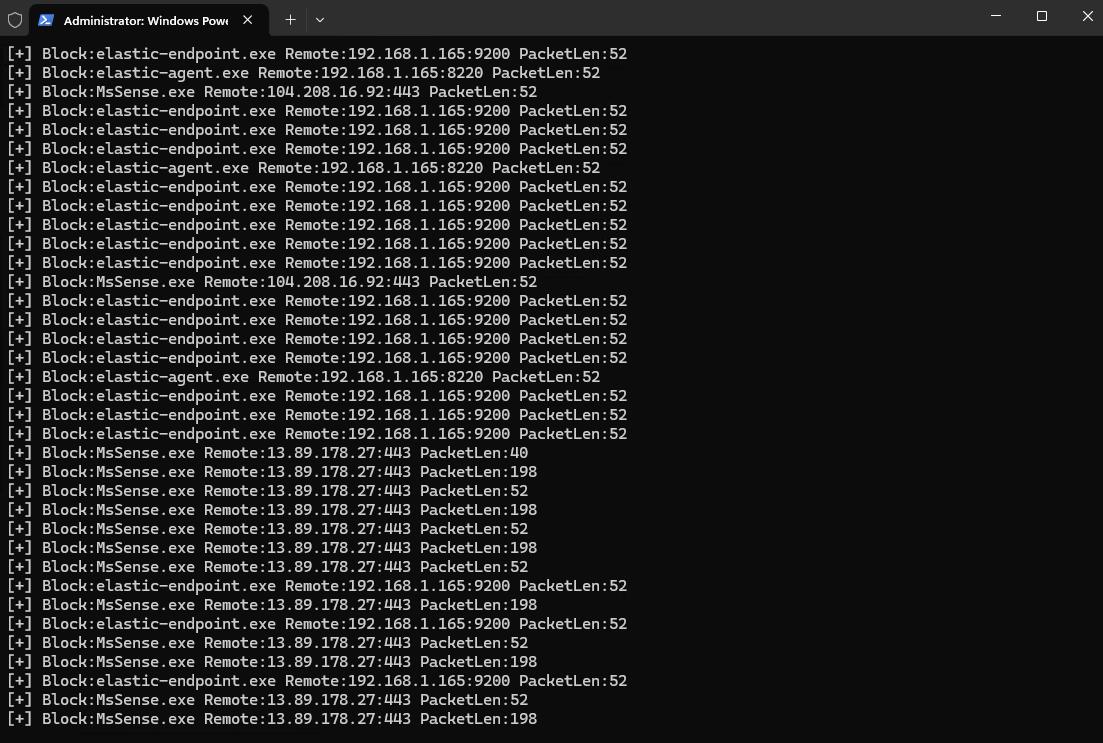
EDRPrison
 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
adversarial-attackids-ips-evasionnetwork-security+2
senzee1984/edrprisonLeverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 toxy4ny/delirium-ai-safety-benchmark
A diagnostic framework for measuring LLM vulnerability to Affective Contextual Erosion (ACE) and related liminal attack vectors. **Delirium** is not…
 kuro0911/cs5446-project
Code repository for CS5446 project exploring defenses against jailbreak attacks on large-language models it includes datasets, notebooks,…
 sunandm/poc-h2-cve-2026-71554
PoC for CVE-2026-71554 - h2 duplicate Host header request smuggling primitive (fixed in 4.4.1)
 safety-research/bloom
Automated behavioral evaluation framework for LLMs that generates diverse test scenarios to probe for sycophancy, bias, and other safety-relevant…
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office
 kevinchunye/prompt_injection
Benchmark harness measuring where prompt injection defenses fire in tool-using LLM agent pipelines, tracking canary tokens across exposed, persisted,…
 nextronsystems/aptsimulator
A toolset to make a system look as if it was the victim of an APT attack
 barre/privaxy
Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…
 saadahla/filelesspeloader
Loading Remote AES Encrypted PE in memory , Decrypted it and run it
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 sleepthegod/windows
Windows And Ways To Break It
 alteredsecurity/disable-tamperprotection
A POC to disable TamperProtection and other Defender / MDE components
 kudaes/split
Apply a divide and conquer approach to bypass EDRs