
RTA
 endgameinc/rta
Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
adversarial-attackeducationlabs-practice+2
1.1k
endgameinc/rtaScripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
 spiralbl0ck/rowhammer-exploit
RowHammer Based-Exploit
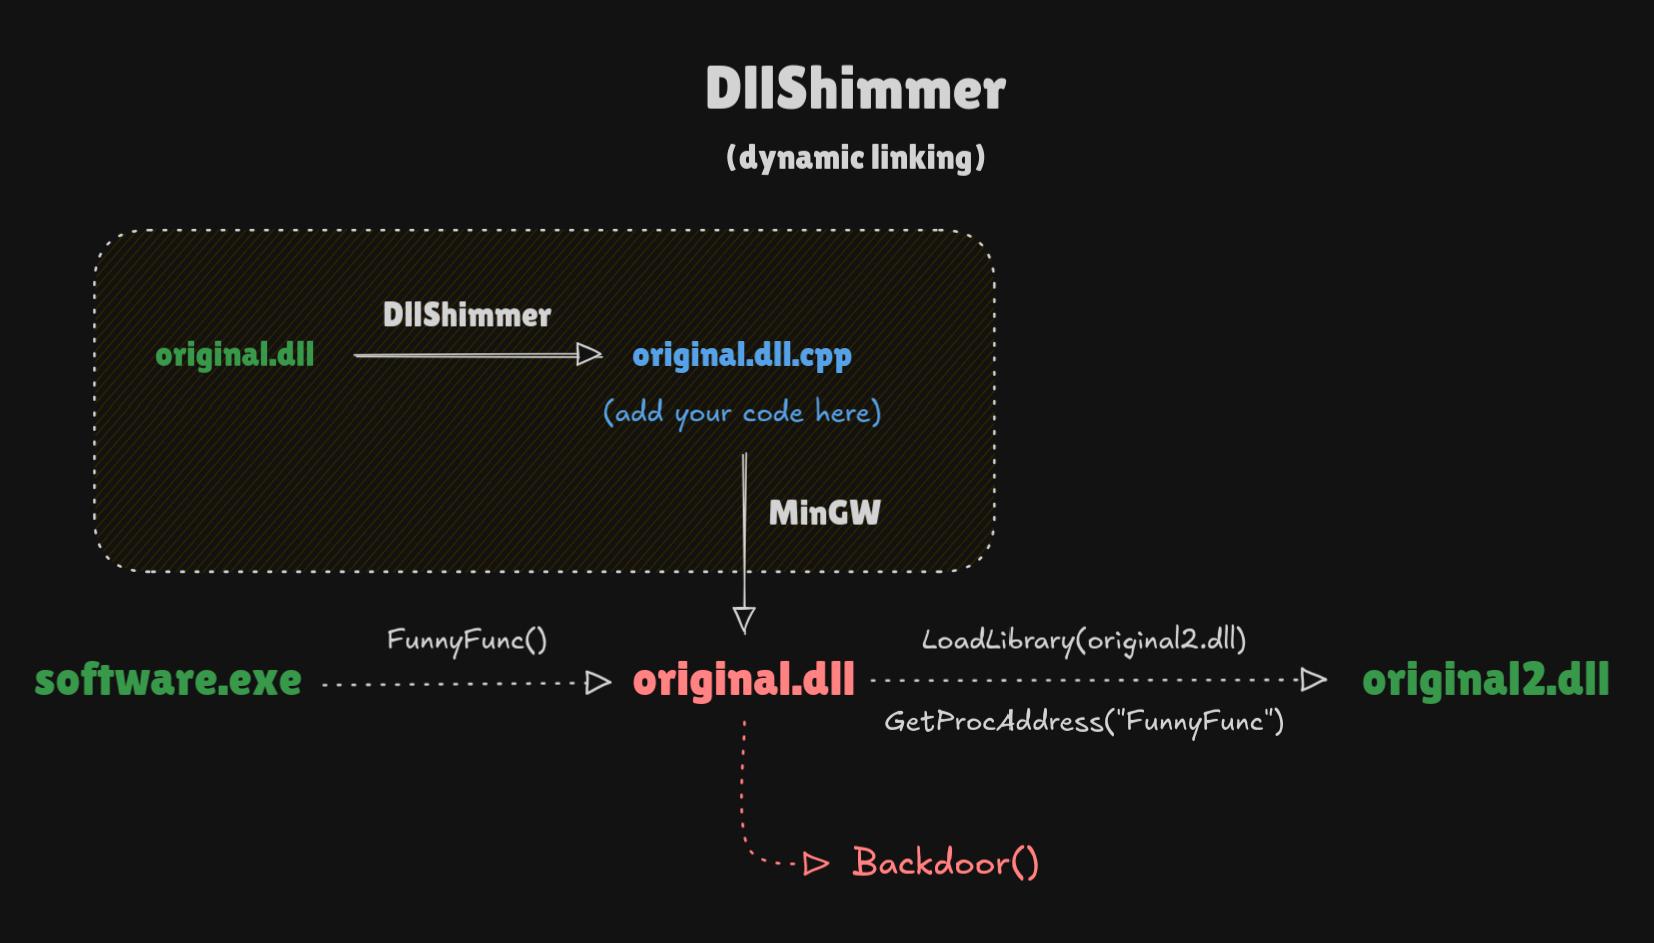 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
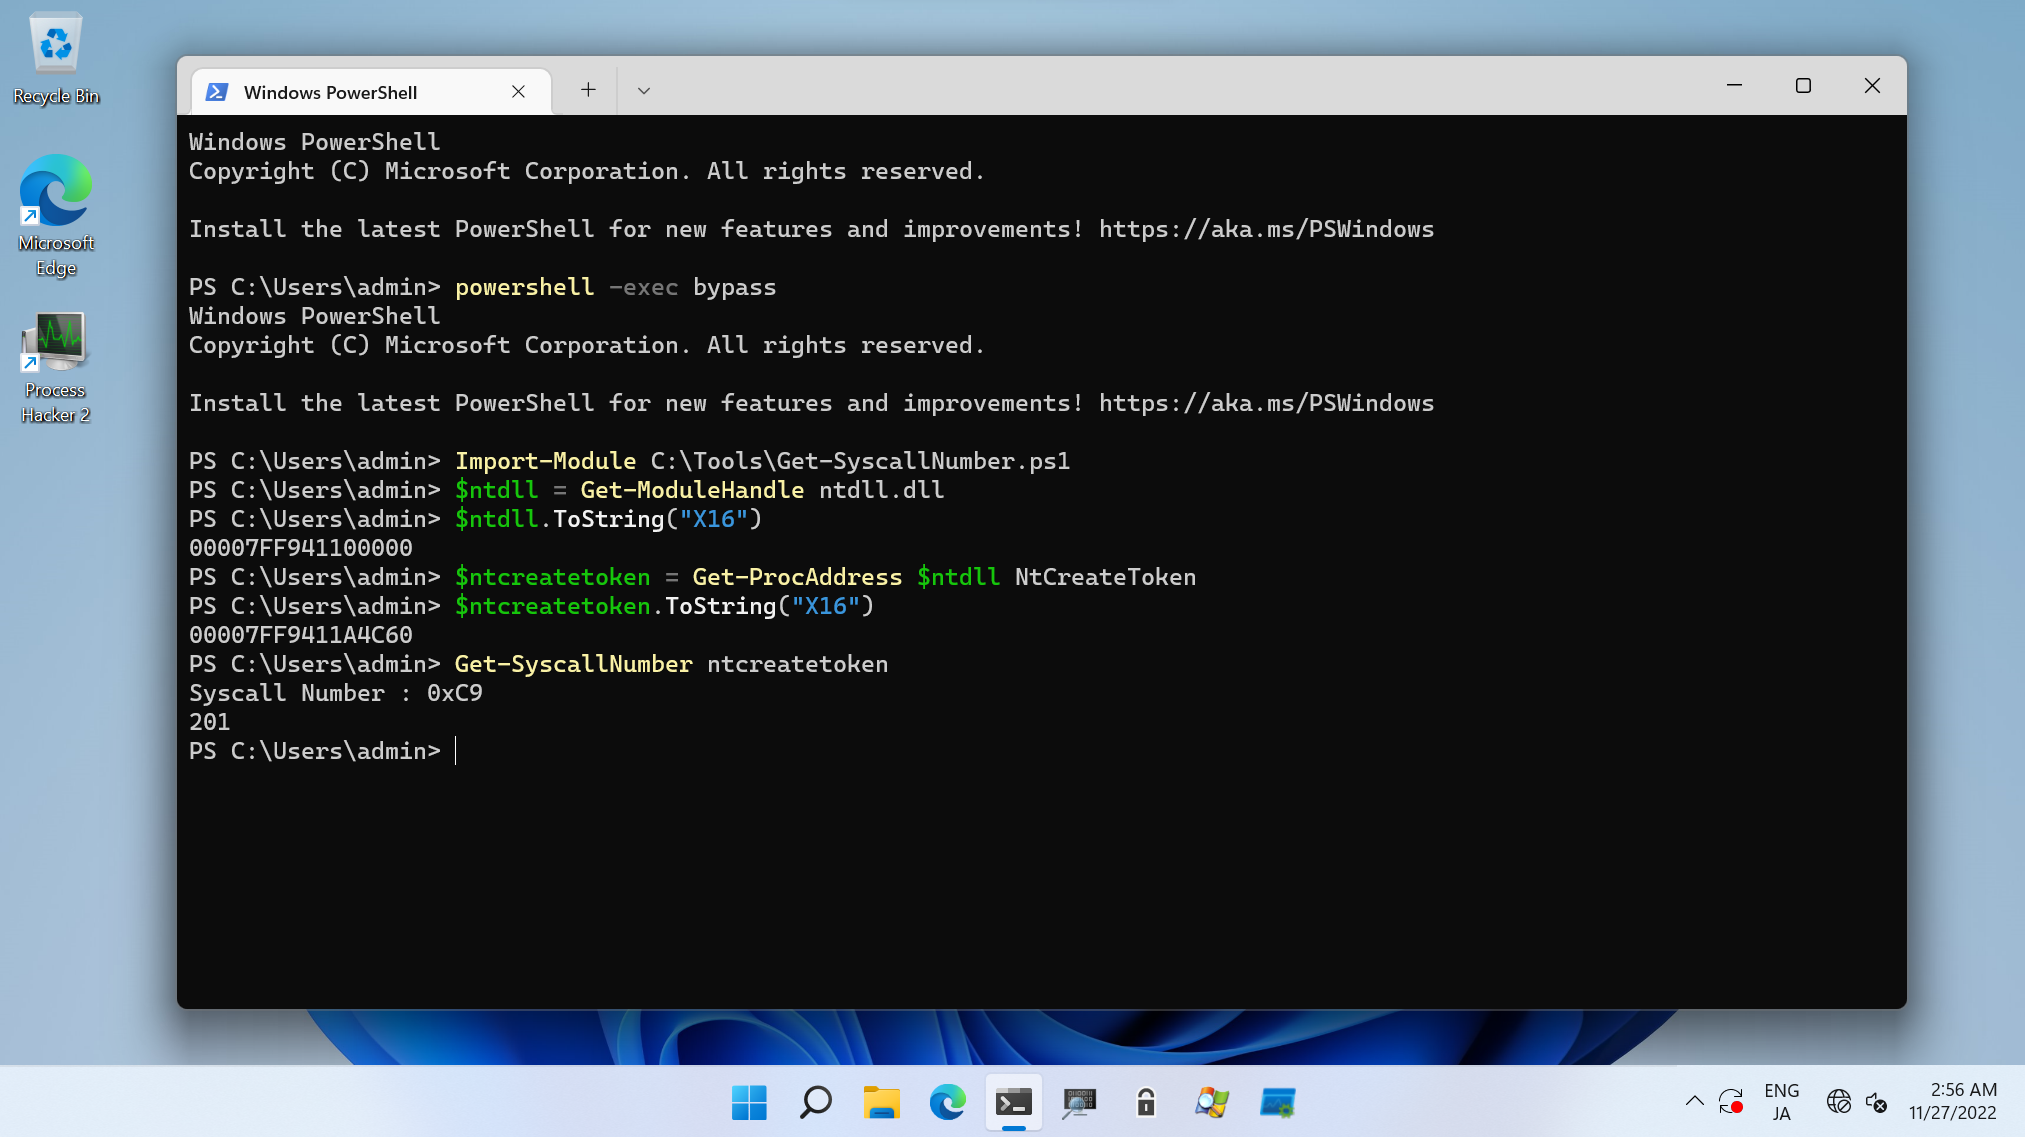 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
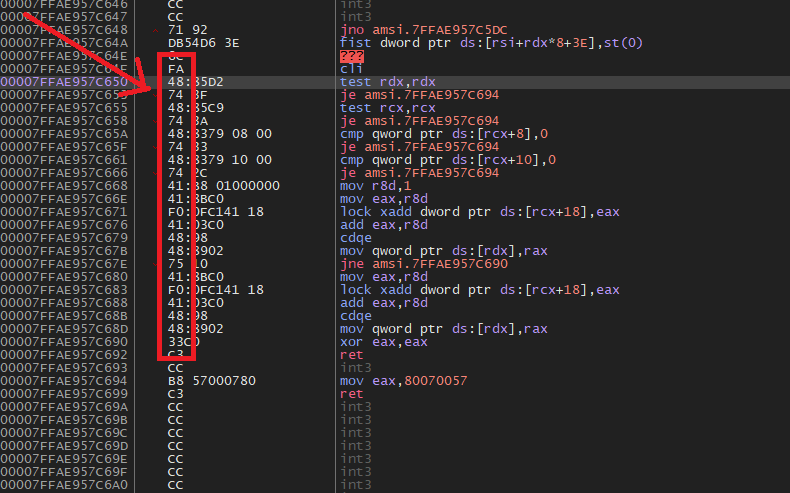 zeromemoryex/amsi-killer
Lifetime AMSI bypass
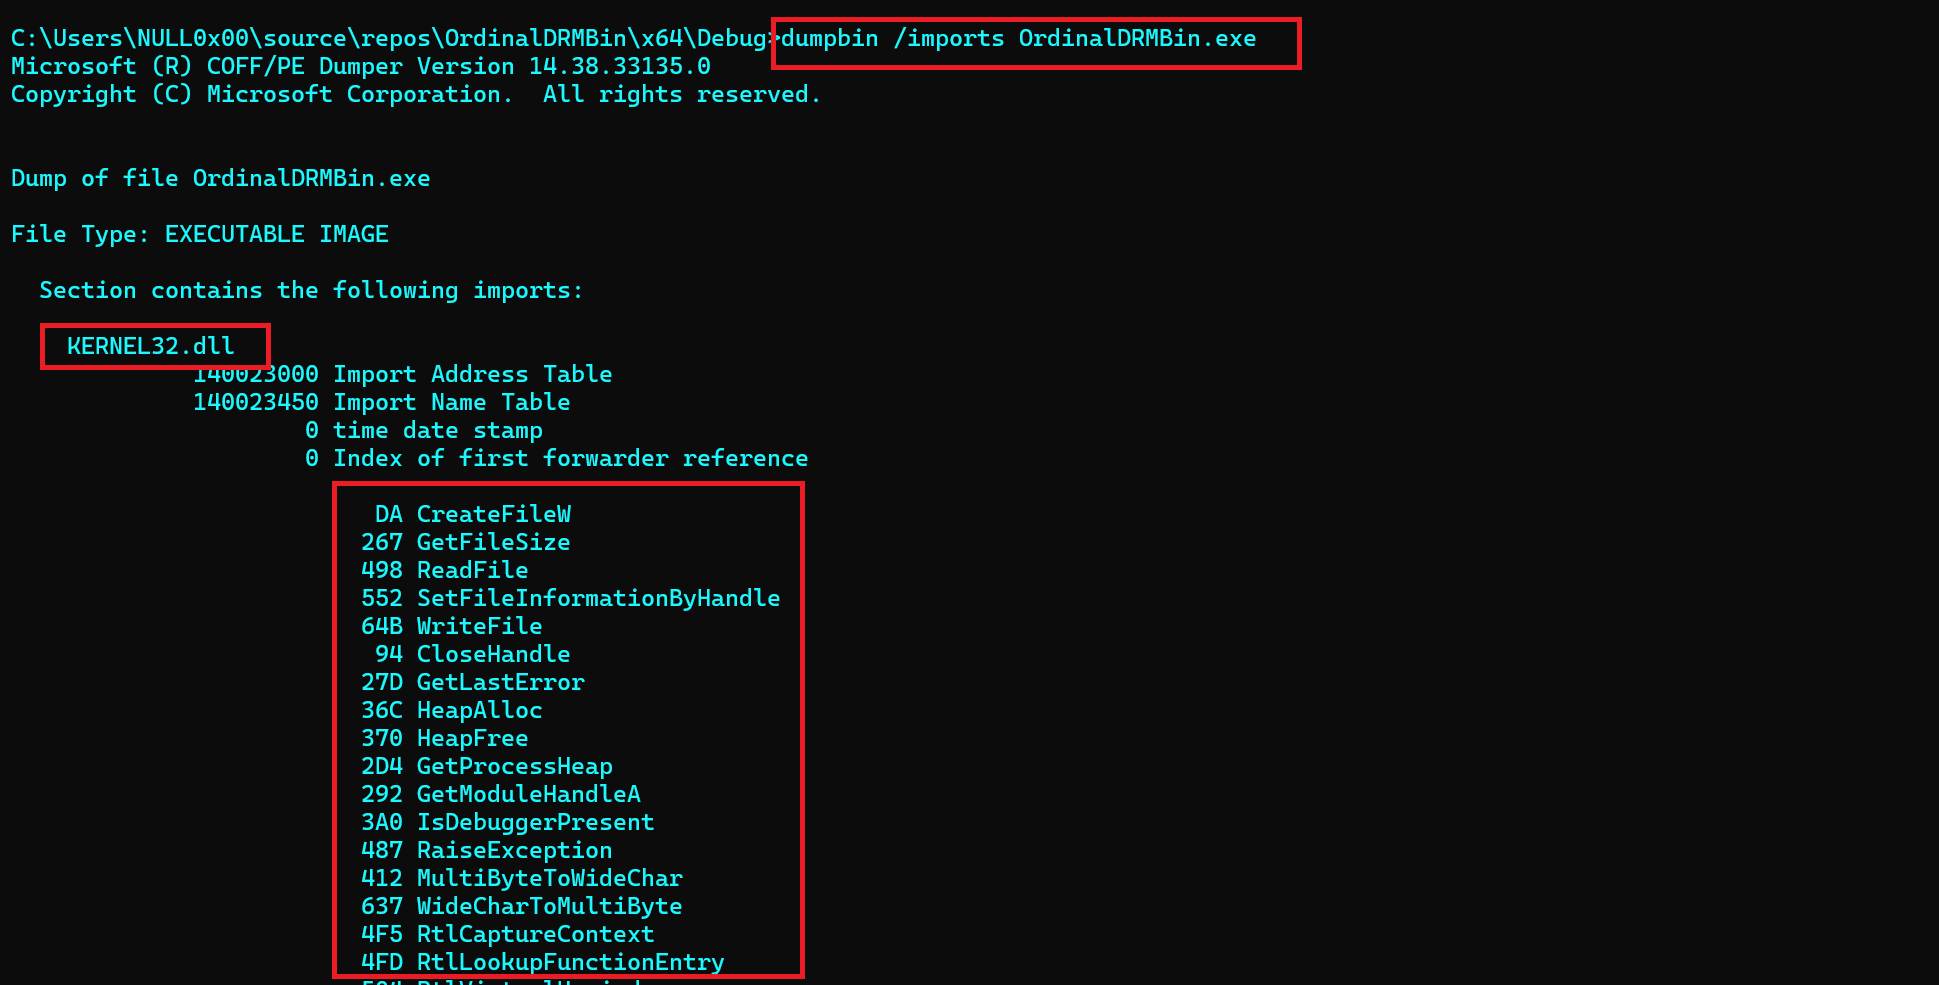 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
 safety-research/bloom
Automated behavioral evaluation framework for LLMs that generates diverse test scenarios to probe for sycophancy, bias, and other safety-relevant…
 whispergate/lldp
C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
 santanderai/autoguardrails
Alignment-research scaffold (autoresearch-style) for LLM guardrails: search over a single policy.md surface
 redteamoperations/redcloud-os
RedCloudOS is a Cloud Adversary Simulation Operating System for Red Teams to assess the Cloud Security of Leading Cloud Service Providers (CSPs)
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
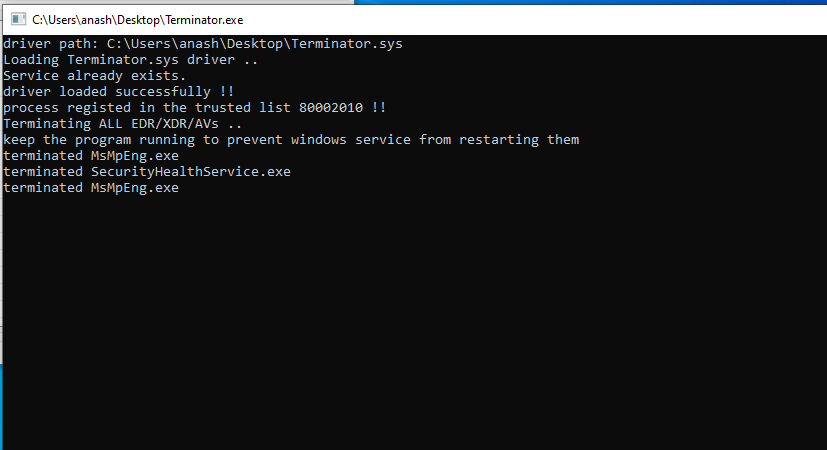 zeromemoryex/terminator
Reproducing Spyboy technique to terminate all EDR/XDR/AVs processes