ShellcodeFluctuation

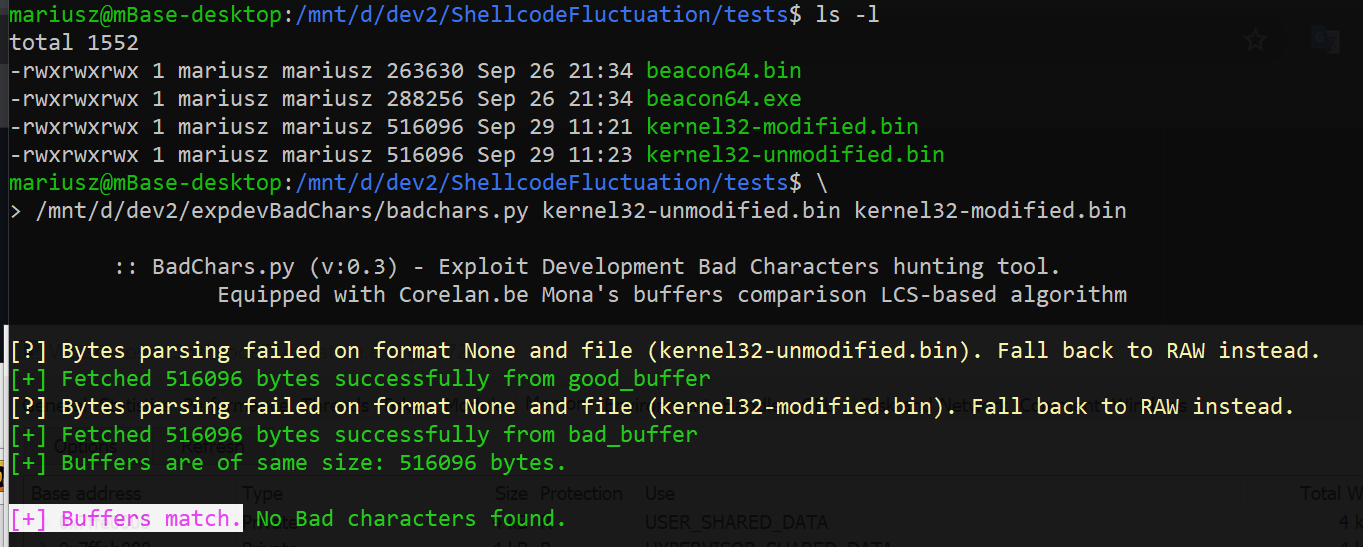
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

PE obfuscator with Evasion in mind

Tools that trigger False Positive AV alerts


Threadless Process Injection using remote function hooking.

A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…

Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.

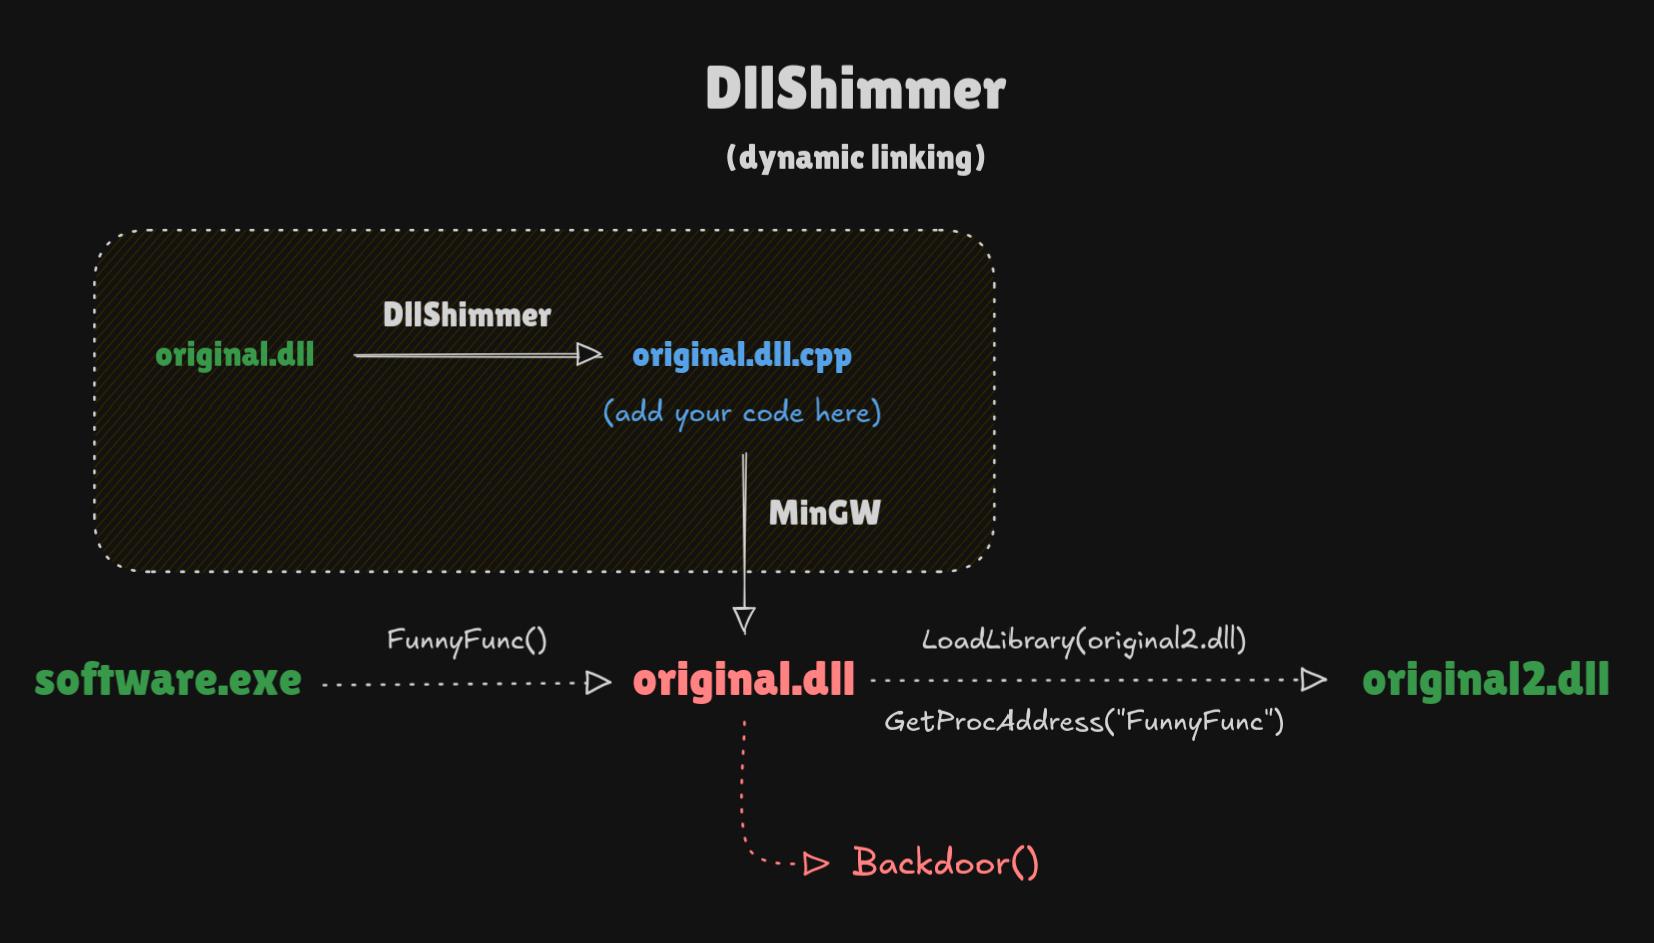
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

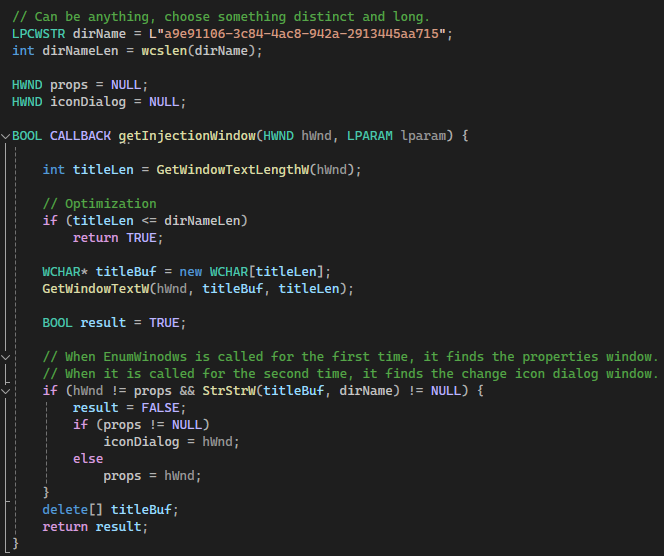
Inject DLLs into the explorer process using icons

macOS Initial Access Payload Generator

A delicious, but malicious SSL-VPN server 🌮

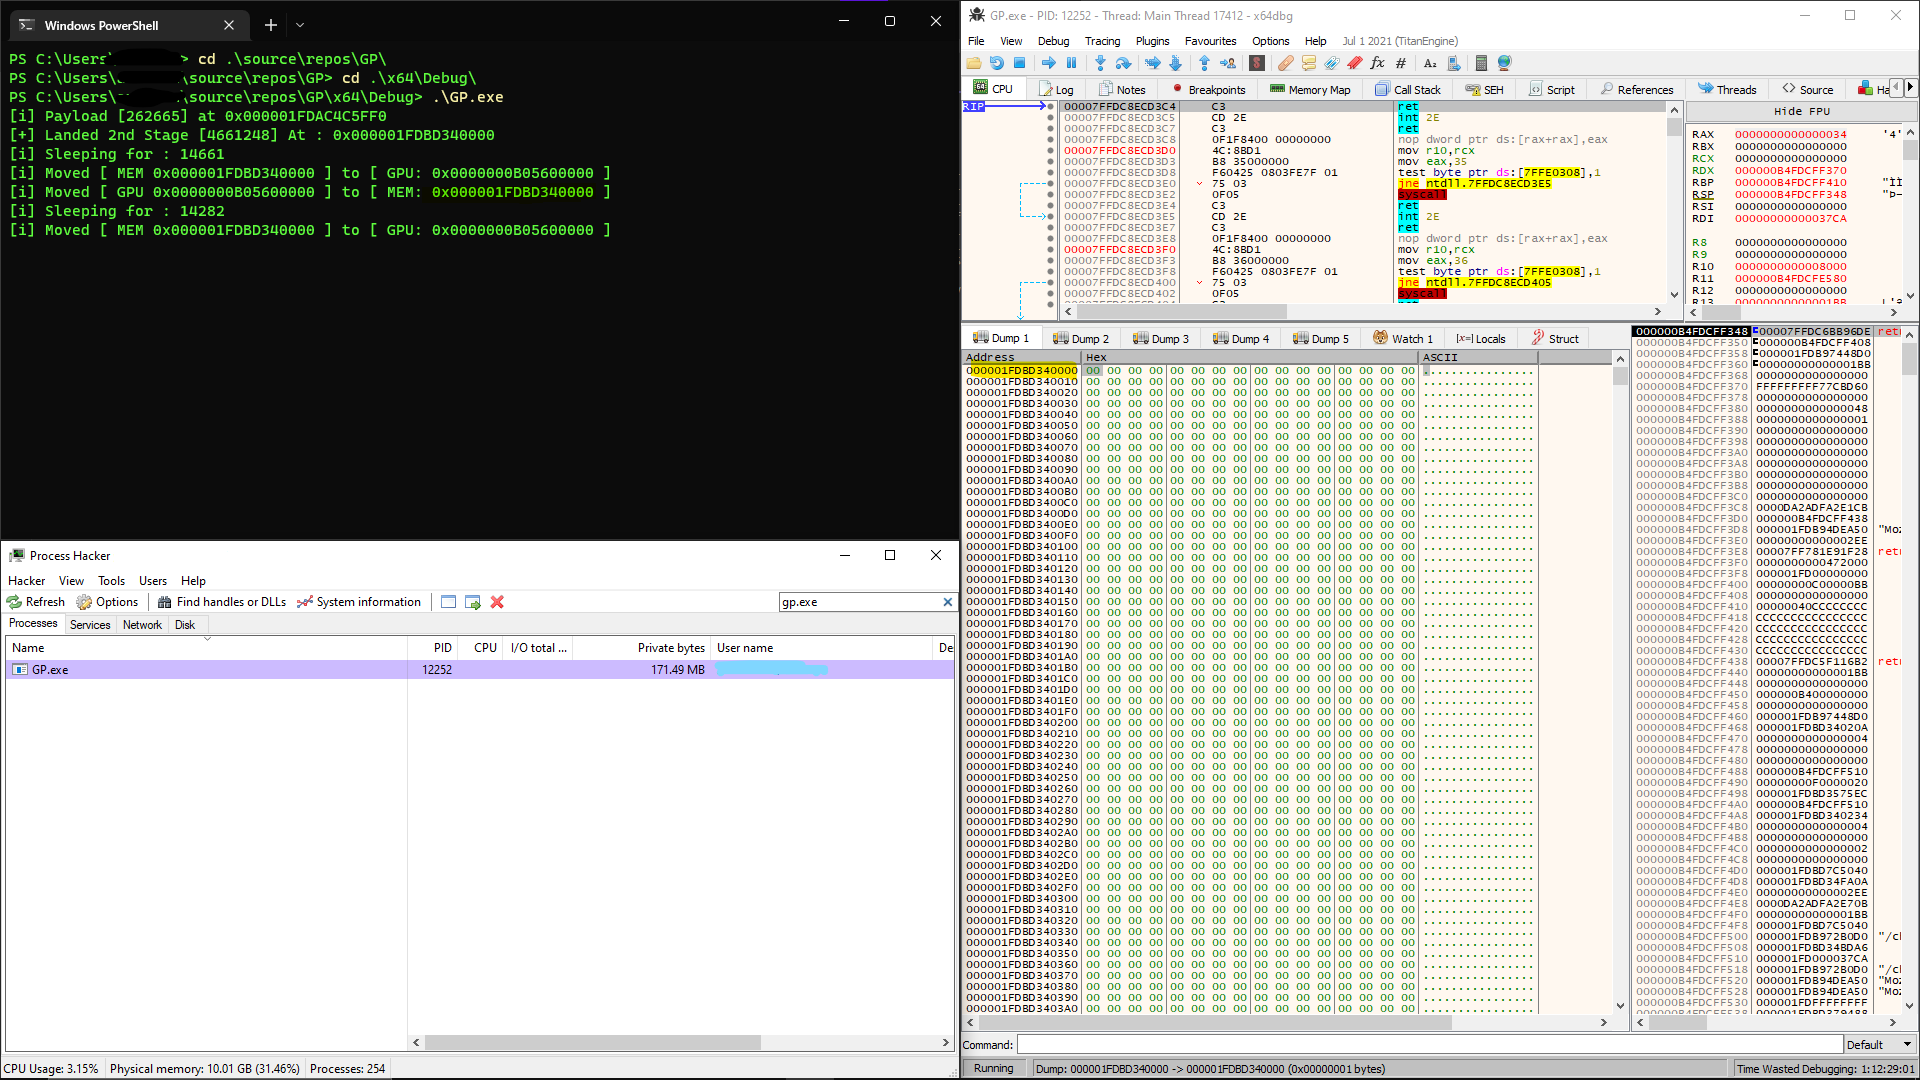
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…

Encypting the Heap while sleeping by hooking and modifying Sleep with our own sleep that encrypts the heap

A simple ptrace-less shared library injector for x64 Linux

Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.

Collection of VBA macro published in our twitter / blog