

blenny
 frank2/blenny
A payload delivery system which embeds payloads in an executable's icon file!
adversarial-attackpayload-developmentpayload-generation+2
frank2/blennyA payload delivery system which embeds payloads in an executable's icon file!
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 thewover/dinvoke
Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.
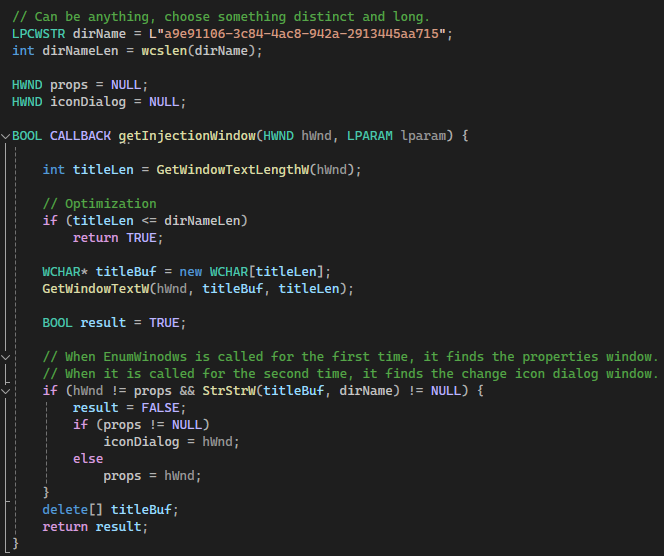 d419h/iconjector
Inject DLLs into the explorer process using icons
 d00mfist/mystikal
macOS Initial Access Payload Generator
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
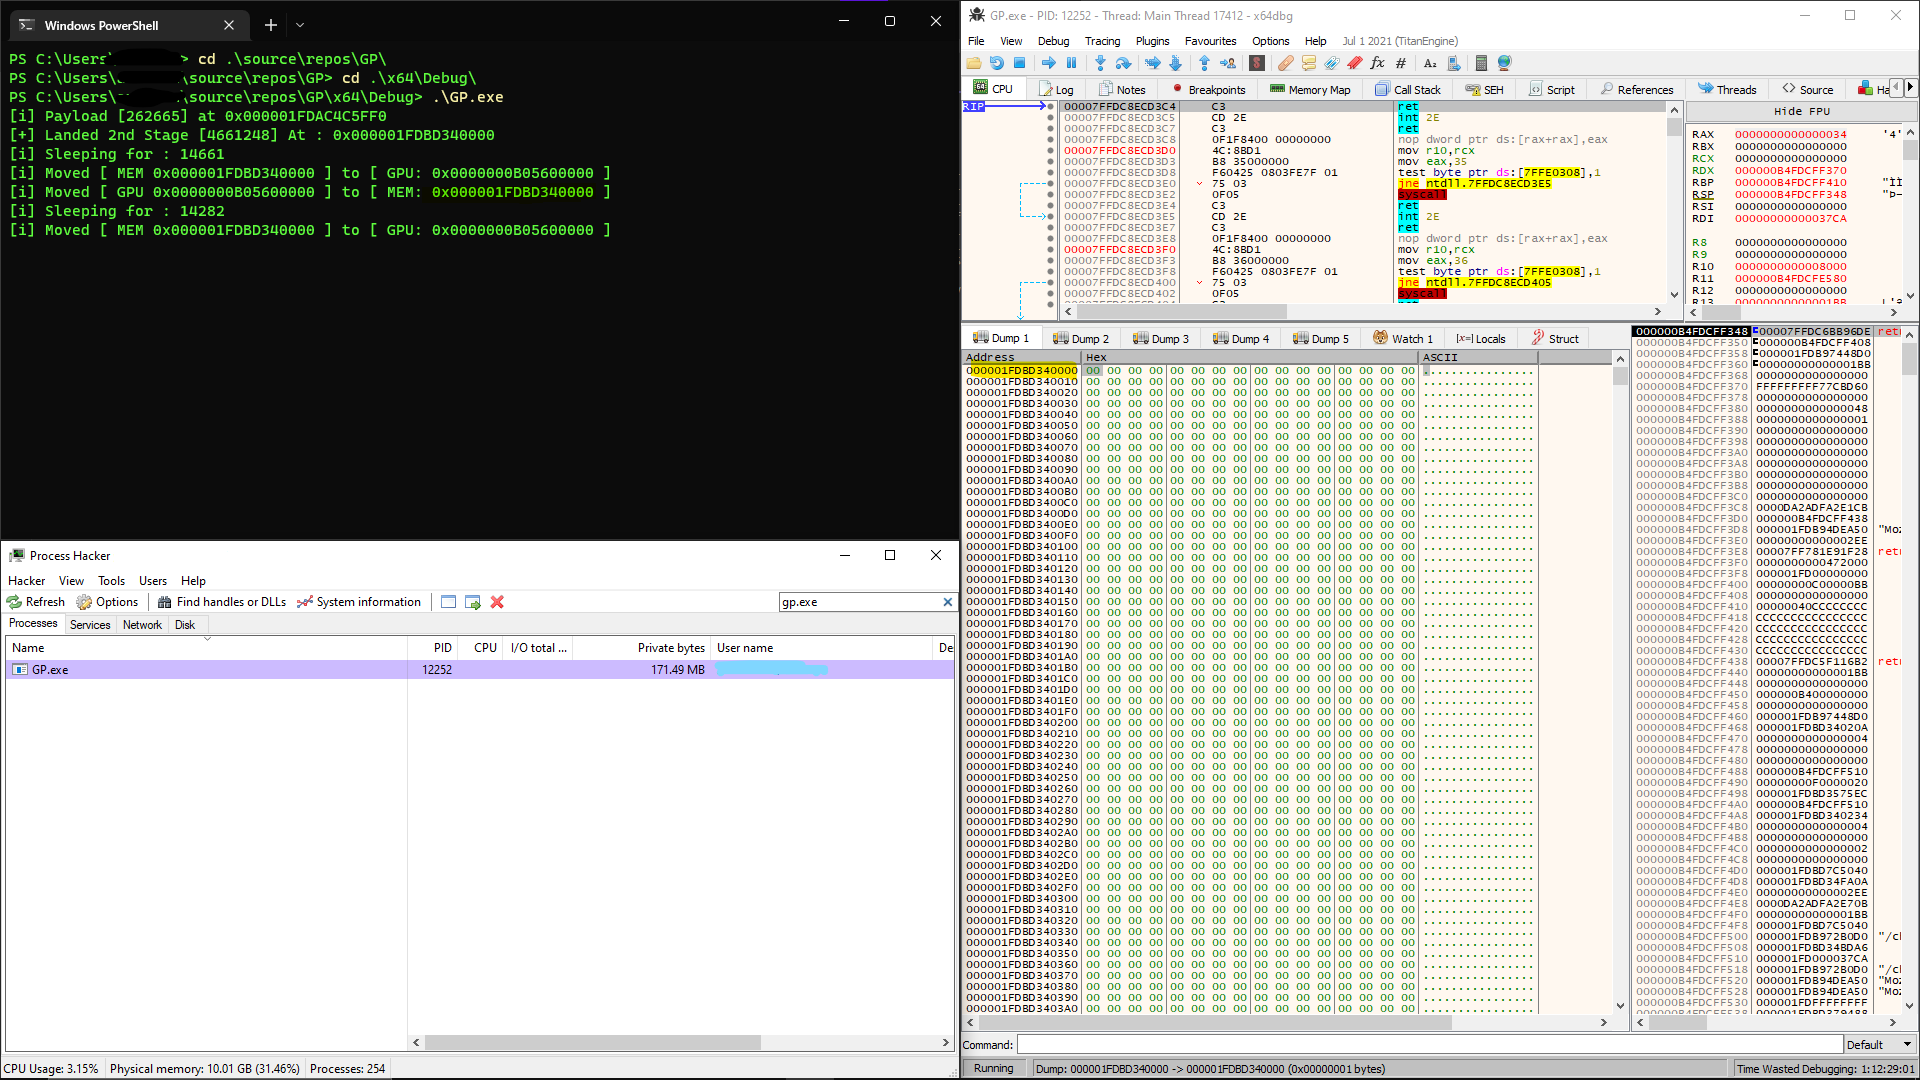 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…
 saadahla/heapcrypt
Encypting the Heap while sleeping by hooking and modifying Sleep with our own sleep that encrypts the heap
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 saadahla/pe-obfuscator
PE obfuscator with Evasion in mind
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.

 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.