Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
42 results
no-defender preview
Archived

no-defender

GitHubes3n1n/no-defender

A slightly more fun way to disable windows defender + firewall. (through the WSC api)

adversarial-attackids-ips-evasionpenetration-testing+3
2.0k
2 years ago
Red-Team-GOAD-Lab-Proxmox preview

Red-Team-GOAD-Lab-Proxmox

GitHubpho5nix/red-team-goad-lab-proxmox

Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
adversarial-attackcommand-and-controldefensive-tools+7
282 days ago
EDRSilencer preview

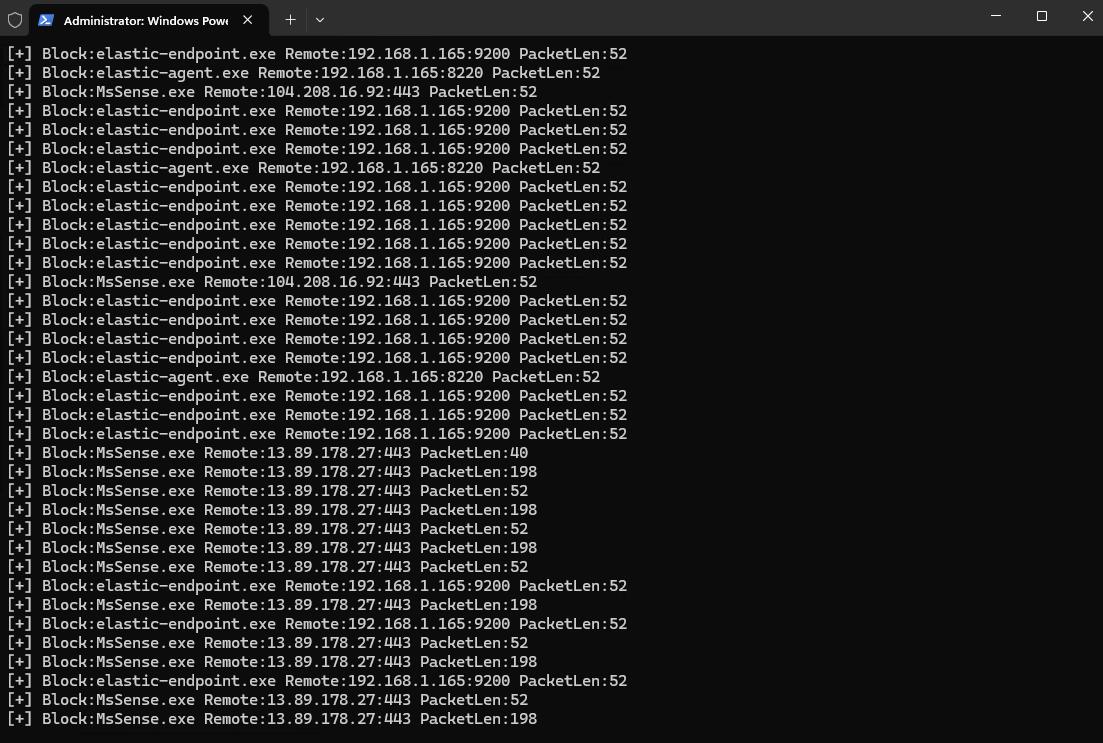
EDRSilencer

GitHubnetero1010/edrsilencer

A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.

adversarial-attackids-ips-evasionpost-exploitation+1
1.9k1 year ago
FilelessPELoader preview

FilelessPELoader

GitHubsaadahla/filelesspeloader

Loading Remote AES Encrypted PE in memory , Decrypted it and run it
adversarial-attackids-ips-evasionpayload-development+3
1.0k3 years ago
HellHall preview

HellHall

GitHubmaldev-academy/hellhall

Performing Indirect Clean Syscalls
adversarial-attackids-ips-evasionpayload-development+1
6284 months ago
WinDefenderKiller preview

WinDefenderKiller

GitHubs12cybersecurity/windefenderkiller

Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)
adversarial-attackexploitationids-ips-evasion+3
5595 months ago
Blackout preview

Blackout

GitHubzeromemoryex/blackout

kill anti-malware protected processes ( BYOVD )

adversarial-attackexploitationids-ips-evasion+1
9913 years ago
hookchain preview

hookchain

GitHubhelviojunior/hookchain

HookChain: A new perspective for Bypassing EDR Solutions
adversarial-attackids-ips-evasionpapers-research+2
6141 year ago
Crystal-Kit preview

Crystal-Kit

GitHubrasta-mouse/crystal-kit

Evasion kit for Cobalt Strike
adversarial-attackcommand-and-controlids-ips-evasion+3
5074 months ago
CallStackSpoofer preview

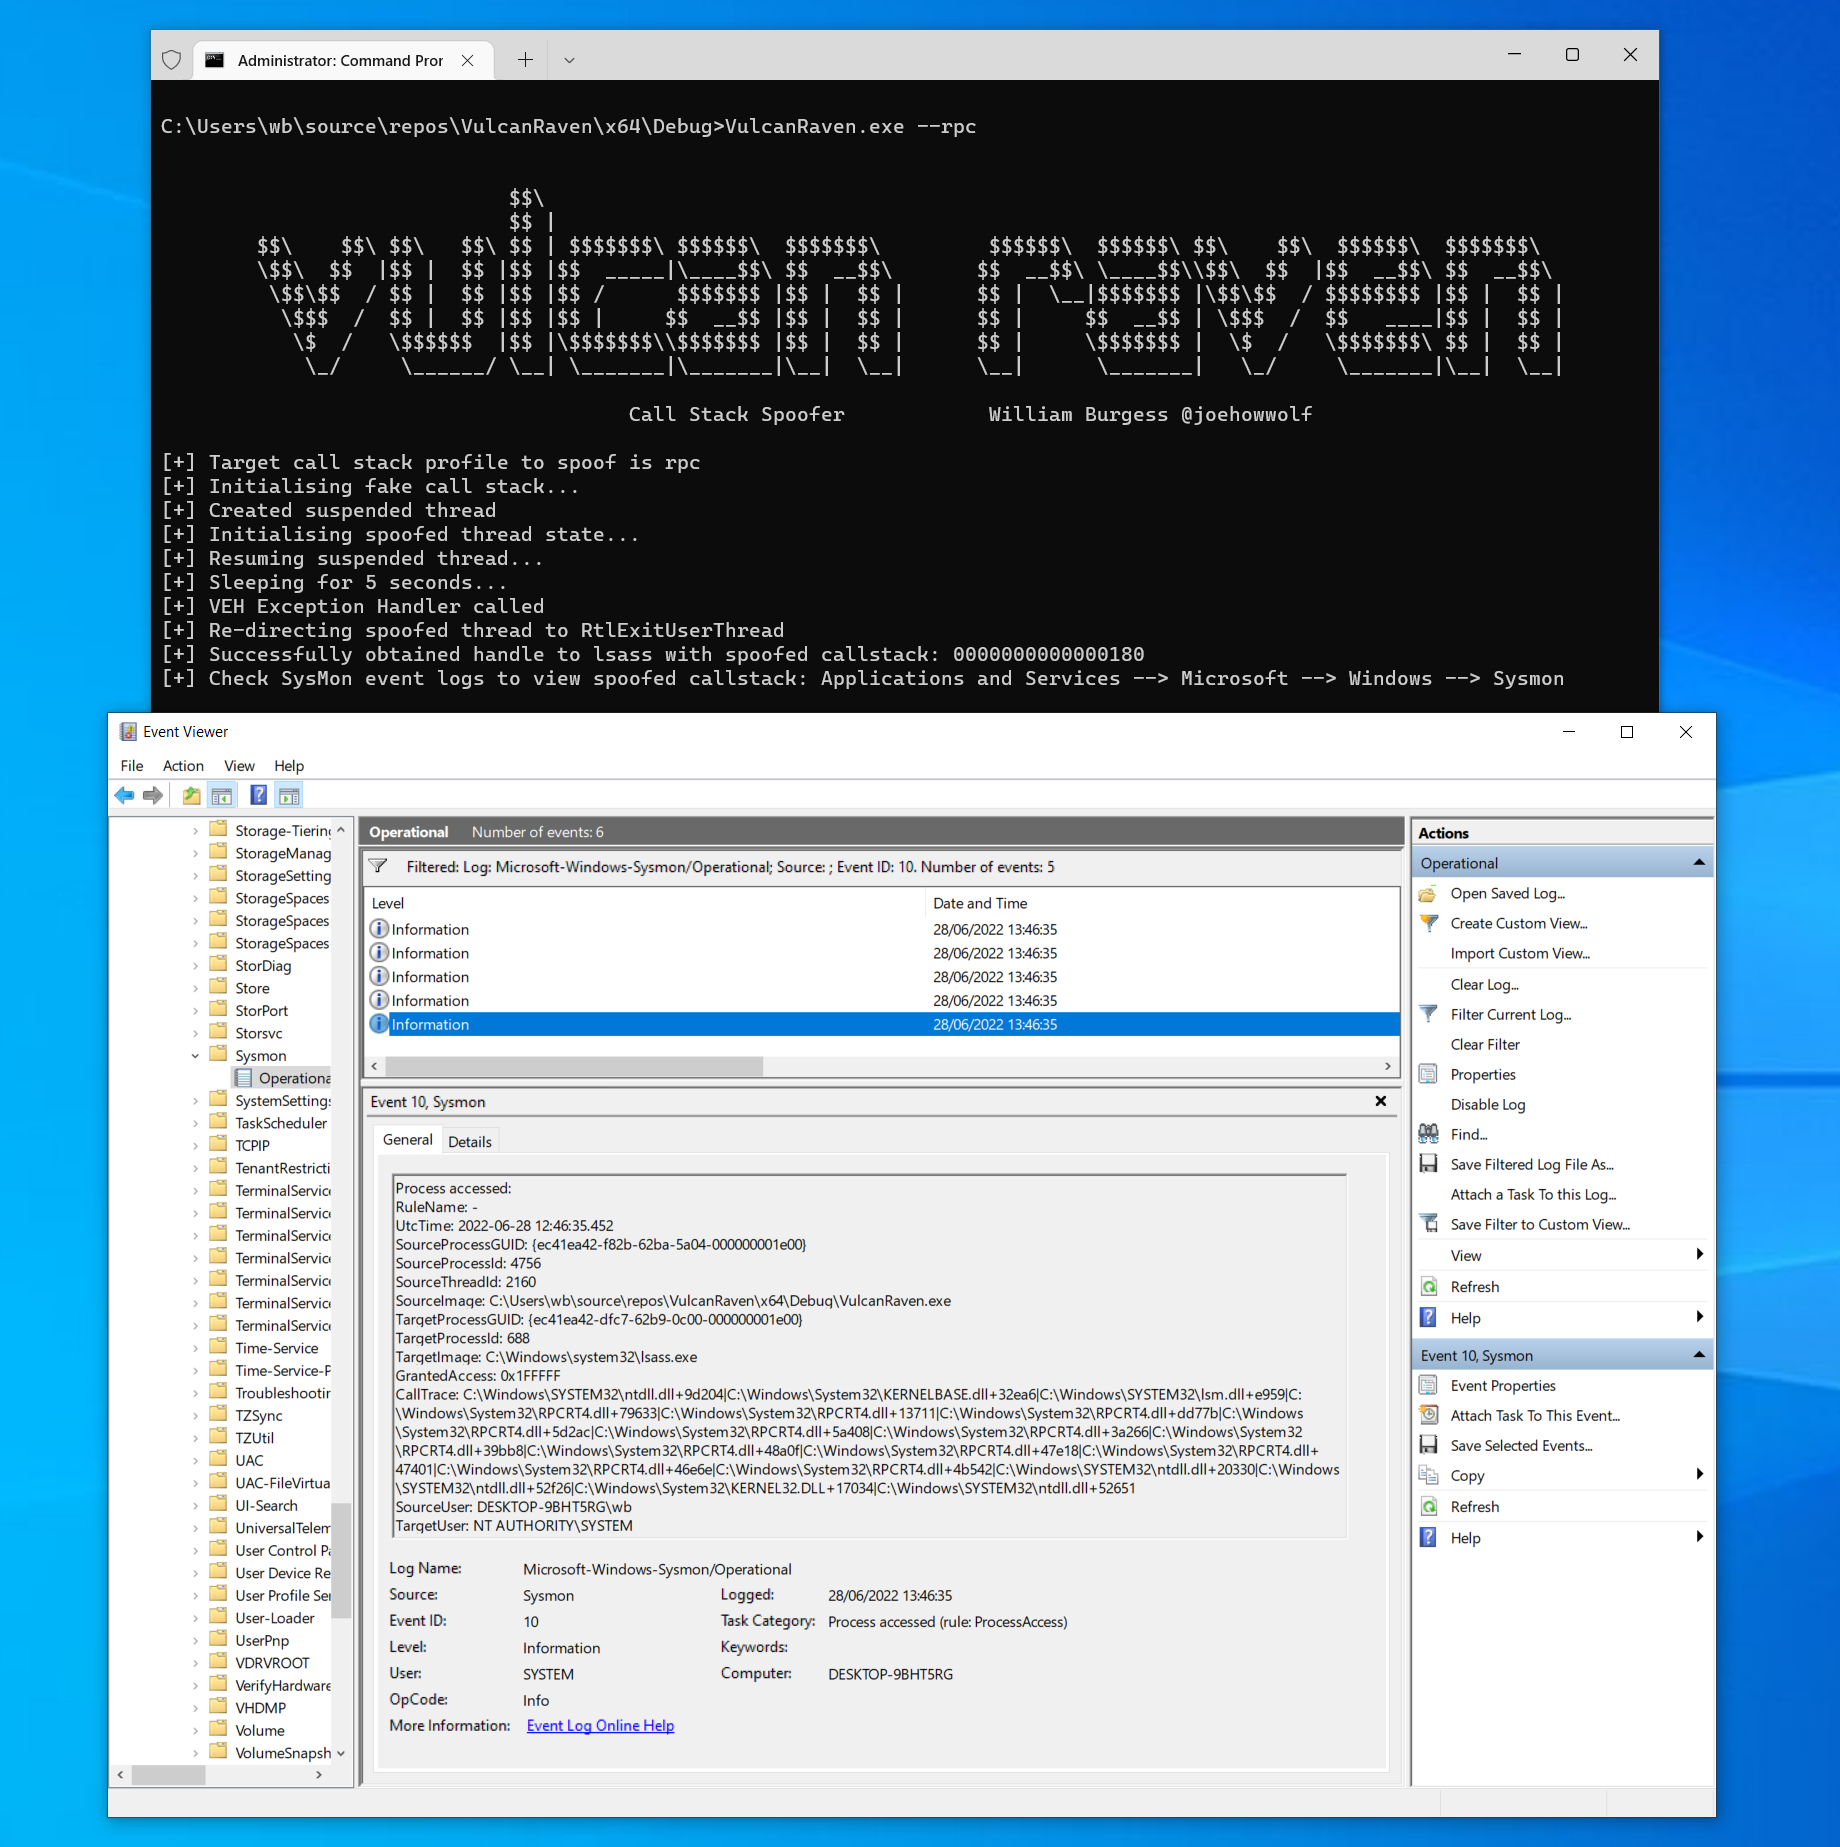
CallStackSpoofer

GitHubwithsecurelabs/callstackspoofer

A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
adversarial-attackids-ips-evasionpost-exploitation+1
5981 year ago
CallstackSpoofingPOC preview

CallstackSpoofingPOC

GitHubpard0p/callstackspoofingpoc

C++ self-Injecting dropper based on various EDR evasion techniques.
adversarial-attackids-ips-evasionpayload-development+1
4452 years ago
EDRPrison preview

EDRPrison

GitHubsenzee1984/edrprison

Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
adversarial-attackids-ips-evasionnetwork-security+2
4782 years ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
adversarial-attackbinary-analysisids-ips-evasion+3
3833 years ago
Amsi_Bypass_In_2023 preview

Amsi_Bypass_In_2023

GitHubsenzee1984/amsi_bypass_in_2023

Amsi Bypass payload that works on Windwos 11
adversarial-attackexploitationids-ips-evasion+4
3783 years ago
Unwinder preview

Unwinder

GitHubkudaes/unwinder

Call stack spoofing for Rust
adversarial-attackids-ips-evasionpayload-development+2
3851 year ago
unhook-bof preview

unhook-bof

GitHubrsmudge/unhook-bof

Remove API hooks from a Beacon process.
adversarial-attackids-ips-evasionpost-exploitation+1
2825 years ago
UnhookingPatch preview

UnhookingPatch

GitHubsaadahla/unhookingpatch

Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime

adversarial-attackids-ips-evasionpayload-development+2
3053 years ago
NTDLLReflection preview

NTDLLReflection

GitHubsaadahla/ntdllreflection

Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…

adversarial-attackids-ips-evasionpost-exploitation+1
3063 years ago
Previous123Next